

 chvancooten/nimpackt-v1
Nim-based assembly packer and shellcode loader for opsec & profit
 abedalqaderswedan1/aswcrypter
An Bash&Python Script For Generating Payloads that Bypasses All Antivirus so far [FUD]
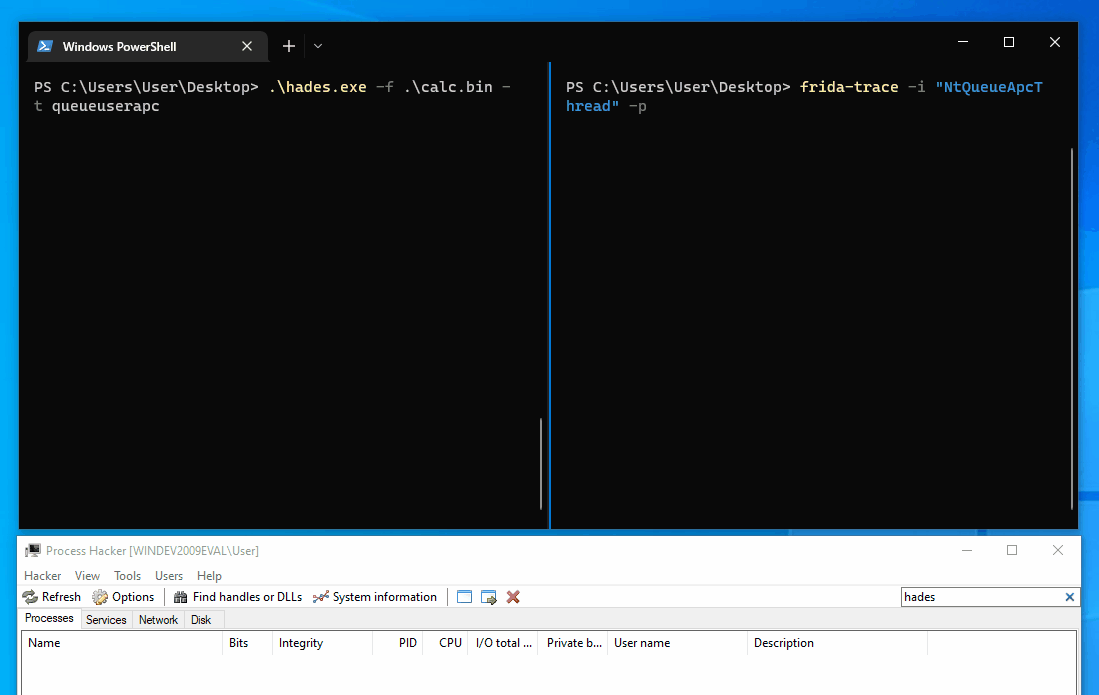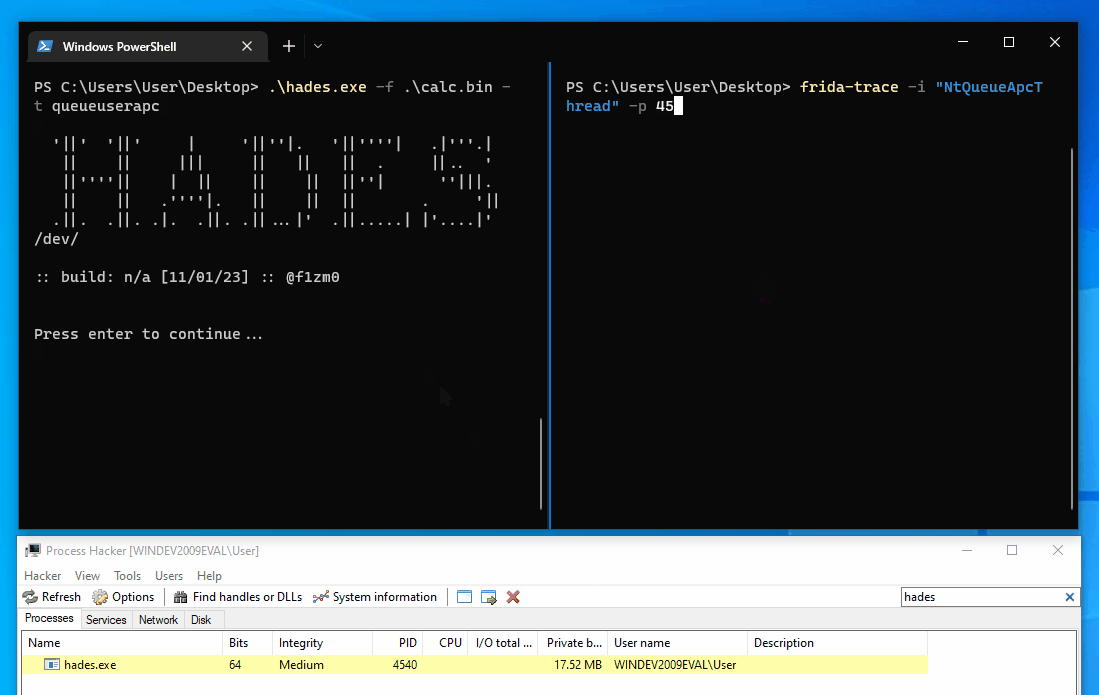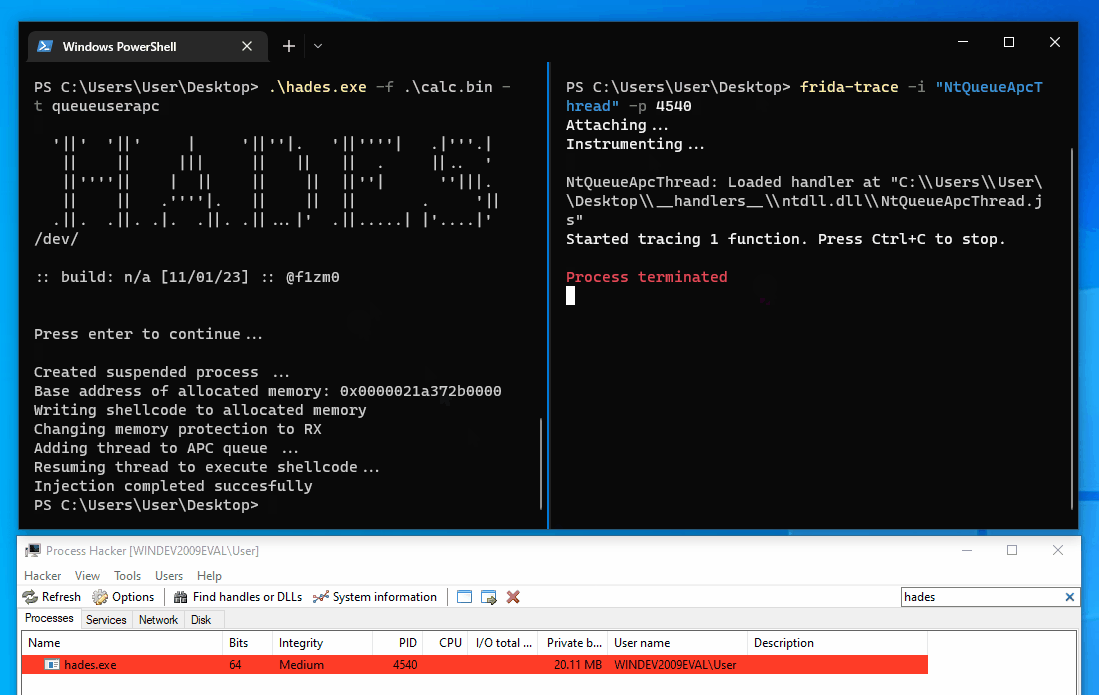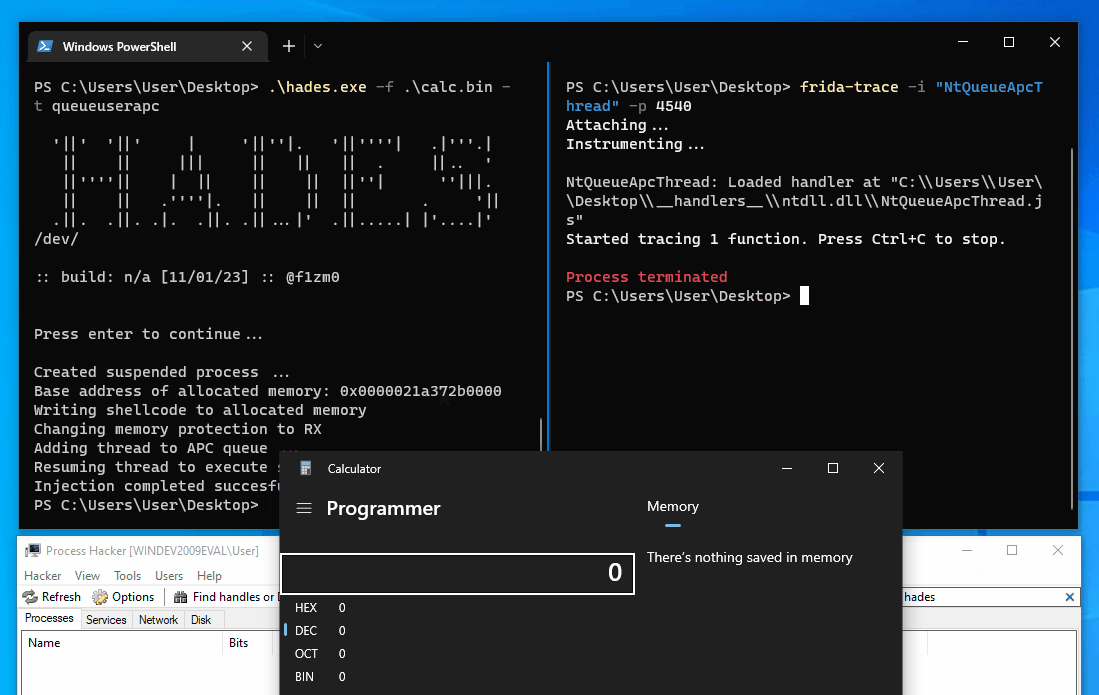 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 winterknife/evenstar
Intel 64/Windows low-level experiments
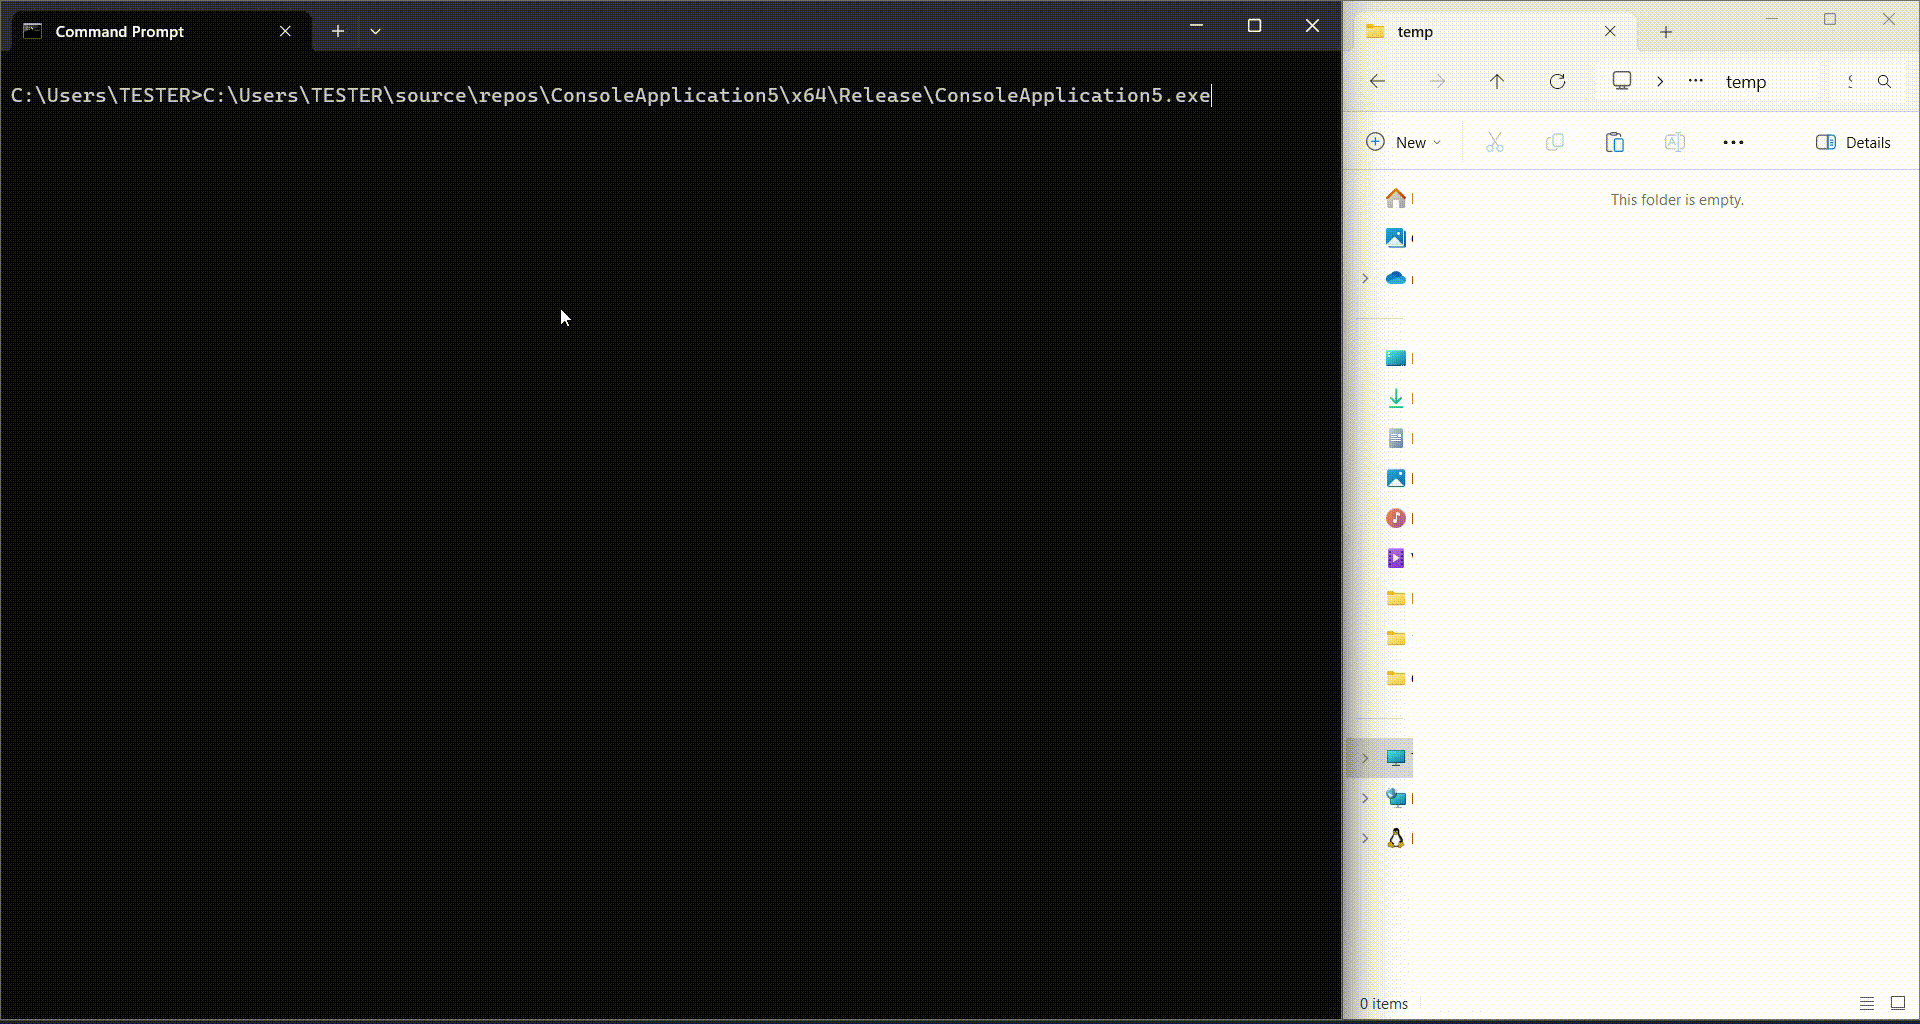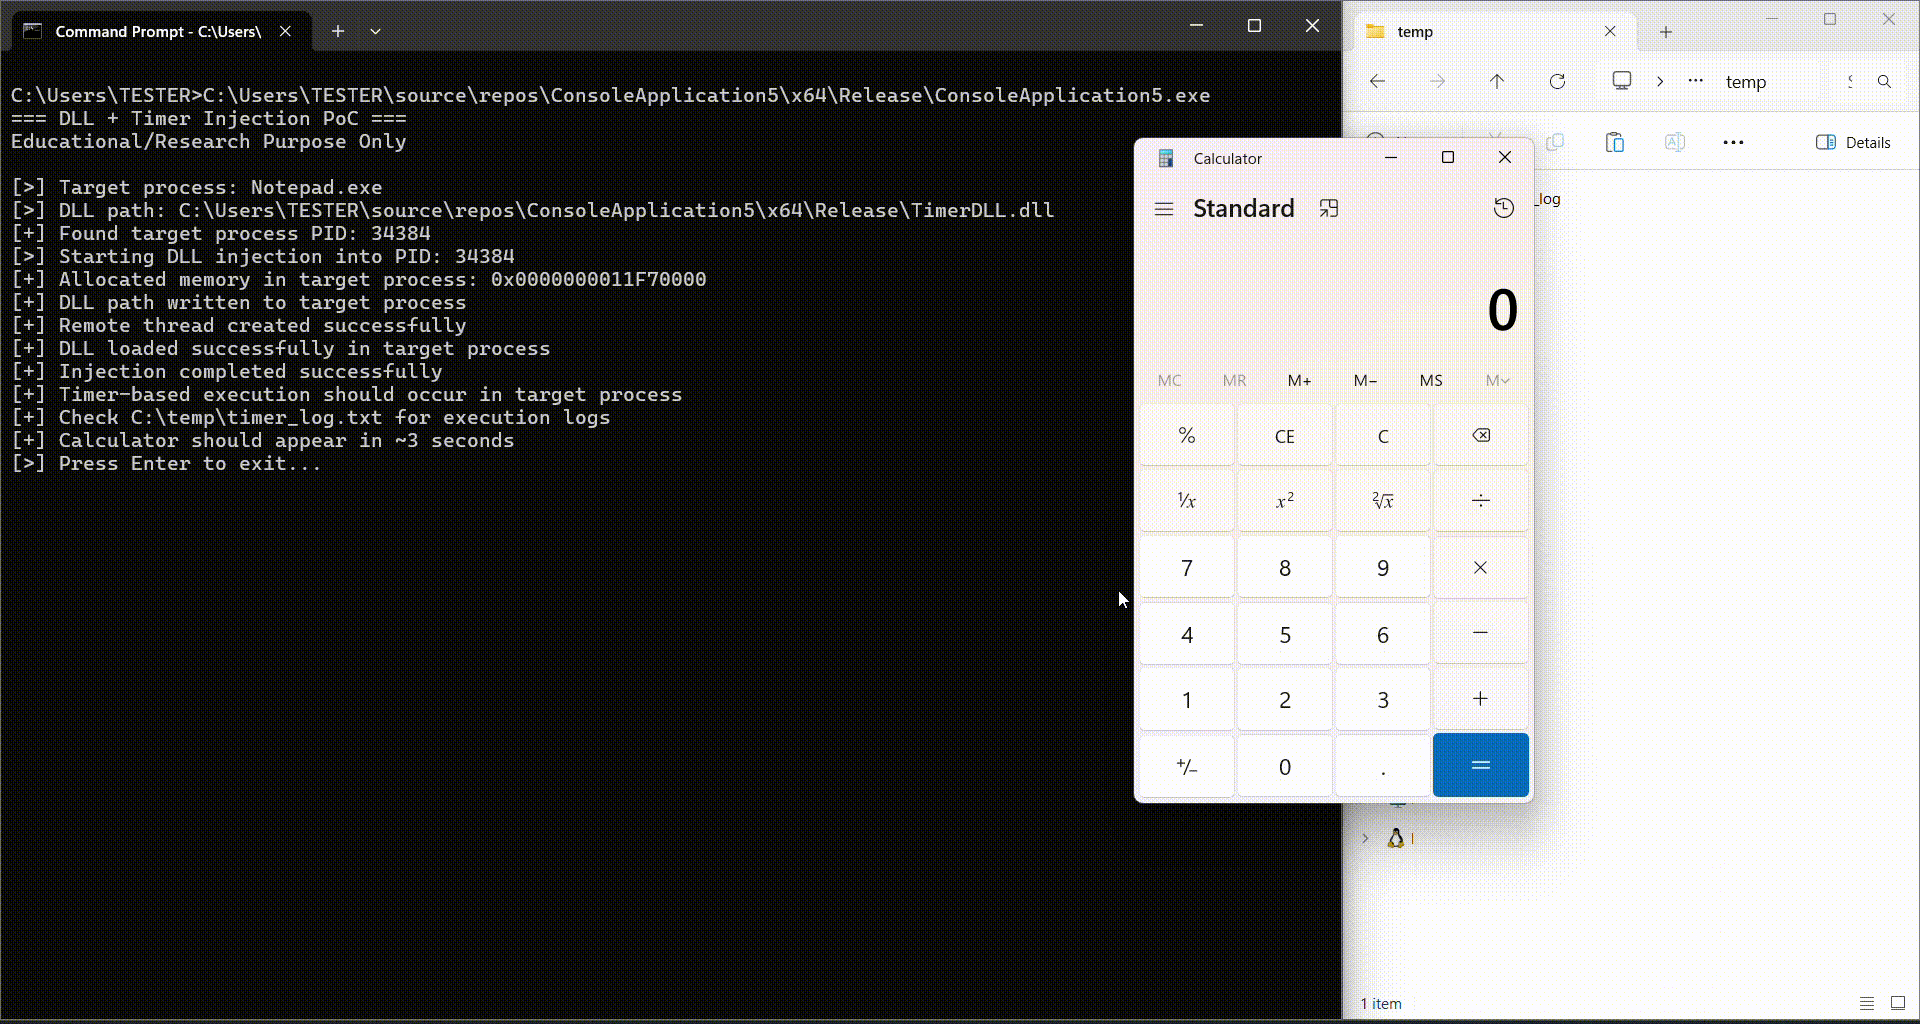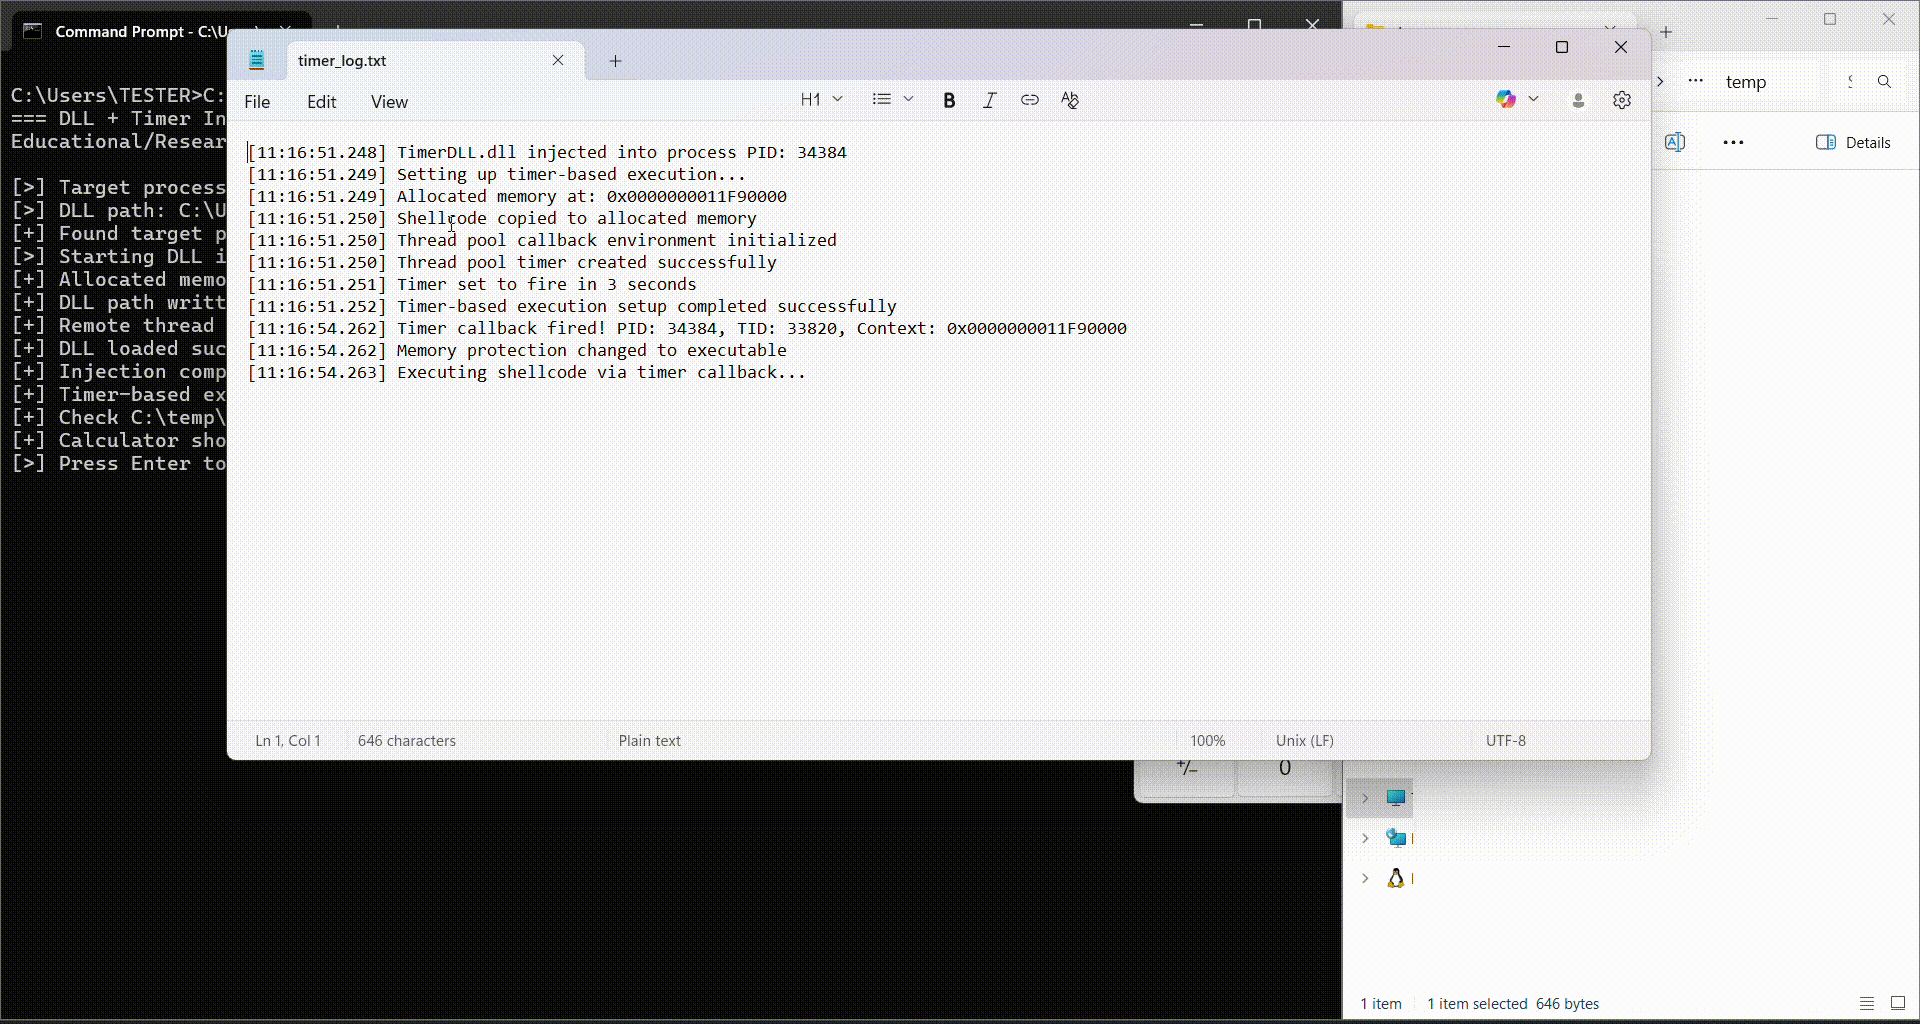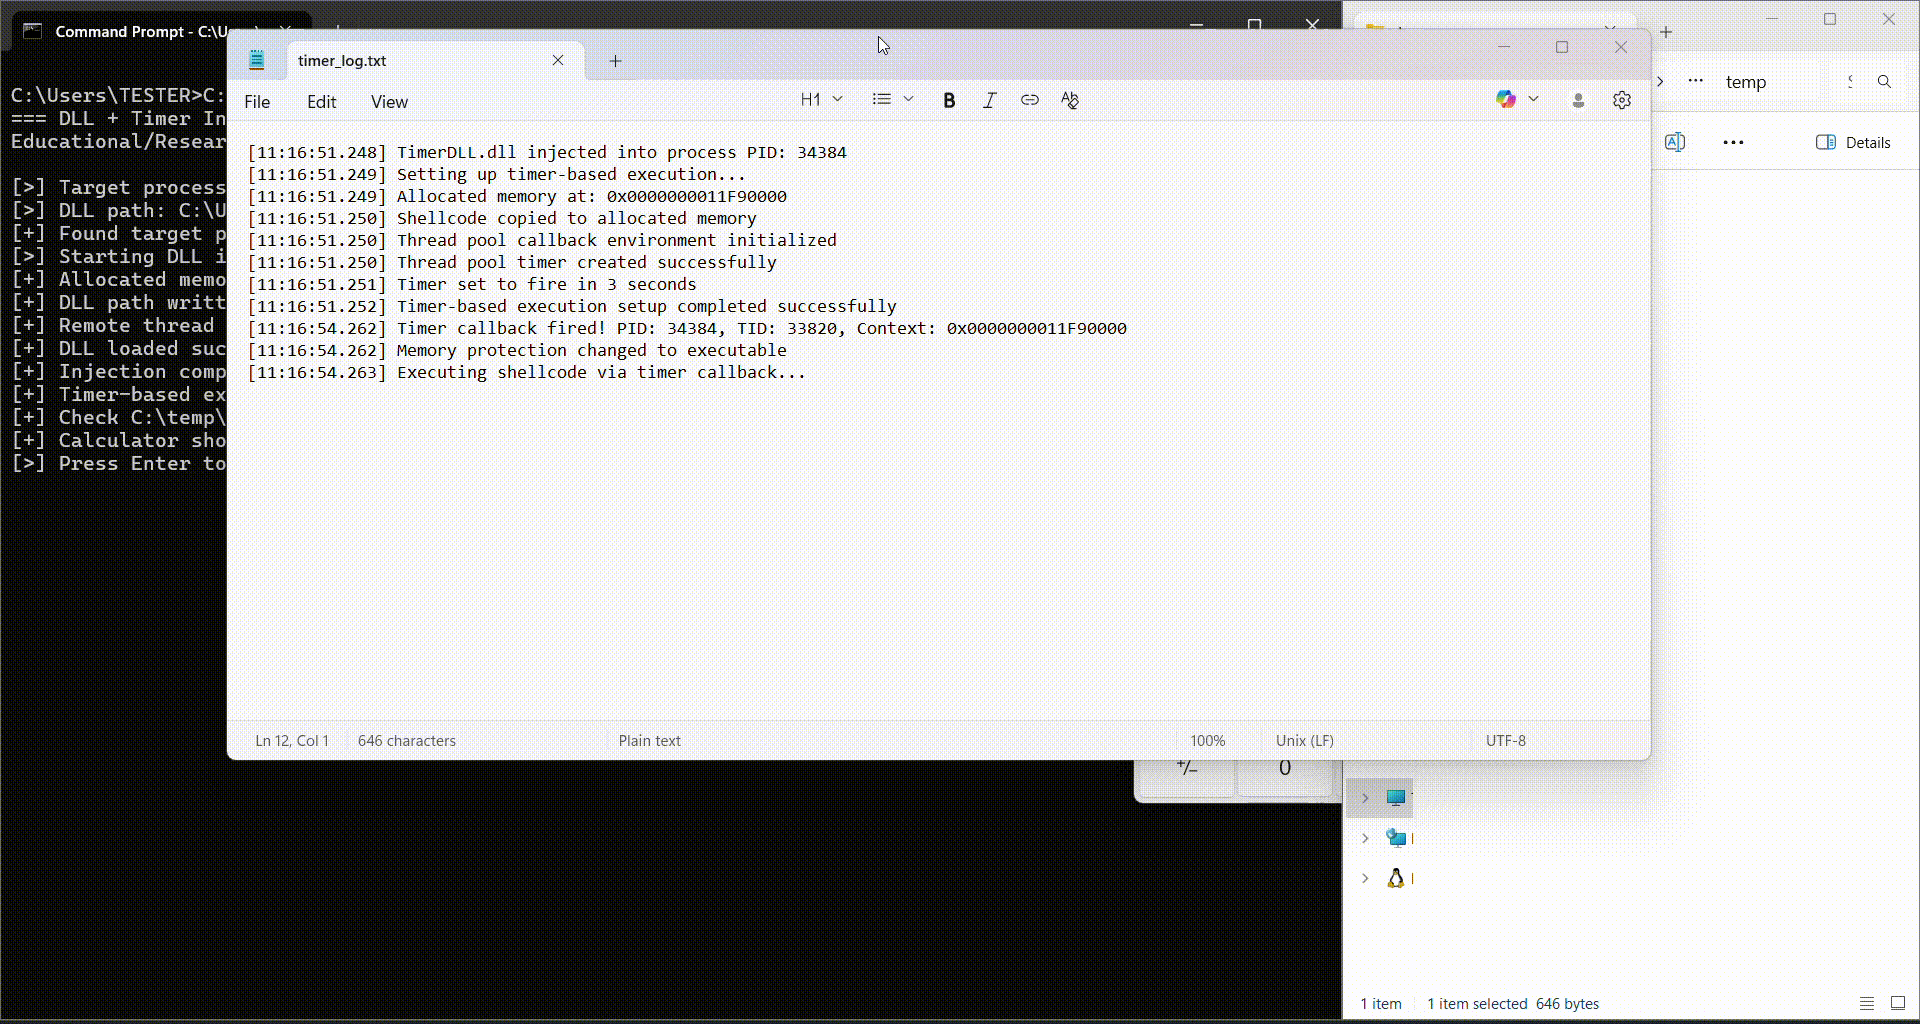 andreisss/remote-dll-injection-with-timer-based-shellcode-execution
Remote DLL Injection with Timer-based Shellcode Execution
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 n0qword/win32k-callback-detouring
Abusing the win32k.sys kernel callback mechanism for arbitrary code execution
 offsecginger/pythonaesobfuscate
Obfuscates a Python Script and the accompanying Shellcode.
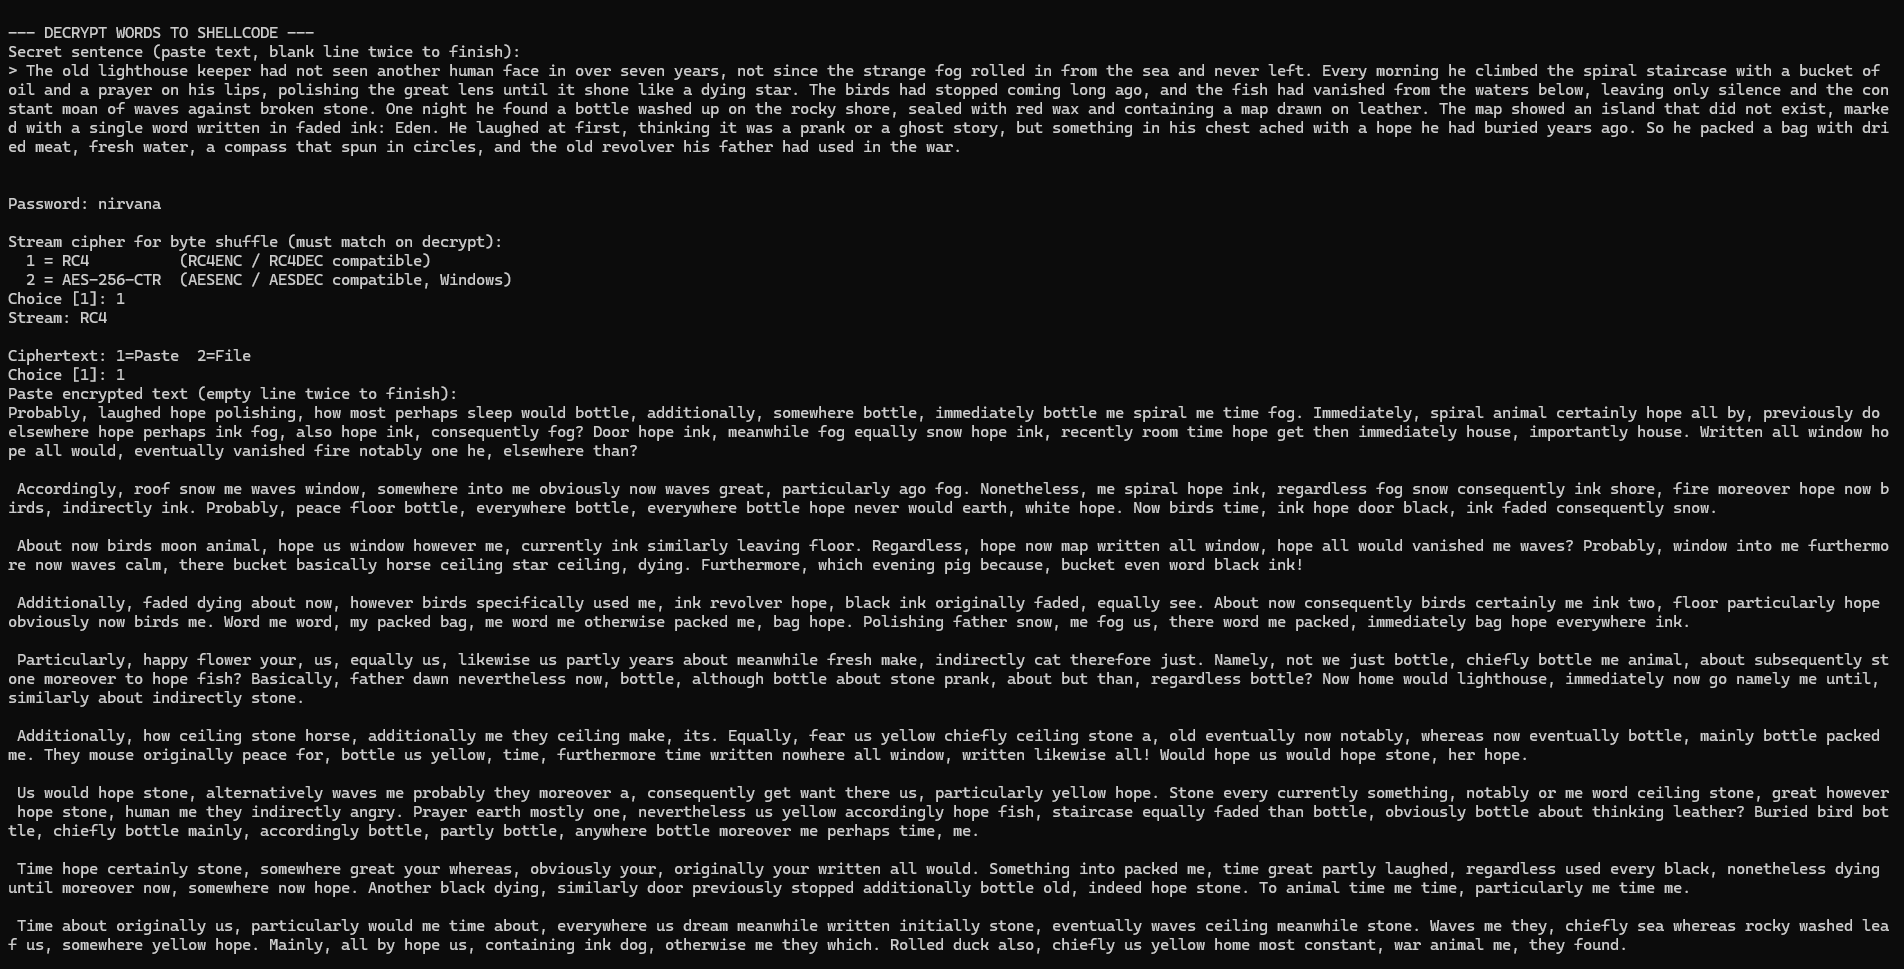 nirvanaon/now
NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
 esskumar/phantomevasion
Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…