
IronPE
 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
binary-analysisbinary-exploitationeducation+5
124
iss4cf0ng/ironpeRust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis
 umpolungfish/byvalver
takes shellcode bad-bytes and banishes them, returning cleaned shellcode with preserved functionalities
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
 boogipop/cve-2023-22527-godzilla-memshell
CVE-2023-22527 内存马注入工具
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 daniel224455/katana
Let's hijack our bootchain - CVE-2021-30327

 exploit-database/exploitdb-bin-sploits
exploitdb-bin-sploits // Exploit-Database's binary exploits (what was located in the /sploits directory)
 chris1sflaggin/lcsajdump
An ML powered Graph-Based Multi-Architecture Approach for ROP Gadget Detection
 pentestical/cve-2020-9484
Bash proof-of-concept exploit for CVE-2020-9484 enabling remote code execution on Apache Tomcat via insecure deserialization in file uploads, with…
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
 synacktiv/canon-mf644
Exploit and firmware analysis toolkit for Canon MF644 printer vulnerabilities, including Python exploits, ARM shellcode, and IDA Pro loader scripts…
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
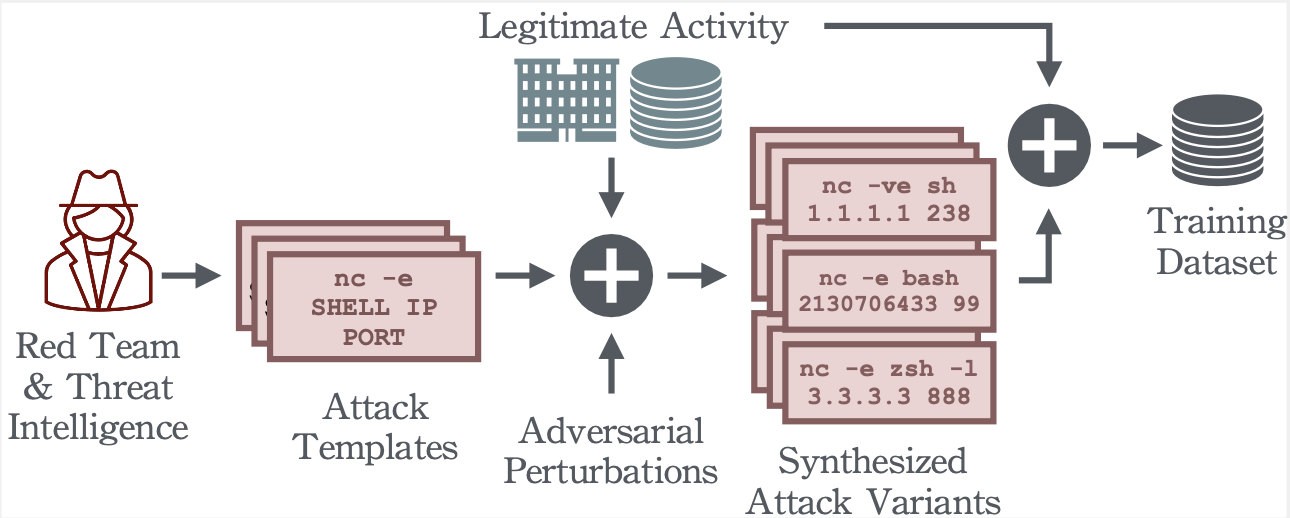 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 sorrow404null/cve-2026-43499-rmx5200
Android 16 local privilege escalation exploit for realme RMX5200 using LD_PRELOAD-based preload.so chain to achieve temporary root access via…
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 guiimoraes/cve-2025-15467
Command Execution PoC for OpenSSL Stack buffer overflow CVE-2025-15467