
asminject
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
container-escapepayload-developmentpenetration-testing+2
149
bishopfox/asminjectHeavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 trungnguyen1909/cve-2019-8781-macos
Exploit POC for the bug CVE-2019-8781, found by @LinusHenze
 3x1t1um/cve-2007-2447
Python exploit for CVE-2007-2447 that triggers Samba username map script command injection to open a reverse shell on vulnerable targets.
 damariion/cve-2017-14980.rce
Buffer overflow in Sync Breeze Enterprise 10.0.28 allows remote attackers to have unspecified impact via a long username parameter to /login
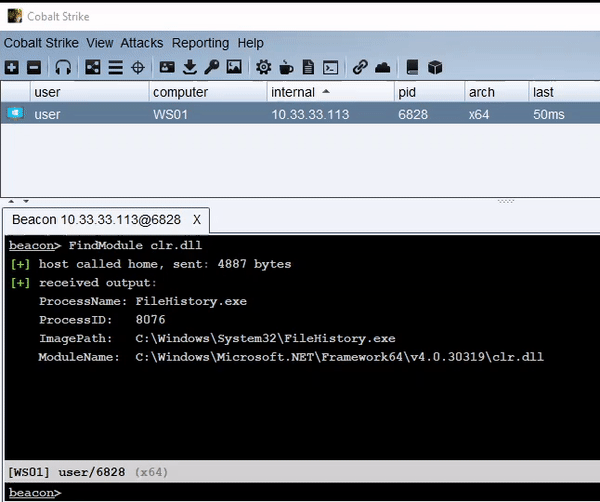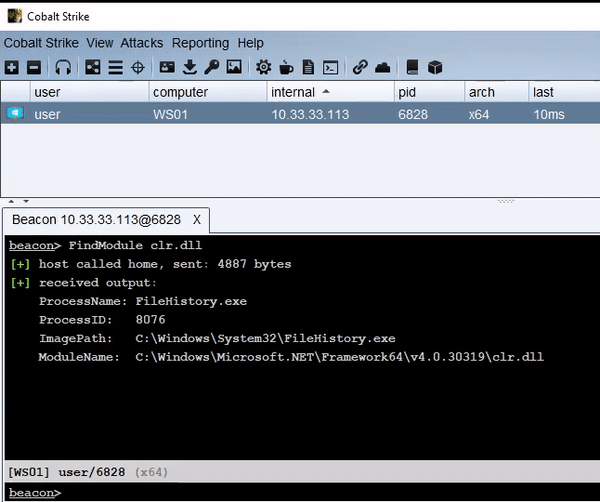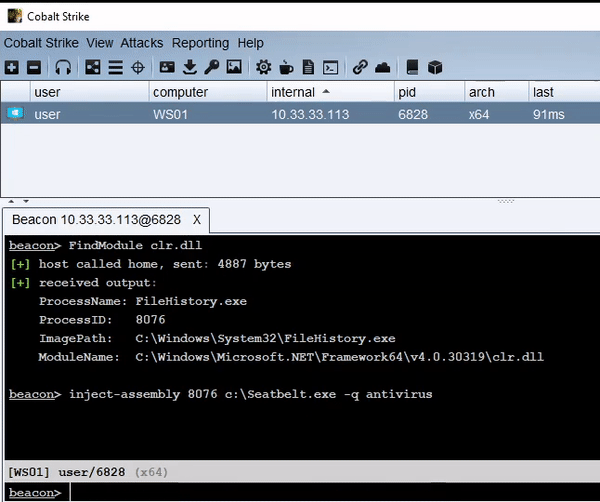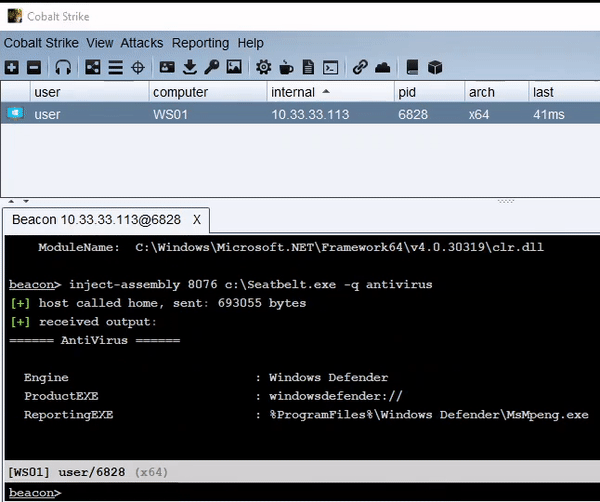 kyleavery/inject-assembly
Inject .NET assemblies into an existing process
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
 r3n3r0/cve-2026-20700
PoC demonstrating dyld as a PAC signing oracle via hand-crafted Mach-O chained fixups on arm64e, achieving controlled PAC-valid pointer writes and…
 syfi/cve-2018-8174
MS Word MS WordPad via IE VBS Engine RCE
 pankass/cve-2024-37032_cve-2024-45436
CVE-2024-45436
 bakalmode/cve-2022-3552
CVE-2022-3552 RCE with detailed exploitation steps
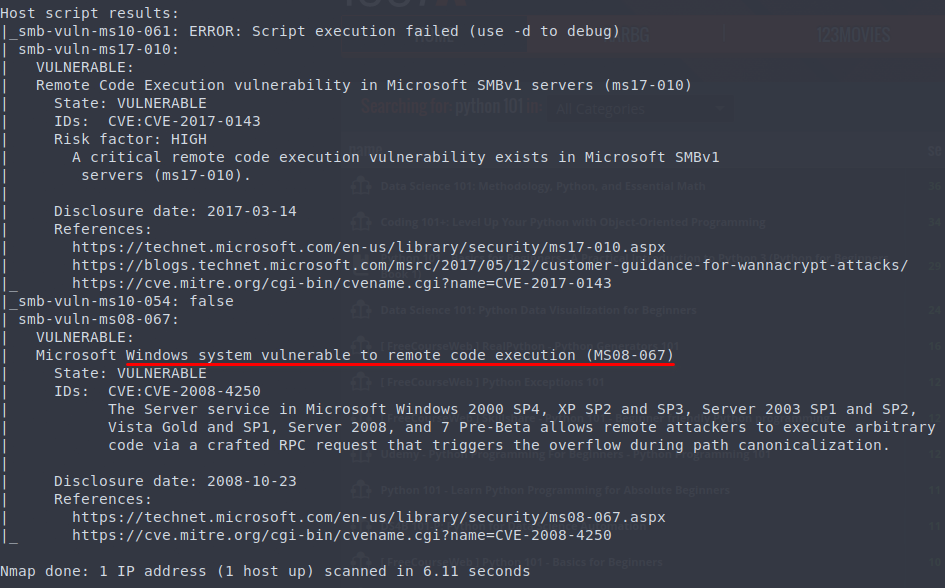 h3x0v3rl0rd/ms08-067
Python-based exploit for MS08-067 (CVE-2008-4250) providing remote code execution via SMB with reverse shell payload generation and automatic target…
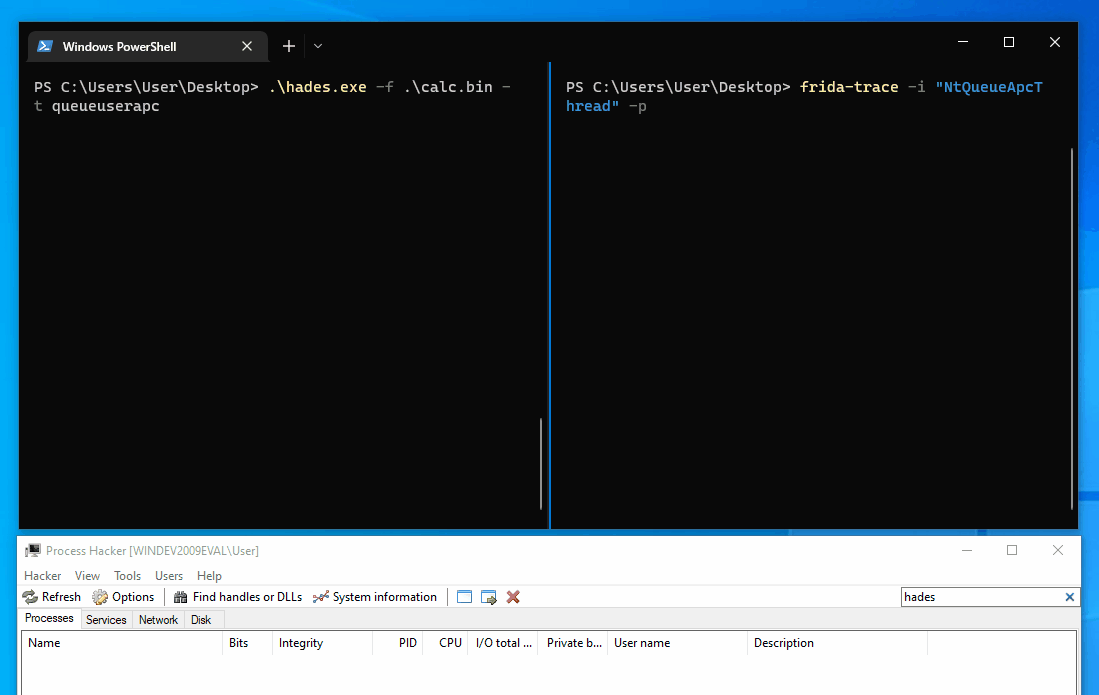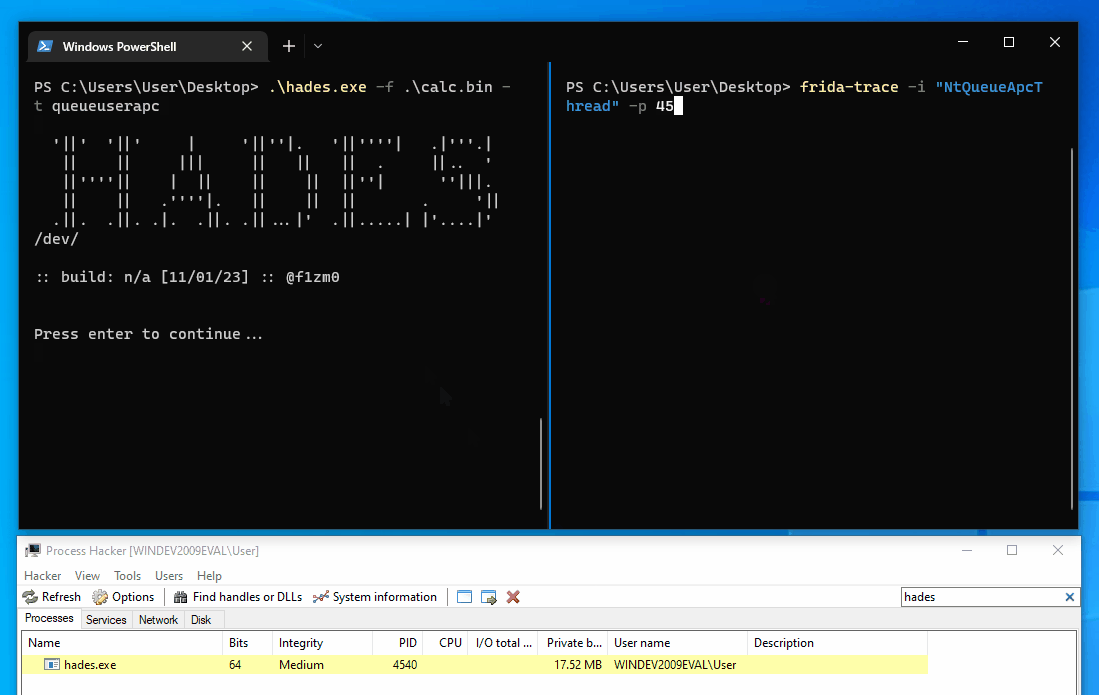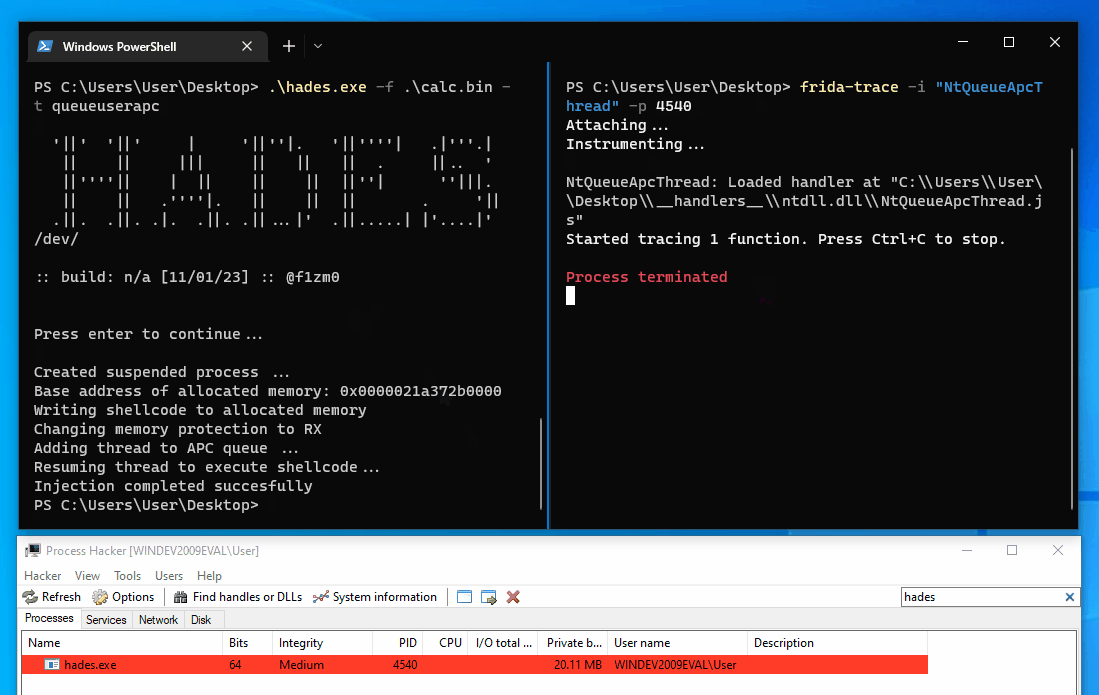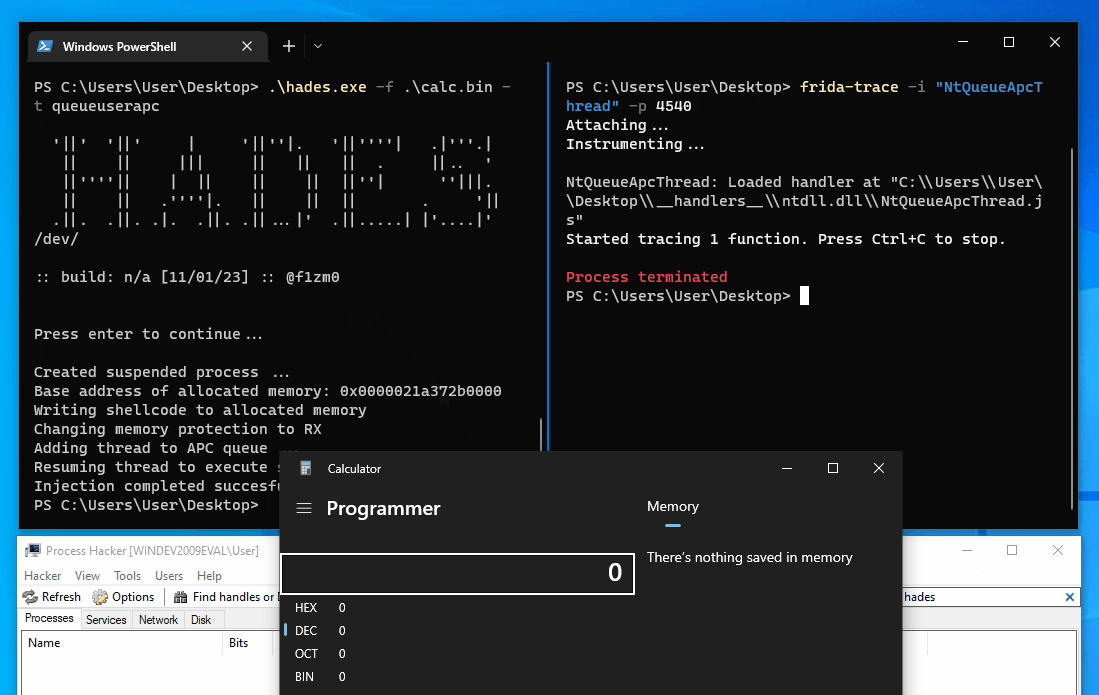 f1zm0/hades
Go shellcode loader that combines multiple evasion techniques
 elrajiii/cve-2025-5548
Buffer overflow in FreeFloat FTP Server 1.0
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.