
Chankro
 tarlogicsecurity/chankro
Herramienta para evadir disable_functions y open_basedir
exploitationpayload-developmentpenetration-testing+3
4957 years ago
tarlogicsecurity/chankroHerramienta para evadir disable_functions y open_basedir
 lepotekil/msfmania
Python AV Evasion Tools
 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
 preemptdev/bluffy
Convert shellcode into :sparkles: different :sparkles: formats!
 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
 0xninjacyclone/asmldr
Dynamic shellcode loader with sophisticated evasion capabilities
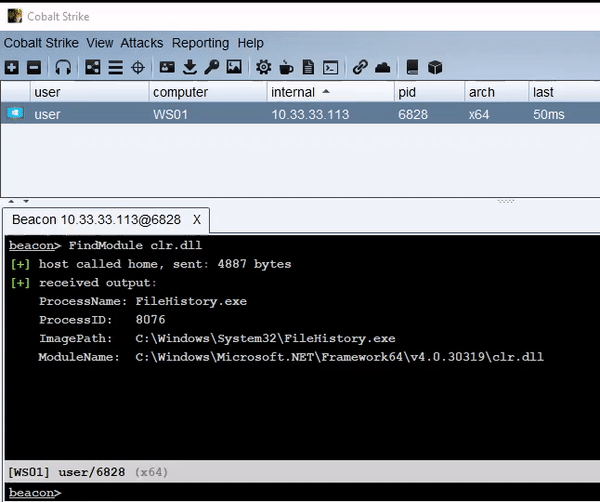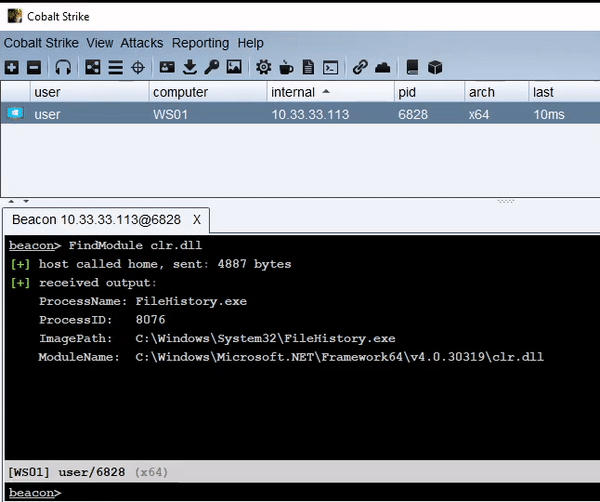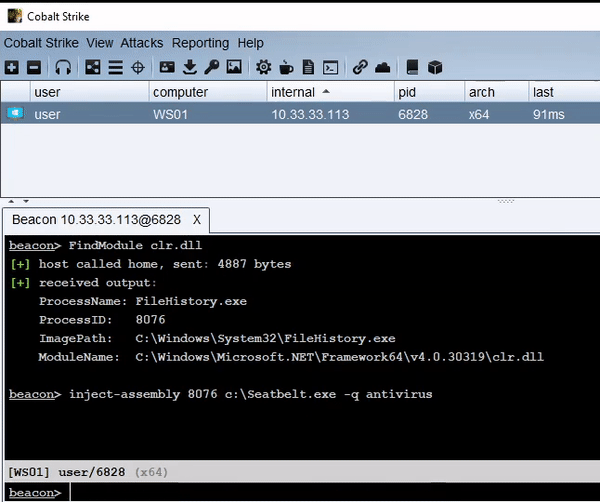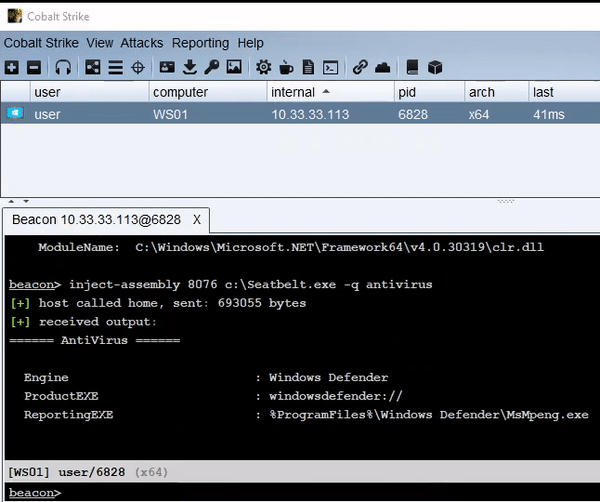 kyleavery/inject-assembly
Inject .NET assemblies into an existing process
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
 cryptolok/morphaes
IDPS & SandBox & AntiVirus STEALTH KILLER. MorphAES is the world's first polymorphic shellcode engine, with metamorphic properties and capability to…
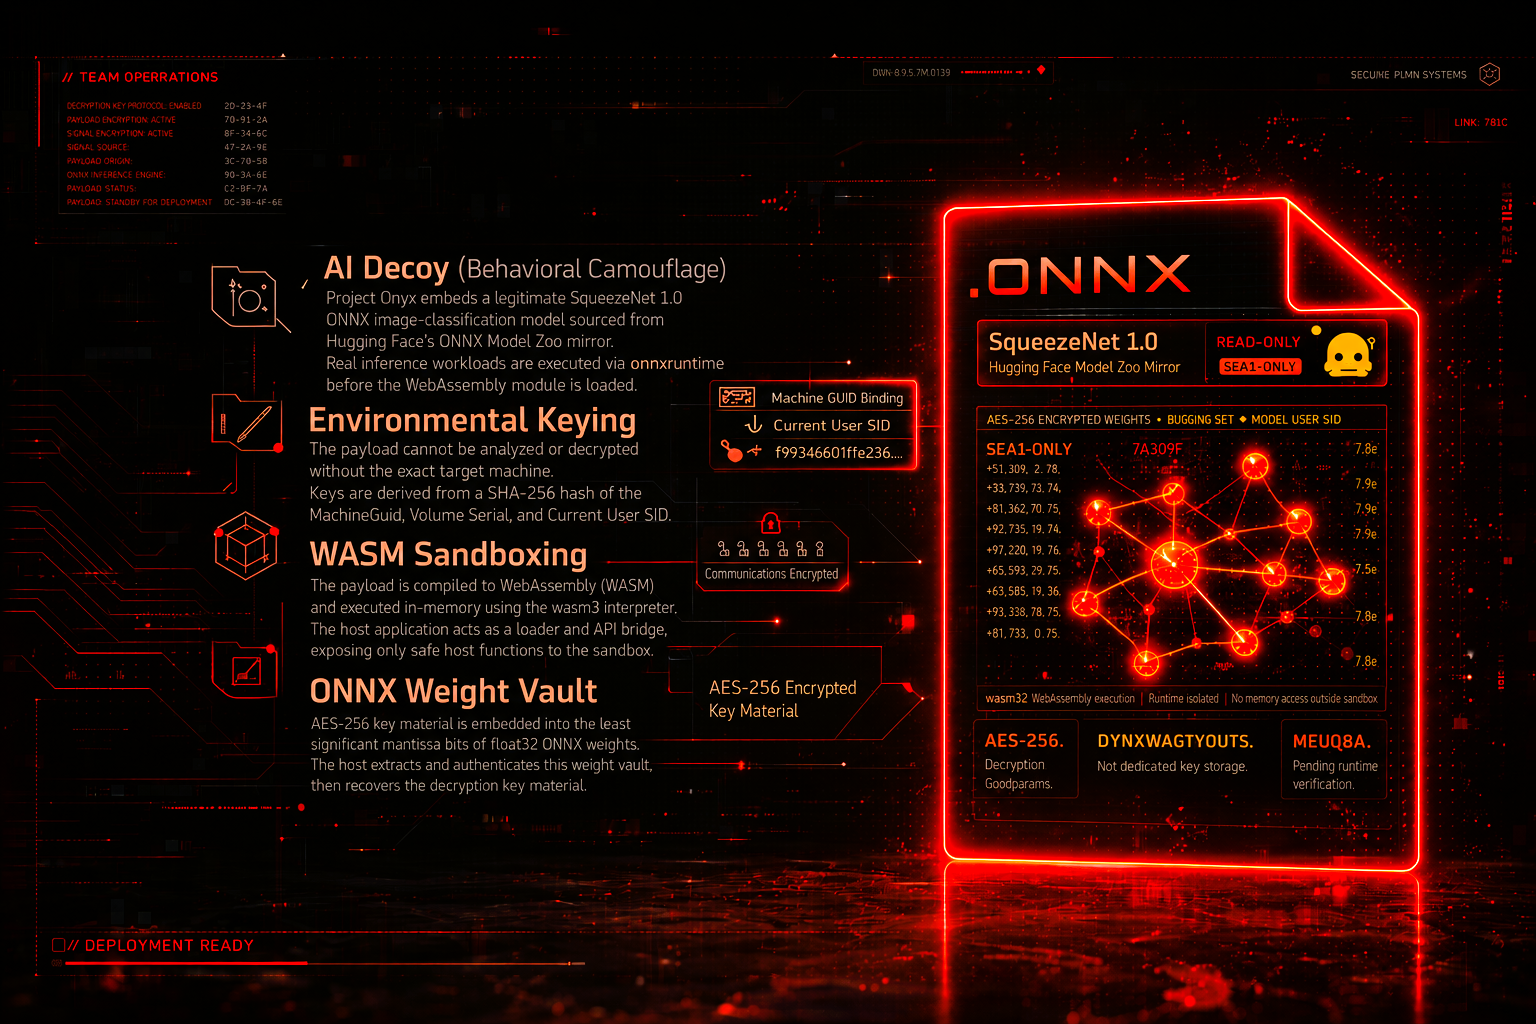 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
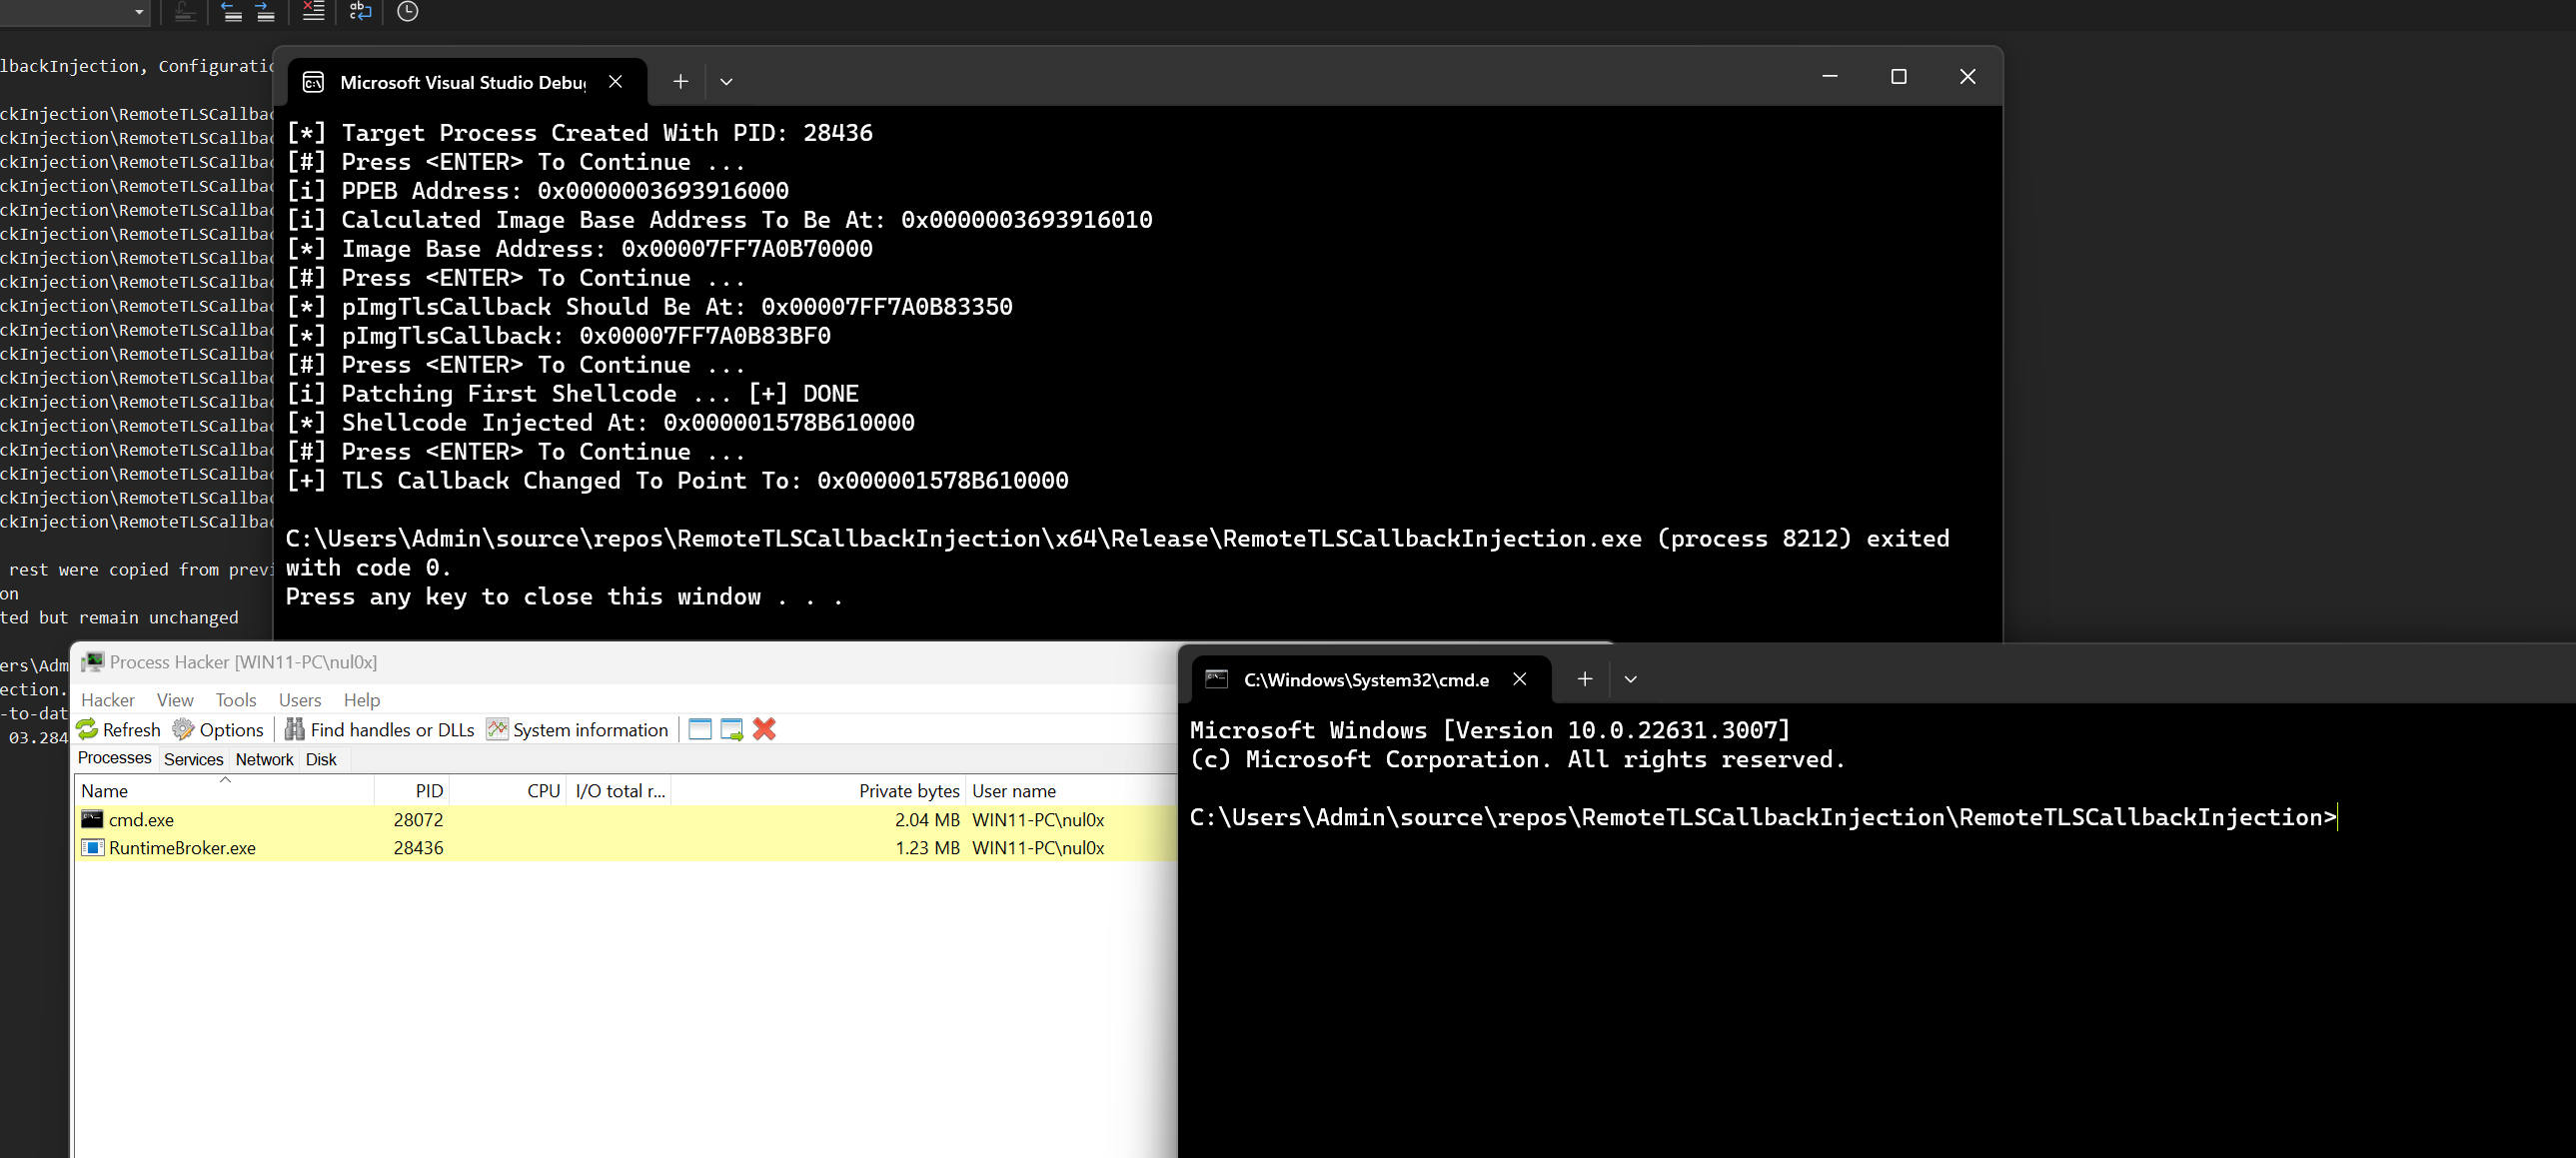 maldev-academy/remotetlscallbackinjection
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process
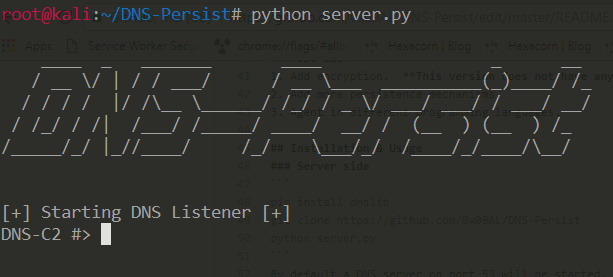 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
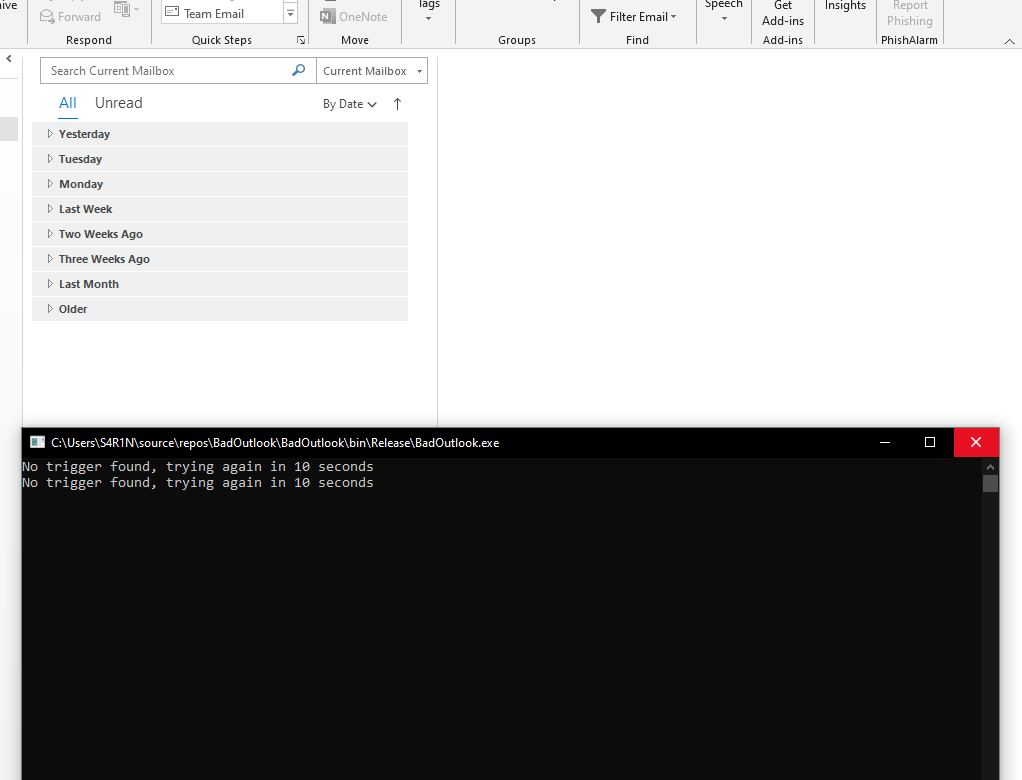 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
 winterknife/silverpick
Windows User-Mode Shellcode Development Framework (WUMSDF)
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
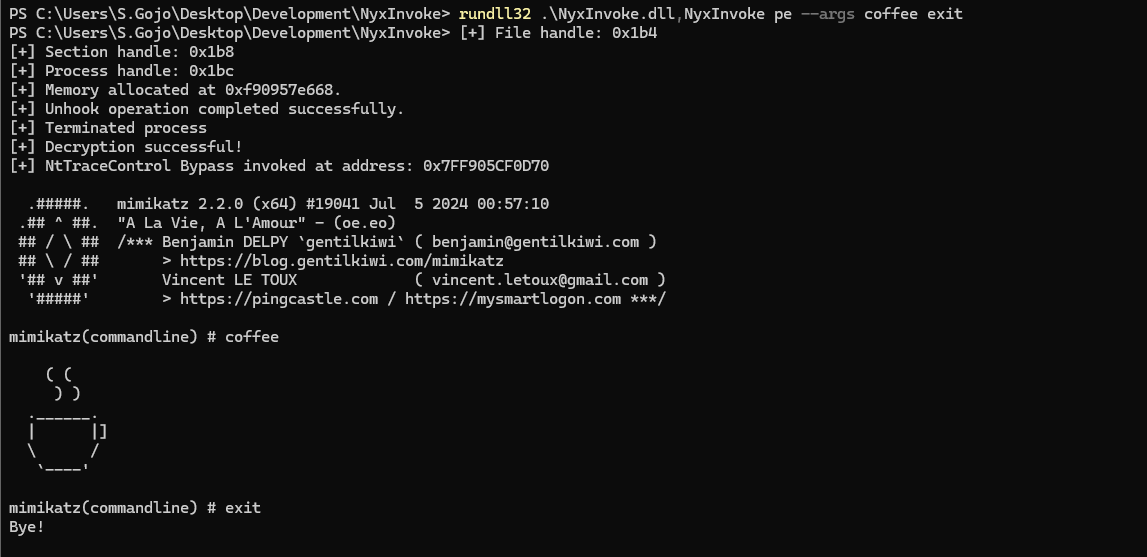 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support