

WebKit-Bug-256172
 wh1te4ever/webkit-bug-256172
Safari 1day RCE Exploit
binary-exploitationexploitationios-security+4
1671 year ago
wh1te4ever/webkit-bug-256172Safari 1day RCE Exploit
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 ariary/volana
🌒 Shell command obfuscation to avoid detection systems
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
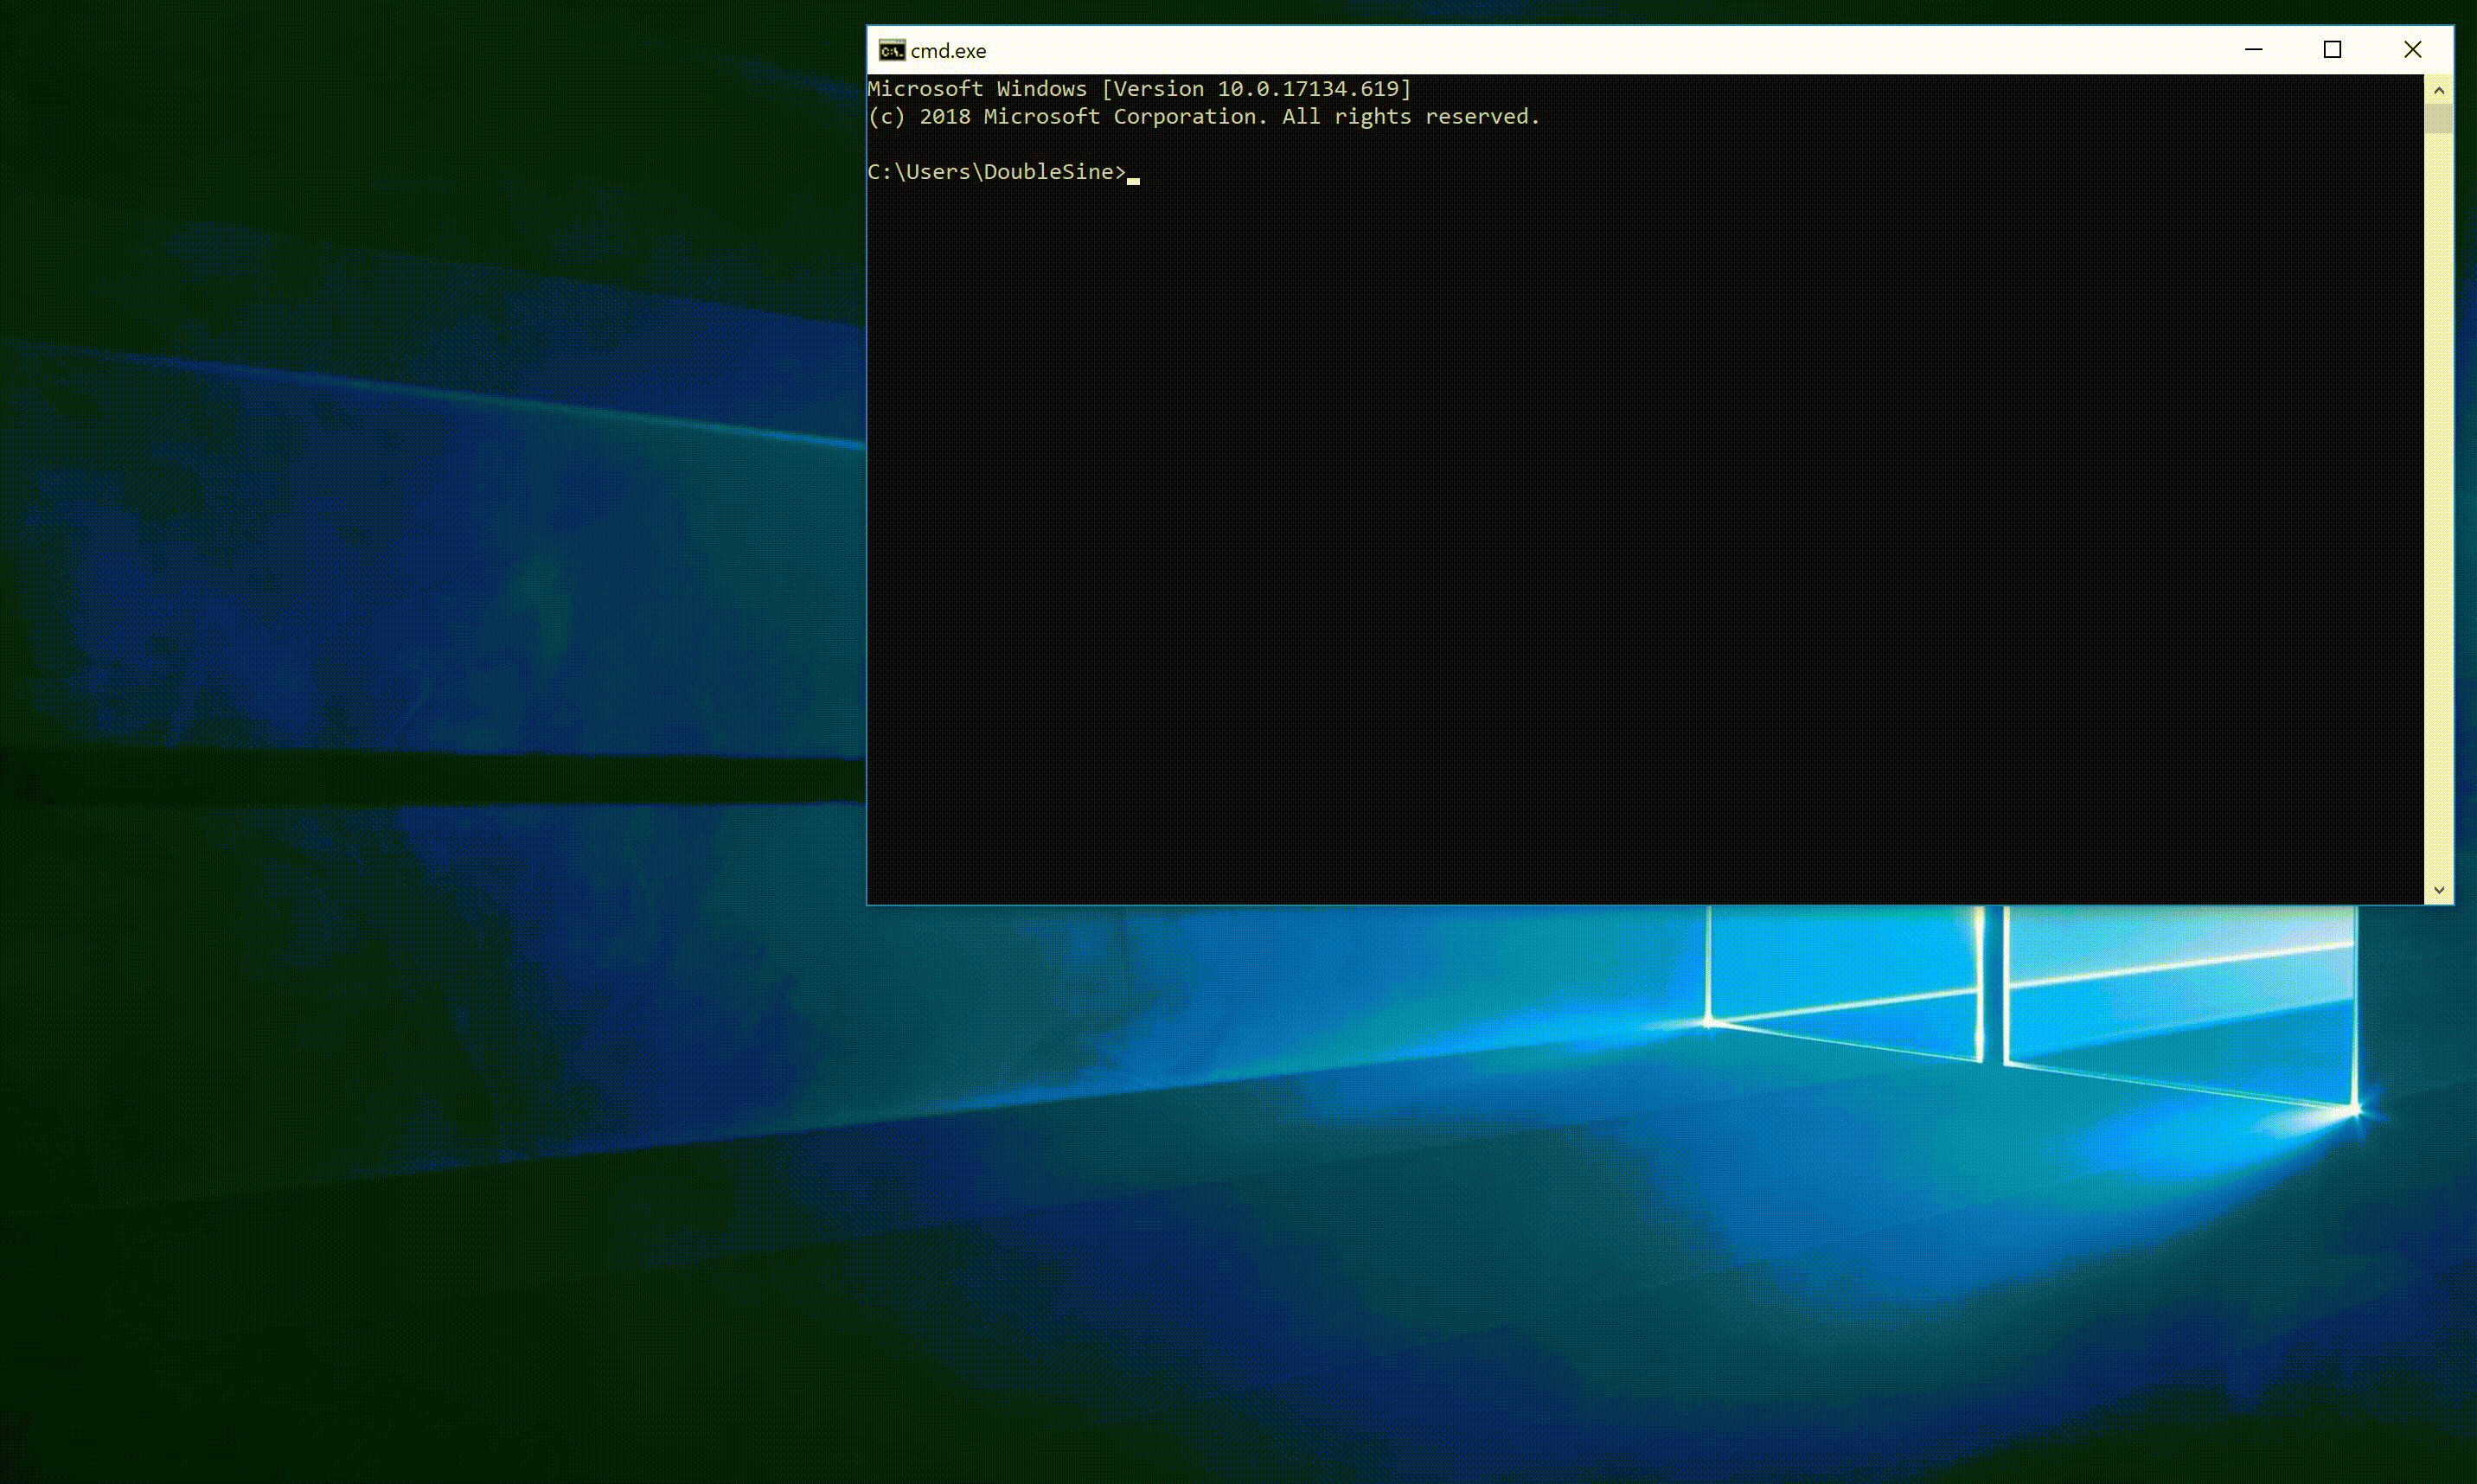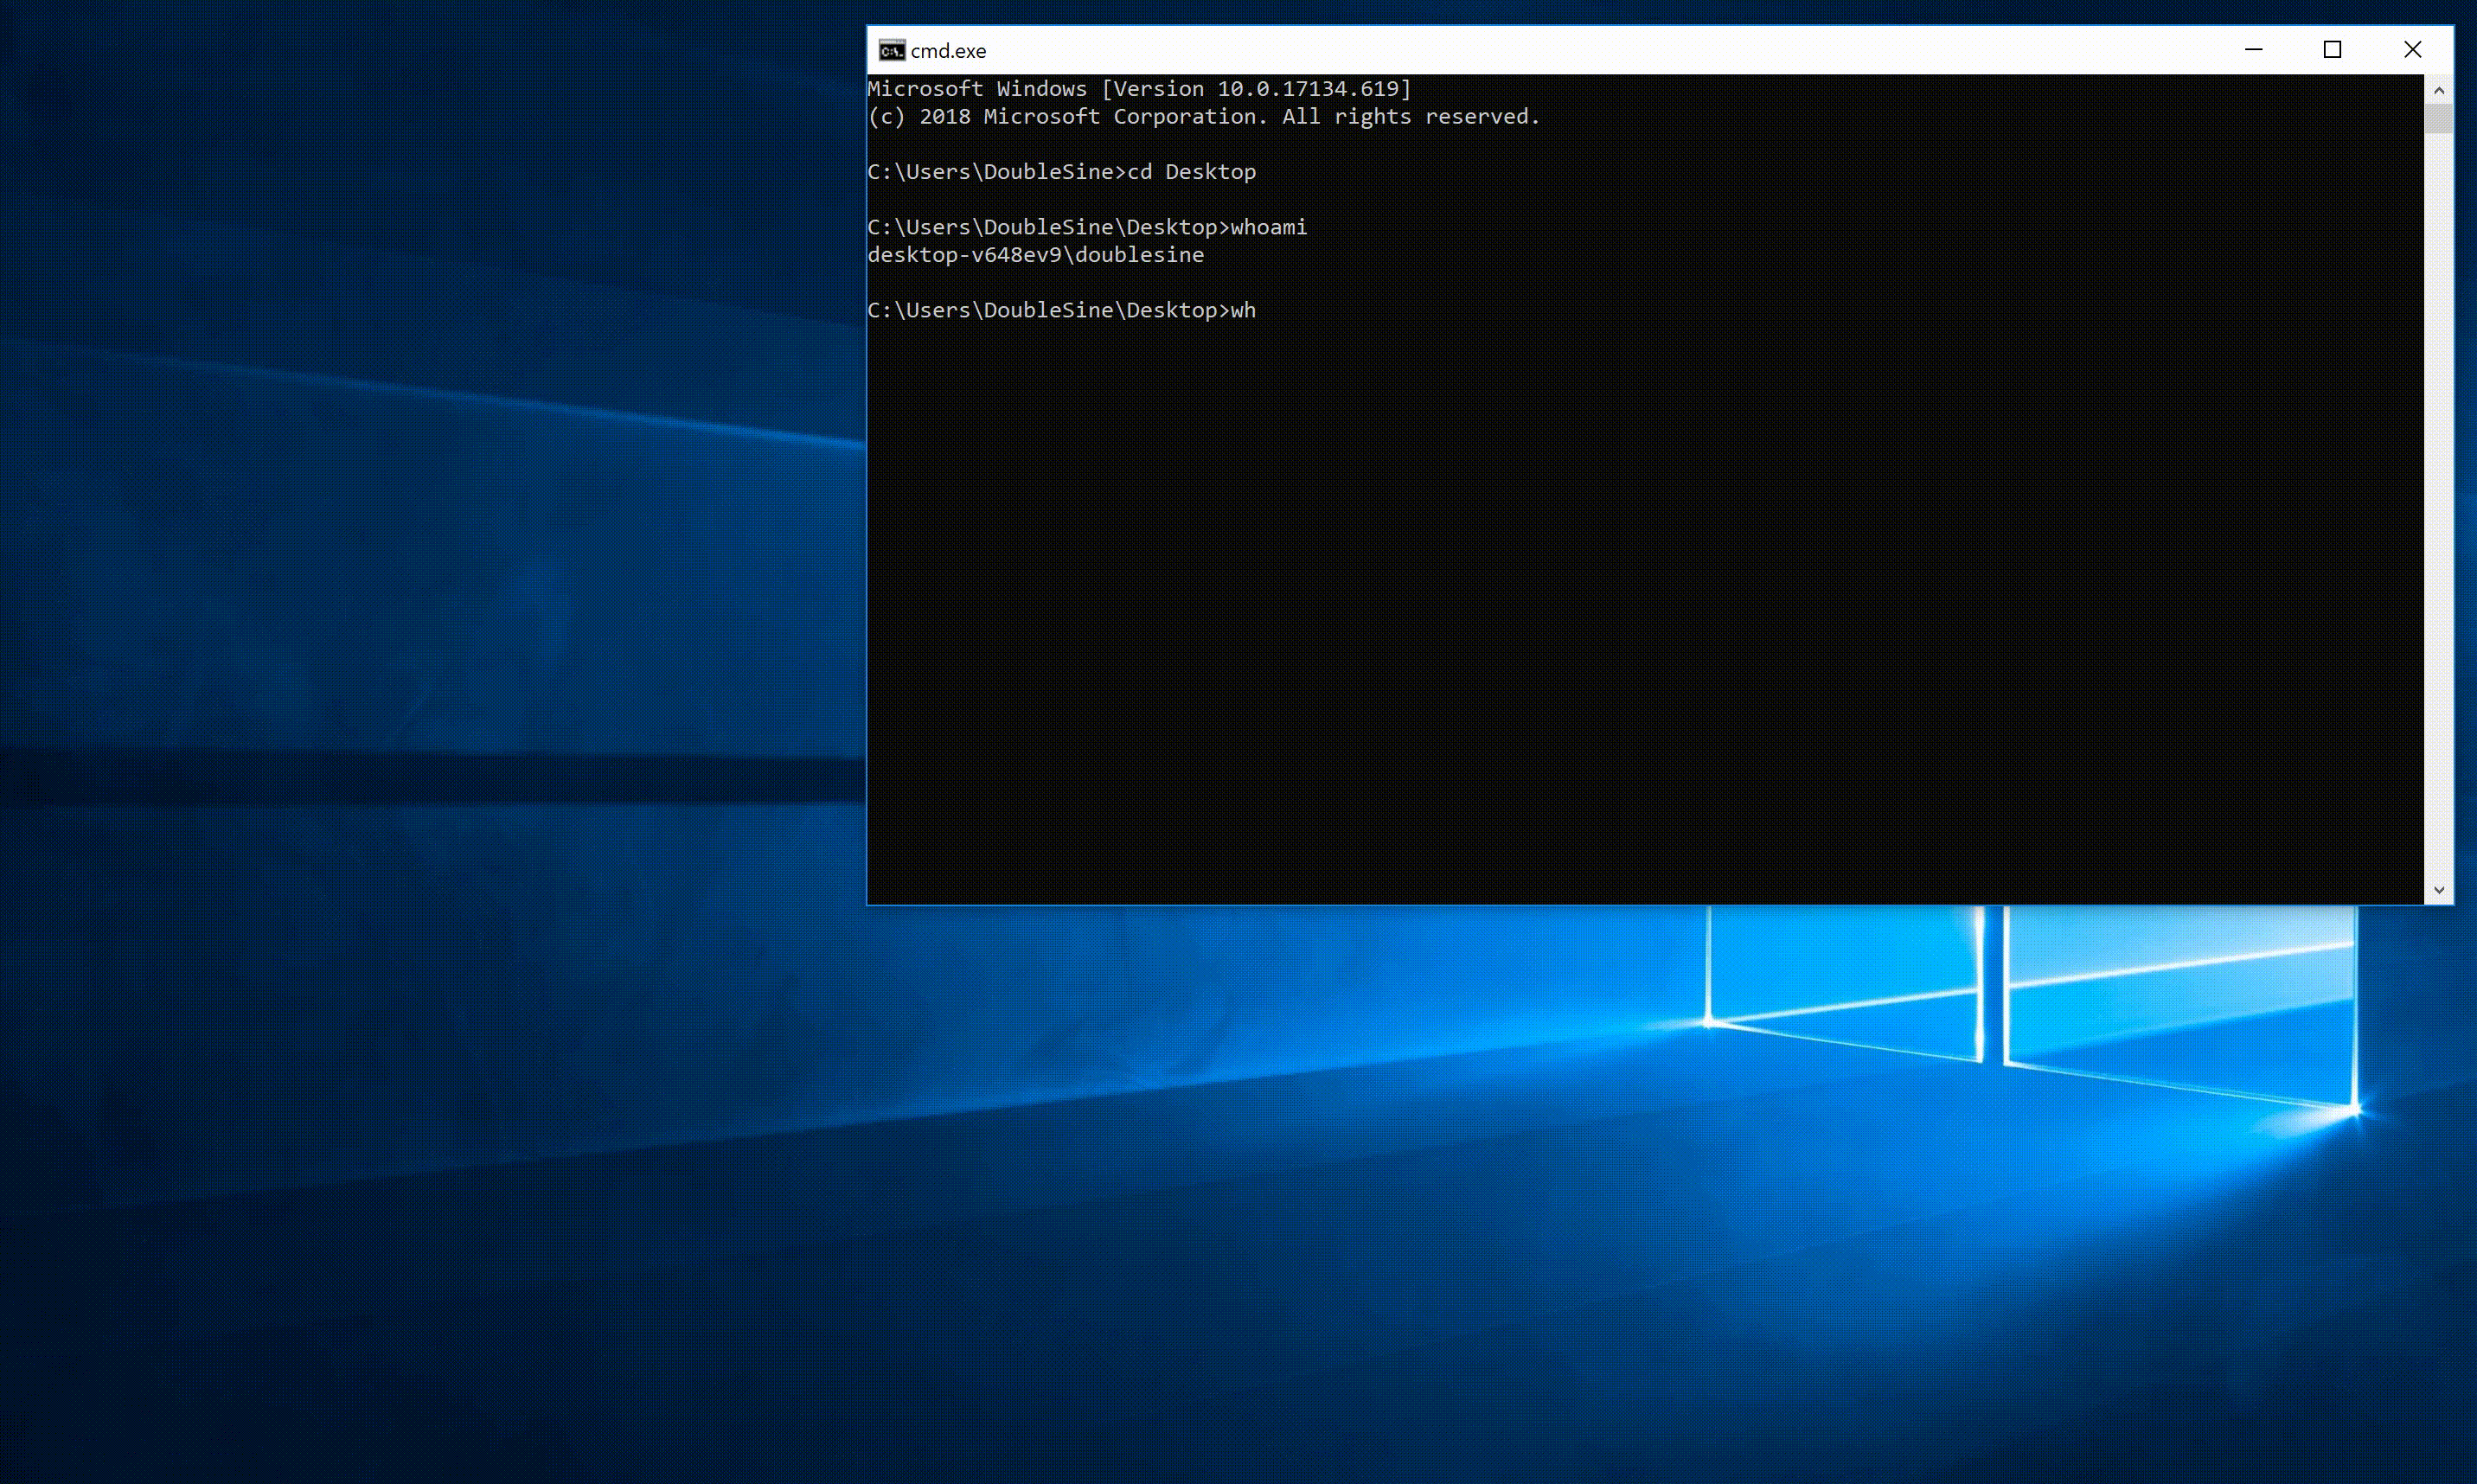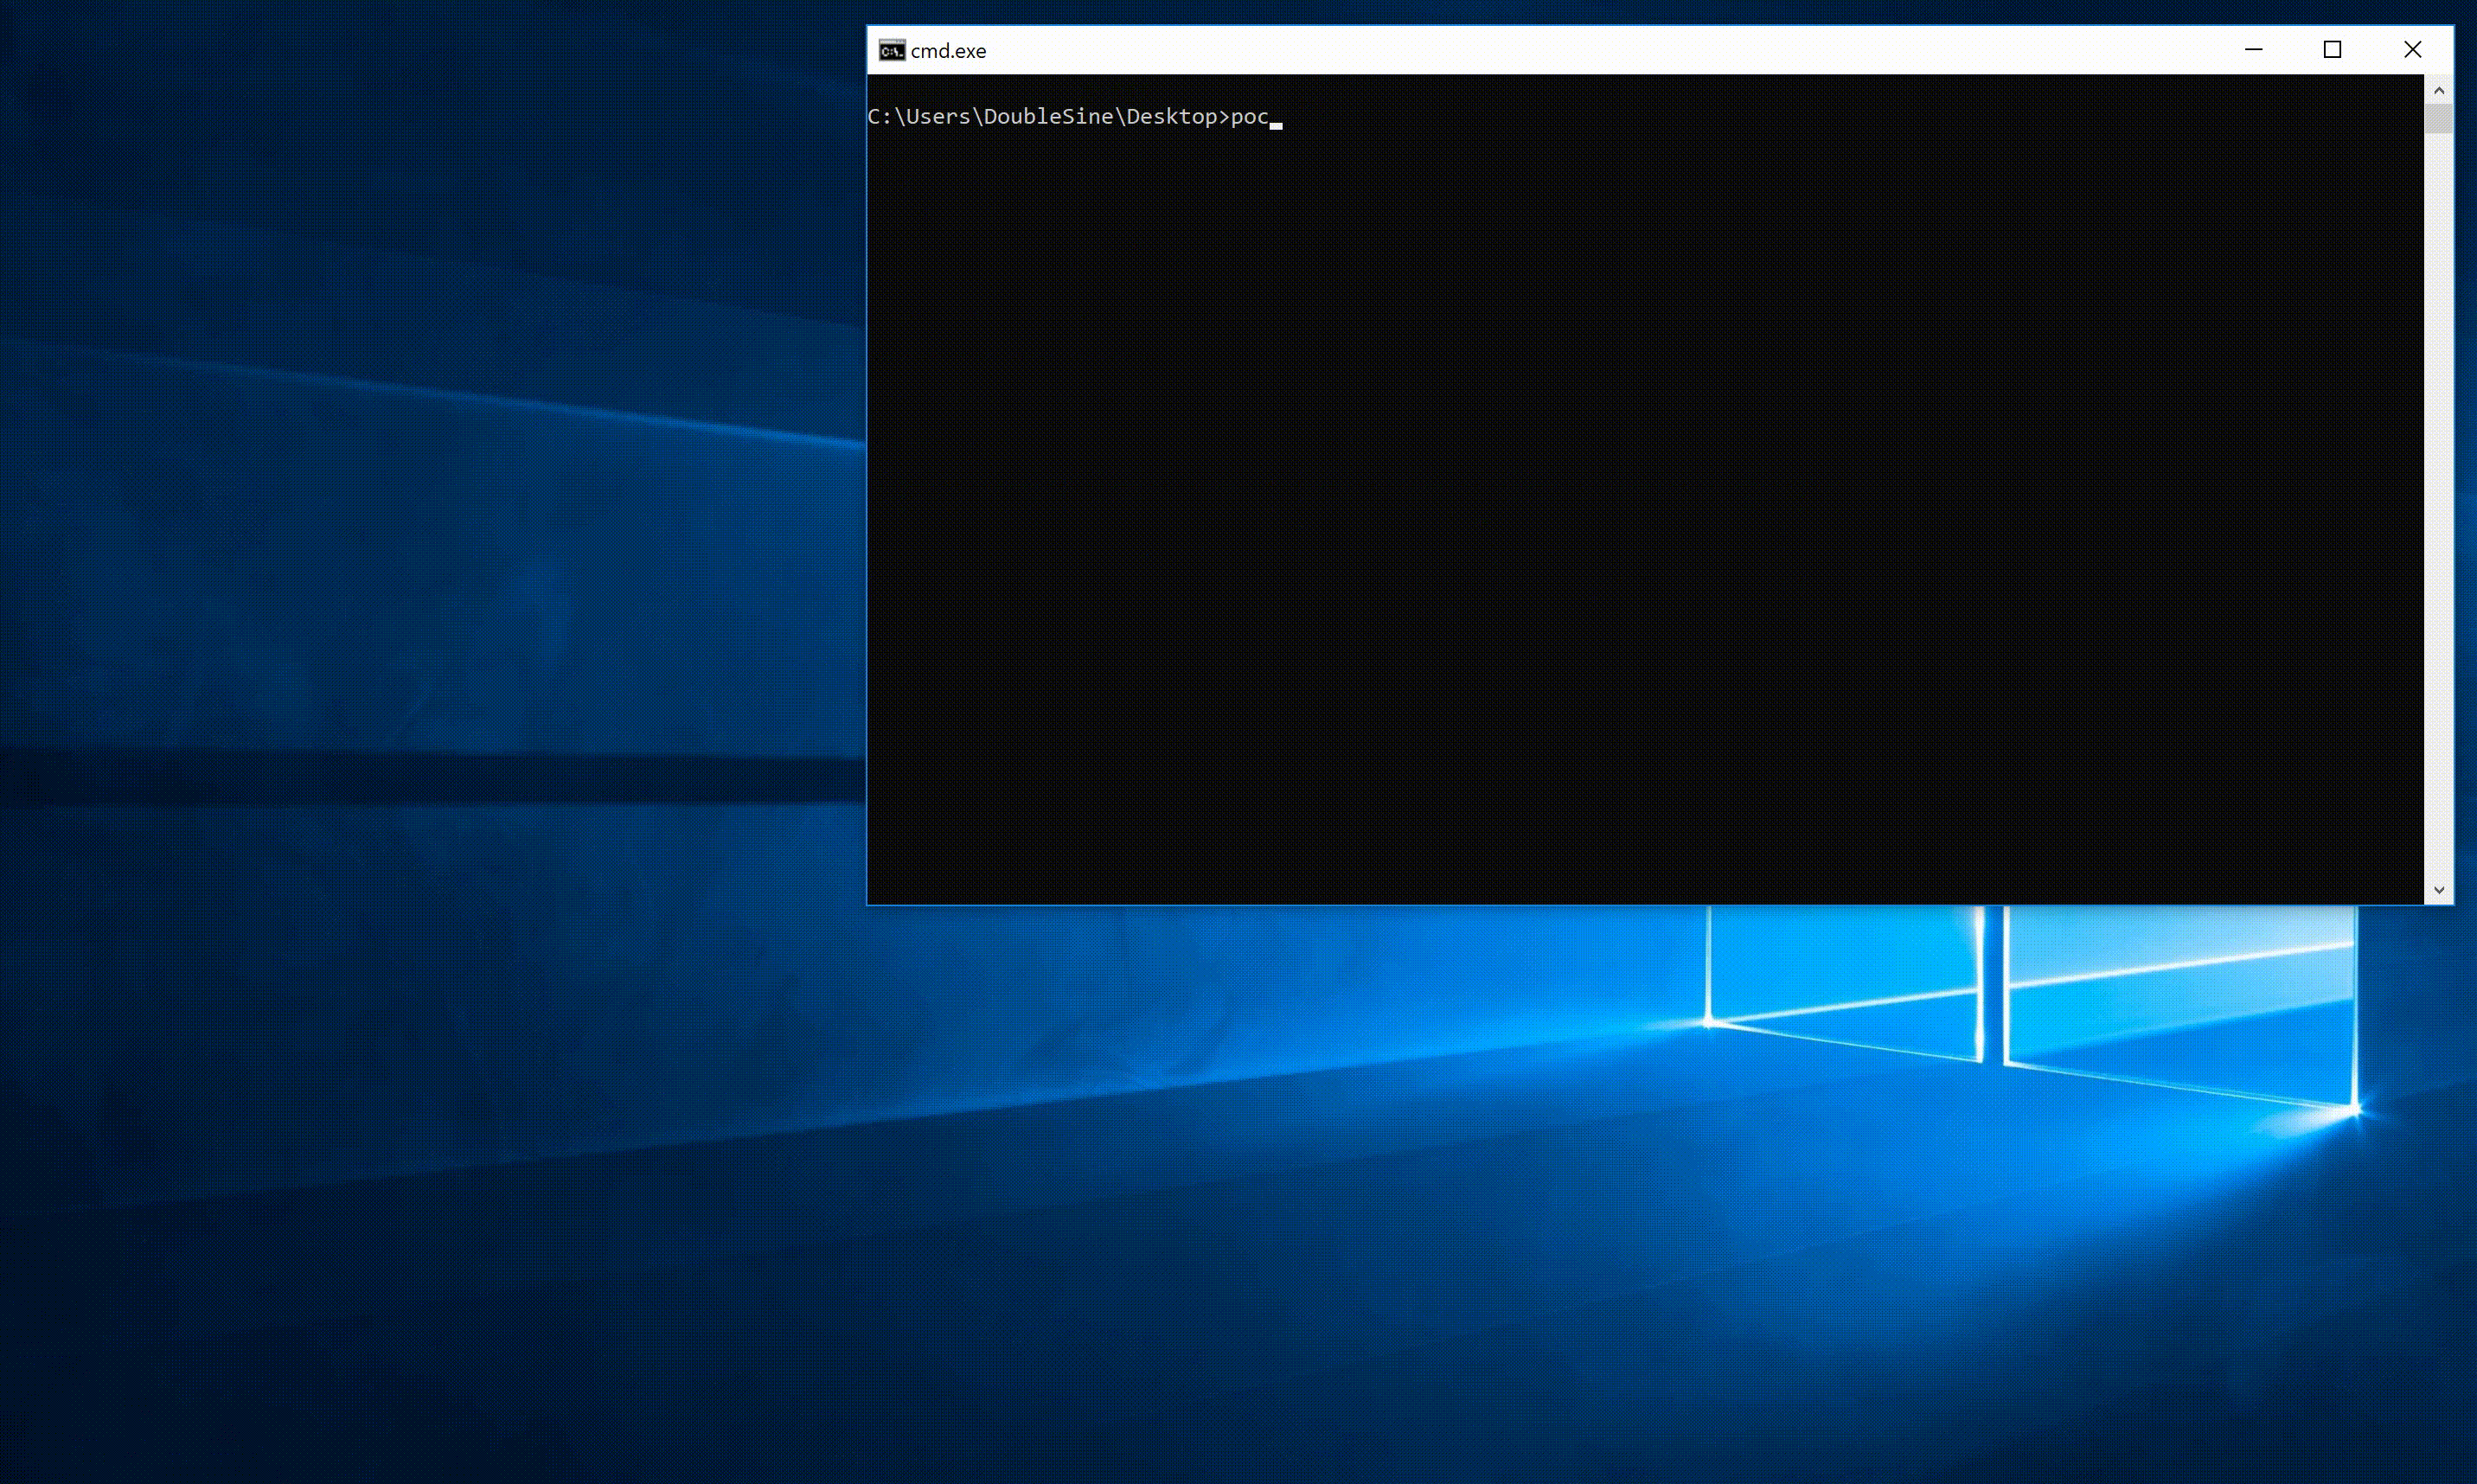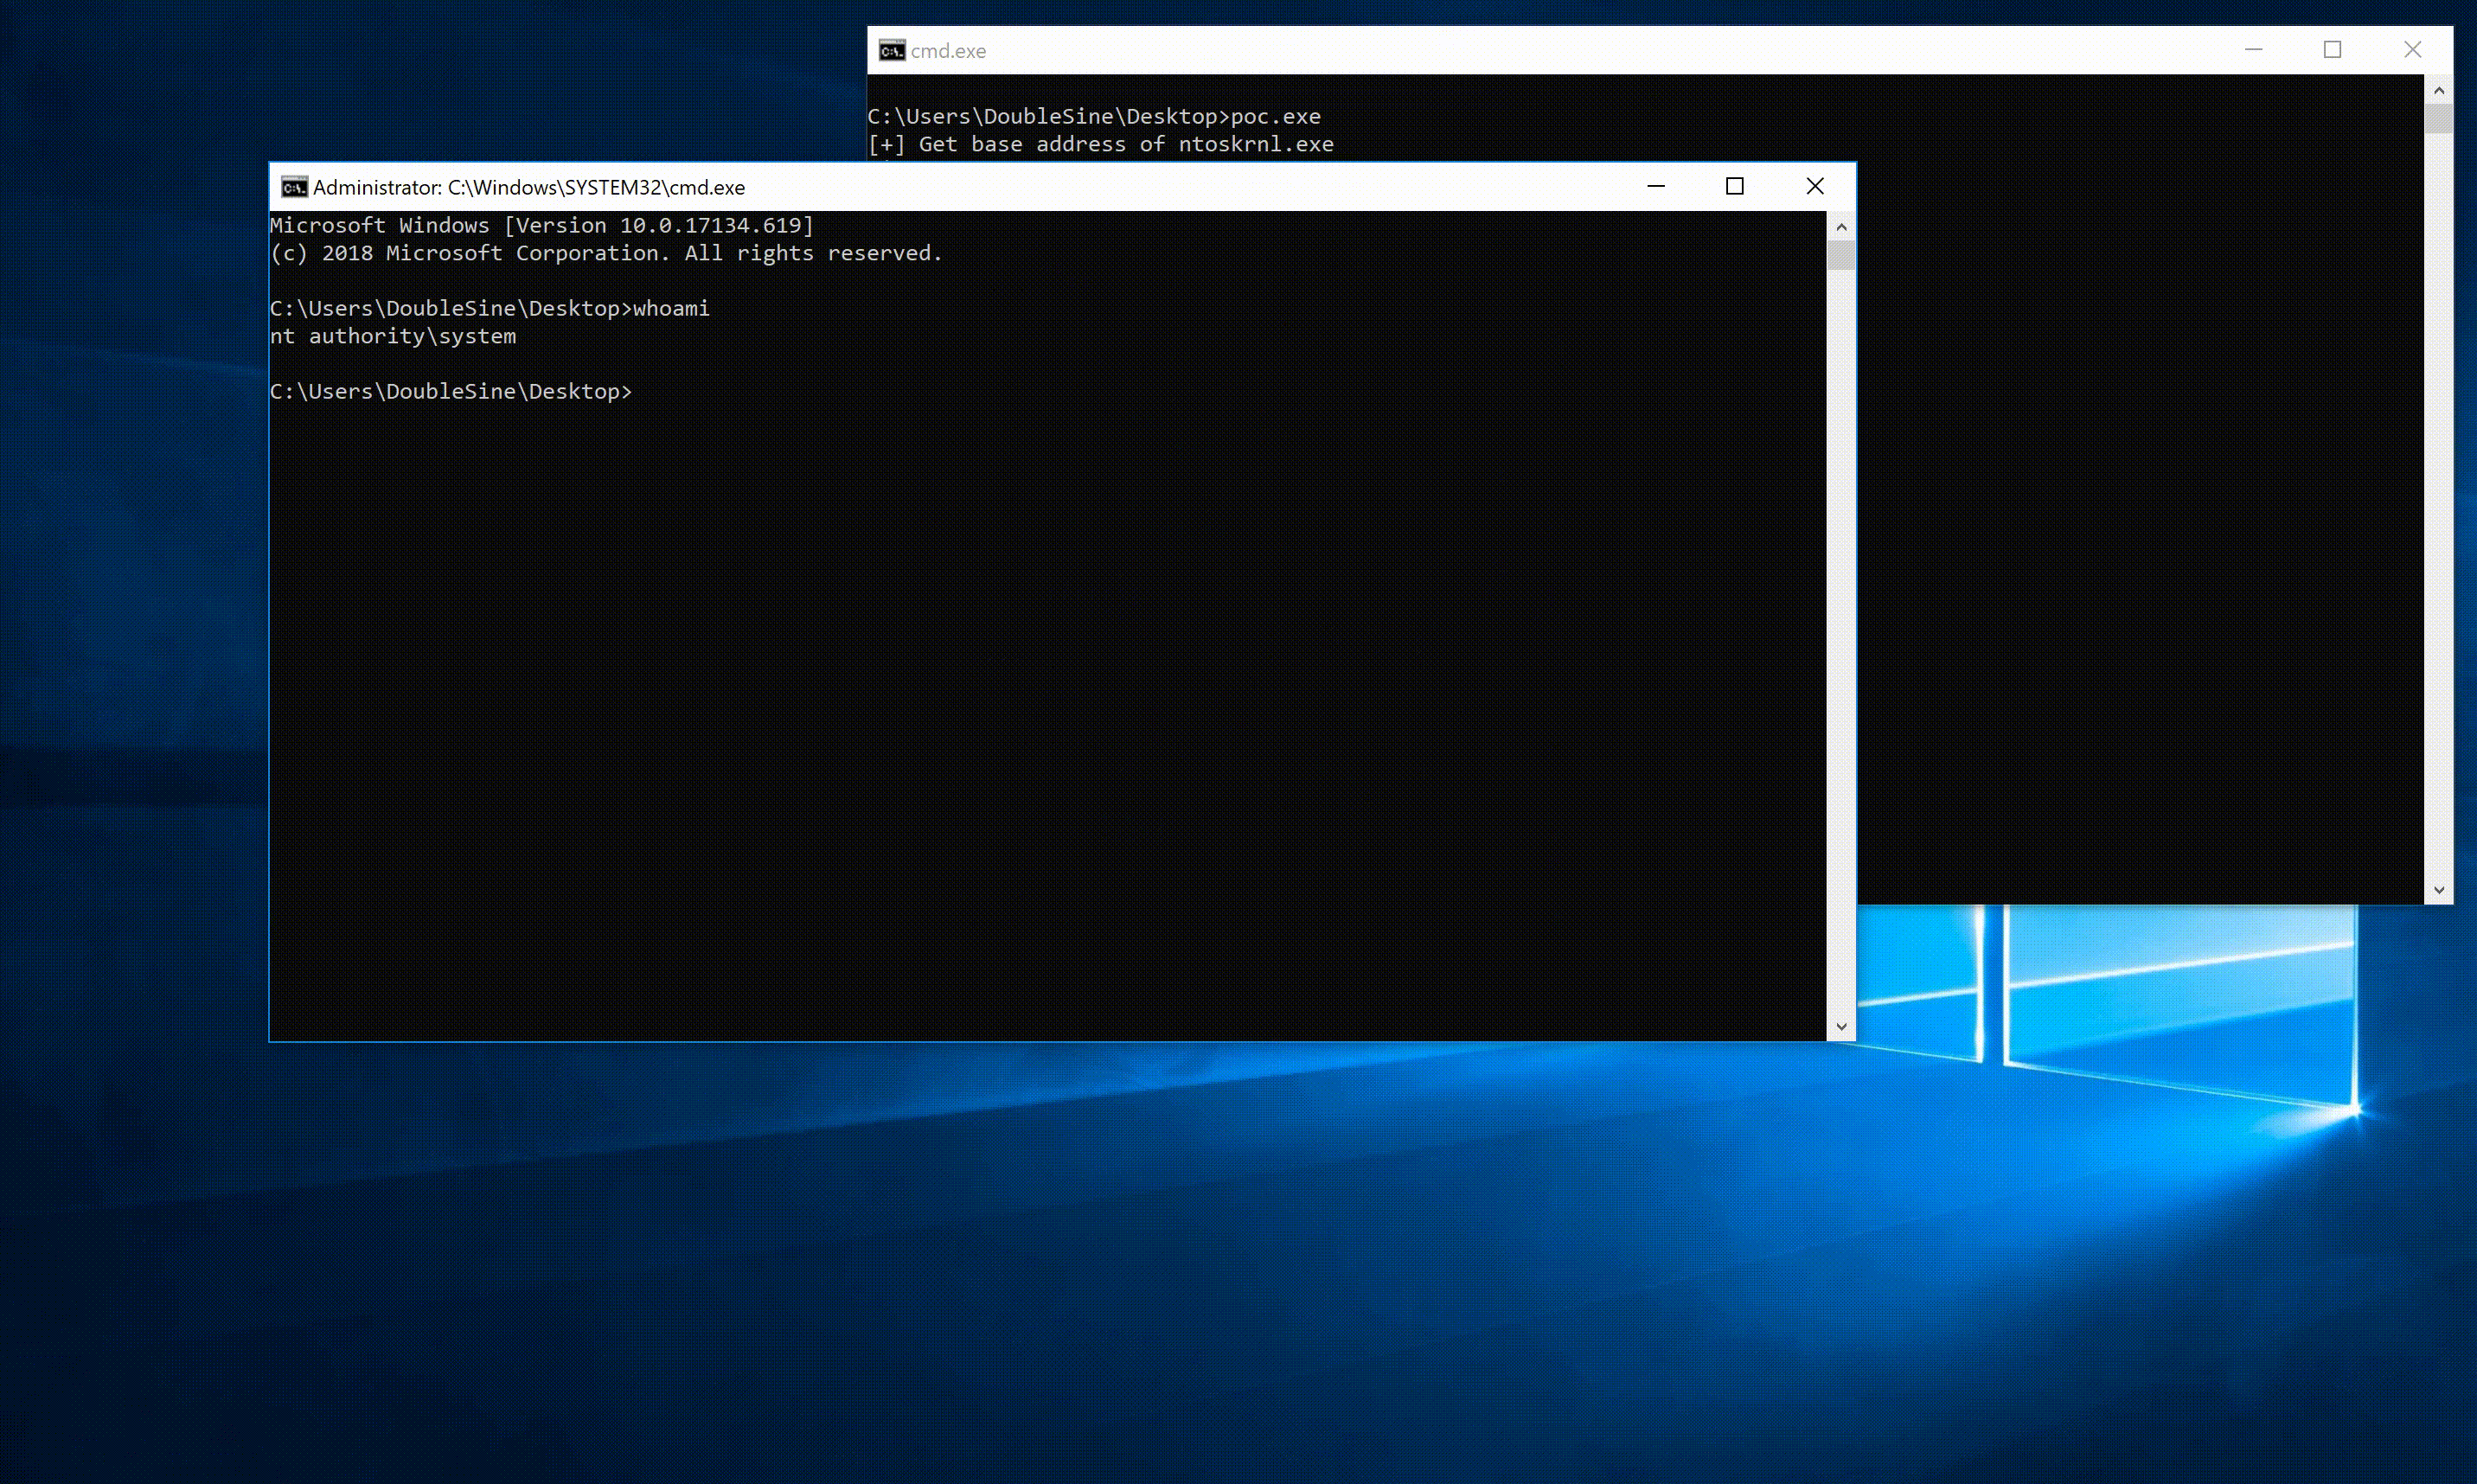 hypersine/sdokeycrypt-sys-local-privilege-elevation
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
 offsecginger/pythonaesobfuscate
Obfuscates a Python Script and the accompanying Shellcode.
 intrinsic-propensity/turing-machine
Python implementation of Minsky's Universal Turing Machine with a built-in exploit demonstrating arbitrary code execution (CVE-2021-32471) for…
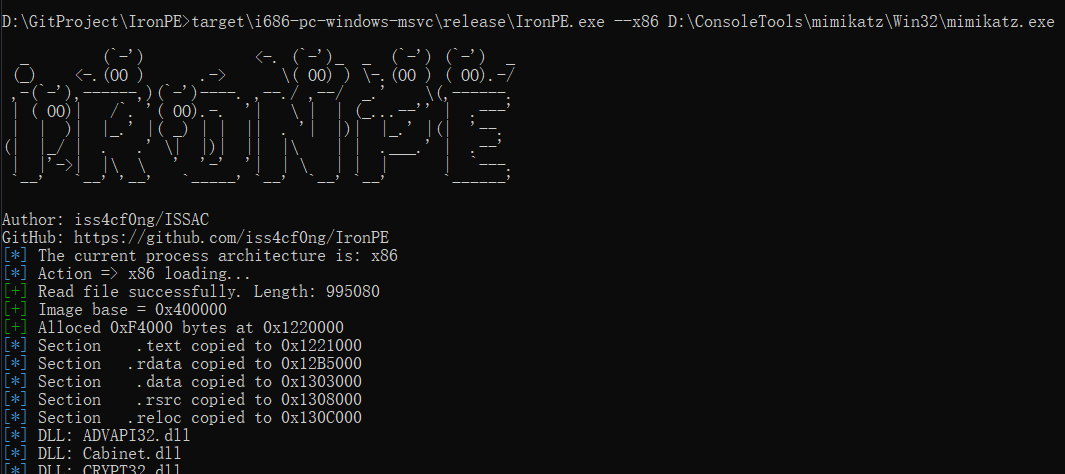 iss4cf0ng/ironpe
Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
 0xdea/shellcode
A collection of my shellcode samples.
 0xsha/cve-2026-6307
Google Chrome CVE-2026-6307 PoC

 maxpl0it/cve-2019-17026-exploit
An exploit for CVE-2019-17026. It pops xcalc and was tested on Ubuntu (x64).
 p33d/cve-2024-45519
SMTP vulnerability scanner and exploit script that checks for CVE-2024-45519 and establishes a reverse shell on vulnerable servers.
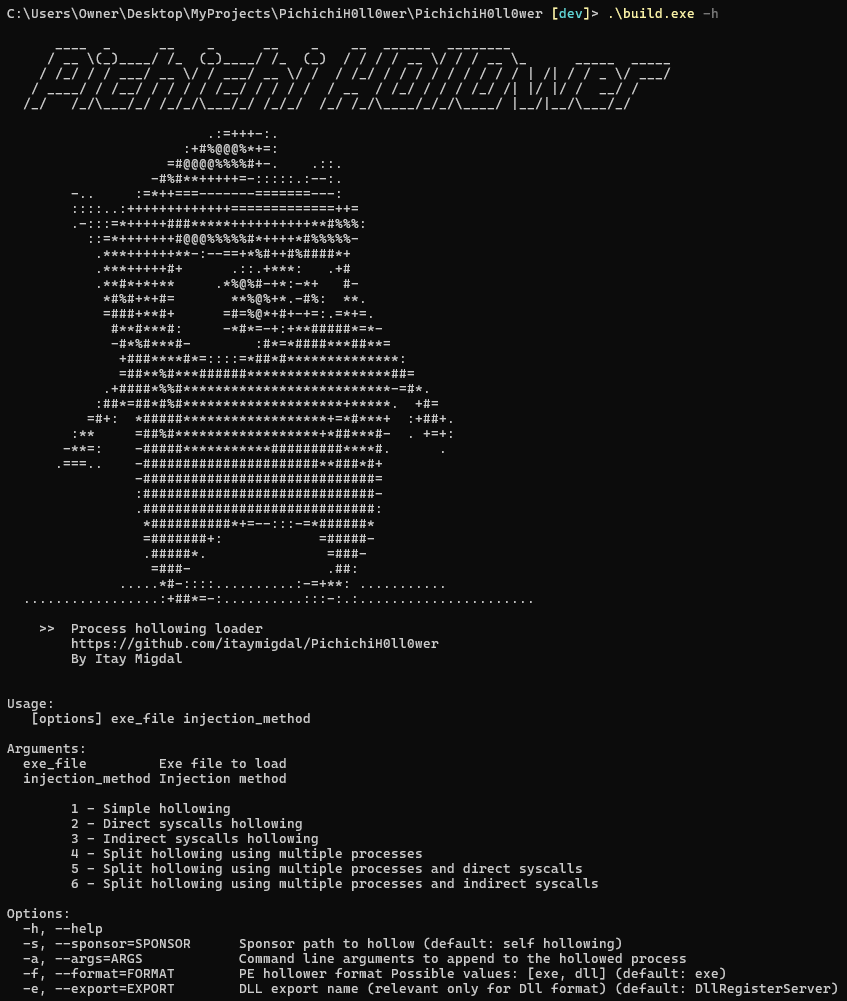 itaymigdal/pichichih0ll0wer
Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 chaelsoo/nimcrypt
Nim-based encryption tool for obfuscating shellcode and payloads for evading Windows Defender.