metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

CTF framework and exploit development library

Some setup scripts for security research tools.

Adversary Emulation Framework

K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…

Windows memory hacking library

Merlin is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in golang.

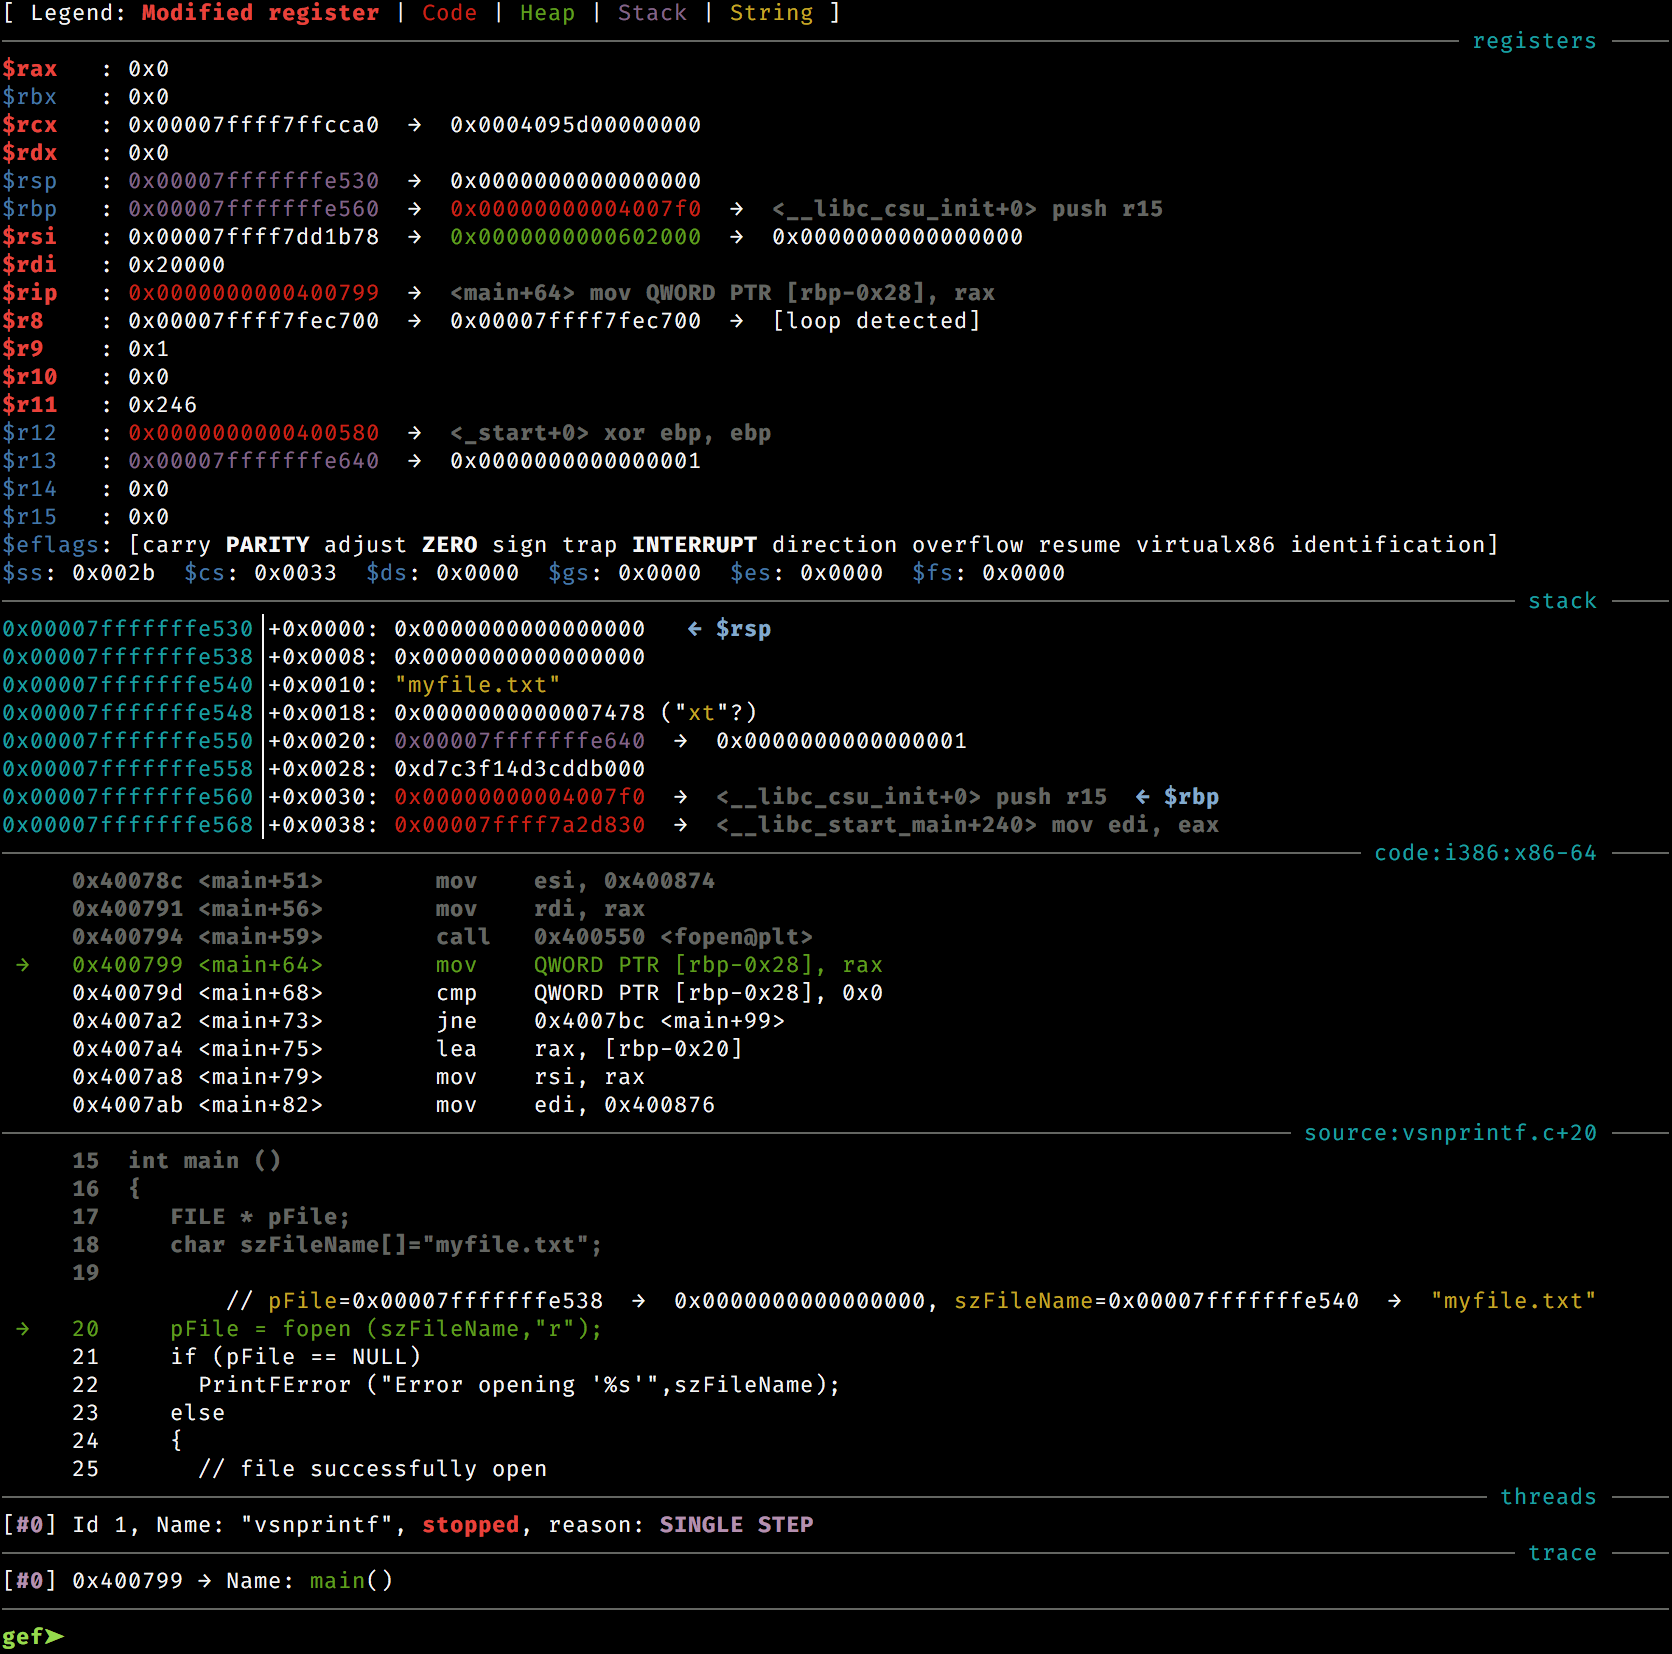
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux

Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)

Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Unified repository for different Metasploit Framework payloads

PEDA - Python Exploit Development Assistance for GDB

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…

My experiments in weaponizing Nim (https://nim-lang.org/)

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode