

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Shellcode — Tools — Page 5 | Kitploit

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
404 results
glimmer preview

glimmer

GitHublinnemanlabs/glimmer

Adversary emulation and C2 framework for security research

penetration-testing-frameworkspersistence-mechanismsids-ips-evasion+8
5
5 months ago
FUD-C2-Framework preview

FUD-C2-Framework

GitHubx3r0day/fud-c2-framework

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

encryption-decryption-toolspersistence-mechanismsids-ips-evasion+9
75 months ago
reverse-shell-generator preview

reverse-shell-generator

GitHub0dayctf/reverse-shell-generator

Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
payload-generationexploitationshellcode+6
4.0k5 months ago
ropr preview

ropr

GitHubben-lichtman/ropr

A blazing fast™ multithreaded ROP Gadget finder. ropper / ropgadget alternative (currently x86 only)

exploitationreverse-engineeringshellcode+1
5555 months ago
micr0_shell preview

micr0_shell

GitHubsenzee1984/micr0_shell

micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
payload-generationexploitationshellcode+2
2226 months ago
Astral_Projection preview

Astral_Projection

GitHubkuwaitist/astral_projection

Cobalt Strike UDRL that performs advanced module stomping using VEH to intercept calls, unmap modules during sleep, and remap fresh modules to evade…

penetration-testing-frameworksexploit-frameworksmemory-forensics+4
726 months ago
libpeconv preview

libpeconv

GitHubhasherezade/libpeconv

Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…

memory-forensicsreverse-engineeringshellcode+4
1.4k6 months ago
SynthAPT preview

SynthAPT

GitHubacedef/synthapt

Playbook-based adversary simulation framework that compiles JSON-defined attack paths into position-independent shellcode payloads for validating…

penetration-testing-frameworksprivilege-escalationexploit-frameworks+8
2316 months ago
win32k-callback-detouring preview

win32k-callback-detouring

GitHubn0qword/win32k-callback-detouring

Abusing the win32k.sys kernel callback mechanism for arbitrary code execution
exploitationshellcodepost-exploitation+3
1086 months ago
Shoggoth preview

Shoggoth

GitHubfrkngksl/shoggoth

Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
exploit-frameworkspayload-generationshellcode+2
8056 months ago
HintInject preview

HintInject

GitHubfrkngksl/hintinject

A PoC project for embedding shellcode to Hint/Name Table

payload-generationexploitationshellcode+3
1146 months ago
Loki preview

Loki

GitHubboku7/loki

🧙‍♂️ Node.js Command & Control for Script-Jacking Vulnerable Electron Applications

persistence-mechanismsexploitationids-ips-evasion+5
1.4k6 months ago
sharem preview

sharem

GitHubbw3ll/sharem

SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
dynamic-analysis-sandboxingreverse-engineeringshellcode+5
4917 months ago
CustomLoadImage preview

CustomLoadImage

GitHubbackdoorskid/customloadimage

Stealthy .NET assembly loading using AssemblyNative::LoadFromBuffer
defensive-toolsexploitationshellcode+3
587 months ago
CVE-2025-5548 preview

CVE-2025-5548

GitHubanasrami12/cve-2025-5548

Methodology for vulnerability analysis and exploit development, covering static/dynamic analysis, fuzzing, patch diffing, and 0-day research with…
vulnerability-analysisexploitationreverse-engineering+8
7 months ago
metasm preview

metasm

GitHubjjyg/metasm

This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
code-analysisreverse-engineeringshellcode+2
4757 months ago
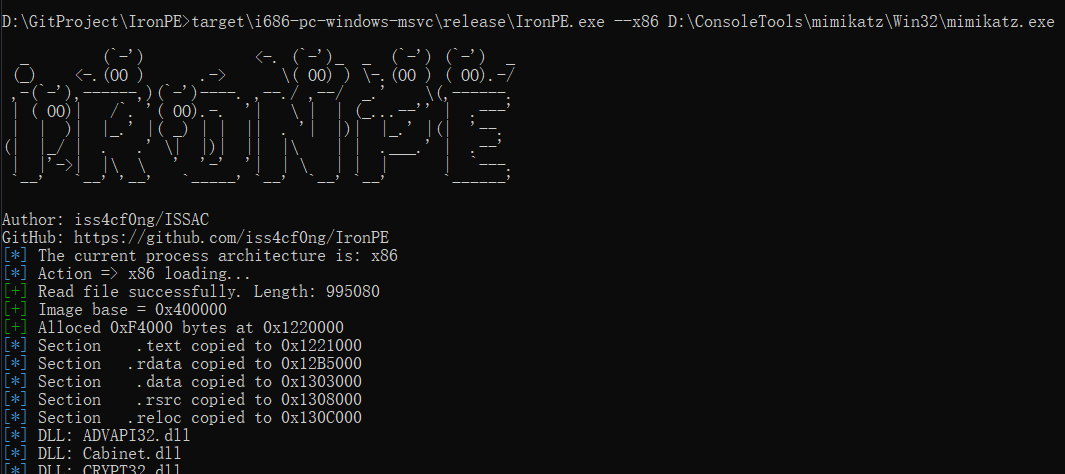
IronPE preview

IronPE

GitHubiss4cf0ng/ironpe

Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
memory-forensicsexploitationreverse-engineering+5
1247 months ago
ASPX_WebShell_COFFLoader preview

ASPX_WebShell_COFFLoader

GitHubepotseluevskaya/aspx_webshell_coffloader

ASPX web shell with COFF loader for executing Beacon Object Files (BOFs) on target servers via a semi-interactive Python client, designed for…

shellcodeweb-application-exploitationpenetration-testing+3
1347 months ago
Previous1…456…23Next