

ICALL-GADGET
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
binary-exploitationexploitationids-ips-evasion+5
1
gmh5225/icall-gadgetExploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 ntfargo/relapse-exploit
PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
 sneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.
Chained Chrome V8 renderer escape proof-of-concept exploiting four CVEs: Float64Array corruption, Wasm overwrite, popup navigation retargeting, and…
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
 solomonsklash/sleepycrypt
A shellcode function to encrypt a running process image when sleeping.
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 secforce/sharpwhispers
C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
 lloydlabs/ntqueueapcthreadex-ntdll-gadget-injection
This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…
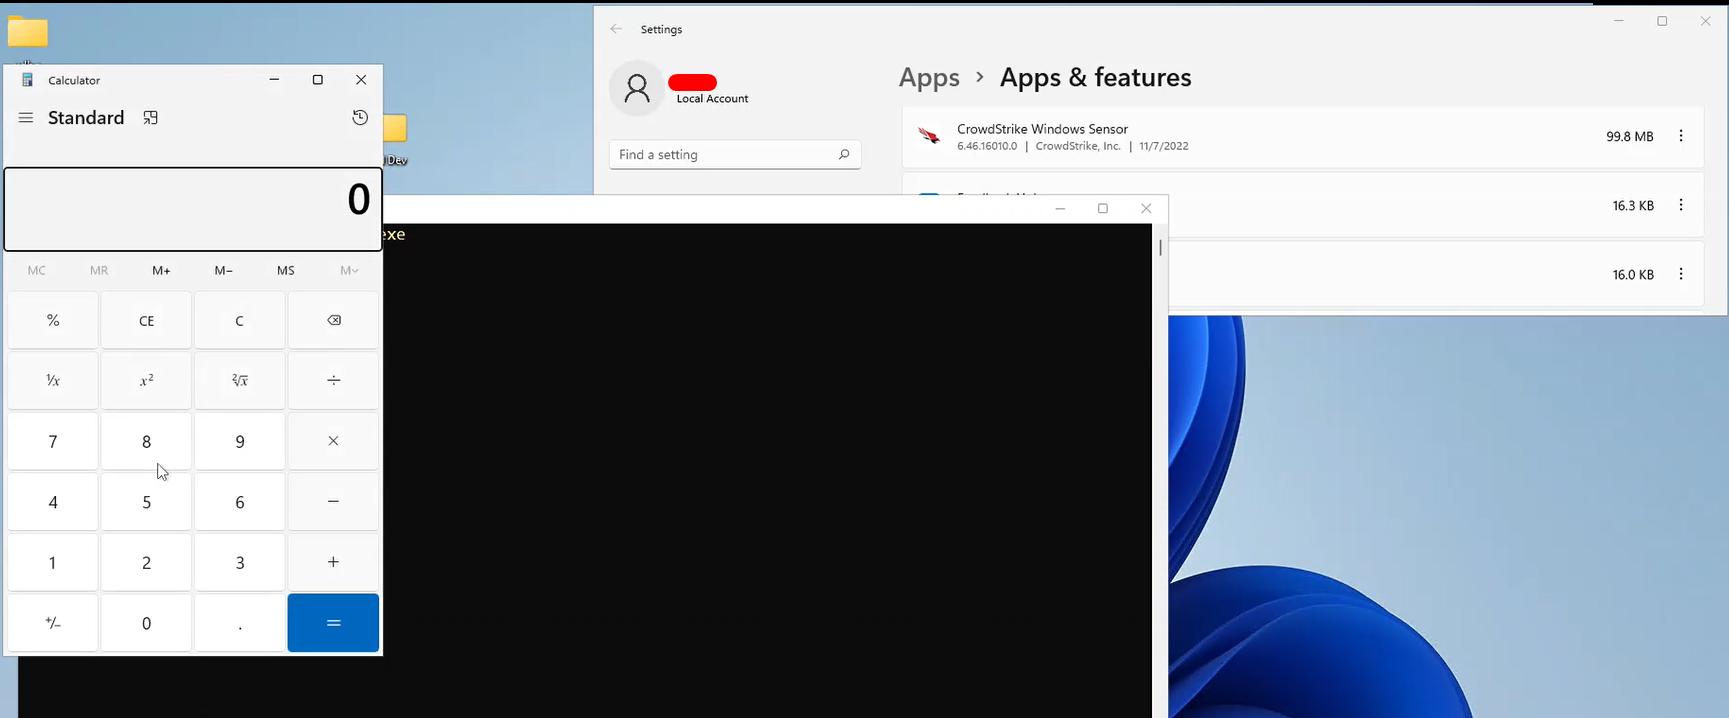 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 yo-yo-yo-jbo/msf_shellcode_analysis
Static analysis walkthrough of a Metasploit Windows shellcode: PowerShell payload decoding, XOR obfuscation, PEB walking, and Export Address Table…
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".

 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver