
nasm_linux_x86_64_pure_sharedlib
 therealdreg/nasm_linux_x86_64_pure_sharedlib
NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
exploitationpayload-developmentpost-exploitation+2
therealdreg/nasm_linux_x86_64_pure_sharedlibNASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".
 spiralbl0ck/partial-deobfuscated-sc-from-hackingteam-malware.-
This repo stores necessary files for the analysis blog which will come soon
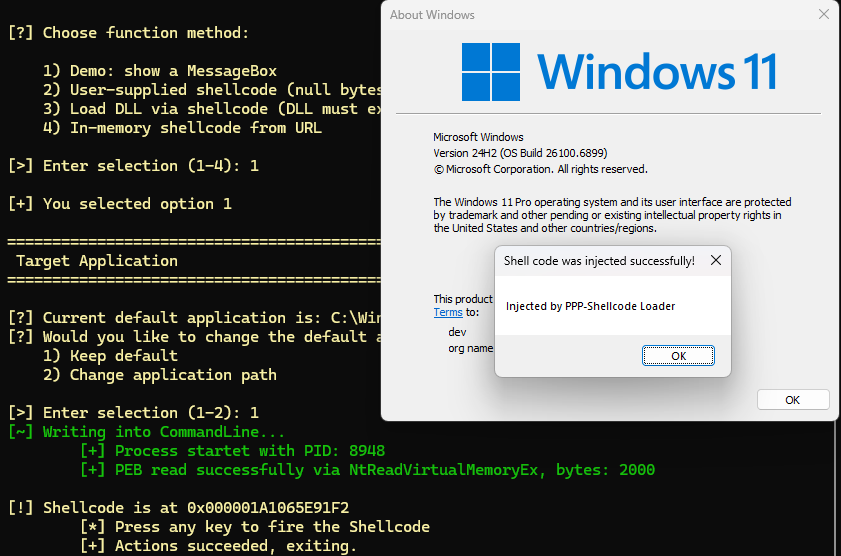 orange-cyberdefense/p3-loader
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
 s0md3v/nano
Nano is a family of PHP web shells which are code golfed for stealth.
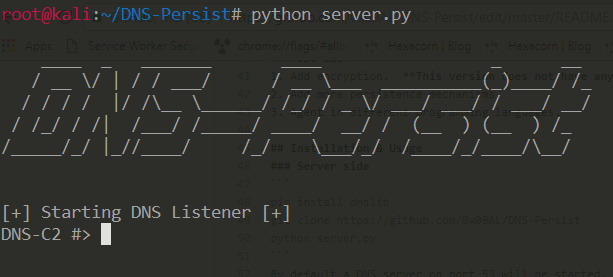 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 smaash/quasibot
complex webshell manager, quasi-http botnet.
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
 substing/cve-2019-11447_reverse_shell_upload
Python exploit for CVE-2019-11447 that uploads a PHP reverse shell to CuteNews 2.1.2, enabling remote command execution on vulnerable web…
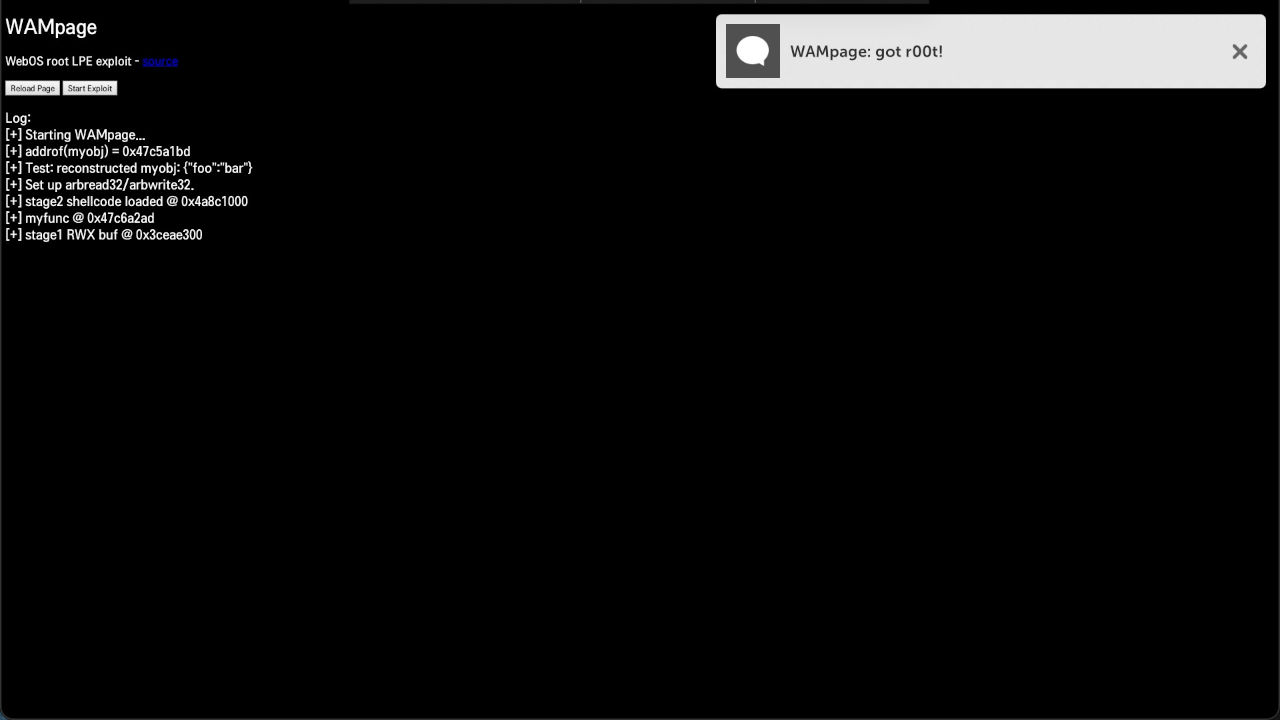 davidbuchanan314/wampage
WAMpage - A WebOS root LPE exploit chain (CVE-2022-23731)
 orf53975/rig-exploit-for-cve-2018-8174
Rig Exploit for CVE-2018-8174 As with its previous campaigns, Rig’s Seamless campaign uses malvertising. In this case, the malvertisements have a…
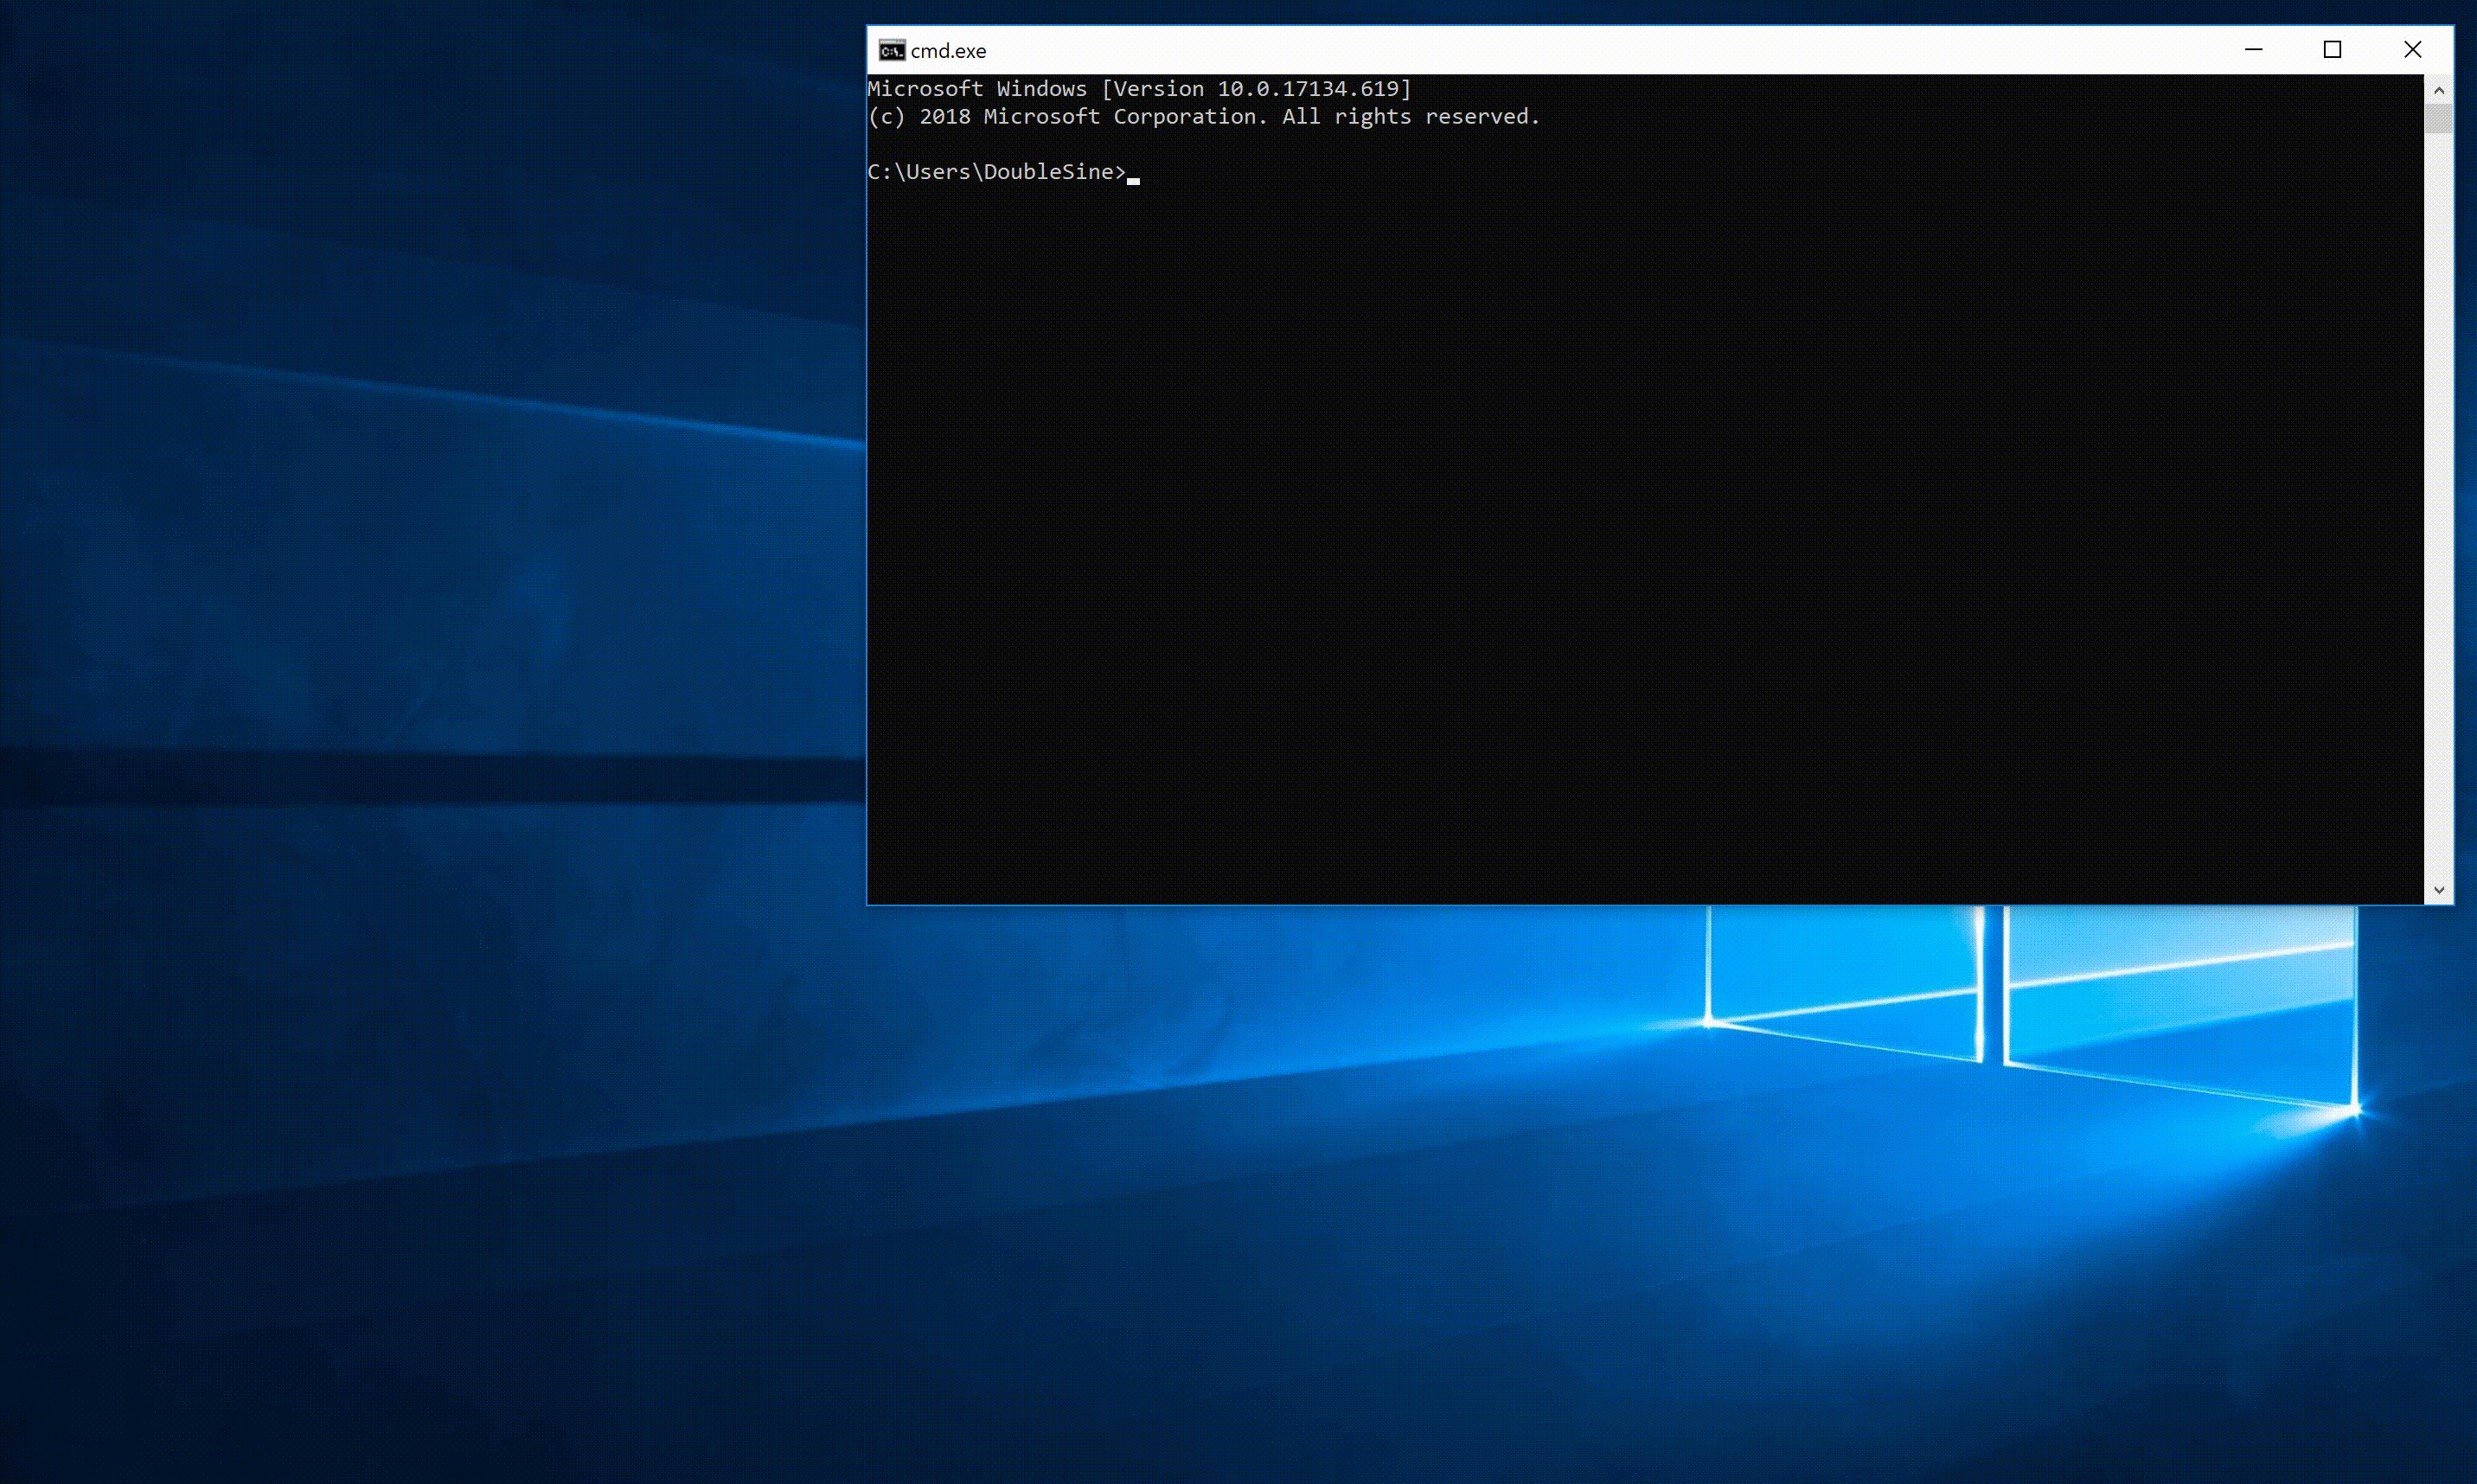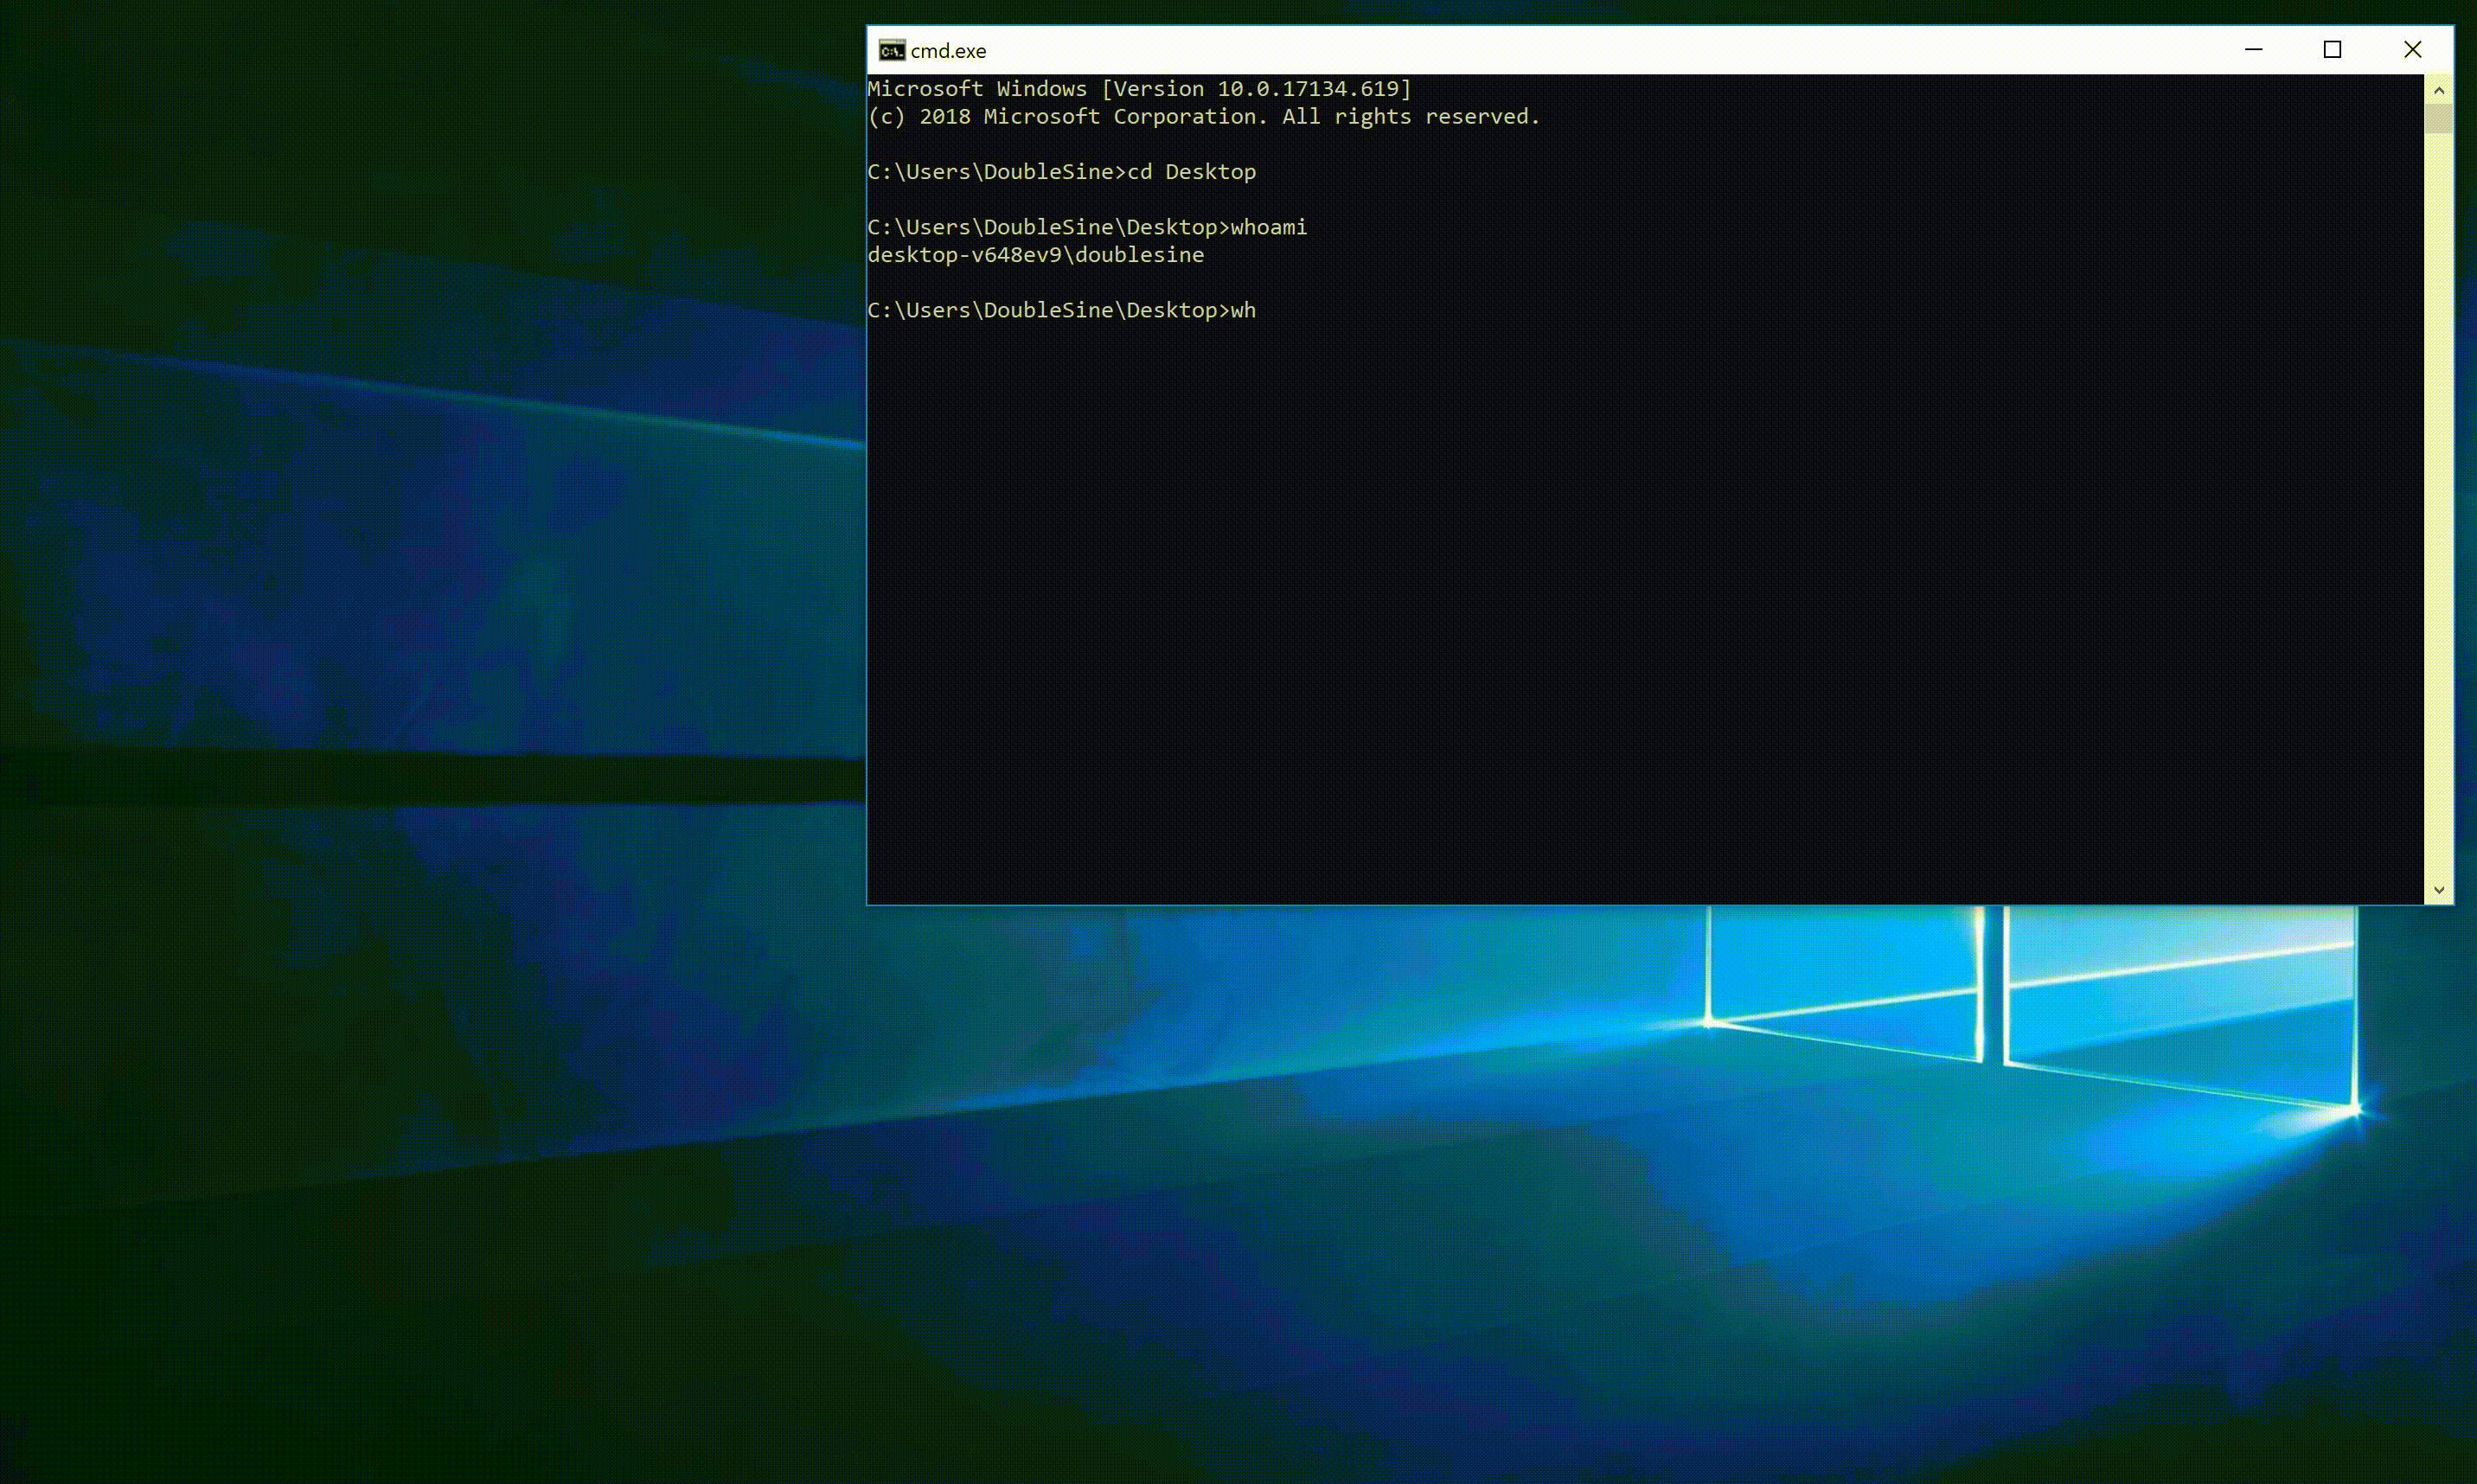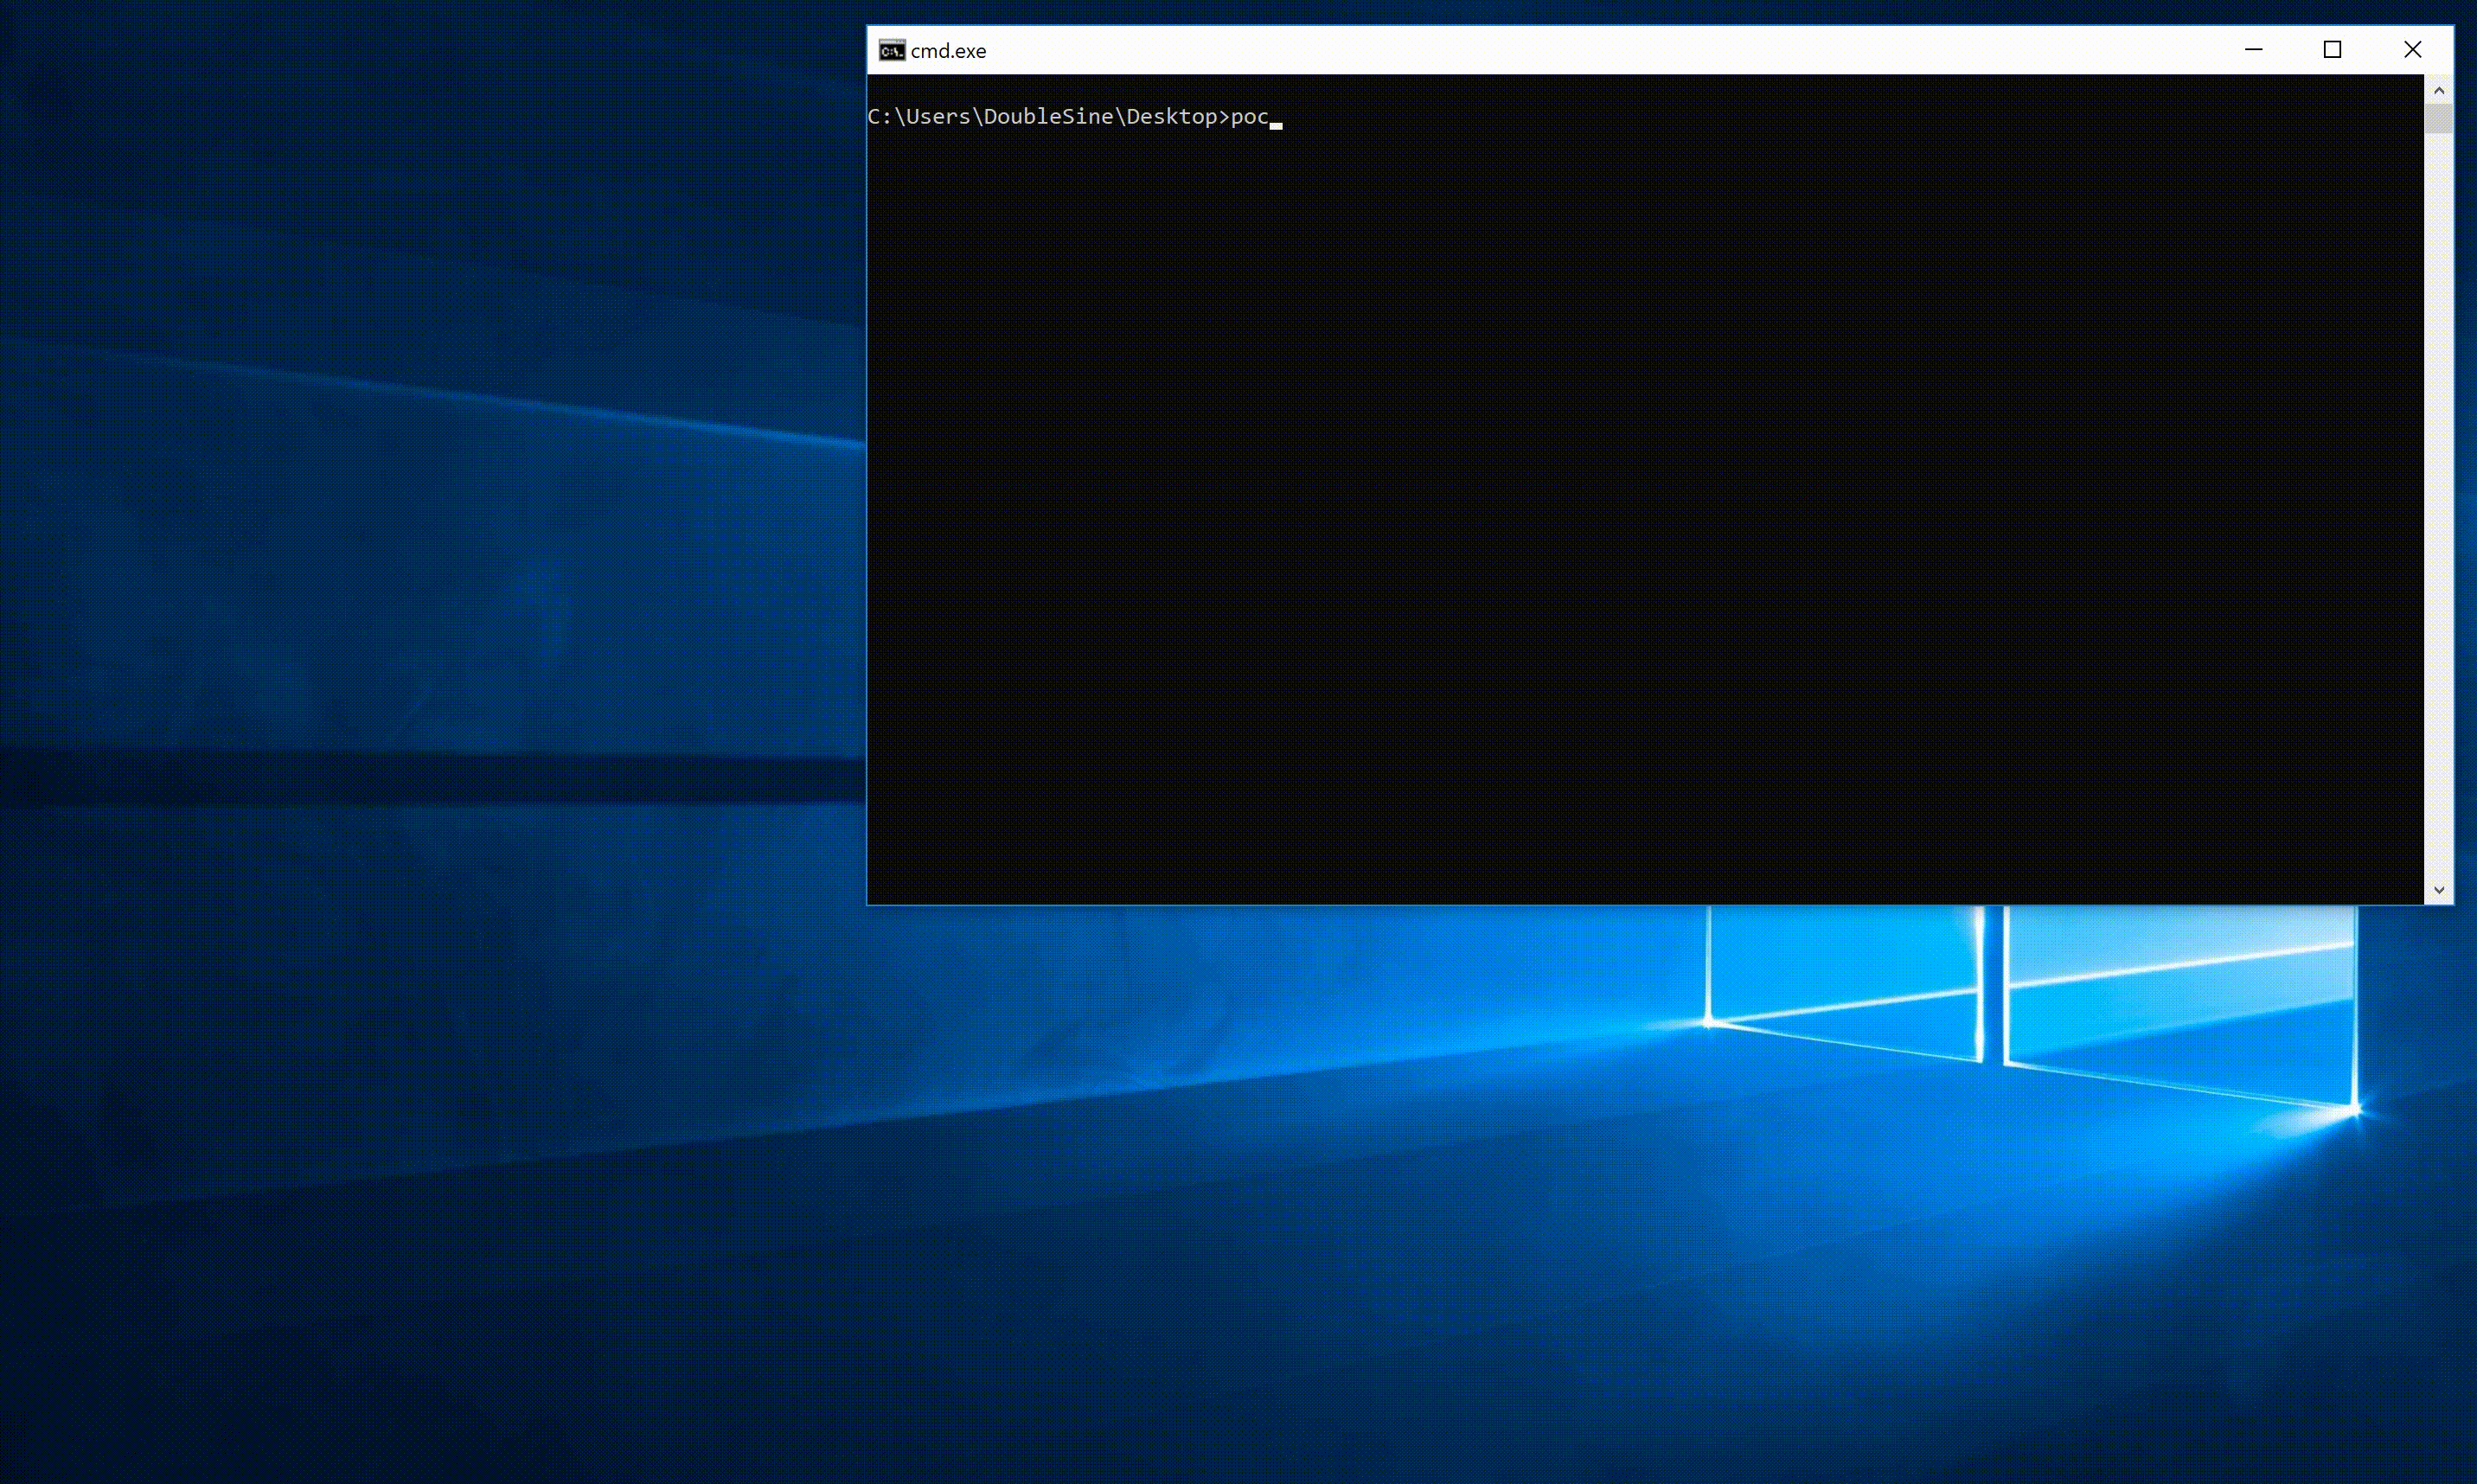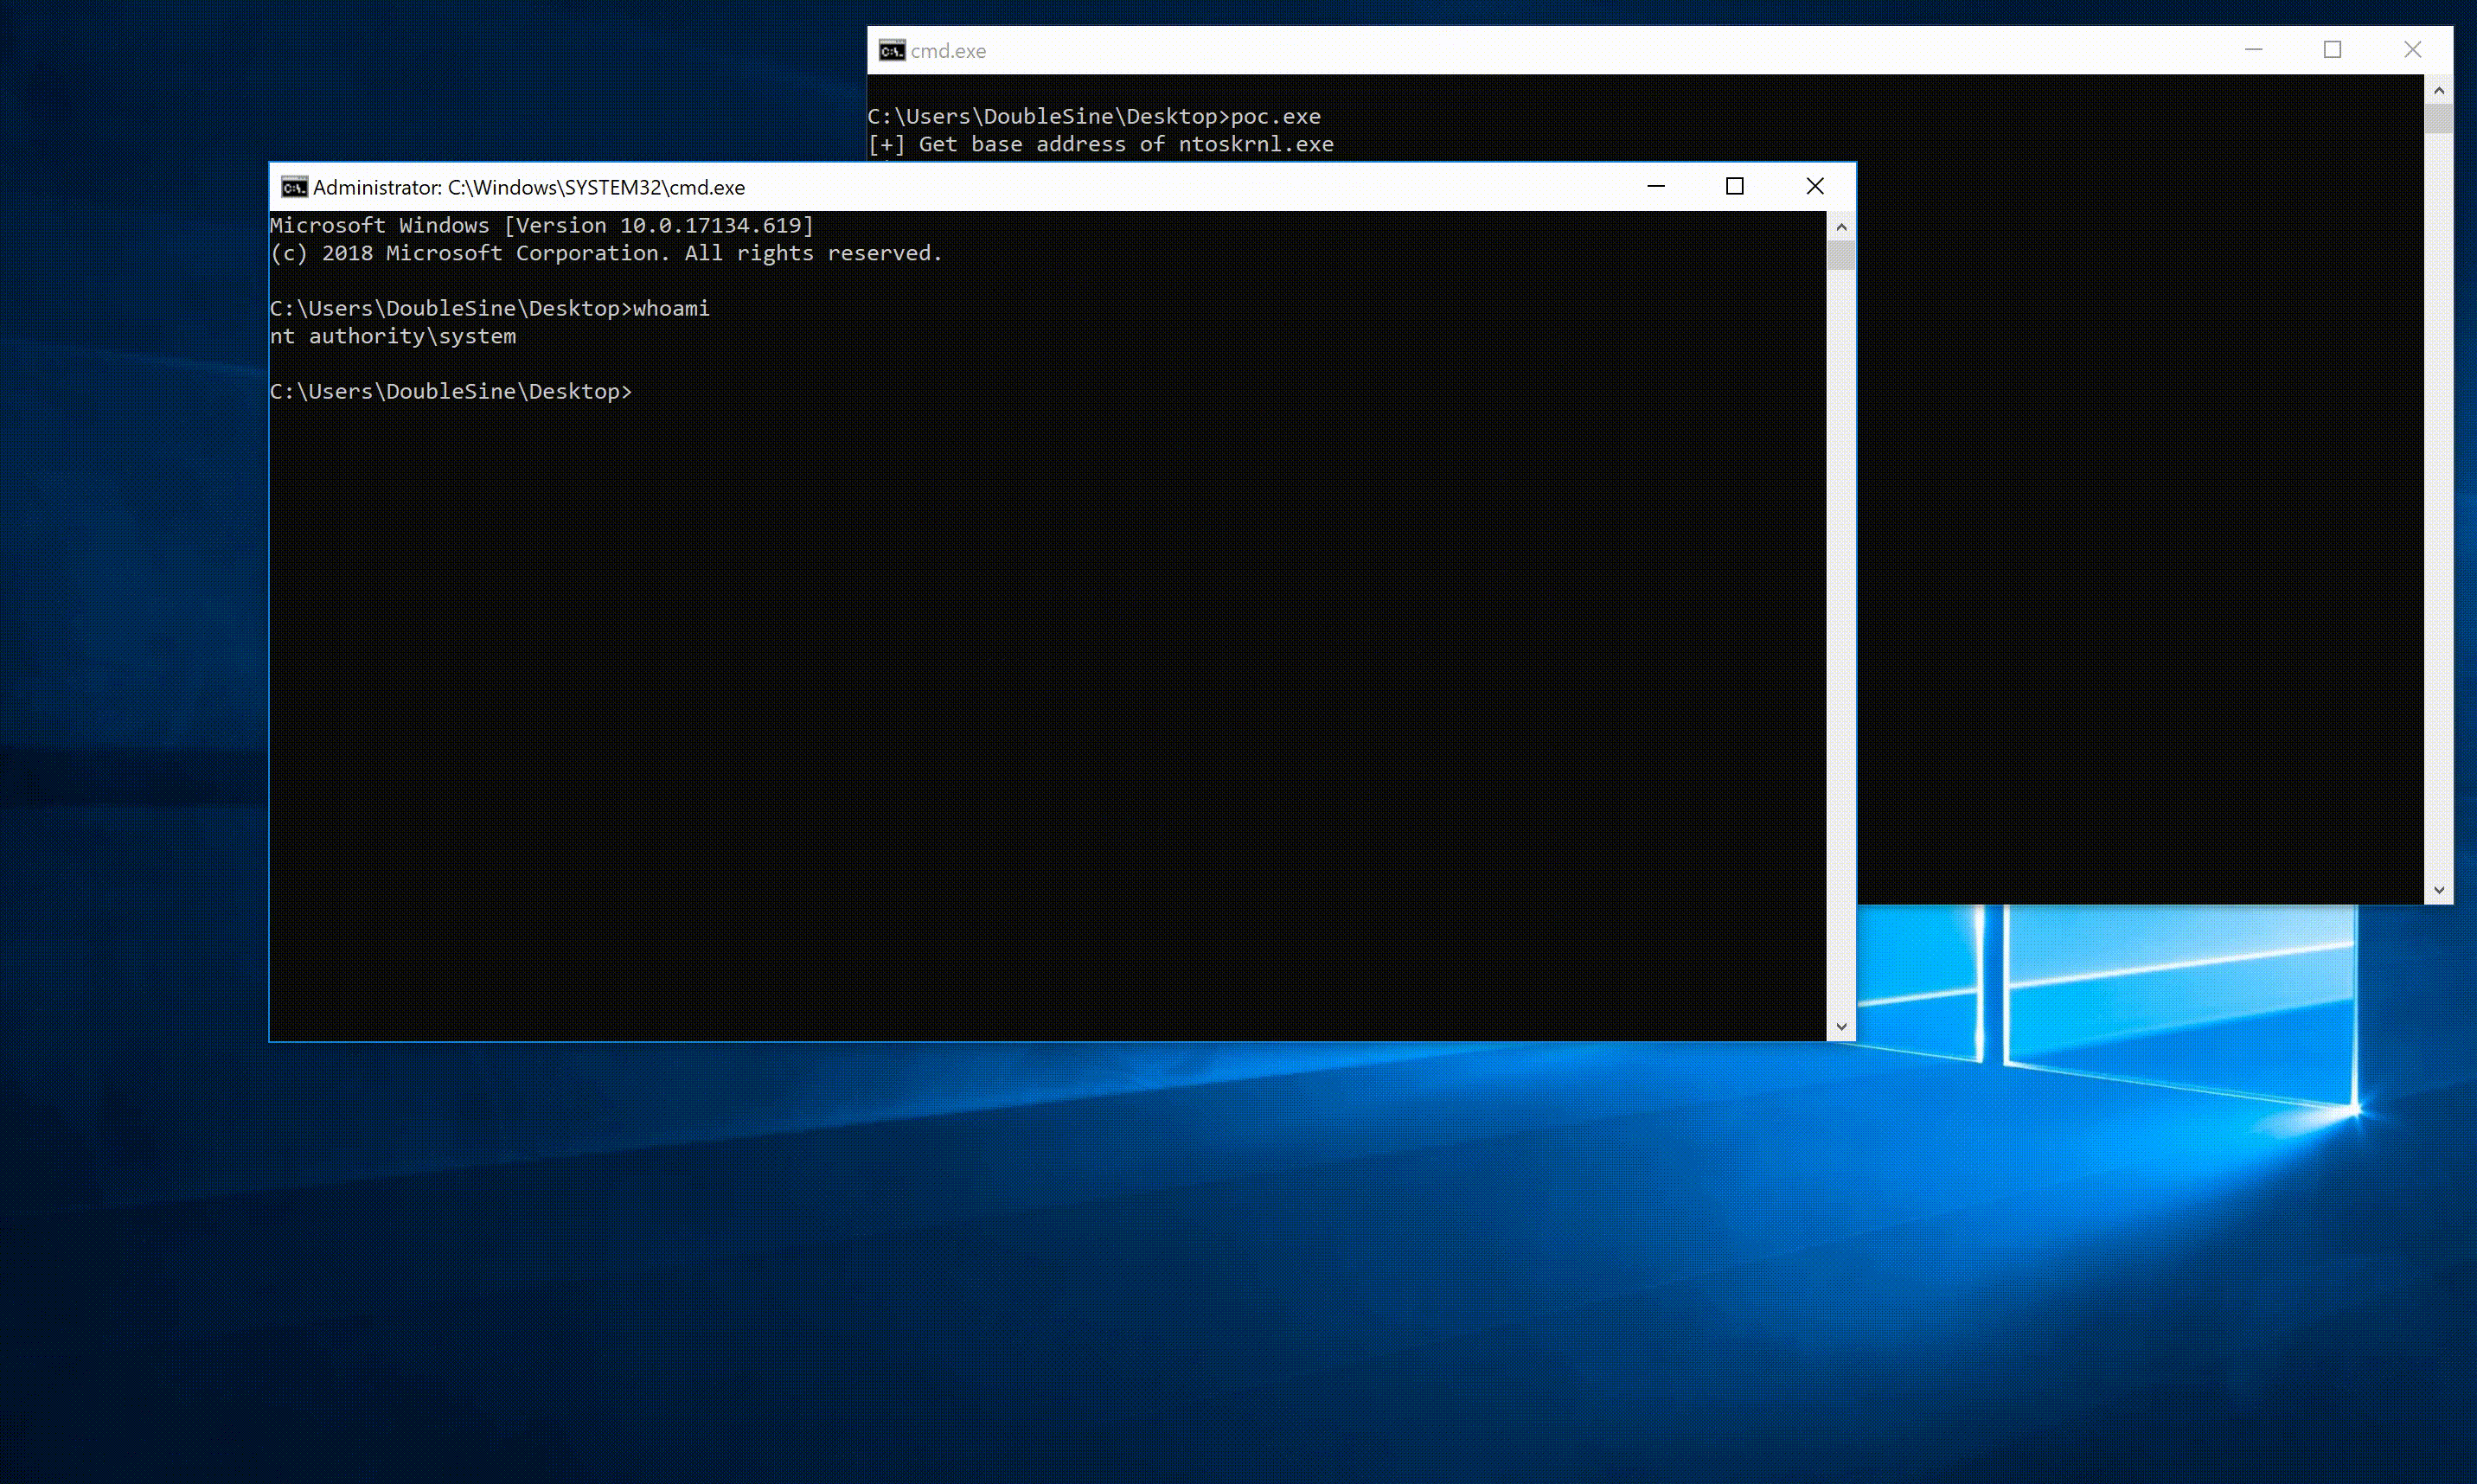 hypersine/sdokeycrypt-sys-local-privilege-elevation
CVE-2019-9729. Transferred from https://github.com/DoubleLabyrinth/SdoKeyCrypt-sys-local-privilege-elevation
 wearehackers160/cve-2026-48907
CVE-2026-48907 is a critical improper access control vulnerability in the JCE editor extension for Joomla. It allows unauthenticated attackers to…
 schn1tzelme1ster/cve-2025-6002
Python exploit for CVE-2025-6002 targeting authenticated arbitrary file upload in VirtueMart < 4.4.10. Logs in, uploads a PHP webshell, and triggers…

 xpltive/cve-2023-41425
WonderCMS v3.2.0 - v3.4.2 XSS to RCE exploit
 thunderstrike9090/conflicker_analysis_scripts
Scripts to analyze conflicker worm which exploits famous netapi vulnerability (CVE-2008-4250) i.e MS08-067
 marcingadz/spring-rce-poc
Testing CVE-2022-22968