
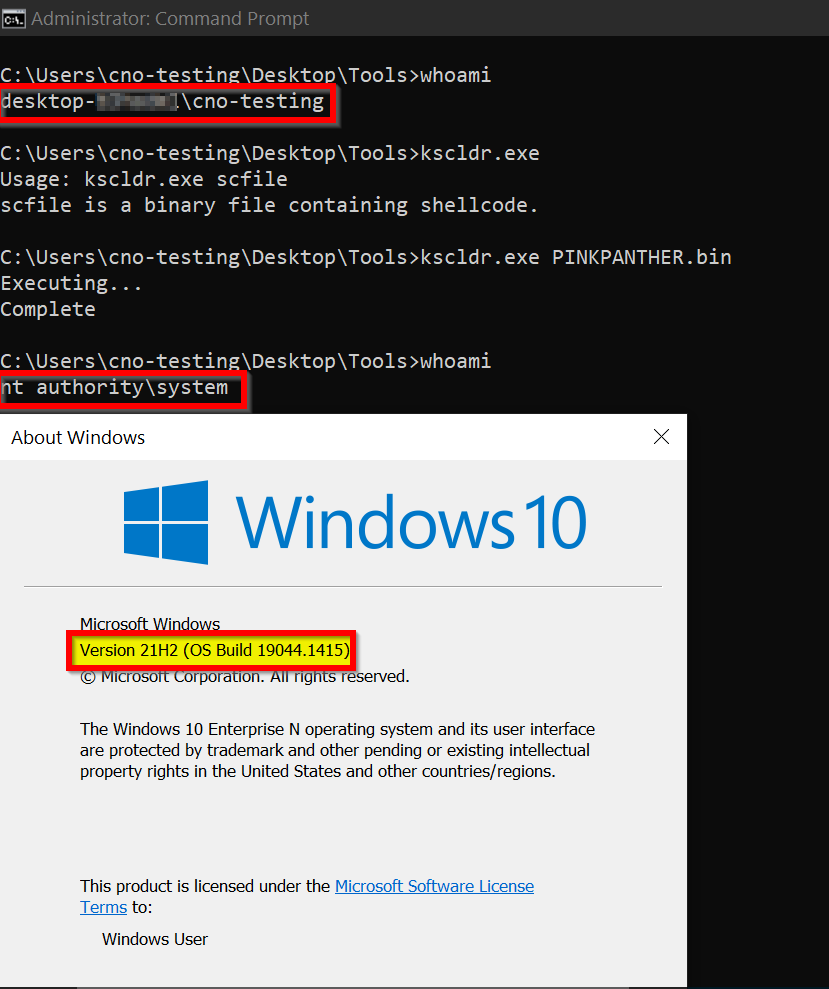
PINKPANTHER
 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
binary-exploitationpayload-developmentpost-exploitation+2
516
winterknife/pinkpantherWindows x64 handcrafted token stealing kernel-mode shellcode
 rsmudge/cve-2020-0796-bof
Cobalt Strike Beacon Object File implementing CVE-2020-0796 SMBGhost local privilege escalation with dual weaponization paths for token theft and…
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.
 jayngng/bludit-cve-2019-17240
Bypass bludit mitigation login form and upload malicious to call a rev shell
 hakivvi/cve-2021-40449
Windows LPE exploit for CVE-2021-40449, a use-after-free in win32kfull!GreResetDCInternal, leveraging token leaking, kernel gadget abuse, and…
 h3x0v3rl0rd/cve-2022-41544
Python exploit script for CVE-2022-41544 in GetSimple CMS. Automates API key leakage, CSRF token extraction, PHP shell upload, and reverse shell…
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
 markoarmitage/metasploit-framework
app turn nil publics and privates into blanks 3 months ago config Use bundler/setup for more graceful bundler related failures 11 days ago data…