

LazZzy_Dump
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
binary-analysiscode-analysisdigital-forensics+6
1
trustedsec/lazzzy_dumpStatically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 ntfargo/relapse-exploit
PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 sneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.
Chained Chrome V8 renderer escape proof-of-concept exploiting four CVEs: Float64Array corruption, Wasm overwrite, popup navigation retargeting, and…
 racoten/reflectivepluginloader
A minimal PE mapper that loads DLLs straight from memory and calls into a clean plugin interface, no LoadLibrary needed.
 donofly/cve-2025-22457-vulnserver-lab
Hands-on lab reproducing CVE-2025-22457: sets up Docker attacker/victim containers, finds stack addresses with GDB, and delivers a msfvenom reverse…
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 bytejmp/ms09-050
Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
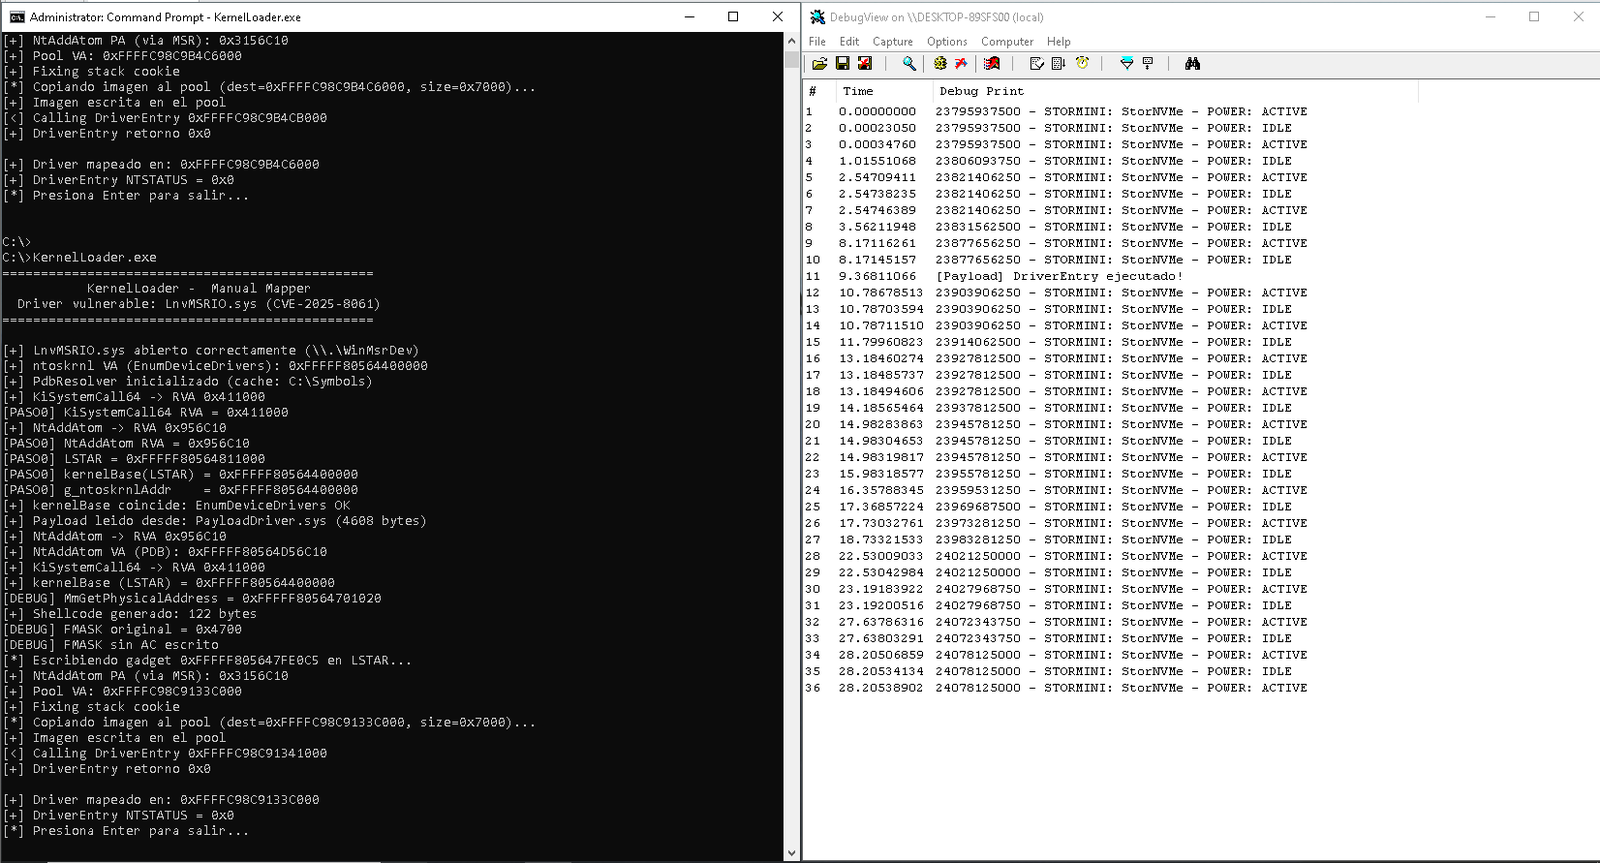 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
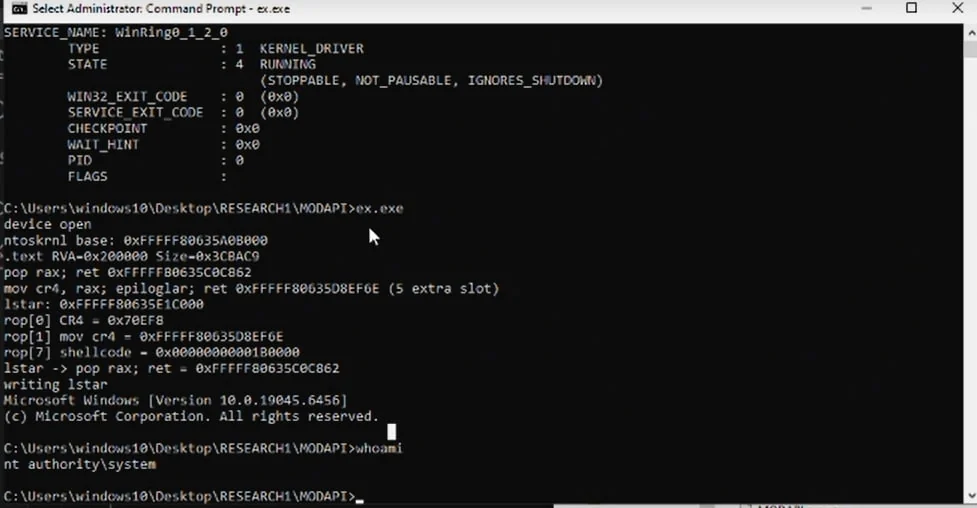 mein-0/lolmodapi
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.
 sneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter
Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
 withsecurelabs/radare2-scripts
Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…