copyFail-CVE-2026-31431-workaround-bash

Provides a bash workaround script to mitigate CVE-2026-31431, preventing remote code execution via copy.fail exploit. Includes usage instructions for…

Provides a bash workaround script to mitigate CVE-2026-31431, preventing remote code execution via copy.fail exploit. Includes usage instructions for…

基于Java实现的Shellcode加载器

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.

Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post

Various ways to execute shellcode

Windows User-Mode Shellcode Development Framework (WUMSDF)

Get your data from the resource section manually, with no need for windows apis

Repository containing exploit scripts for various CVEs, targeting web applications, binaries, and network services, suitable for penetration testing…

ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.

Herramienta para evadir disable_functions y open_basedir

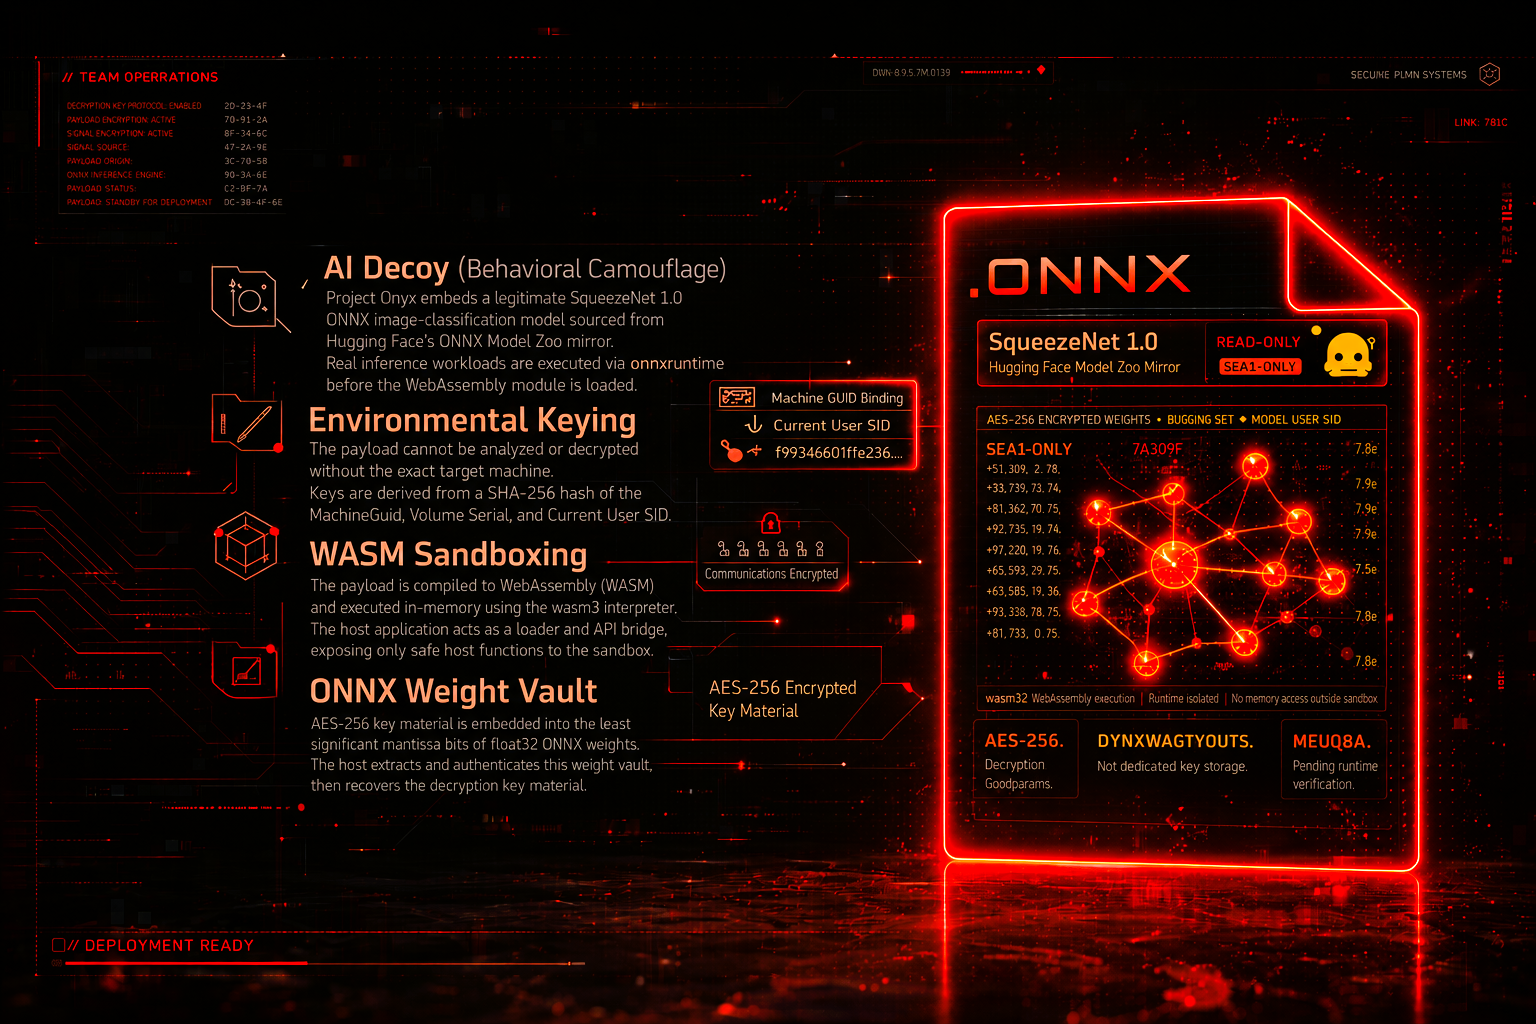
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…

Proof of concept for CVE-2022-31814

Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

Full-chain exploit for CVE-2025-2783 (Ipcz Sandbox Escape & RCE).


Evaluation framework for studying LLM agents that automatically generate working exploits from vulnerability reports, bypassing modern security…

On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.