

Chimay-Red
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
binary-exploitationembedded-systems-securityexploitation+8
6684 years ago
bignerd95/chimay-redWorking POC of Mikrotik exploit from Vault 7 CIA Leaks
 linnemanlabs/glimmer
Adversary emulation and C2 framework for security research
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
 sneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter
Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
 withsecurelabs/radare2-scripts
Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 therealdreg/nasm_linux_x86_64_pure_sharedlib
NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
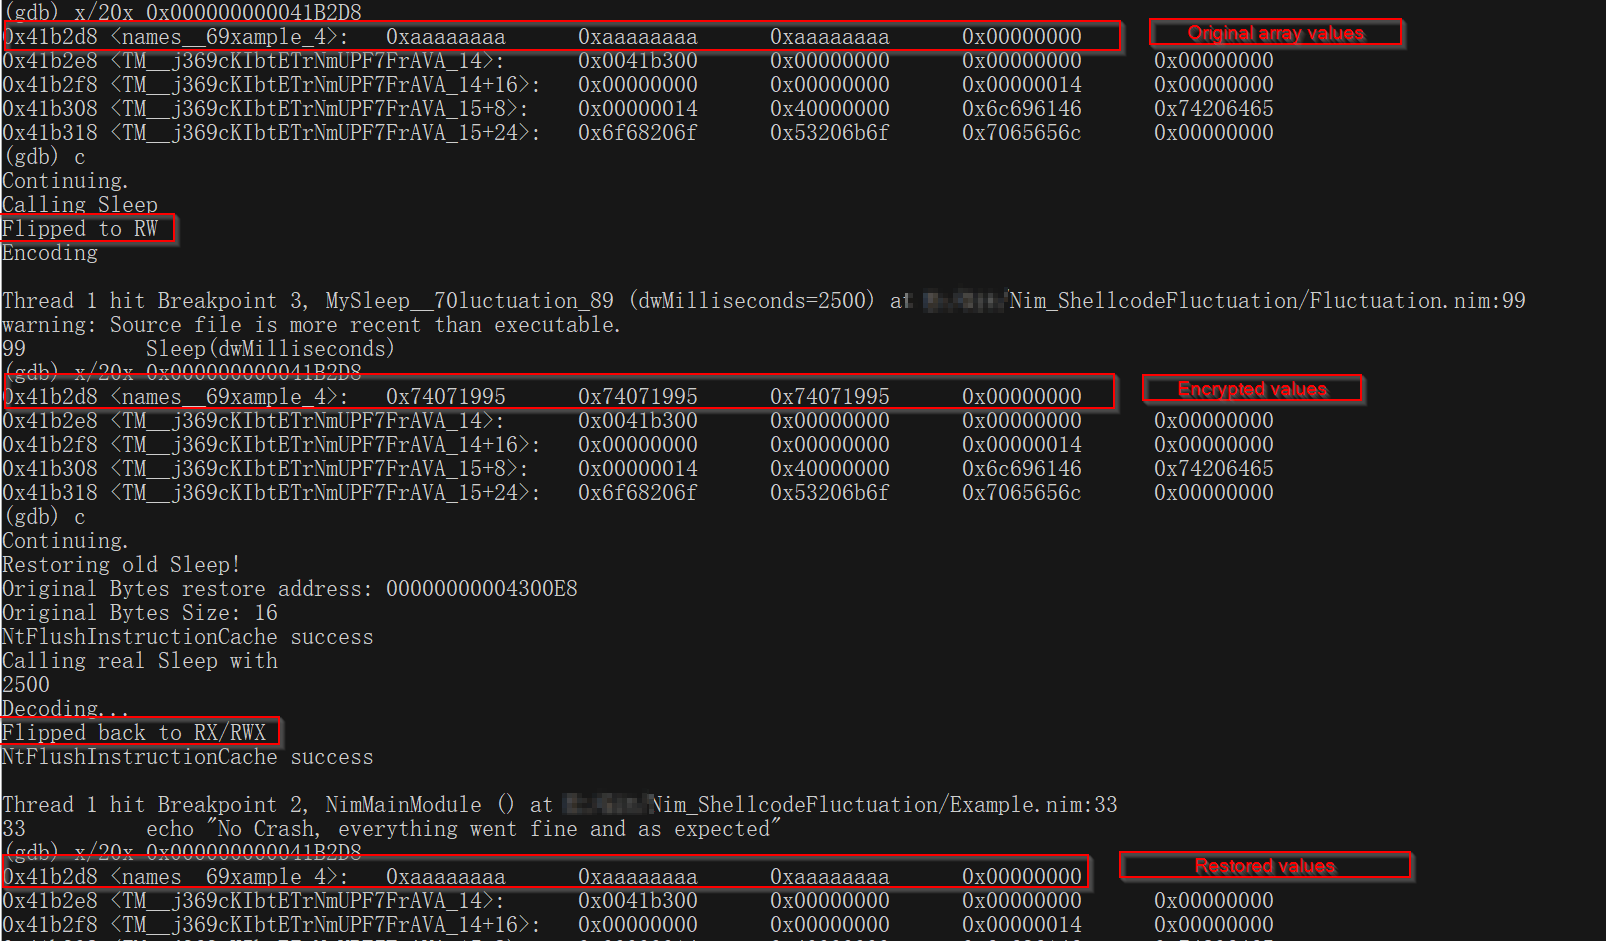 s3cur3th1ssh1t/nimshellcodefluctuation
ShellcodeFluctuation PoC ported to Nim
 saadahla/d1rkldr
Shellcode Loader with Indirect Dynamic syscall Implementation , shellcode in MAC format, API resolving from PEB, Syscall calll and syscall…
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".
 iilegacyyii/datainject-bof
Hijacks code execution via overwriting Control Flow Guard pointers in combase.dll
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis
 touhidshaikh/bin2shell
bin2shell is very small utils for extract shell code from the binary file
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
