
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
26 results
IKEV2-POC preview

IKEV2-POC

GitHubepsilonpointori/ikev2-poc

IKEv2, ikeext.dll, CVE-2026-33824, double free, heap grooming, ROP, SKF fragmentation, Windows exploit, anti-debug, obfuscation, API hooking,…
binary-exploitationcommand-and-controlexploit-frameworks+3
6
3 months ago
Medusa preview

Medusa

GitHubmythicagents/medusa

Cross-platform C2 agent for Mythic with dynamic function loading, SOCKS5 proxy, file operations, shellcode injection, and macOS/Windows…
command-and-controlexploit-frameworkslateral-movement+8
2121 month ago
CVE-2015-1578-PoC-Metasploit preview

CVE-2015-1578-PoC-Metasploit

GitHubyaldobaoth/cve-2015-1578-poc-metasploit

This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
binary-exploitationexploitationexploit-frameworks+6
1 year ago
Obfusk8 preview

Obfusk8

GitHubx86byte/obfusk8

Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
cryptographyexploit-frameworkspayload-development+4
8223 months ago
CrystalSliver preview

CrystalSliver

GitHublicitrasimone/crystalsliver

Crystal Palace Evasion kit for Sliver

command-and-controlexploit-frameworksids-ips-evasion+9
1183 months ago
CVE-2003-0264 preview

CVE-2003-0264

GitHubadenkiewicz/cve-2003-0264

Exploit for CVE-2003-0264 based on pwntools and metasploit's windows/reverse_tcp
binary-exploitationexploitationexploit-frameworks+3
8 years ago
rwsploit preview

rwsploit

GitHubabq0/rwsploit

Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…

exploitationinformation-gatheringpayload-generation+6
64 months ago
PhantomEvasion preview

PhantomEvasion

GitHubesskumar/phantomevasion

Python-based antivirus evasion tool generating undetectable executables from msfvenom payloads with advanced techniques like junkcode injection,…

exploit-frameworkspayload-generationpenetration-testing+5
176 years ago
Winpayloads preview

Winpayloads

GitHubnccgroup/winpayloads

Undetectable Windows Payload Generation
command-and-controlexploit-frameworkslateral-movement+9
1.6k7 years ago
msfpc preview

msfpc

GitHubg0tmi1k/msfpc

MSFvenom Payload Creator (MSFPC)
command-and-controlexploit-frameworkspayload-development+5
1.3k5 years ago
DAws preview

DAws

GitHubdotcppfile/daws

Advanced Web Shell

ids-ips-evasionpayload-generationpenetration-testing+6
5809 years ago
YAPS preview

YAPS

GitHubnickguitar/yaps

Yet Another PHP Shell - The most complete PHP reverse shell
command-and-controlexploitationinformation-gathering+7
834 years ago
REW-sploit preview

REW-sploit

GitHubrew-sploit/rew-sploit

Emulate and Dissect MSF and *other* attacks

bluetooth-securitydebuggersdefensive-tools+6
1442 years ago
Villain preview

Villain

GitHubt3l3machus/villain

Villain is a high level stage 0/1 C2 framework that can handle multiple reverse TCP & HoaxShell-based shells, enhance their functionality with…
command-and-controlexploit-frameworkspayload-generation+4
4.5k1 year ago
reverse_ssh preview

reverse_ssh

GitHubnhas/reverse_ssh

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
shellcodeshellcode-generation
1.5k18 days ago
gmailc2 preview

gmailc2

GitHubmachine1337/gmailc2

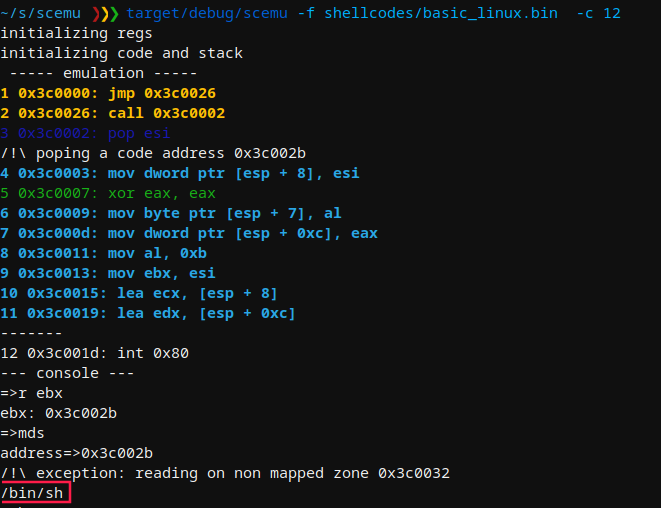
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
command-and-controleducationpayload-generation+4
4891 year ago
mwemu preview

mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
binary-analysisexploit-frameworksmalware-analysis+2
31511h 21m ago
Blackbone preview

Blackbone

GitHubdarthton/blackbone

Windows memory hacking library

binary-analysisdebuggersdynamic-analysis-sandboxing+9
5.5k4 years ago
Previous12Next