
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
226 results
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
binary-exploitationdebuggerseducation+7
3
1 month ago
CVE-2026-87575-CVE-2026-87606-CVE-2026-87491-and-CVE-2026-85046.-Escape-the-v8-carcass. preview

CVE-2026-87575-CVE-2026-87606-CVE-2026-87491-and-CVE-2026-85046.-Escape-the-v8-carcass.

GitHubsneakynachos/cve-2026-87575-cve-2026-87606-cve-2026-87491-and-cve-2026-85046.-escape-the-v8-carcass.

Chained Chrome V8 renderer escape proof-of-concept exploiting four CVEs: Float64Array corruption, Wasm overwrite, popup navigation retargeting, and…

binary-exploitationexploitationpapers-research+5
511 days ago
MSRKit preview

MSRKit

GitHubrurixis/msrkit

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
binary-exploitationexploitationpayload-development+5
96 days ago
MS09-050 preview

MS09-050

GitHubbytejmp/ms09-050

Python exploit for MS09-050 (CVE-2009-3103) SMBv2 srv2.sys buffer overflow, with vulnerability scanner, arch auto-detection, and x86/x64 reverse…
exploitationinformation-gatheringnetwork-security+7
9 days ago
LolModapi preview

LolModapi

GitHubmein-0/lolmodapi

Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.
binary-exploitationexploitationprivilege-escalation+2
414 days ago
CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter preview

CVE-2026-87491-and-CVE-2026-85046-the-bagel-fell-off-the-counter

GitHubsneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter

Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
binary-exploitationexploitationmemory-forensics+3
315 days ago
radare2-scripts preview

radare2-scripts

GitHubwithsecurelabs/radare2-scripts

Collection of radare2 scripts for malware analysis: carve binaries from memory dumps, patch PE headers, and decode hashed function imports in…

binary-analysisdigital-forensicsmalware-analysis+3
328 years ago
Anti_suspend preview

Anti_suspend

GitHubgmh5225/anti_suspend

Protect process by shellcode
defensive-toolsreverse-engineeringshellcode
53 years ago
CVE-2026-2766-but-with-wasm preview

CVE-2026-2766-but-with-wasm

GitHubsneakynachos/cve-2026-2766-but-with-wasm

CVE-2026-2766, but with wasm
binary-exploitationexploitationpayload-development+2
11 month ago
nasm_linux_x86_64_pure_sharedlib preview

nasm_linux_x86_64_pure_sharedlib

GitHubtherealdreg/nasm_linux_x86_64_pure_sharedlib

NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
exploitationpayload-developmentpost-exploitation+2
313 years ago
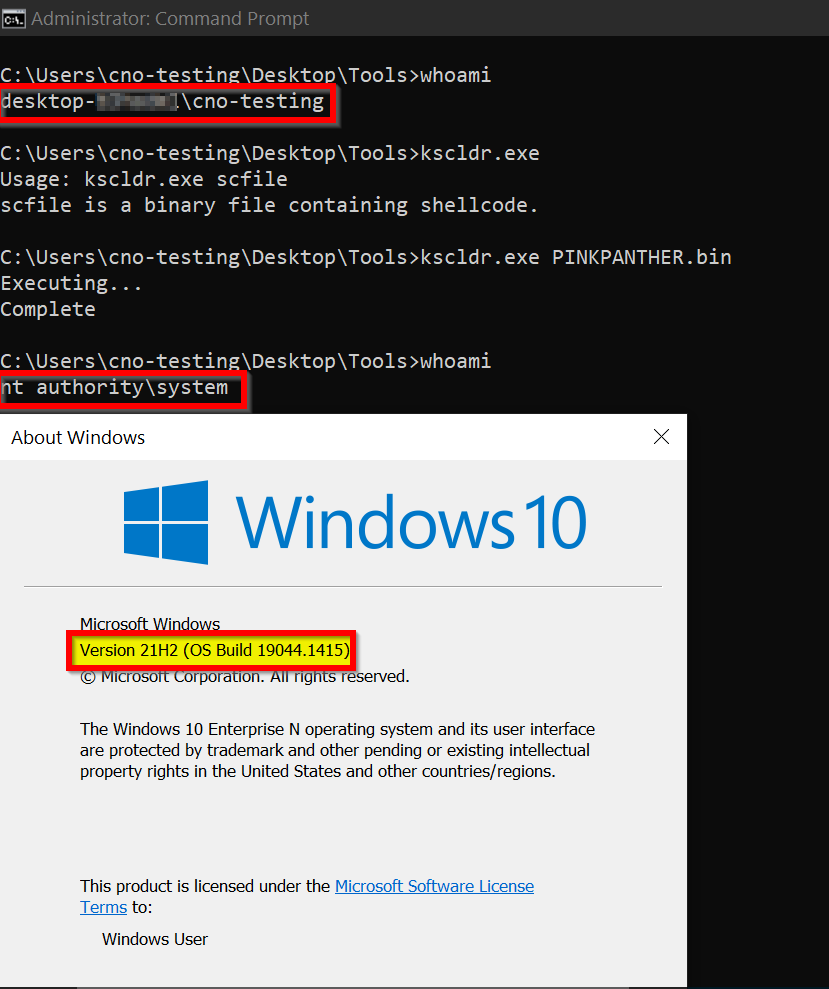
PINKPANTHER preview

PINKPANTHER

GitHubwinterknife/pinkpanther

Windows x64 handcrafted token stealing kernel-mode shellcode
binary-exploitationpayload-developmentpost-exploitation+2
5162 years ago
OneDriveUpdaterSideloading preview

OneDriveUpdaterSideloading

GitHubchoisg/onedriveupdatersideloading

Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post

adversarial-attackpayload-developmentred-teaming+1
1013 years ago
Pokemon-Shellcode-Loader preview

Pokemon-Shellcode-Loader

GitHubtechryptic/pokemon-shellcode-loader

Tired of looking at hex all day and popping '\x41's? Rather look at Lugia/Charmander? I have the solution for you.

adversarial-attackpayload-developmentpayload-generation+3
1274 years ago
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
9597 months ago
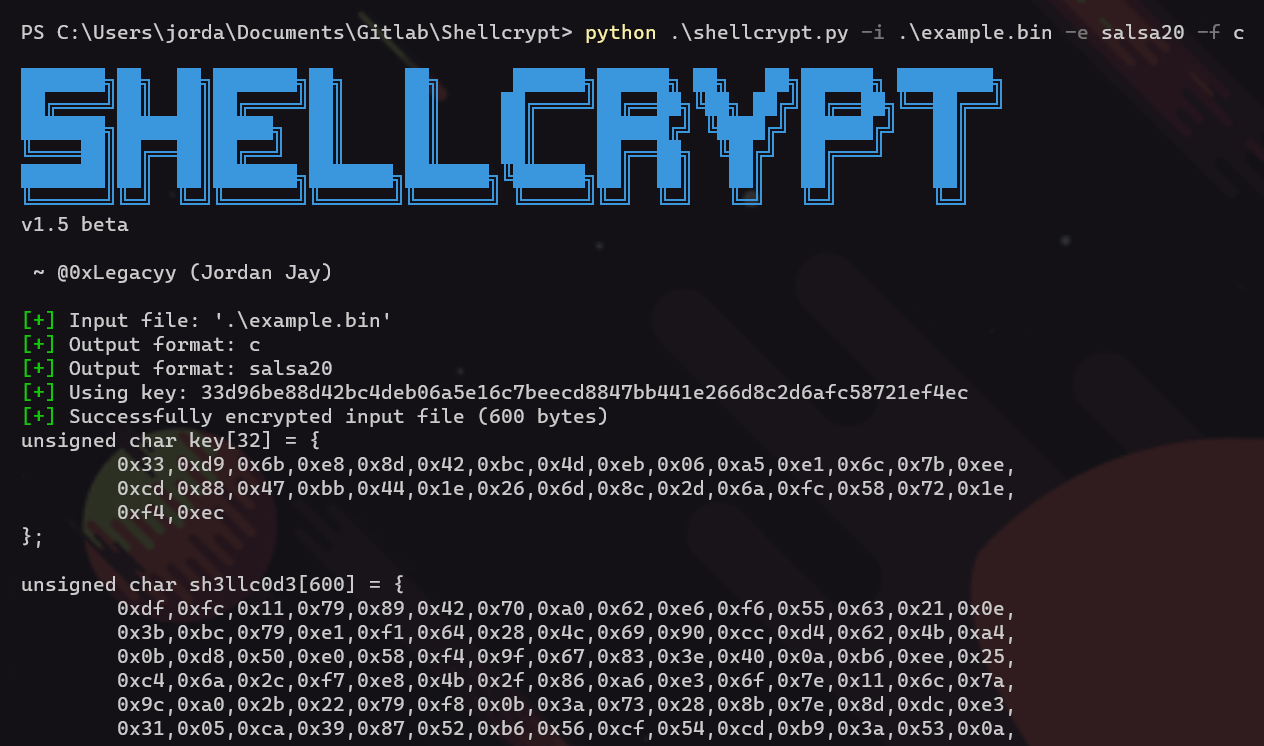
Shellcrypt preview

Shellcrypt

GitHubiilegacyyii/shellcrypt

A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.

cryptographyencryption-decryption-toolspayload-development+3
2178 days ago
SharpWhispers preview

SharpWhispers

GitHubsecforce/sharpwhispers

C# porting of SysWhispers2. It uses SharpASM to find the code caves for executing the system call stub.

ids-ips-evasionpayload-developmentpost-exploitation+2
1123 years ago
NimShellcodeFluctuation preview

NimShellcodeFluctuation

GitHubs3cur3th1ssh1t/nimshellcodefluctuation

ShellcodeFluctuation PoC ported to Nim

adversarial-attackpayload-developmentpost-exploitation+2
773 years ago
ntqueueapcthreadex-ntdll-gadget-injection preview

ntqueueapcthreadex-ntdll-gadget-injection

GitHublloydlabs/ntqueueapcthreadex-ntdll-gadget-injection

This novel way of using NtQueueApcThreadEx by abusing the ApcRoutine and SystemArgument[0-3] parameters by passing a random pop r32; ret gadget can…

adversarial-attackids-ips-evasionpayload-development+3
2663 years ago
Previous12…13Next