
CSharpScripts
C# offensive scripts for reflective PE and shellcode injection, in-memory payload execution, XOR brute-force shellcode decryption, and .NET assembly…

C# offensive scripts for reflective PE and shellcode injection, in-memory payload execution, XOR brute-force shellcode decryption, and .NET assembly…

Linux C2 beacon with native in-memory ELF BOF loader, AES-256-CFB encrypted polling, and a Python C2 server for fileless post-exploitation modules.

C++ process hollowing injector that encrypts and obfuscates shellcode with XOR, Base64, and dynamic API resolution to deploy stealthy reverse shells…

Reduce Entropy And Obfuscate Youre Payload With Serialized Linked Lists

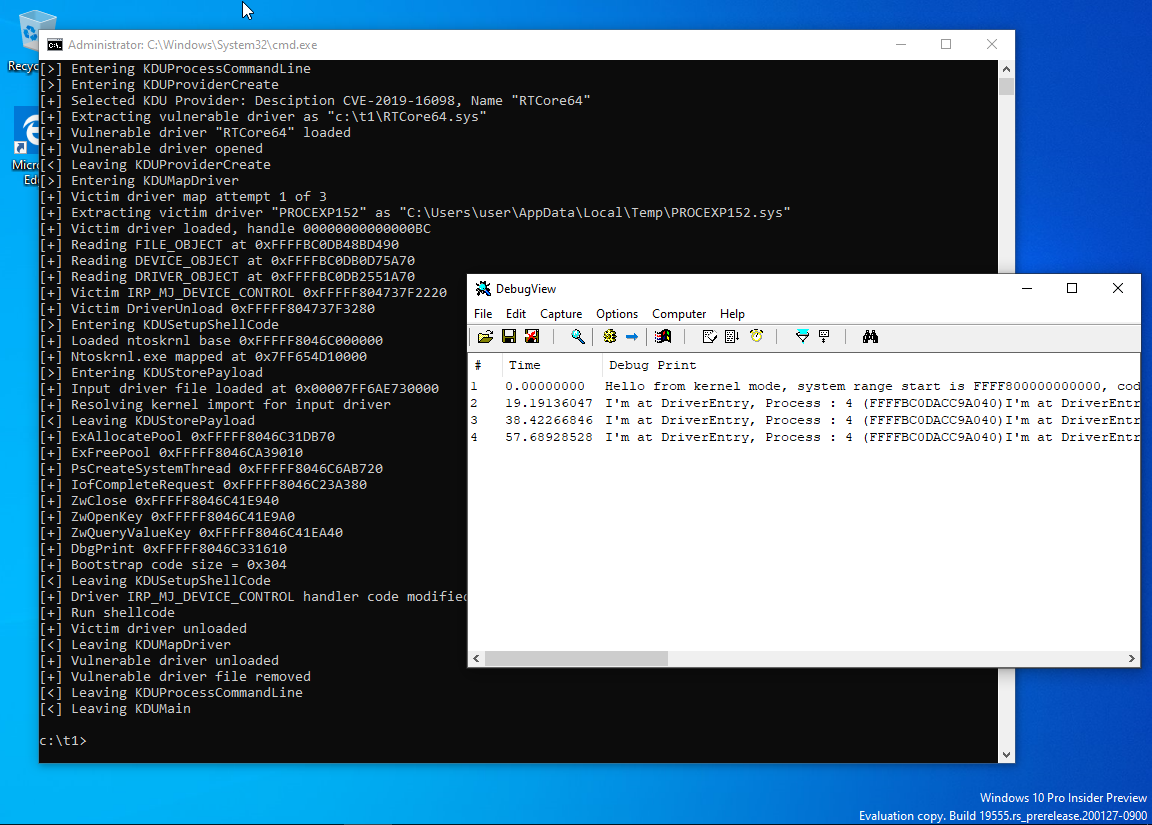
Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…

Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…

A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.

A PoC on how to use a Compute Shader as Payload

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)

Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…

C# Reflective loader for unmanaged binaries.

A QoL tool to obfuscate shellcode. In the future will be able to chain encoding/encryption/compression methods.

This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)

A dynamic unpacking tool

Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver

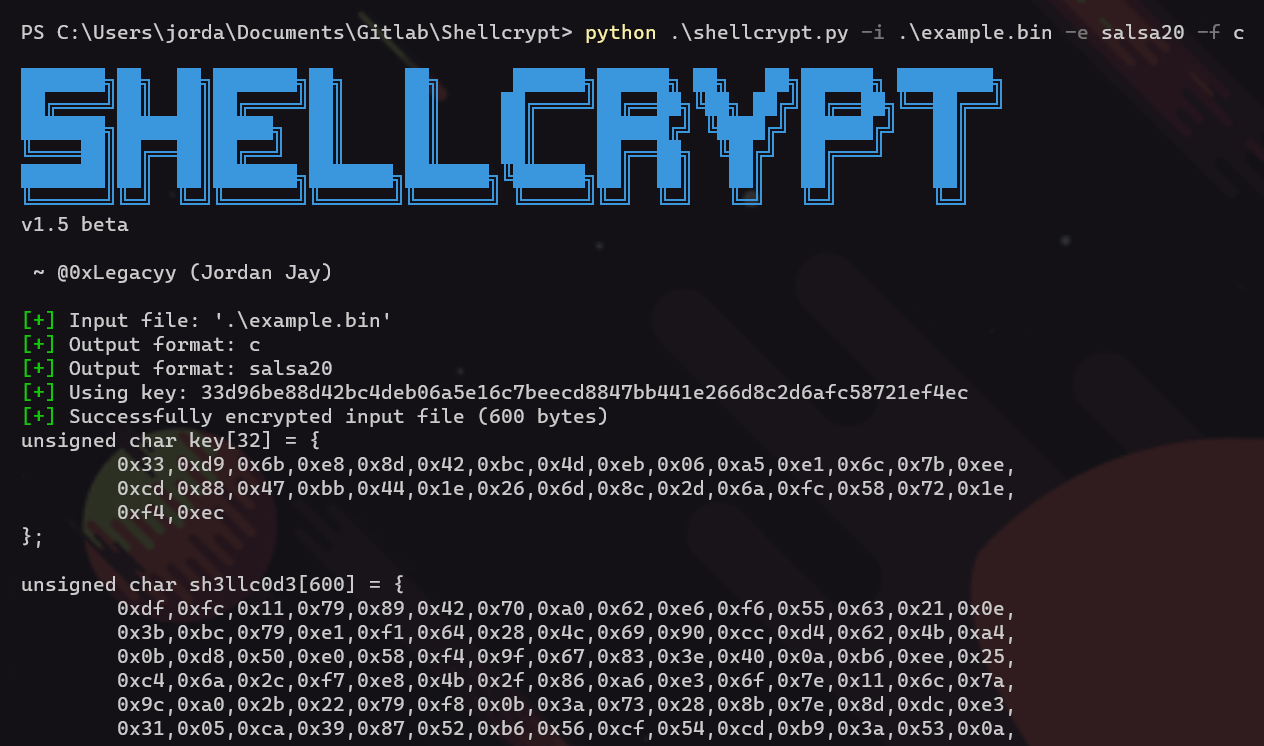
Swiss Army Knife for payload encryption, obfuscation, and conversion to byte arrays – all in a single command (14 output formats supported)! ☢️

Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.

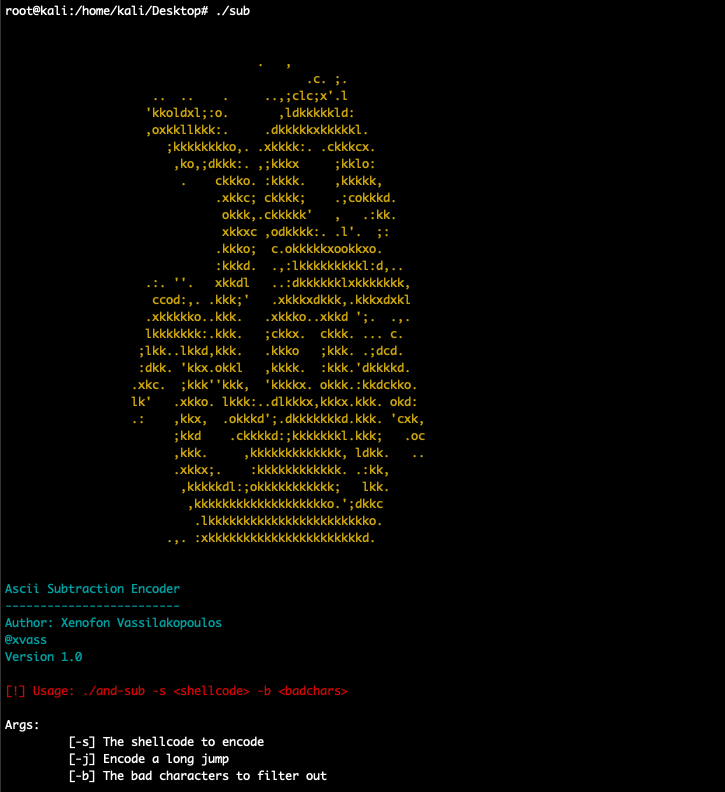
This is a custom ASCII AND/SUB Encoder developed during my preparation for the legacy OSCE/CTP course