
Exploit-Development
 wetw0rk/exploit-development
CVE-2020-8012, CVE-2016-10709, CVE-2017-17099, CVE-2017-18047, CVE-2019-1003000, CVE-2018-1999002
exploitationexploit-frameworkspayload-development+3
83
wetw0rk/exploit-developmentCVE-2020-8012, CVE-2016-10709, CVE-2017-17099, CVE-2017-18047, CVE-2019-1003000, CVE-2018-1999002
 jeromeyoung/cve-2021-27965
Proof of concept for CVE-2021-27965 (Stack-based Buffer Overflow)
 hakkuri01/r2rs
Interactive Ruby shell for authorized CVE-2025-55182 (react2shell) testing
 theleopard65/cve-2021-3156-baron-samedit
A simple Docker lab and Exploit setup for CVE-2021-3156 - "Baron Samedit".
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 m4sc3r4n0/astroid
ASTROID v 1.2 bypass most A.V softwares
 trustedsec/meterssh
MeterSSH is a way to take shellcode, inject it into memory then tunnel whatever port you want to over SSH to mask any type of communications as a…
 cryptolok/aslray
Linux ELF x32/x64 ASLR DEP/NX bypass exploit with stack-spraying
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool
 machine1337/gmailc2
A Fully Undetectable C2 Server That Communicates Via Google SMTP to evade Antivirus Protections and Network Traffic Restrictions
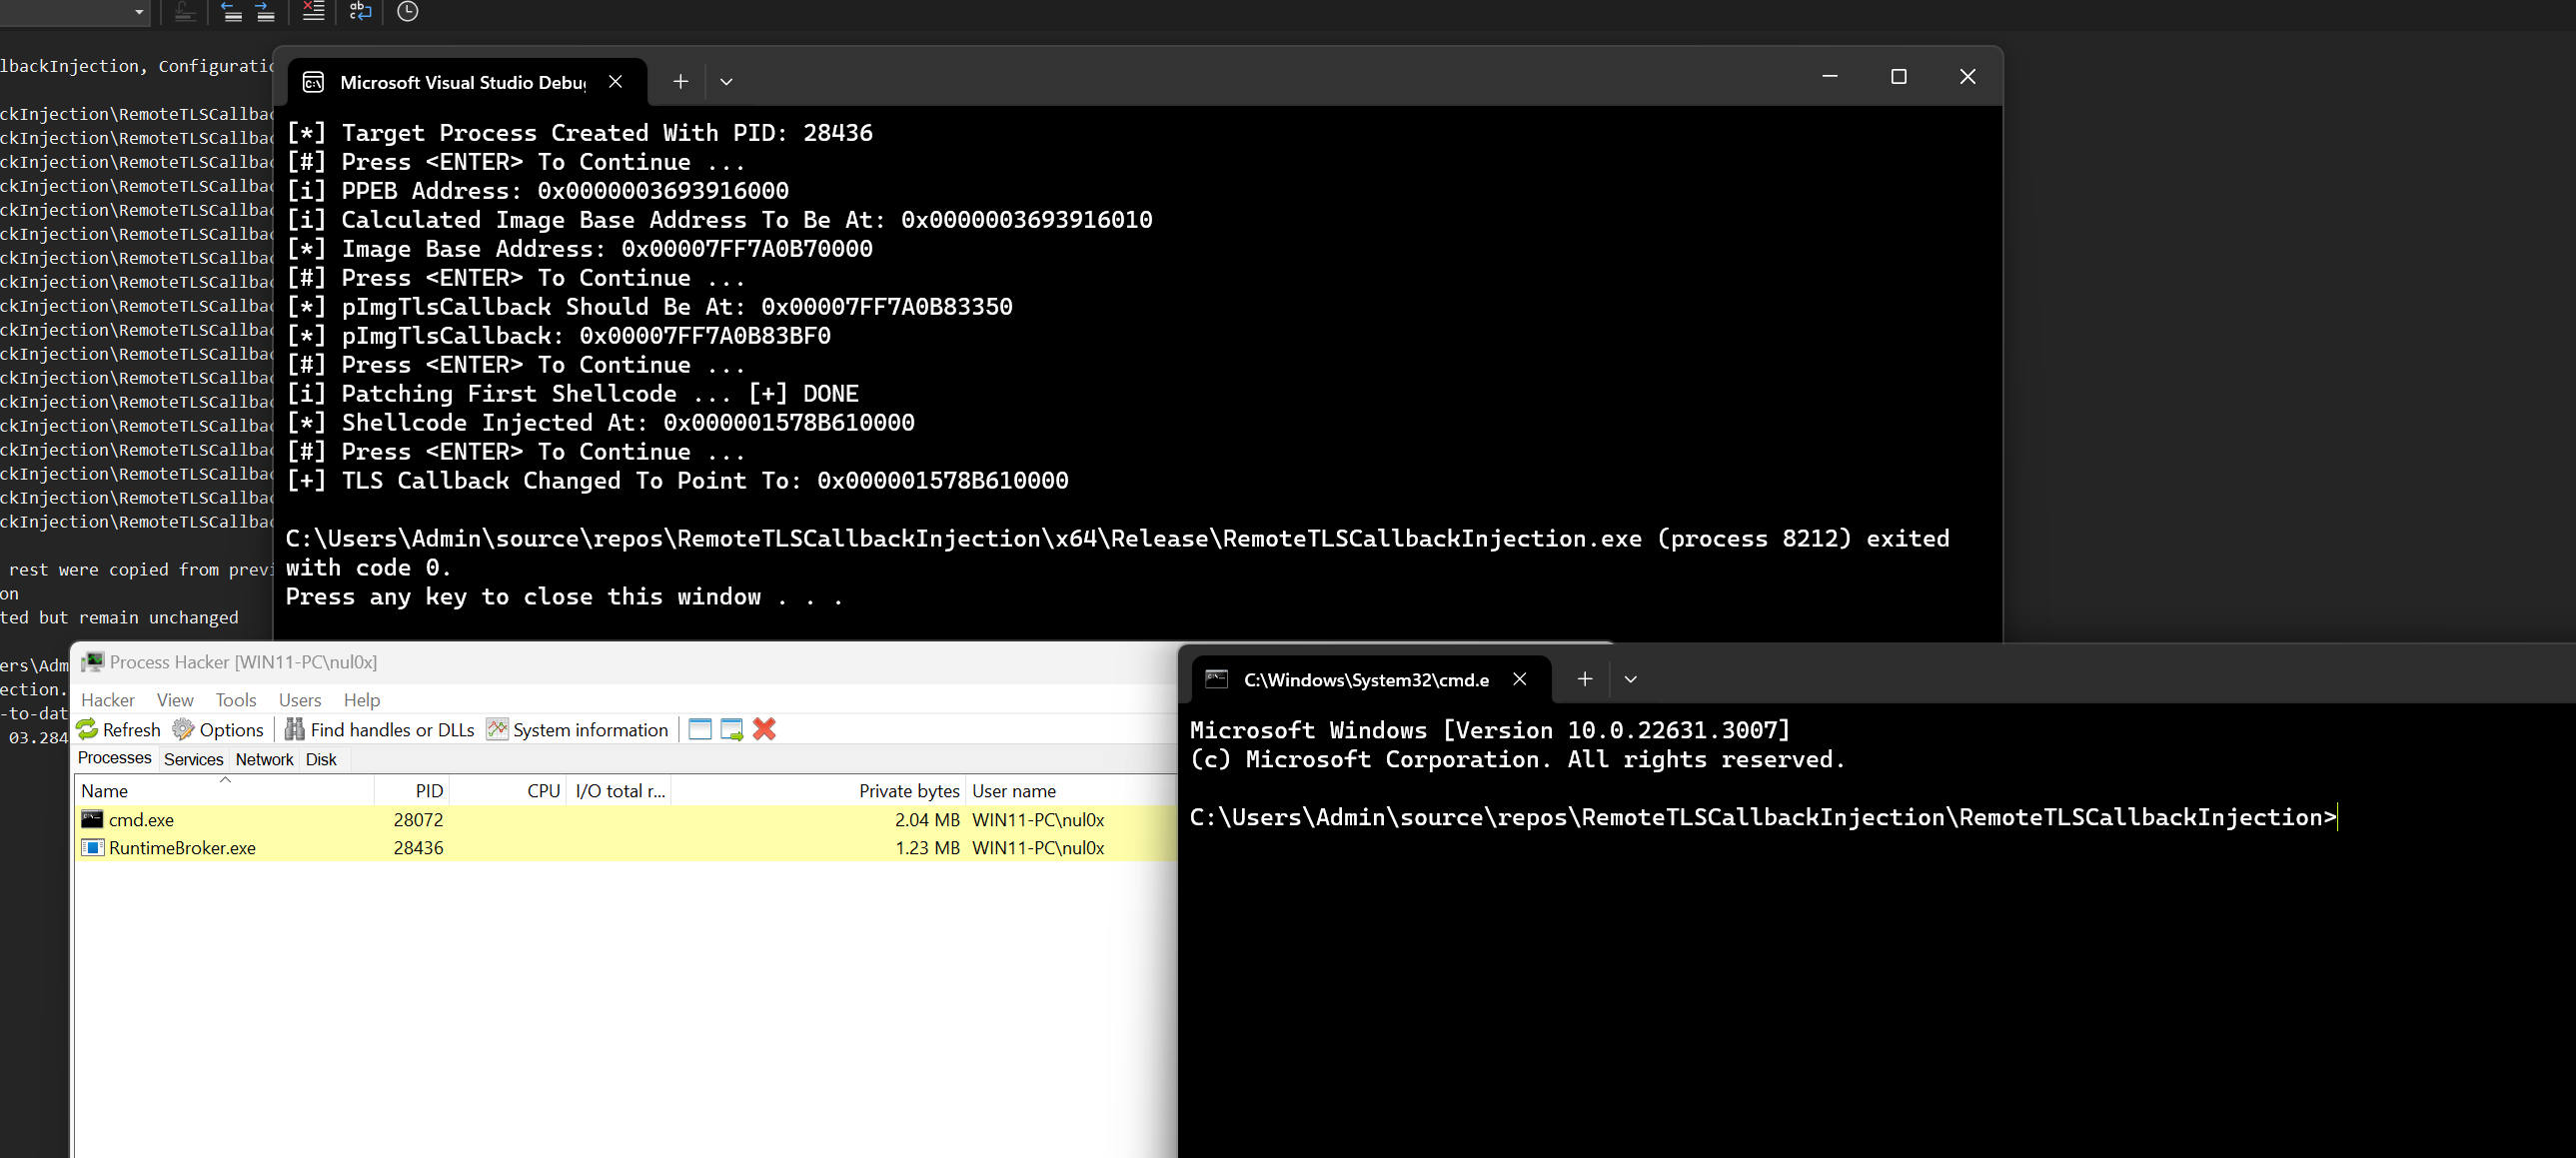 maldev-academy/remotetlscallbackinjection
Utilizing TLS callbacks to execute a payload without spawning any threads in a remote process
 enelg52/kittystager
KittyStager is a simple stage 0 C2. It is made of a web server to host the shellcode and an implant, called kitten. The purpose of this project is to…