

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.

 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
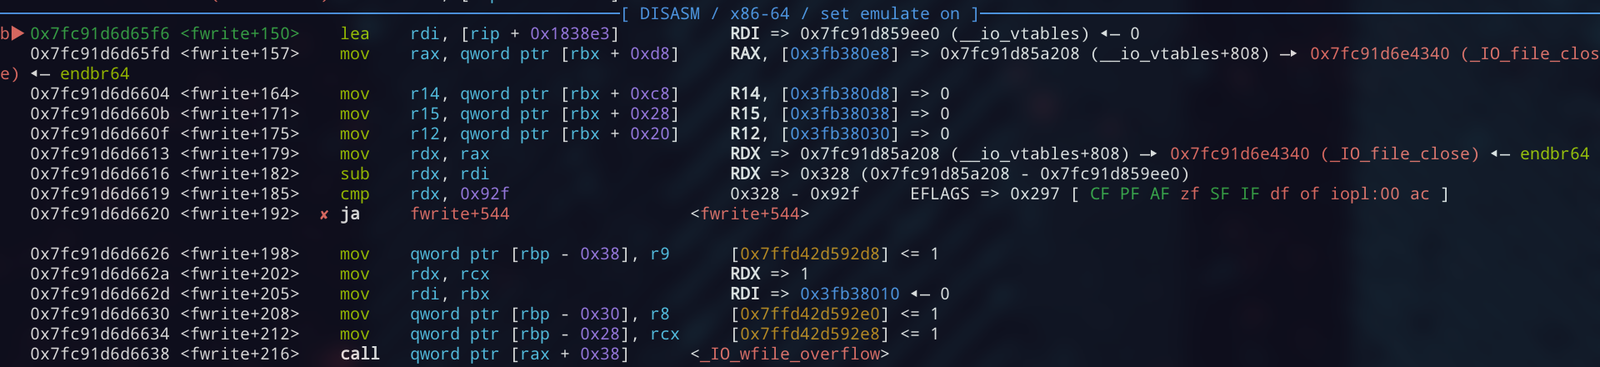 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 1llu50ry/mcp-gamehacking
MCP server exposing a 4,100+ skill game-hacking and reverse-engineering knowledge base with source archives, specialized agents, subagents, plugins…
 darthton/blackbone
Windows memory hacking library
 sk4r4b/ntdll-reconstruction
A technique that mixes NTDLL unhooking and hellsgate gate varients
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 sammyenigma/cve-2026-43499-s26
Android GKI 6.12 kernel exploit for CVE-2026-43499, chaining an rt_mutex rollback bug with pselect stack overwrite to gain root on Samsung and Pixel…
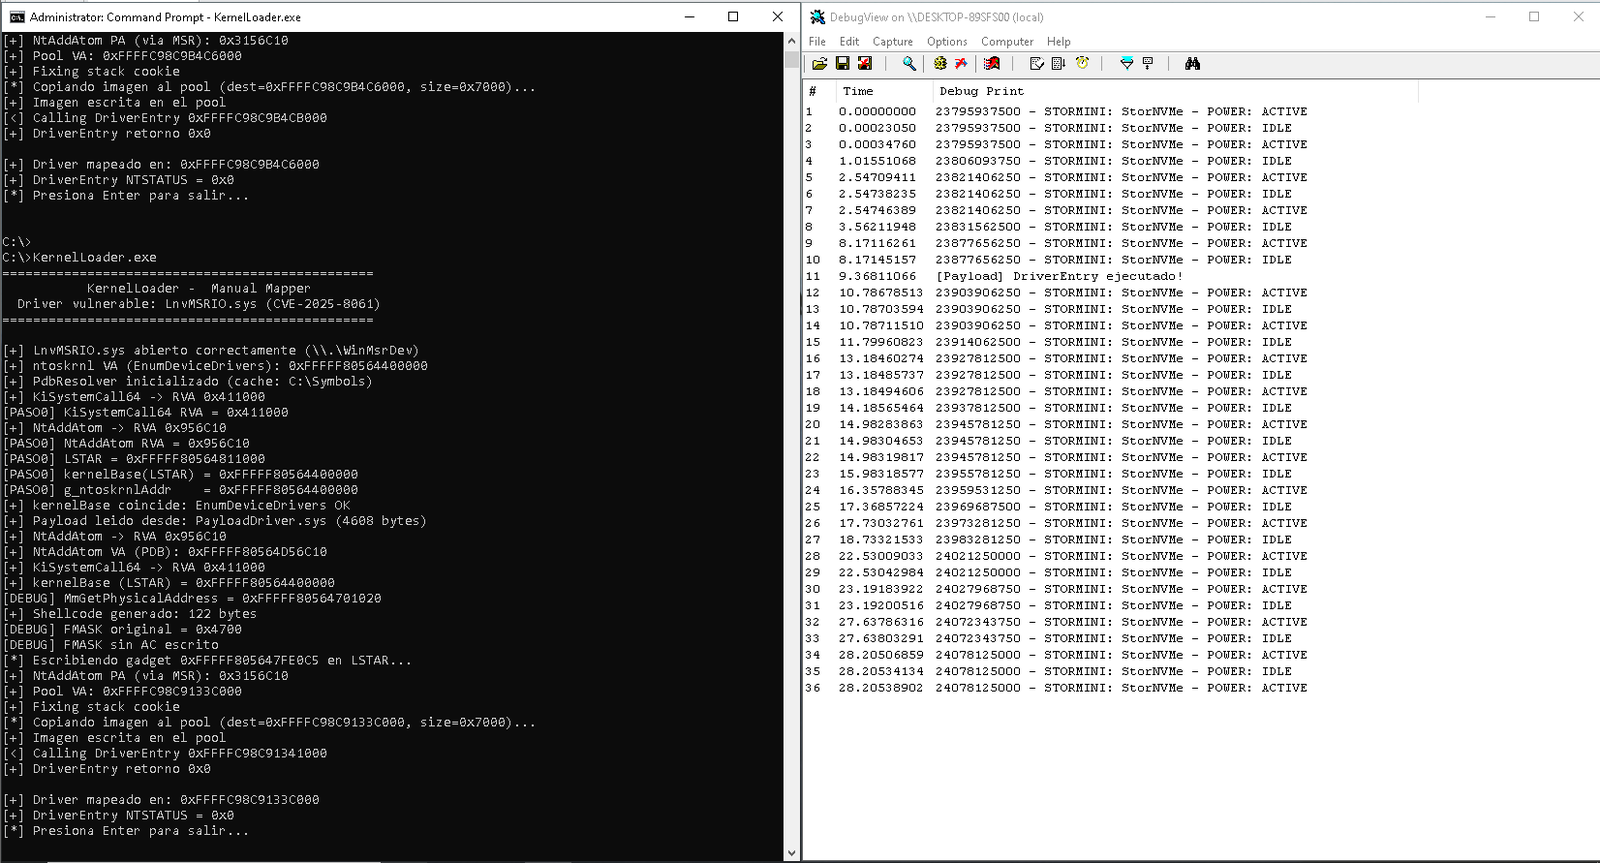 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…