
xsser
 varbaek/xsser
From XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
exploitationpayload-developmentpenetration-testing+3
varbaek/xsserFrom XSS to RCE 2.75 - Black Hat Europe Arsenal 2017 + Extras
 zeronohacker/cve-2019-9766
Free MP3 CD Ripper 2.6 版本中存在栈缓冲区溢出漏洞 (CVE-2019-9766),远程攻击者可借助特制的 .mp3 文件利用该漏洞执行任意代码。
 khaidtraivch/cve-2021-41773-apache-2.4.49-
Exploit scripts for CVE-2021-41773 (Apache 2.4.49) enabling path traversal and remote code execution via CGI, including a reverse shell payload.
 czeti/baron-samedit
This repository contains a Proof-of-Concept (PoC) exploit for the Baron Samedit vulnerability (CVE-2021-3156). The exploit demonstrates privilege…
 yzddmr6/java-shellcode-loader
基于Java实现的Shellcode加载器
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 sslab-gatech/pwn2own2020
Compromising the macOS Kernel through Safari by Chaining Six Vulnerabilities
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 namazso/linux_injector
A simple ptrace-less shared library injector for x64 Linux
 damariion/cve-2015-1925.rce
Stack-based buffer overflow in the server in IBM Tivoli Storage Manager FastBack 6.1 before 6.1.12 allows remote attackers to cause a denial of…
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader
 somecorp/copyfail-cve-2026-31431-workaround-bash
Provides a bash workaround script to mitigate CVE-2026-31431, preventing remote code execution via copy.fail exploit. Includes usage instructions for…
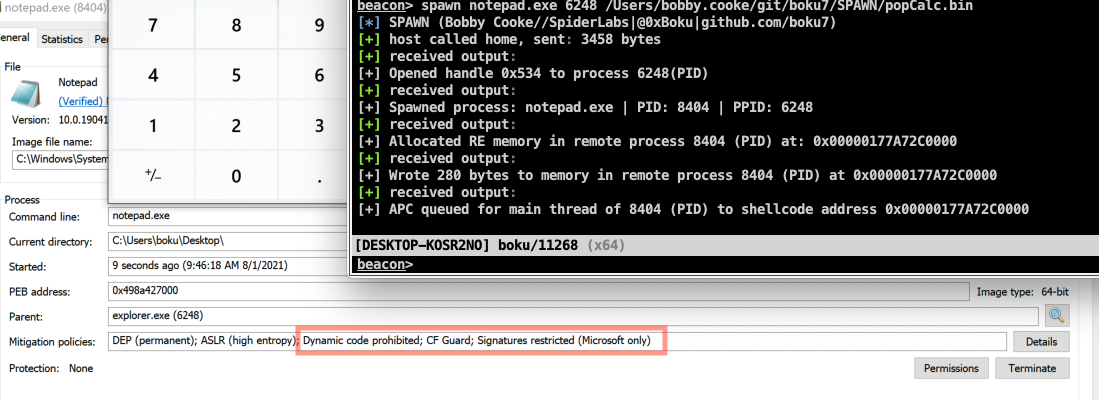 boku7/spawn
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…
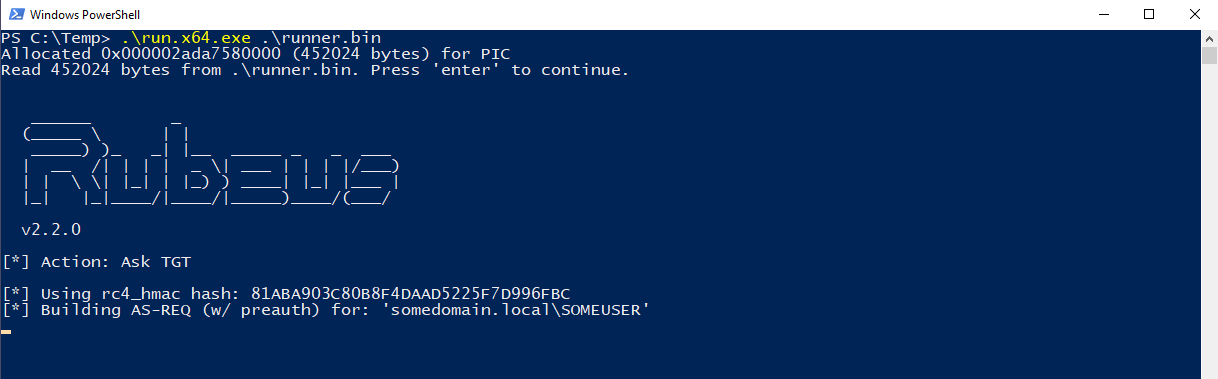 ofasgard/execute-assembly-pico
A PICO for Crystal Palace that implements CLR hosting to execute a .NET assembly in memory.
 l0n3m4n/cve-2024-6387
PoC - Remote Unauthenticated Code Execution Vulnerability in OpenSSH server (Scanner and Exploit)
 gildasio/wshlient
A simple tool to interact with web shells and command injection vulnerabilities