
PEzor-Docker
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!
educationexploitationpayload-generation+2
154 years ago
cyb3r-techie/pezor-dockerWith the help of this docker image, you can easily access PEzor on your system!
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 zznop/sploit
Go package that aids in binary analysis and exploitation
 zardus/ctf-tools
Some setup scripts for security research tools.
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 nhas/reverse_ssh
SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 sneakynachos/cve-2026-2764-but-with-wasm
Proof-of-concept exploit chain for Firefox JIT CVE-2026-2764, chaining JIT miscompilation and use-after-free into arbitrary read/write and WASM…
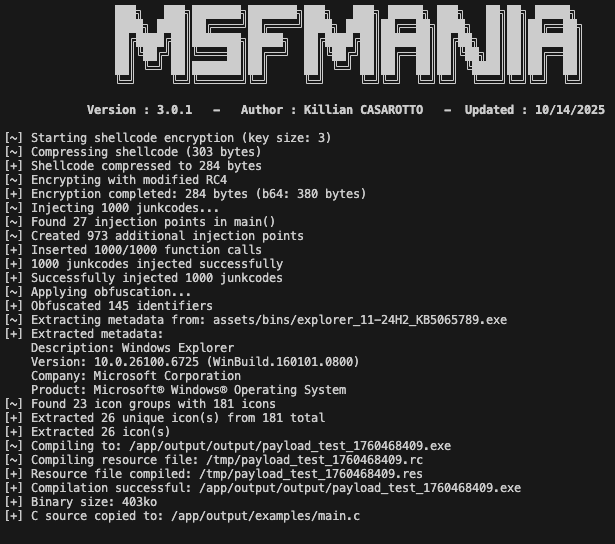 lepotekil/msfmania
Python AV Evasion Tools
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 vanivamshi/cve-2013-2028-exploit
Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…

 chvancooten/nimpackt-v1
Nim-based assembly packer and shellcode loader for opsec & profit
 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 hulnothutu/cve-2026-31431
对 CVE-2026-31431 的复现分析、C 改编的 exp。
 hujiaozhuzhu/cve-2025-55182_liyon
Python-based exploit for CVE-2025-55182 (React Server Components RCE) with interactive shell, reverse shell, batch scanning, and Docker-based…
 h3x0v3rl0rd/ms17-010_cve-2017-0143
MS17-010_CVE-2017-0143