
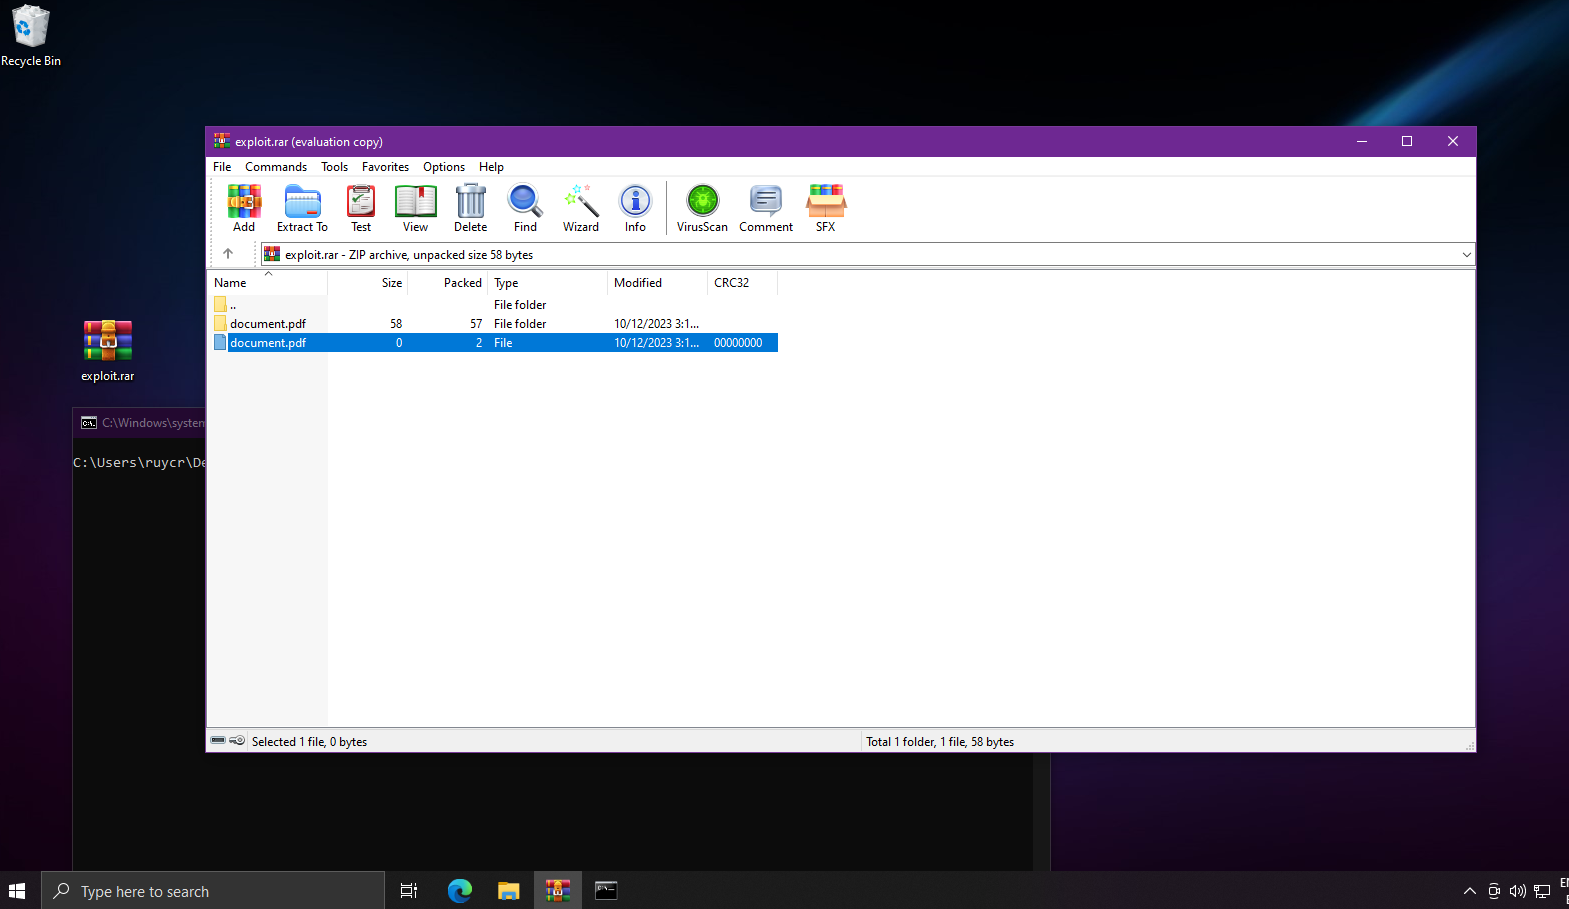
CVE-2023-38831
 ruycr4ft/cve-2023-38831
Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
exploitationpayload-generationpenetration-testing+3
1
ruycr4ft/cve-2023-38831Proof-of-concept exploit for CVE-2023-38831 targeting vulnerable versions, delivering a reverse shell via automated exploitation.
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 redsiege/excelntdonut
Excel 4.0 (XLM) Macro Generator for injecting DLLs and EXEs into memory.
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 redcode-labs/gosh
Golang reverse/bind shell generator
 a3h1nt/gimmesh
For pentesters who don't wanna leave their terminals.
 barriuso/smbghost_automateexploitation
SMBGhost (CVE-2020-0796) Automate Exploitation and Detection
 joelgmsec/invoke-stealth
Simple & Powerful PowerShell Script Obfuscator
 blindma1den/cve-2023-46818-exploit
This is my own exploit for CVE-2023-46818 happy hacking!
 dreadlocked/drupalgeddon2
Exploit for Drupal v7.x + v8.x (Drupalgeddon 2 / CVE-2018-7600 / SA-CORE-2018-002)
 blacknbunny/mcreator
Encoded Reverse Shell Generator With Techniques To Bypass AV's

 jasperla/cve-2017-9101
Authenticated remote code execution exploit for PlaySMS 1.4 via CSV phonebook upload. Provides single-command and interactive shell modes for…
 sec13b/ms09-050_cve-2009-3103
CVE-2009-3103 ms09-050
 cbwang505/cve-2019-0708-exp-windows
CVE-2019-0708-EXP-Windows版单文件exe版,运行后直接在当前控制台反弹System权限Shell
 hatriot/shellme
simple shellcode generator
 orangepirate/cve-2018-9948-9958-exp
a exp for cve-2018-9948/9958 , current shellcode called win-calc
 mzeyong/cve-2017-13089
CVE-2017-13089