
GoSH
 redcode-labs/gosh
Golang reverse/bind shell generator
exploitationpayload-developmentpayload-generation+4
redcode-labs/goshGolang reverse/bind shell generator
 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 inf0secrabbit/badassmacros
C# tool that generates malicious VBA macros with shellcode injection, VBA purging, and sandbox detection for red team operations.
 aniqfakhrul/sharperner
Simple executable generator with encrypted shellcode.
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 sensepost/ruler
A tool to abuse Exchange services
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 zerx0r/dvenom
🐍 Double Venom (DVenom) is a tool that provides an encryption wrapper and loader for your shellcode.
 u20024804/bash-4.3-fixed-cve-2014-6271
Patched GNU Bash 4.3 with fix for Shellshock (CVE-2014-6271). Provides a secure Bourne Again SHell with command-line editing, job control, and…
 u20024804/bash-3.2-fixed-cve-2014-6271
Patched GNU Bash 3.2 with a fix for CVE-2014-6271 (Shellshock). Provides a standard POSIX shell with command-line editing, job control, and history…
 egebalci/amber
Reflective PE packer.
 0xsch1zo/nullgate
Library that eases the use of indirect syscalls. Quite interesting AV/EDR bypass as PoC.
 nickvourd/supernova
Multi-cipher shellcode encryptor and obfuscator with automatic output conversion to C, C#, Rust, Nim, Python, and more. Supports ROT, XOR, RC4, AES,…
 buzzer-re/shinigami
A dynamic unpacking tool
 d3ext/dfshell
Python-based forward shell tool that creates a TTY-like interactive shell over HTTP using named pipes, enabling command execution on firewalled…
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
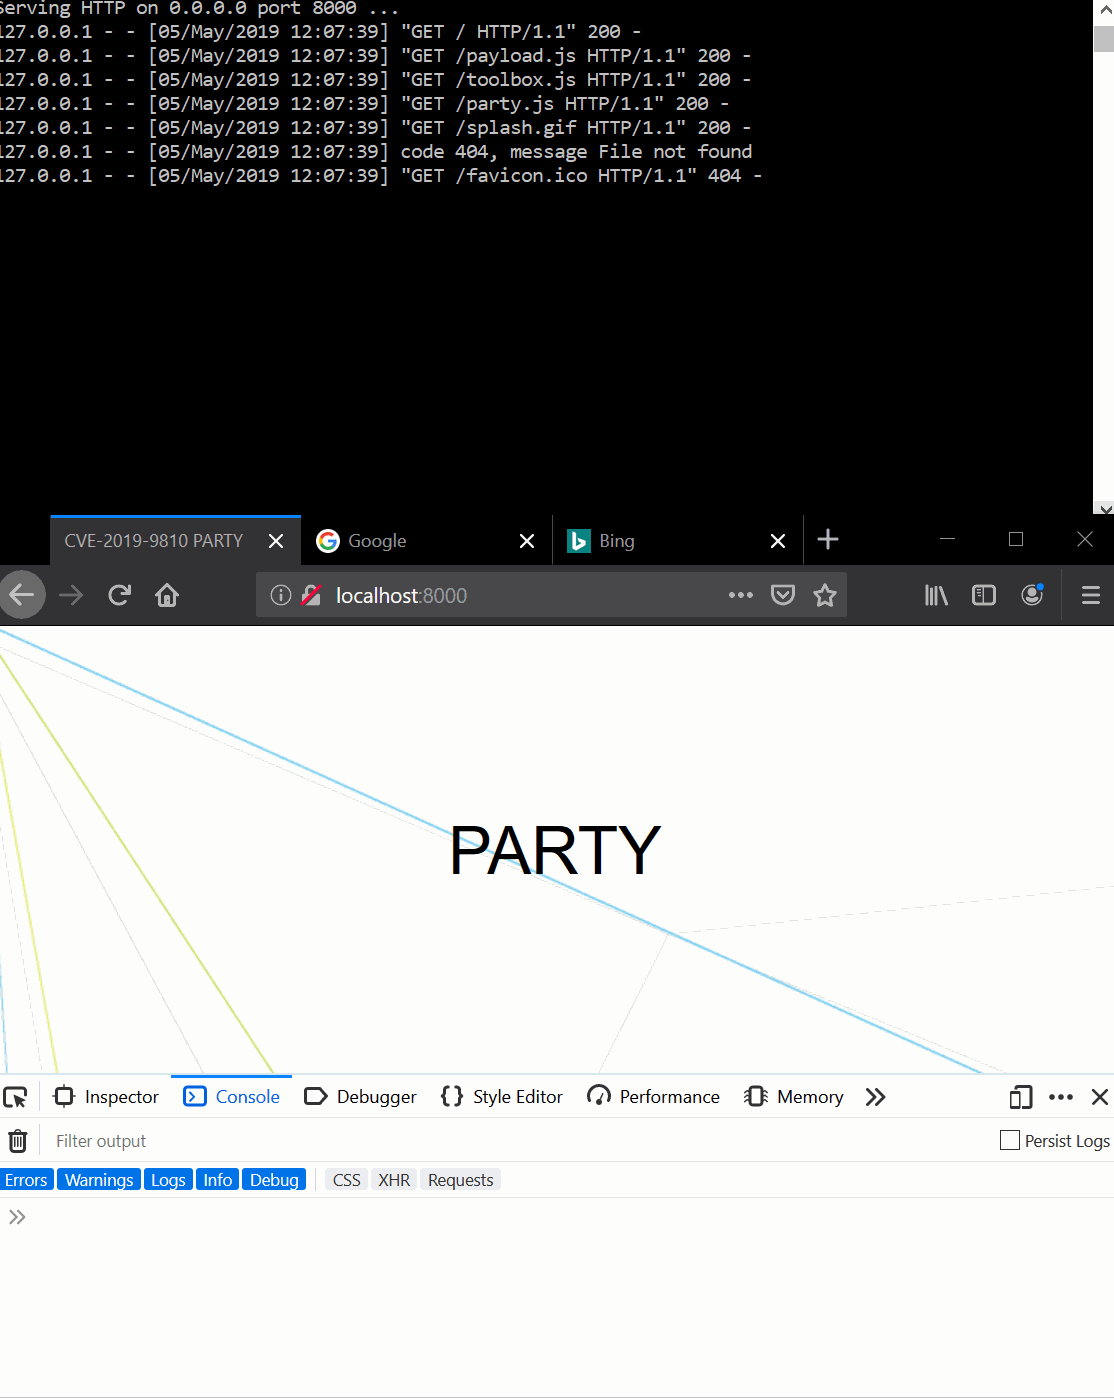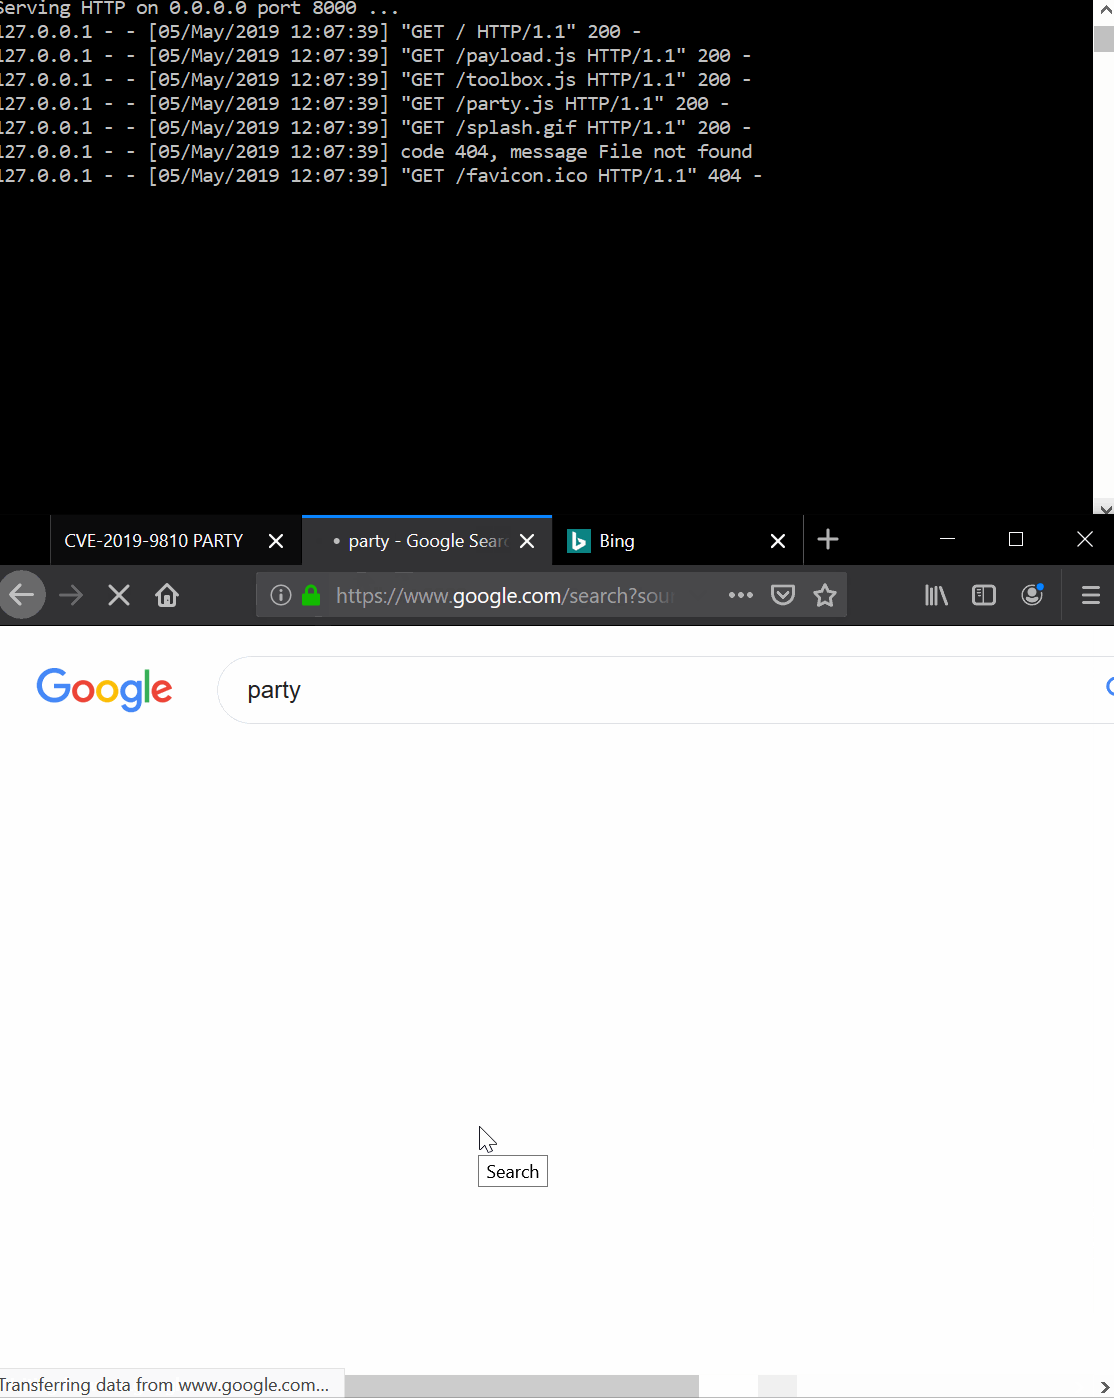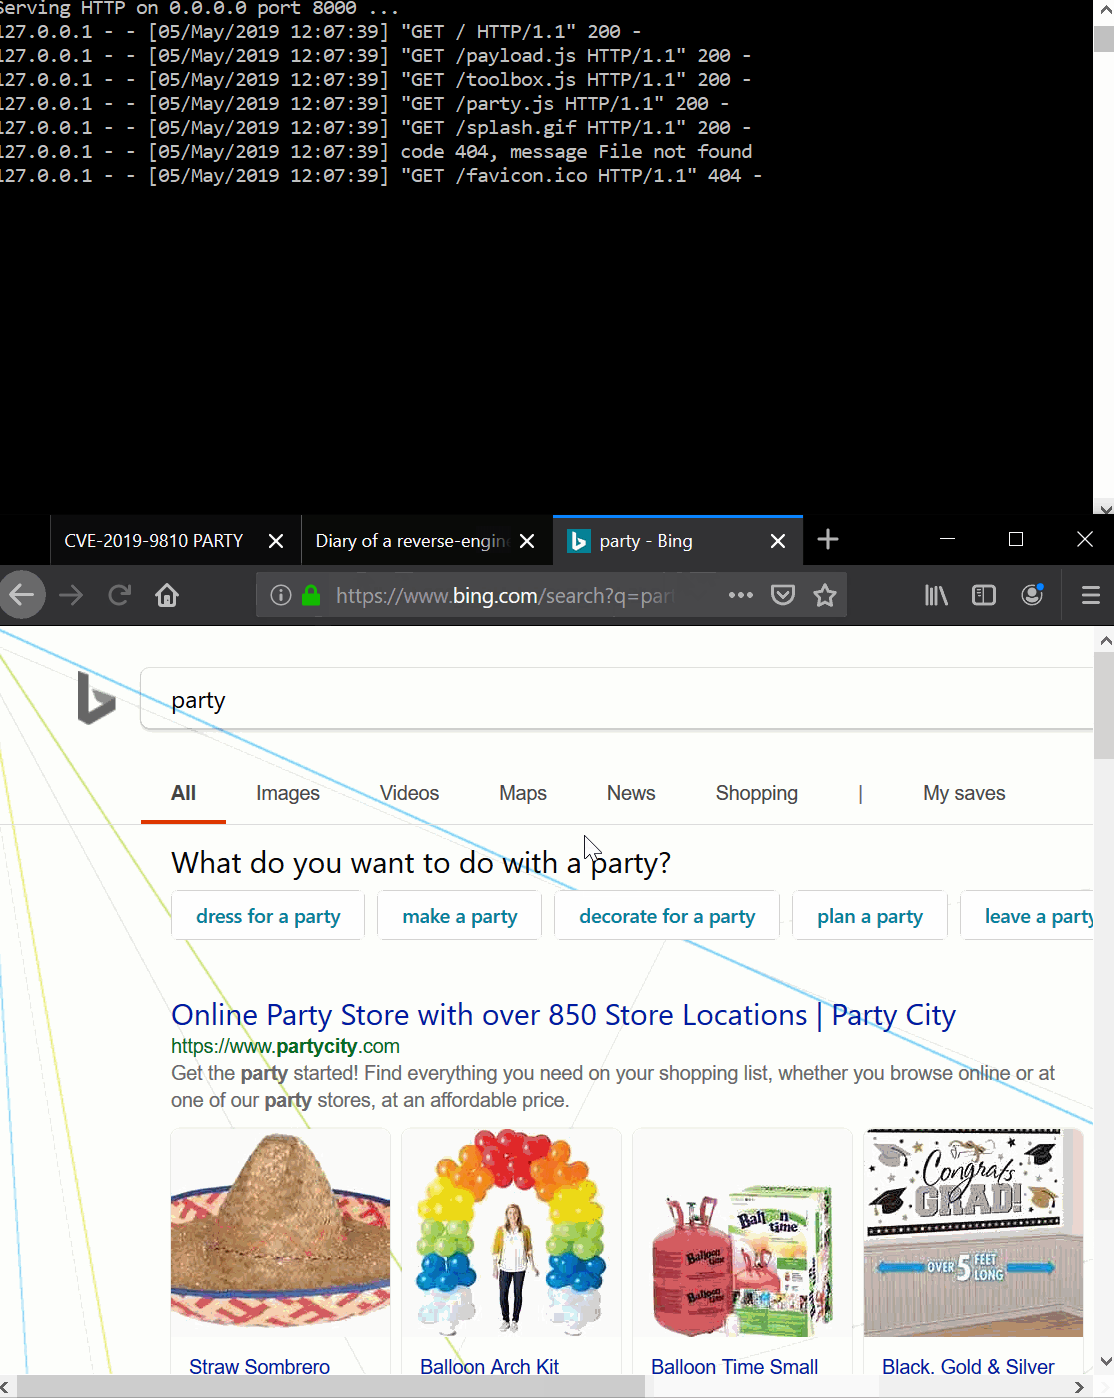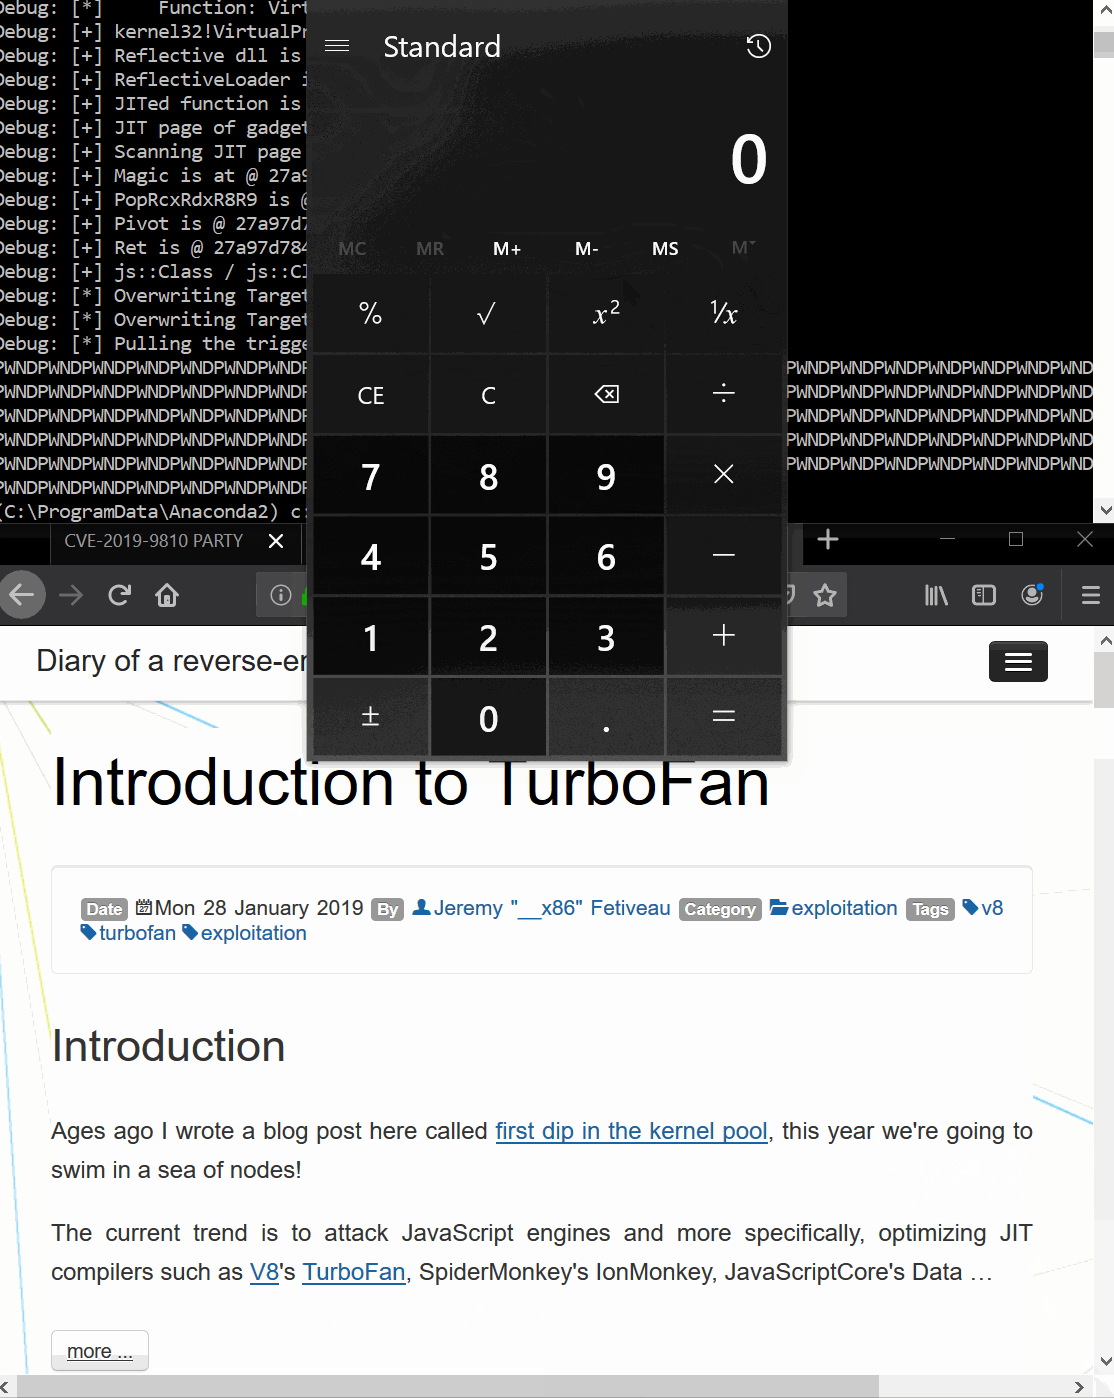 0vercl0k/cve-2019-9810
Exploit for CVE-2019-9810 Firefox on Windows 64-bit.