

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 cyb3r-techie/pezor-docker
With the help of this docker image, you can easily access PEzor on your system!
 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
 0dayctf/reverse-shell-generator
Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 zardus/ctf-tools
Some setup scripts for security research tools.
 klezvirus/syswhispers3
SysWhispers on Steroids - AV/EDR evasion via direct system calls.
 trickster0/offensiverust
Rust Weaponization for Red Team Engagements.
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
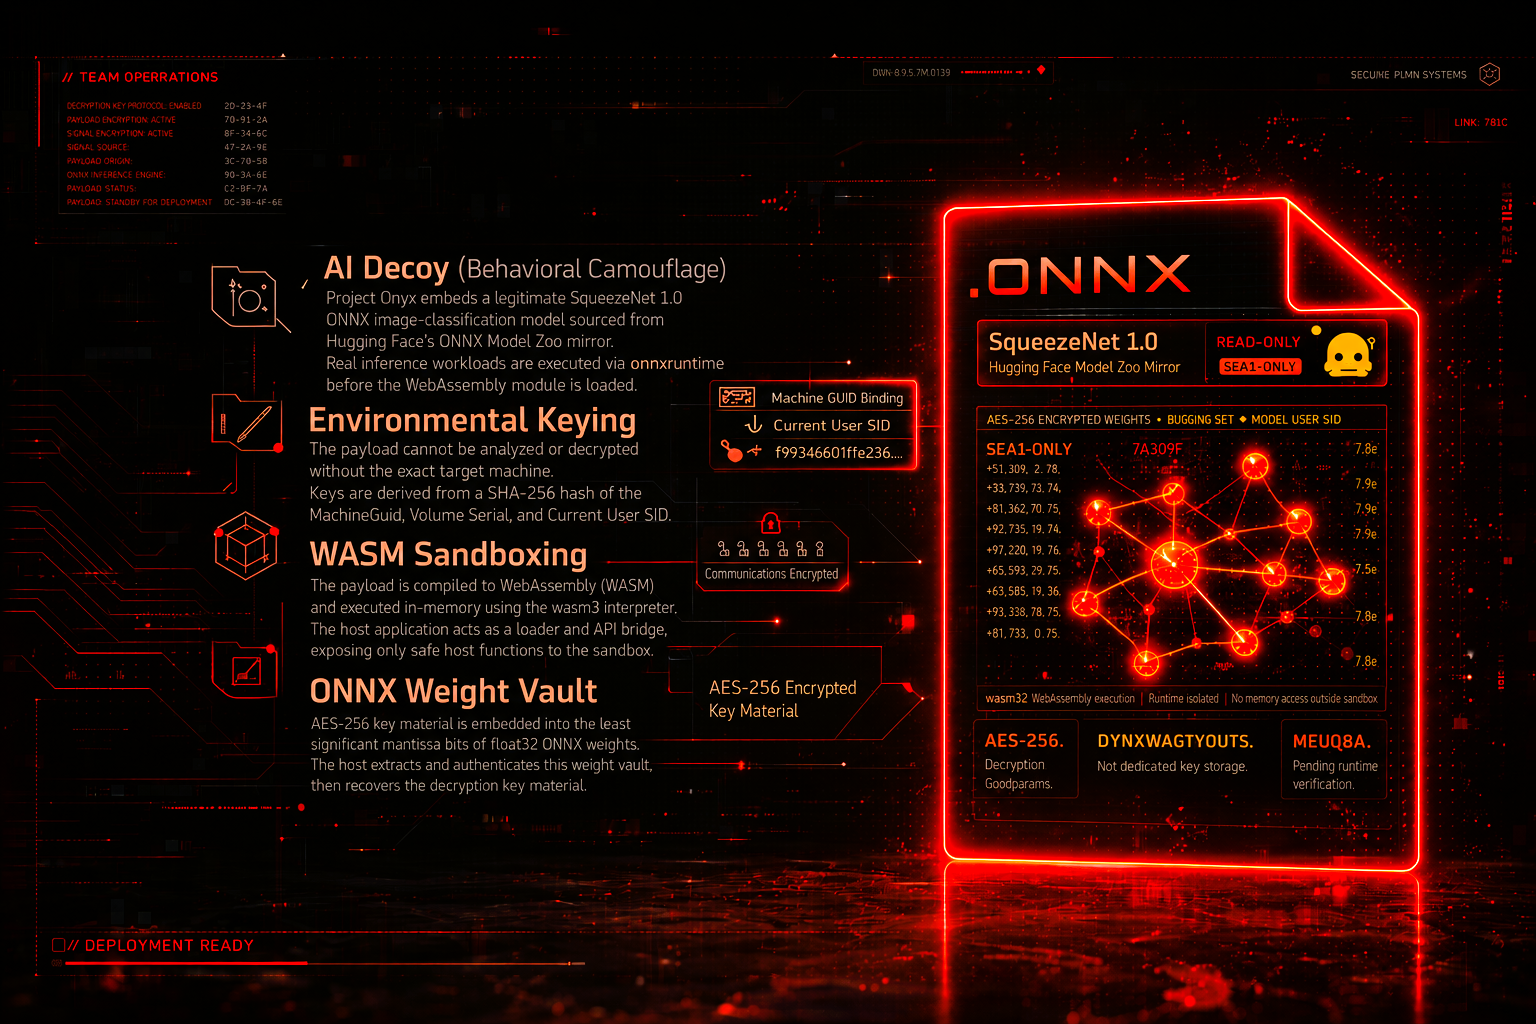 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
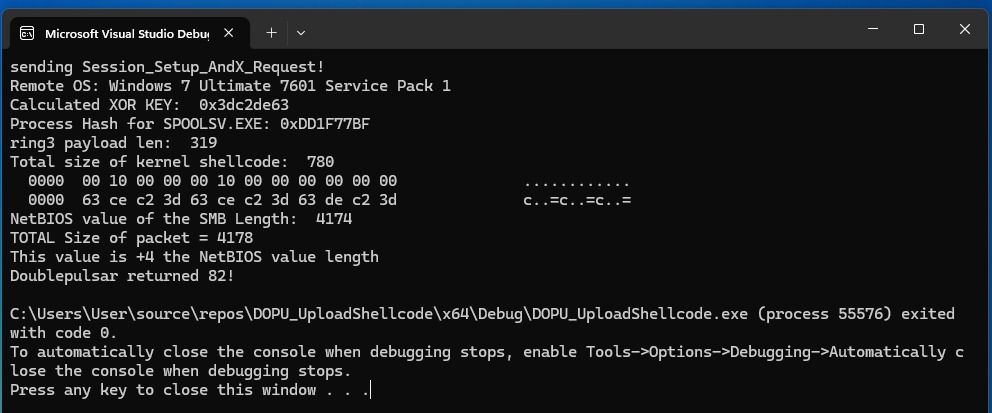 bhassani/eternalbluec
EternalBlue suite remade in C/C++ which includes: MS17-010 Exploit, EternalBlue vulnerability detector, DoublePulsar detector and DoublePulsar…
 s0lst1c3/dropengine
DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
 petrusviet/cve-2019-11581
Atlassian Jira unauthen template injection
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.