
Exploits + Shellcode + GHDB
 exploit-database/exploitdb
exploitdb // The official Exploit-Database repository
curated-resourceseducationexploitation+7
260
exploit-database/exploitdbexploitdb // The official Exploit-Database repository
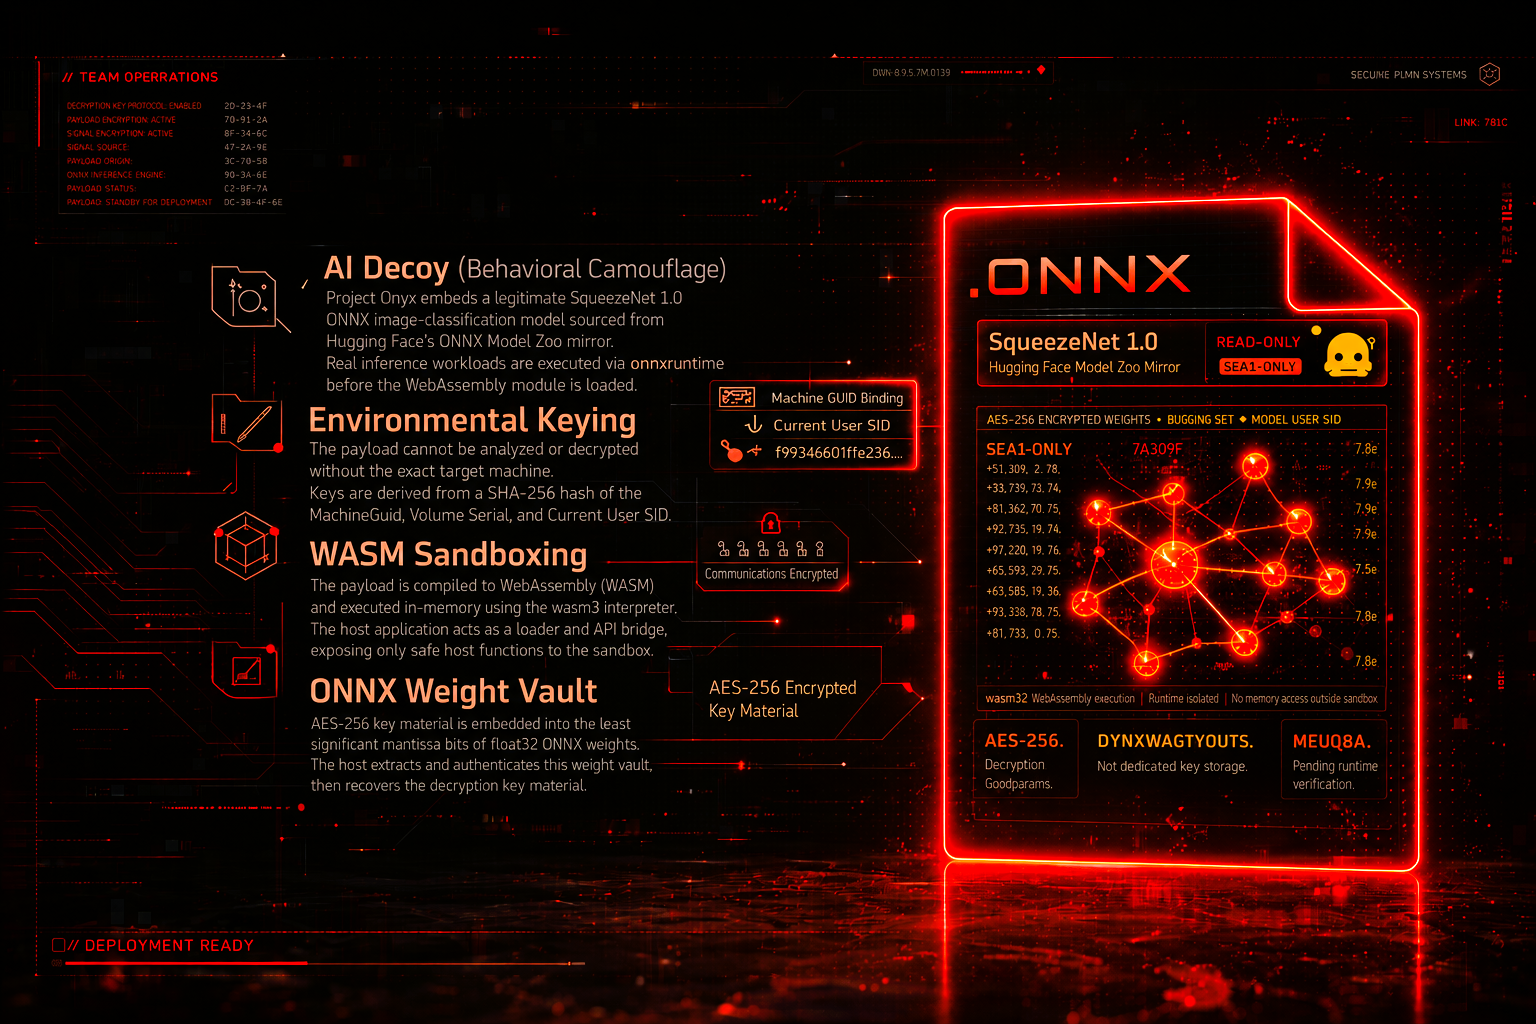
 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
 blacksnufkin/novaldr
Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
 allevon412/teamsimplant
Stealthy DLL proxying implant for Microsoft Teams that injects AES-encrypted shellcode via unhooking techniques, providing persistent backdoor access…
 nettitude/runpe
C# Reflective loader for unmanaged binaries.
 ch0pin/aviator
Antivirus evasion project
 sysdream/hershell
Hershell is a simple TCP reverse shell written in Go.
 an00brektn/gopher47
A third-party Gopher Assassin for the Havoc Framework.
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 bishopfox/asminject
Heavily-modified fork of David Buchanan's dlinject project. Injects arbitrary assembly (or precompiled binary) payloads directly into x86-64, x86,…
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 wra7h/flavortown
Various ways to execute shellcode
 codewhitesec/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level

 ps1337/lastenzug
Socks4a proxy leveraging PIC, Websockets and static obfuscation on assembly level
 virtualalllocex/defcon-31-syscalls-workshop
Contains all the material from the DEF CON 31 workshop "(In)direct Syscalls: A Journey from High to Low".
 jephthai/evilvm
Forth-based compiler deployed as position-independent x86_64 shellcode, providing a remote code execution agent with interactive REPL over TCP, HTTP,…