

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
280 results
sliver preview

sliver

GitHubbishopfox/sliver

Adversary Emulation Framework

adversarial-attackcommand-and-controldata-exfiltration+16
12.2k3 days ago
KDU preview

KDU

GitHubhfiref0x/kdu

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…

binary-exploitationdefensive-toolsexploitation+8
2.8k29 days ago
phantom-frida preview

phantom-frida

GitHubtheqmaks/phantom-frida

Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.


android-securitybinary-analysisdynamic-analysis-sandboxing+7
4013 months ago
Exploits + Shellcode + GHDB preview

Exploits + Shellcode + GHDB

GitLabexploit-database/exploitdb

exploitdb // The official Exploit-Database repository

curated-resourceseducationexploitation+7
2651 day ago
house_of_apple_2 preview

house_of_apple_2

GitHubjazho76/house_of_apple_2

Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
binary-exploitationdebuggerseducation+7
52 months ago
CVE-2024-31317-PoC-Deployer preview

CVE-2024-31317-PoC-Deployer

GitHubwebldix/cve-2024-31317-poc-deployer

Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
android-securitybinary-exploitationexploitation+5
571 year ago
PEzor-Docker preview

PEzor-Docker

GitHubcyb3r-techie/pezor-docker

With the help of this docker image, you can easily access PEzor on your system!

educationexploitationpayload-generation+2
154 years ago
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
exploitationids-ips-evasionmemory-forensics+7
2.6k4 years ago
reverse-shell-generator preview

reverse-shell-generator

GitHub0dayctf/reverse-shell-generator

Hosted Reverse Shell generator with a ton of functionality. -- (Great for CTFs)
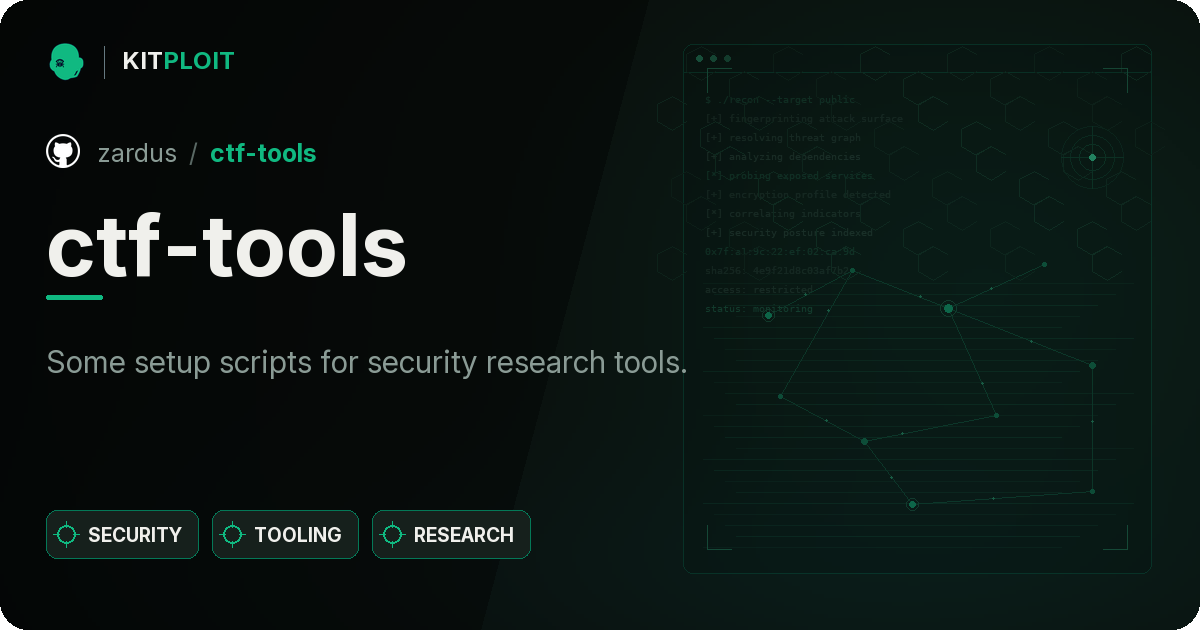
ctfexploitationpayload-development+6
4.1k6 months ago
ctf-tools preview

ctf-tools

GitHubzardus/ctf-tools

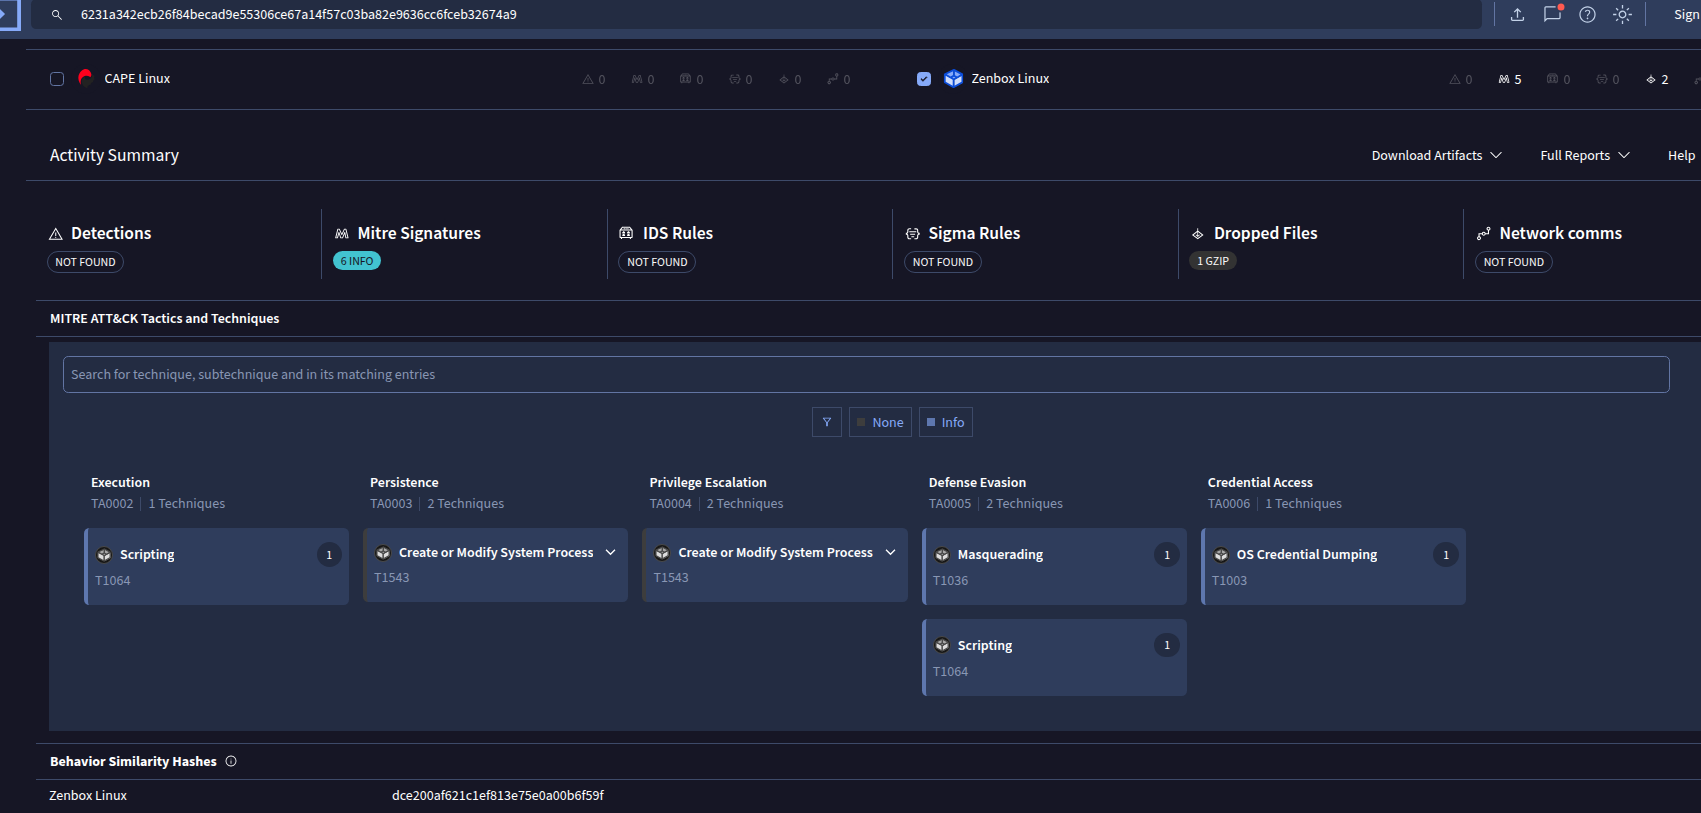
Some setup scripts for security research tools.
binary-analysiscryptographyctf+9
9.6k7 days ago
Phantom-Evasion-Loader preview

Phantom-Evasion-Loader

GitHubjm00nj/phantom-evasion-loader

x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…

binary-exploitationcommand-and-controleducation+6
1163 months ago
SysWhispers3 preview

SysWhispers3

GitHubklezvirus/syswhispers3

SysWhispers on Steroids - AV/EDR evasion via direct system calls.
defensive-toolsexploitationids-ips-evasion+5
1.7k2 years ago
Girsh preview

Girsh

GitHubnodauf/girsh

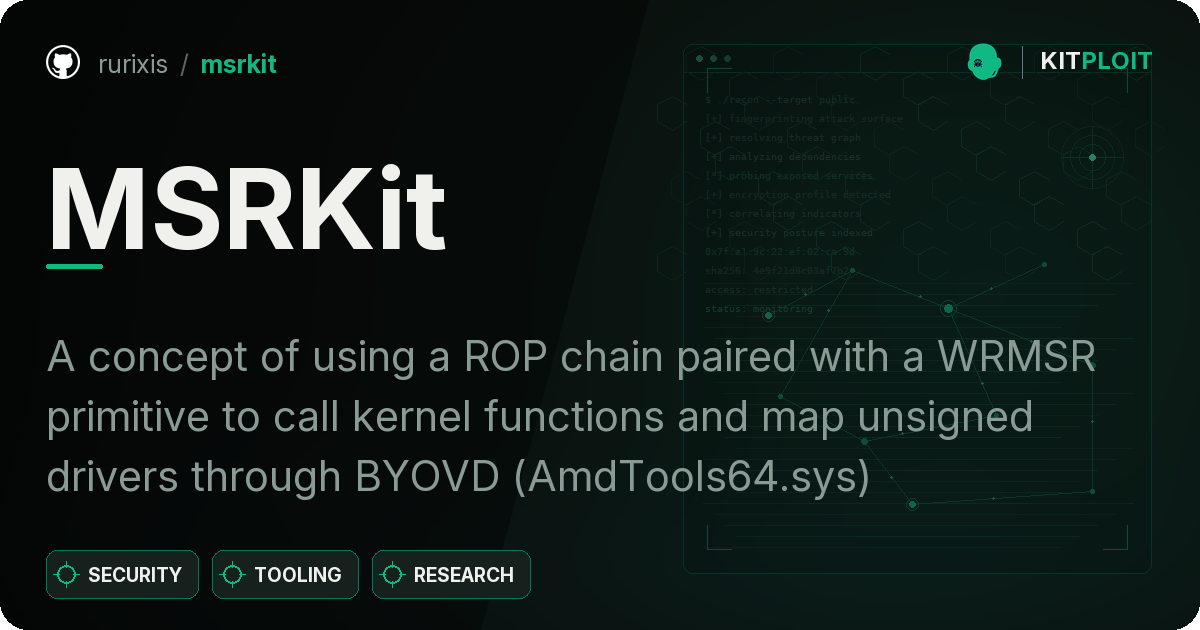
Automatically spawn a reverse shell fully interactive for Linux or Windows victim
command-and-controlexploitationpayload-generation+5
3593 years ago
MSRKit preview

MSRKit

GitHubrurixis/msrkit

A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)

binary-exploitationexploitationpayload-development+5
671 month ago
SyscallRevenant preview

SyscallRevenant

GitHubsilentisvox/syscallrevenant

Clean Indirect Syscalls with Syscall Tampering.

binary-exploitationexploitationids-ips-evasion+6
443 days ago
dropengine preview

dropengine

GitHubs0lst1c3/dropengine

DropEngine provides a malleable framework for creating shellcode runners, allowing operators to choose from a selection of components and combine…
defensive-toolsexploit-frameworkspayload-development+5
2135 years ago
InjectSetConsole preview

InjectSetConsole

GitHubtwosevenonet/injectsetconsole

Proof of Concept for Process Code Injection Without Using WriteProcessMemory

command-and-controlexploitationids-ips-evasion+7
1591 month ago
Fritter preview

Fritter

GitHub0xrootpls/fritter

Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…

binary-exploitationexploitationpayload-development+5
2602 months ago
Previous12…16Next
