
Archived
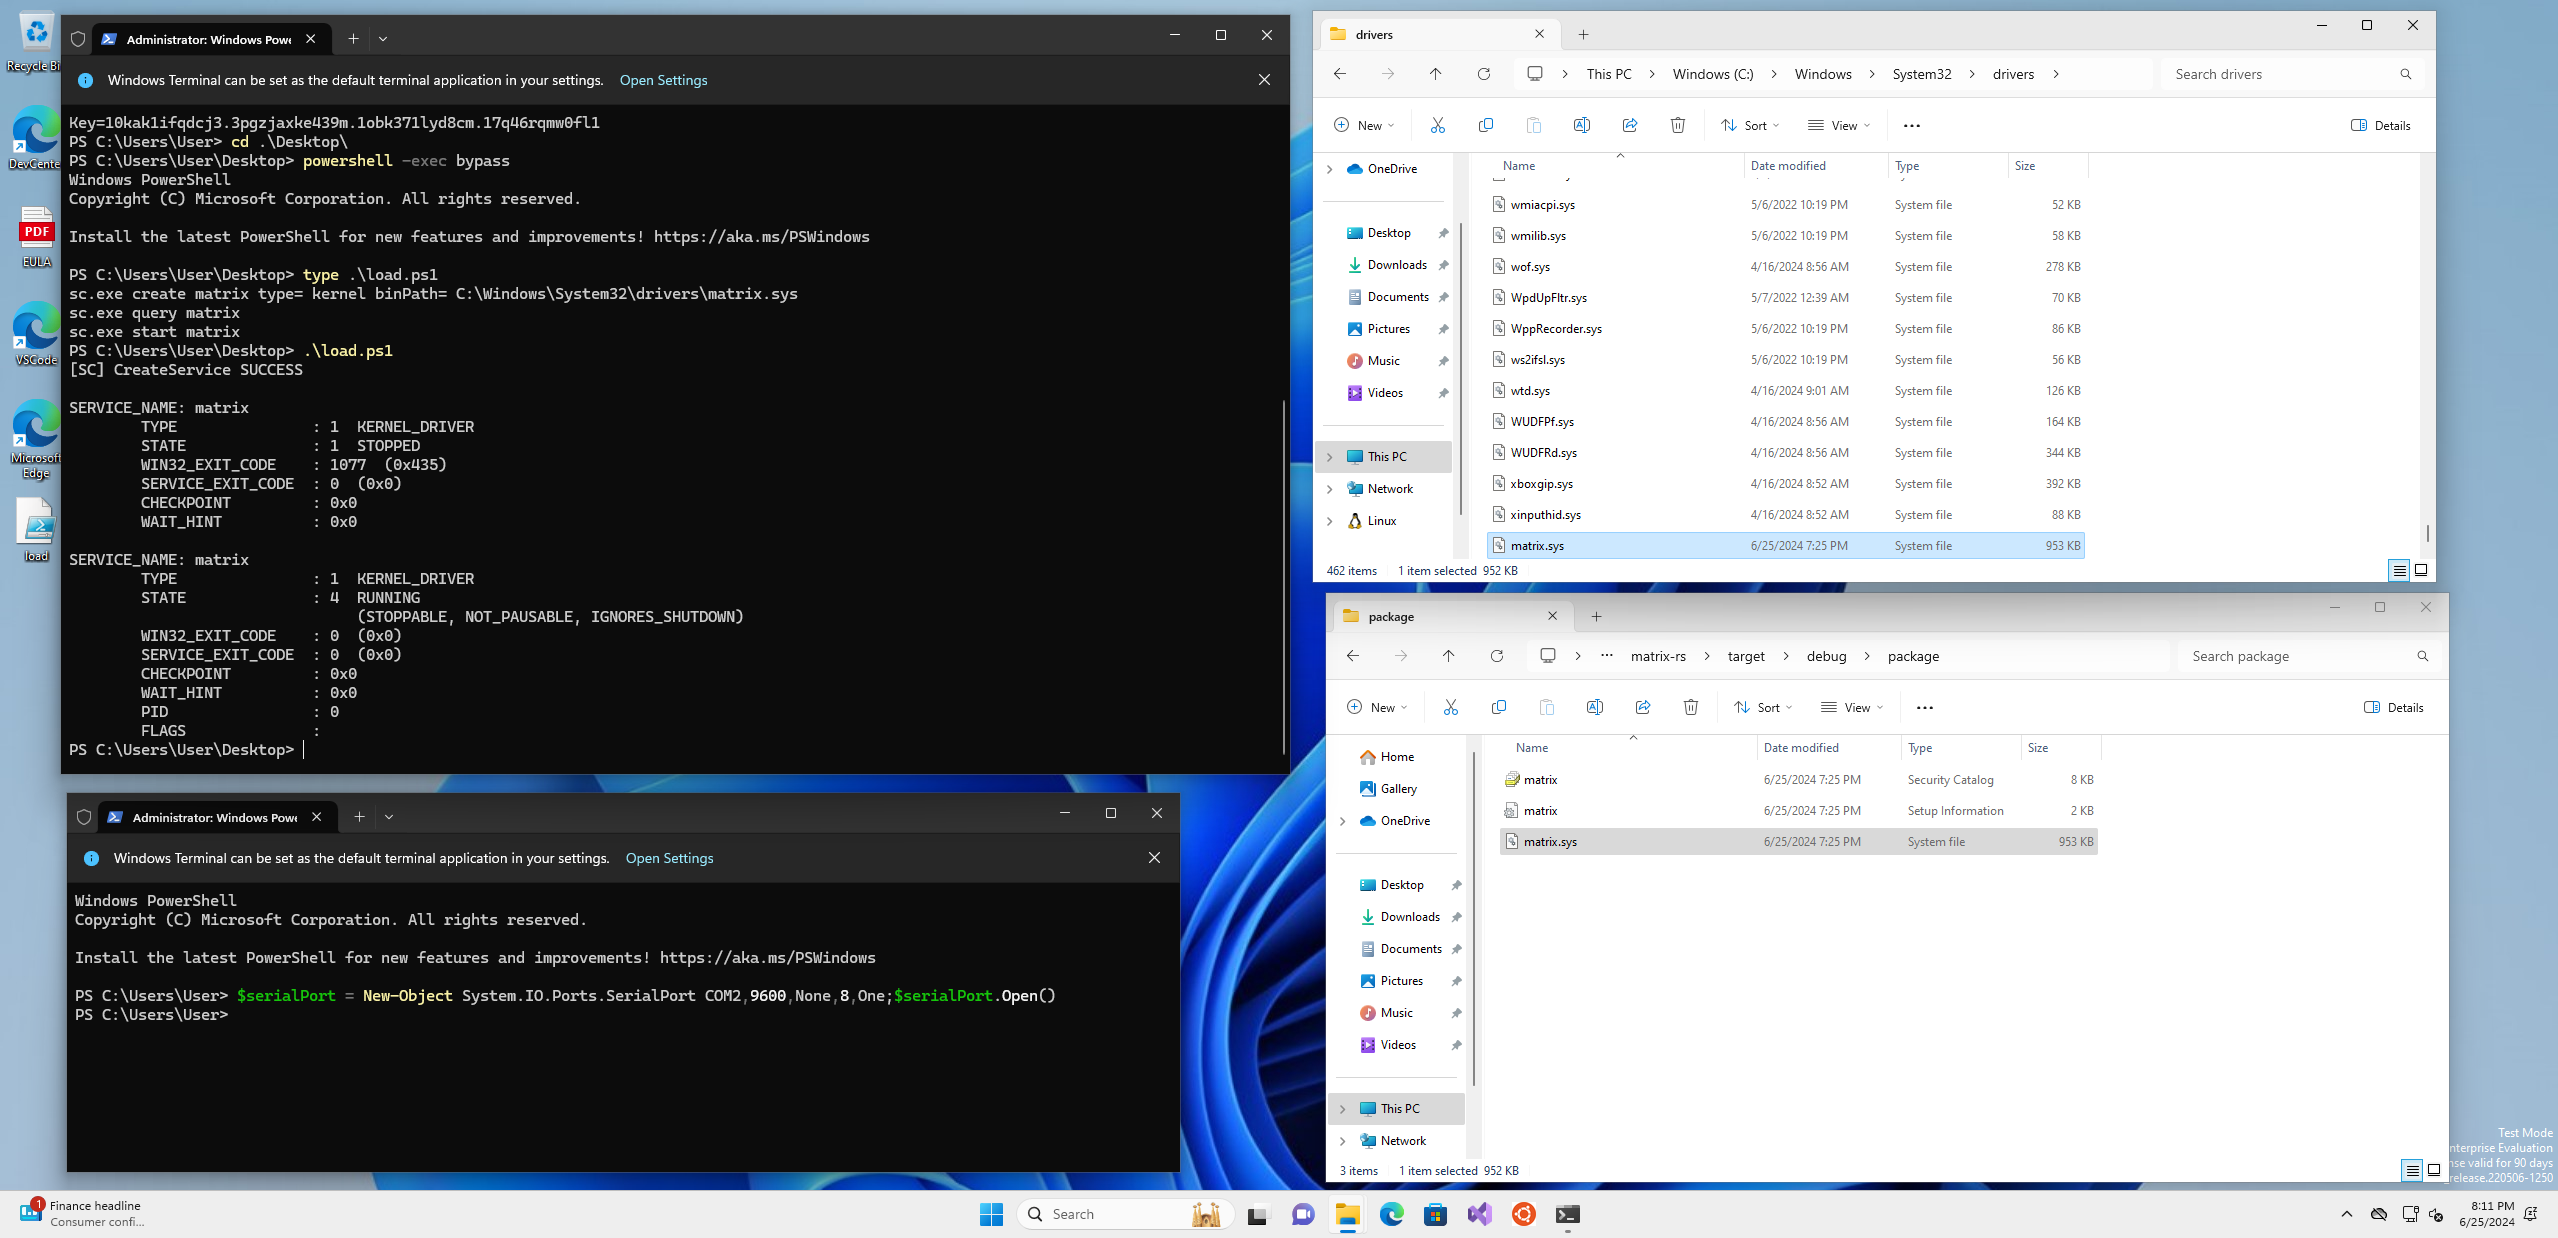
matrix-rs
 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
dynamic-code-analysiseducationids-ips-evasion+3
356
 yym8538/cve-2026-40897
Proof-of-concept exploit for CVE-2026-40897, a Math.js expression parser sandbox bypass enabling remote code execution via crafted payloads and a…
 pwnvader/cve-2026-87902-poc-pwnvader
Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
 1833ravikumar-max/cve-2021-41773-apache-path-traversal-lab
Docker-based cybersecurity lab for studying and reproducing CVE-2021-41773 in an isolated environment.
 shivammittal2403/cve-2026-59827-metabase-cyber-range
Educational cyber range for CVE-2026-59827 (Metabase H2 unsafe deserialization / CWE-502). Isolated Docker lab — training only, not for attacking…
 jinook-kim/cve-2025-64512_poc
Python PoC for CVE-2025-64512, a pdfminer.six pickle deserialization RCE. Generates gzipped pickle payloads and polyglot PDFs, then delivers them to…
 aramosf/cve-2026-61500
Python PoC and Docker lab for CVE-2026-61500: recovers Rejetto HFS V8 PRNG state to forge an admin session cookie and achieve RCE via server_code.
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…
 guneykabel/cve-2026-85706
Python PoC exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass, with writeup and…
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 eqstlab/cve-2026-49869
PoC and Docker lab for CVE-2026-49869, an unauthenticated RCE in Kestra OSS via an AuthenticationFilter path bypass that allows flow creation and…
 abraxas/cve-2026-5430
Disclosure pack and Python PoC for CVE-2026-5430, a JWT algorithm-confusion flaw in WSO2 API Manager 4.5.0 enabling unauthenticated admin account…
 hassham1/cve-2026-12227-visualcomposer-lfi-poc
Docker validation lab and safe-oracle PoC for CVE-2026-12227, an unauthenticated LFI in Visual Composer via vcv-template, with a nuclei detection…
 abraxas/cve-2026-22599
Python PoC and Docker lab for CVE-2026-22599, an authenticated SQL injection in Strapi's Content-Type Builder write API via Knex raw defaultTo.
 hassham1/cve-2026-89274-wp-recipe-maker-poc
Docker validation lab and Python PoC for CVE-2026-89274, proving arbitrary shortcode execution in WP Recipe Maker <= 10.8.1 via rating-comment…
 abraxas/cve-2026-48356
Proof-of-concept and lab pack for CVE-2026-48356, an unauthenticated unrestricted file upload in Magento Open Source guest-cart REST custom options.