

BEAR-C2
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
adversarial-attackcommand-and-controldata-exfiltration+8
687
s3n4t0r-0x0/bear-c2The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 squeeze440/zotlit-poc
PoC — attachment import copies files from unapproved local paths in ZotLit (GHSA-4qh7-66xv-h329, CVE-2026-87000, CVSS 5.5).
 qubesos/qvm-create-windows-qube
Spin up new Windows qubes quickly, effortlessly and securely on Qubes OS
 cisagov/esxiargs-recover
A tool to recover from ESXiArgs ransomware
 mimi89999/webauthn_tpm_portable
Portable, hardware-backed WebAuthn credentials using TPM 2.0. Deterministic parent key derived from a master seed enables cross-device credential…
 anantaakotal/agentcyte
Generates reproducible CORE network topologies from XML scenario files for cybersecurity training and experimentation. Provides Web GUI and CLI for…
 remnux/distro
Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
 0xcyberstan/cve-2026-59346-poc
PoC for CVE-2026-59346 - 32-bit integer overflow in VMware's VMXNET3 TSO segmentation path, guest-to-host crash.
 sinakarvandi/hypervisor-from-scratch
Source code of a multiple series of tutorials about the hypervisor. Available at: https://rayanfam.com/tutorials
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
 rapid7/metasploitable3
Metasploitable3 is a VM that is built from the ground up with a large amount of security vulnerabilities.
 d4rksystem/vmwarecloak
A PowerShell script that attempts to help malware analysts hide their VMware Windows VM's from malware that may be trying to evade analysis.
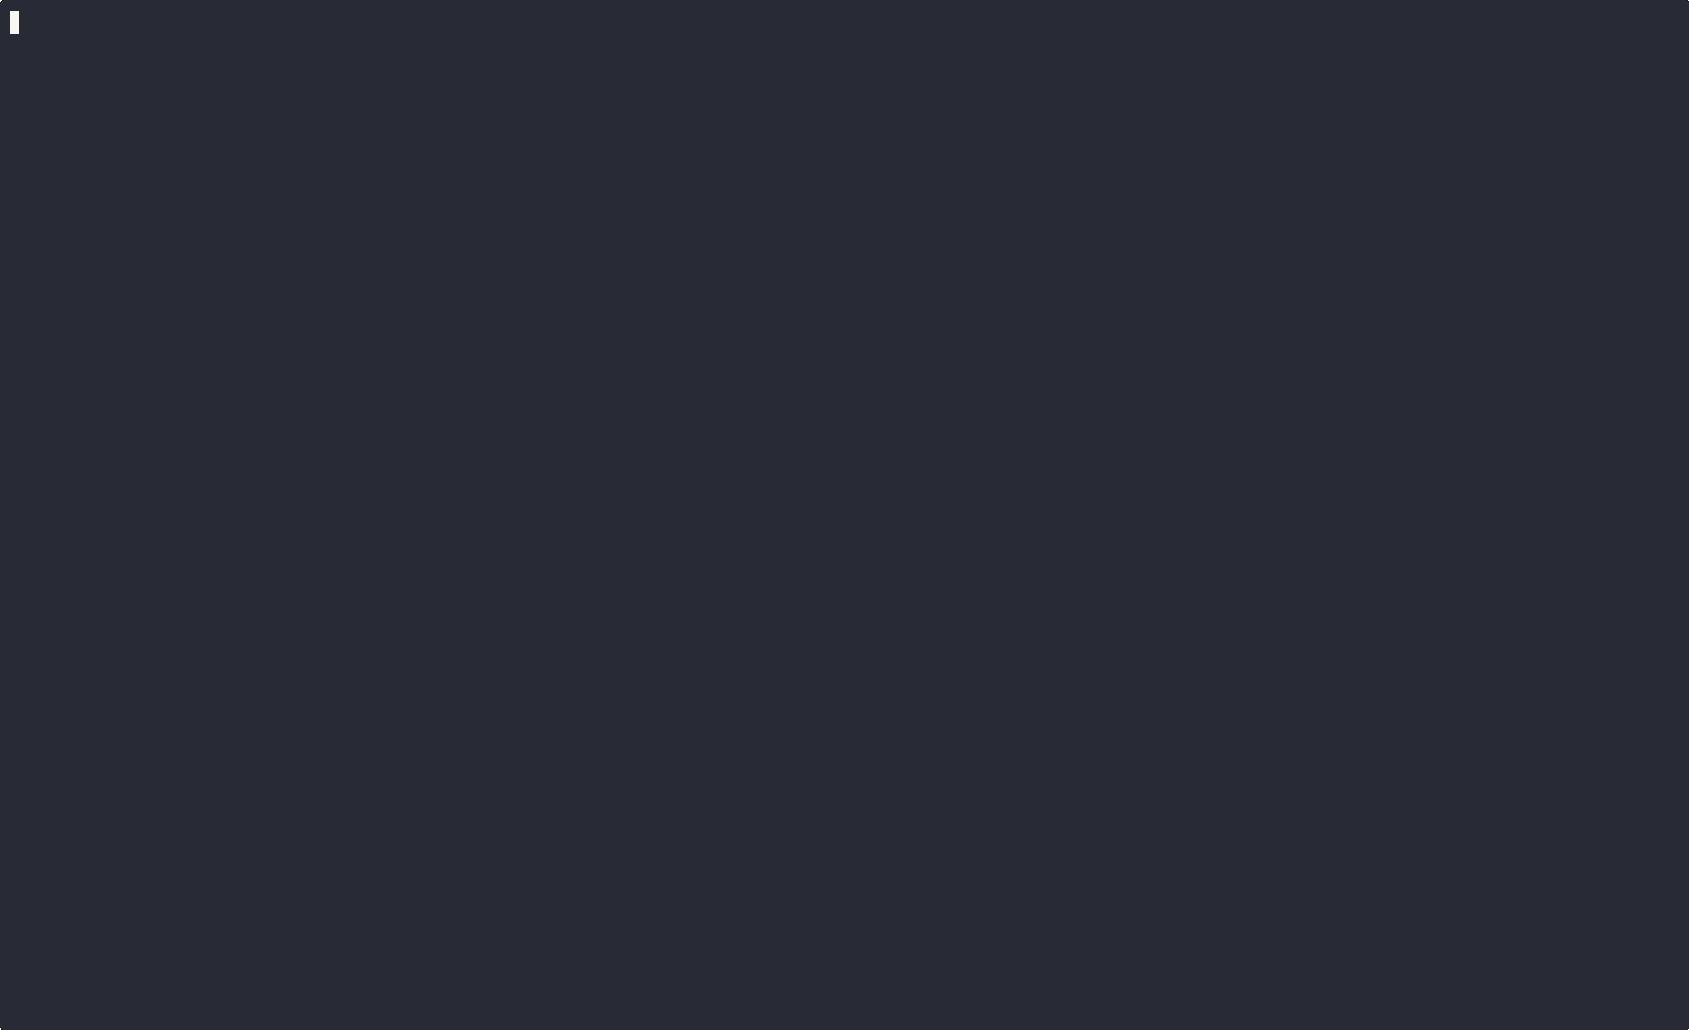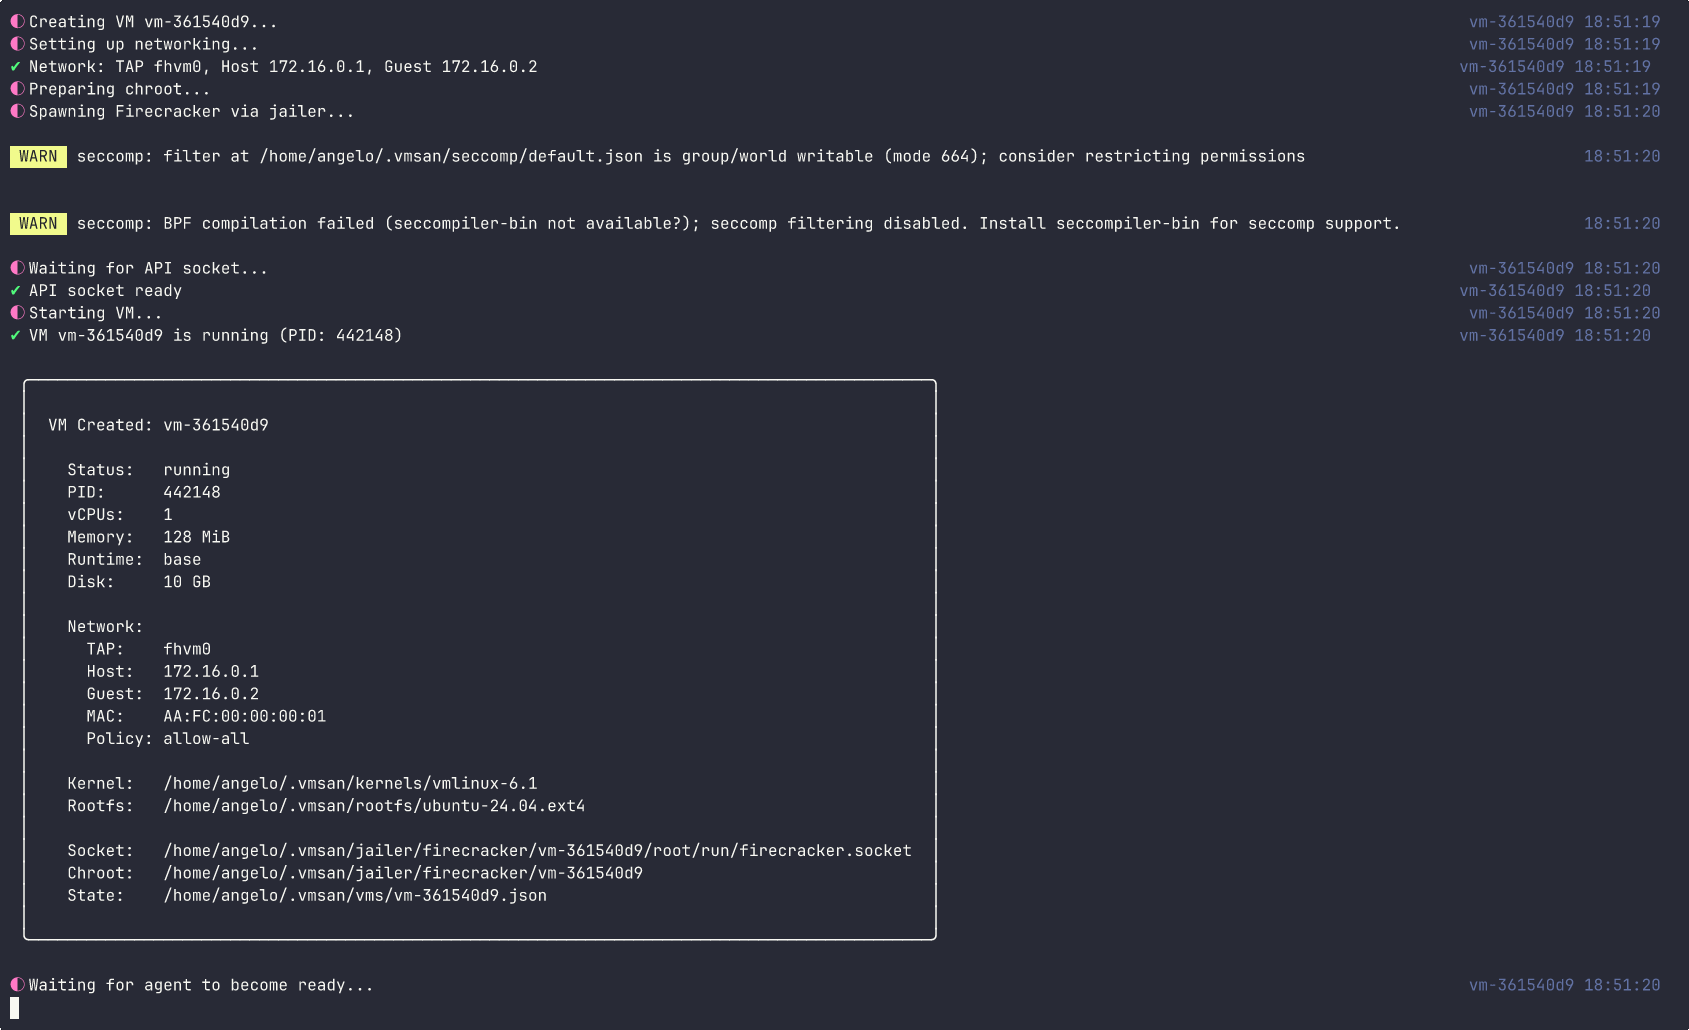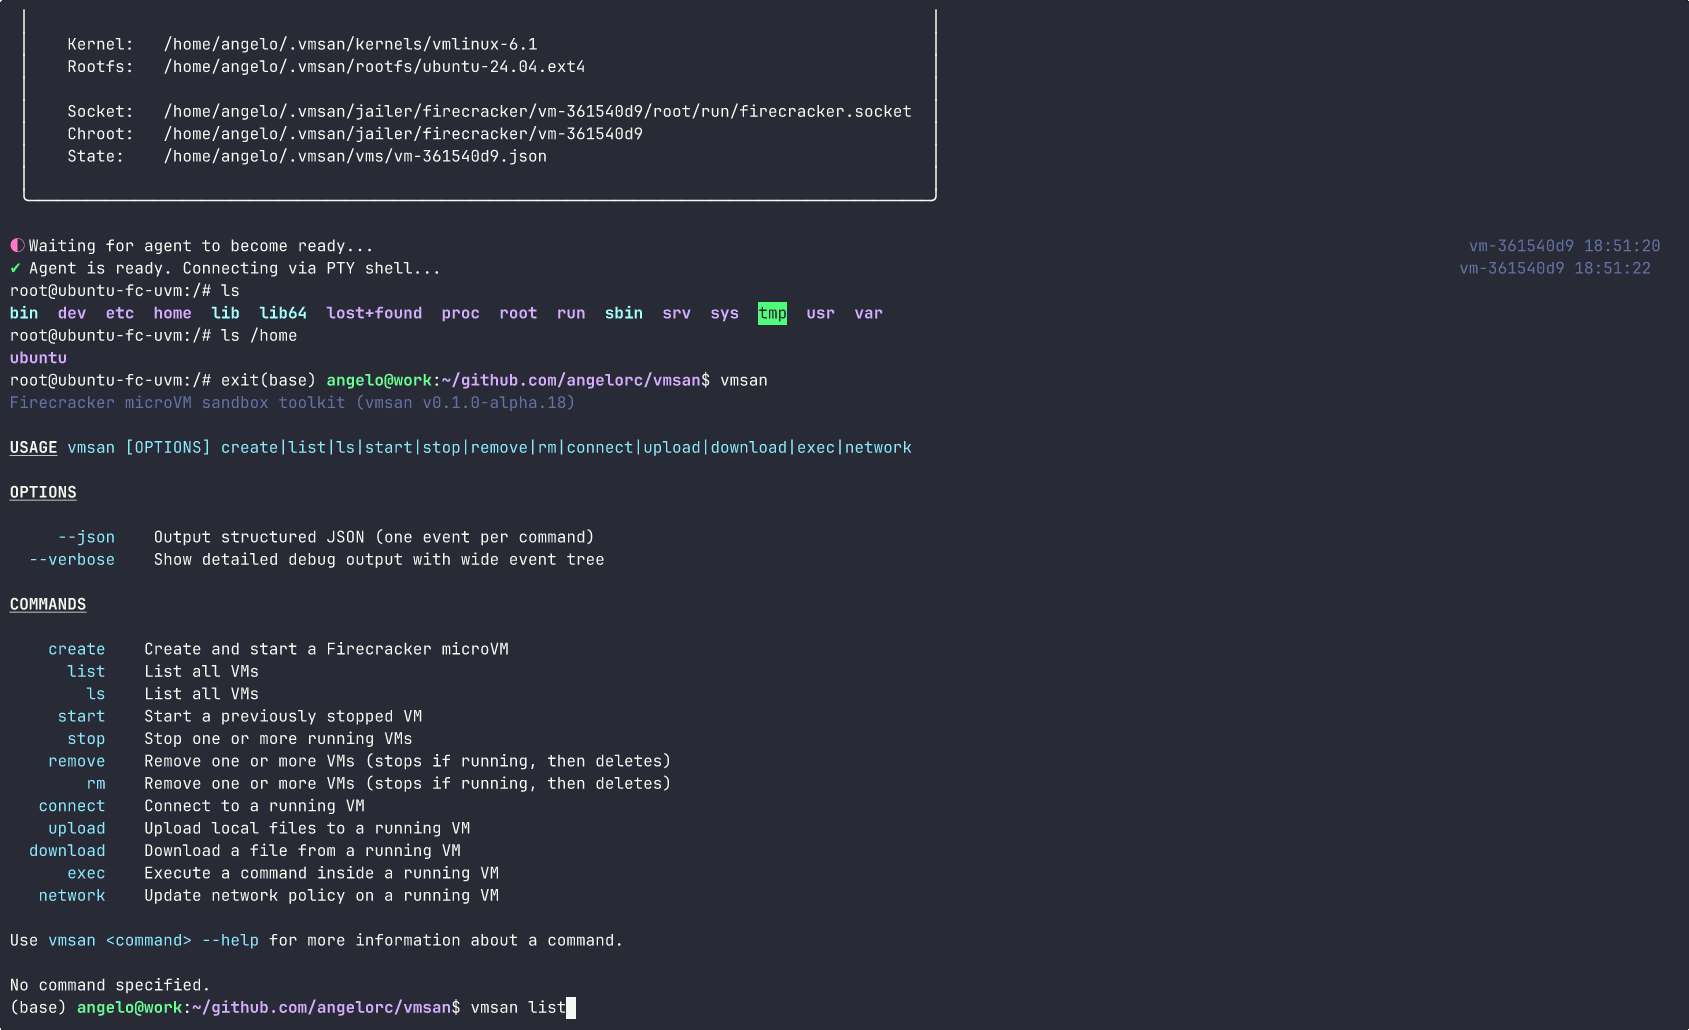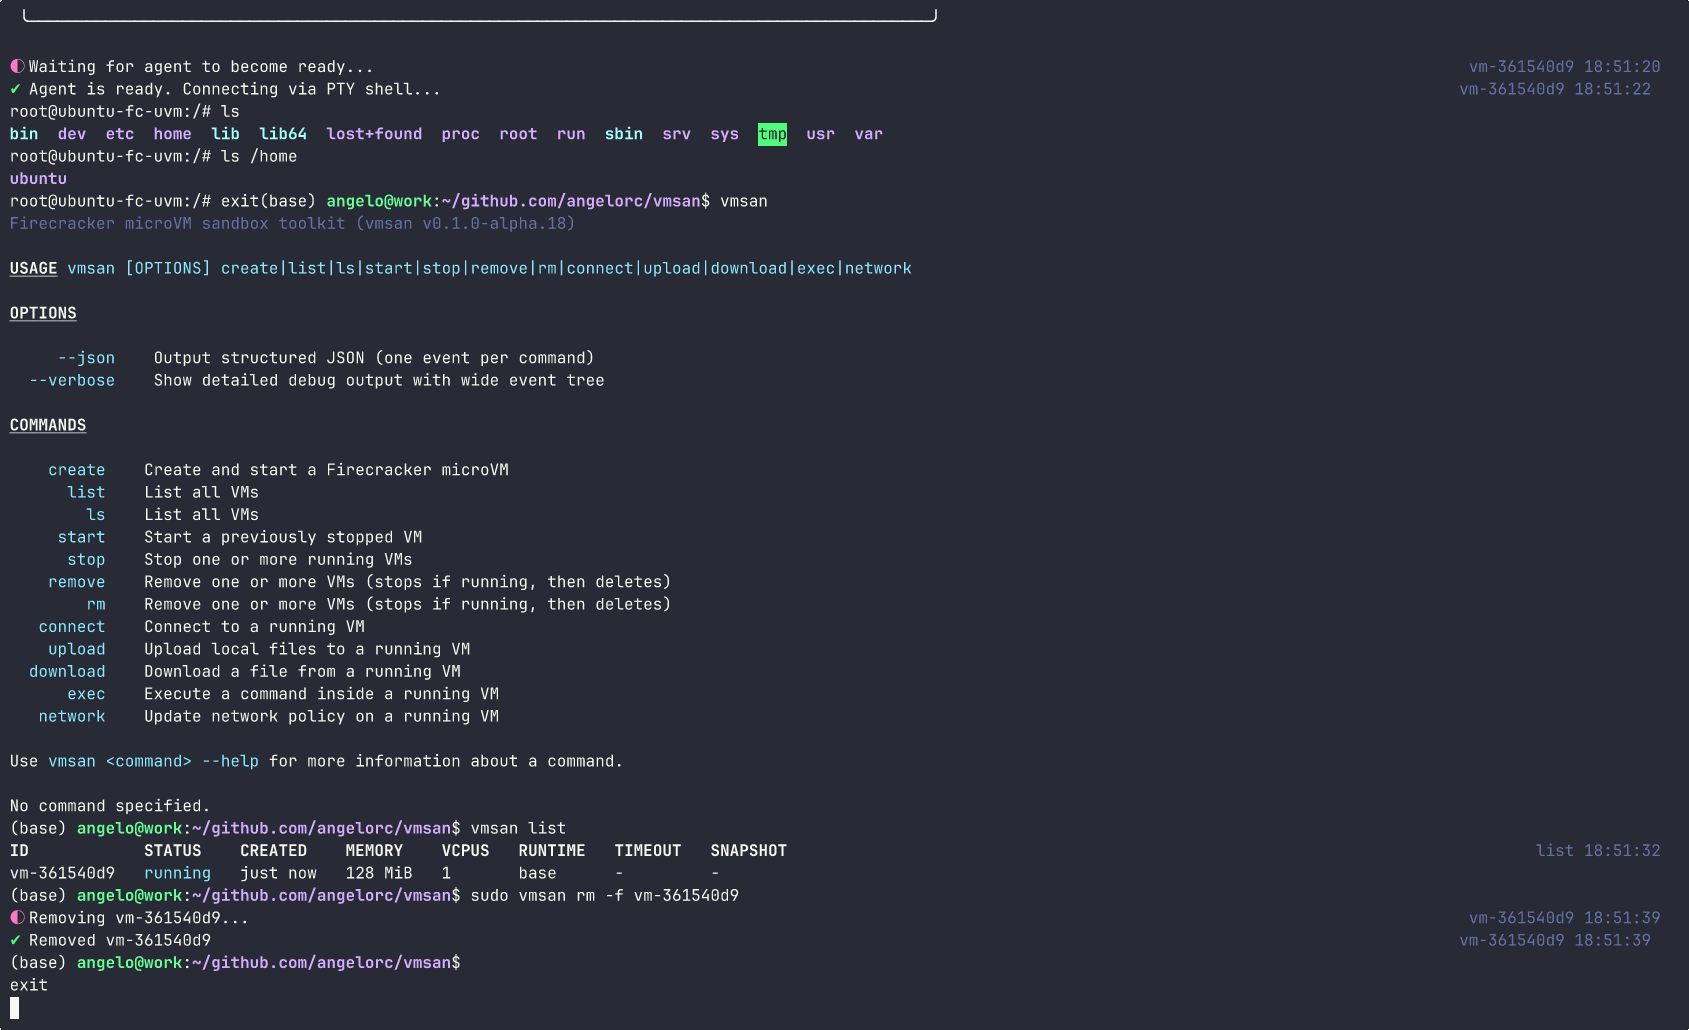 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 kalilinux/build-scripts/kali-cloud
Scripts to build Kali cloud images (fork of https://salsa.debian.org/cloud-team/debian-cloud-images)
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.