
cuckoo3
 cert-ee/cuckoo3
Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.
dynamic-analysis-sandboxingmalware-analysissecurity-virtualization
cert-ee/cuckoo3Open-source automated malware analysis sandbox that runs suspicious files and URLs in isolated VMs and generates detailed behavioral reports.
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 theqmaks/resolver
This extension integrates popular CAPTCHA solution services into BurpSuite to process different types of CAPTCHAs without manual intervention.
 lxc/incus-os
Immutable Linux OS image optimized for running Incus containers and virtual machines, with UEFI Secure Boot, TPM 2.0 disk encryption, and automated…
 owasp/secure-headers-project
OWASP knowledge base and validator for HTTP security response headers, providing recommendations, statistics, and automated configuration checks.
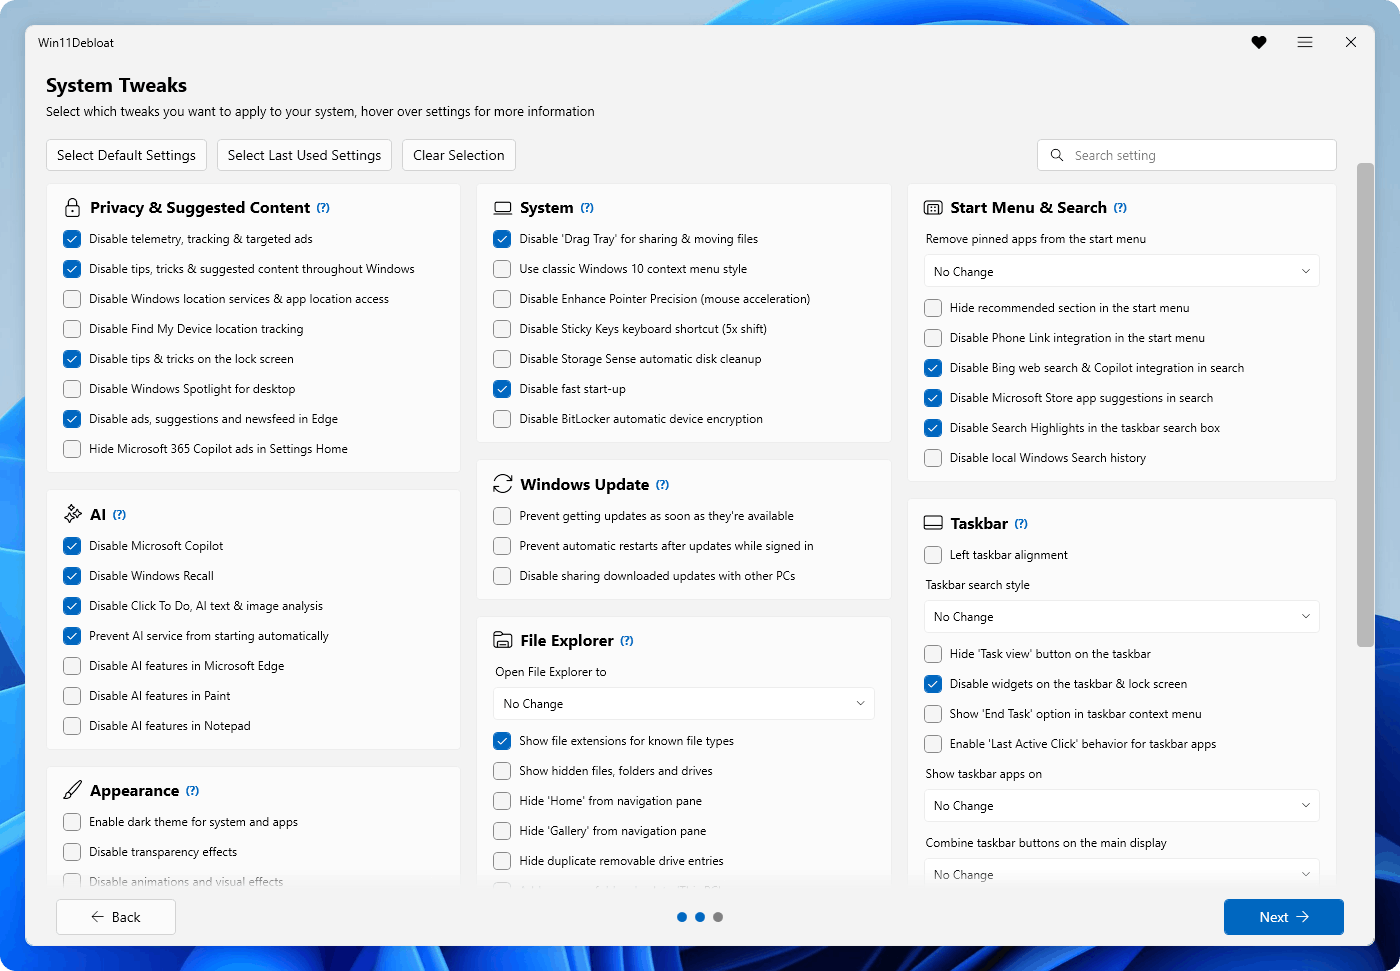 raphire/win11debloat
A simple, lightweight PowerShell script that allows you to remove pre-installed apps, disable telemetry, as well as perform various other changes to…
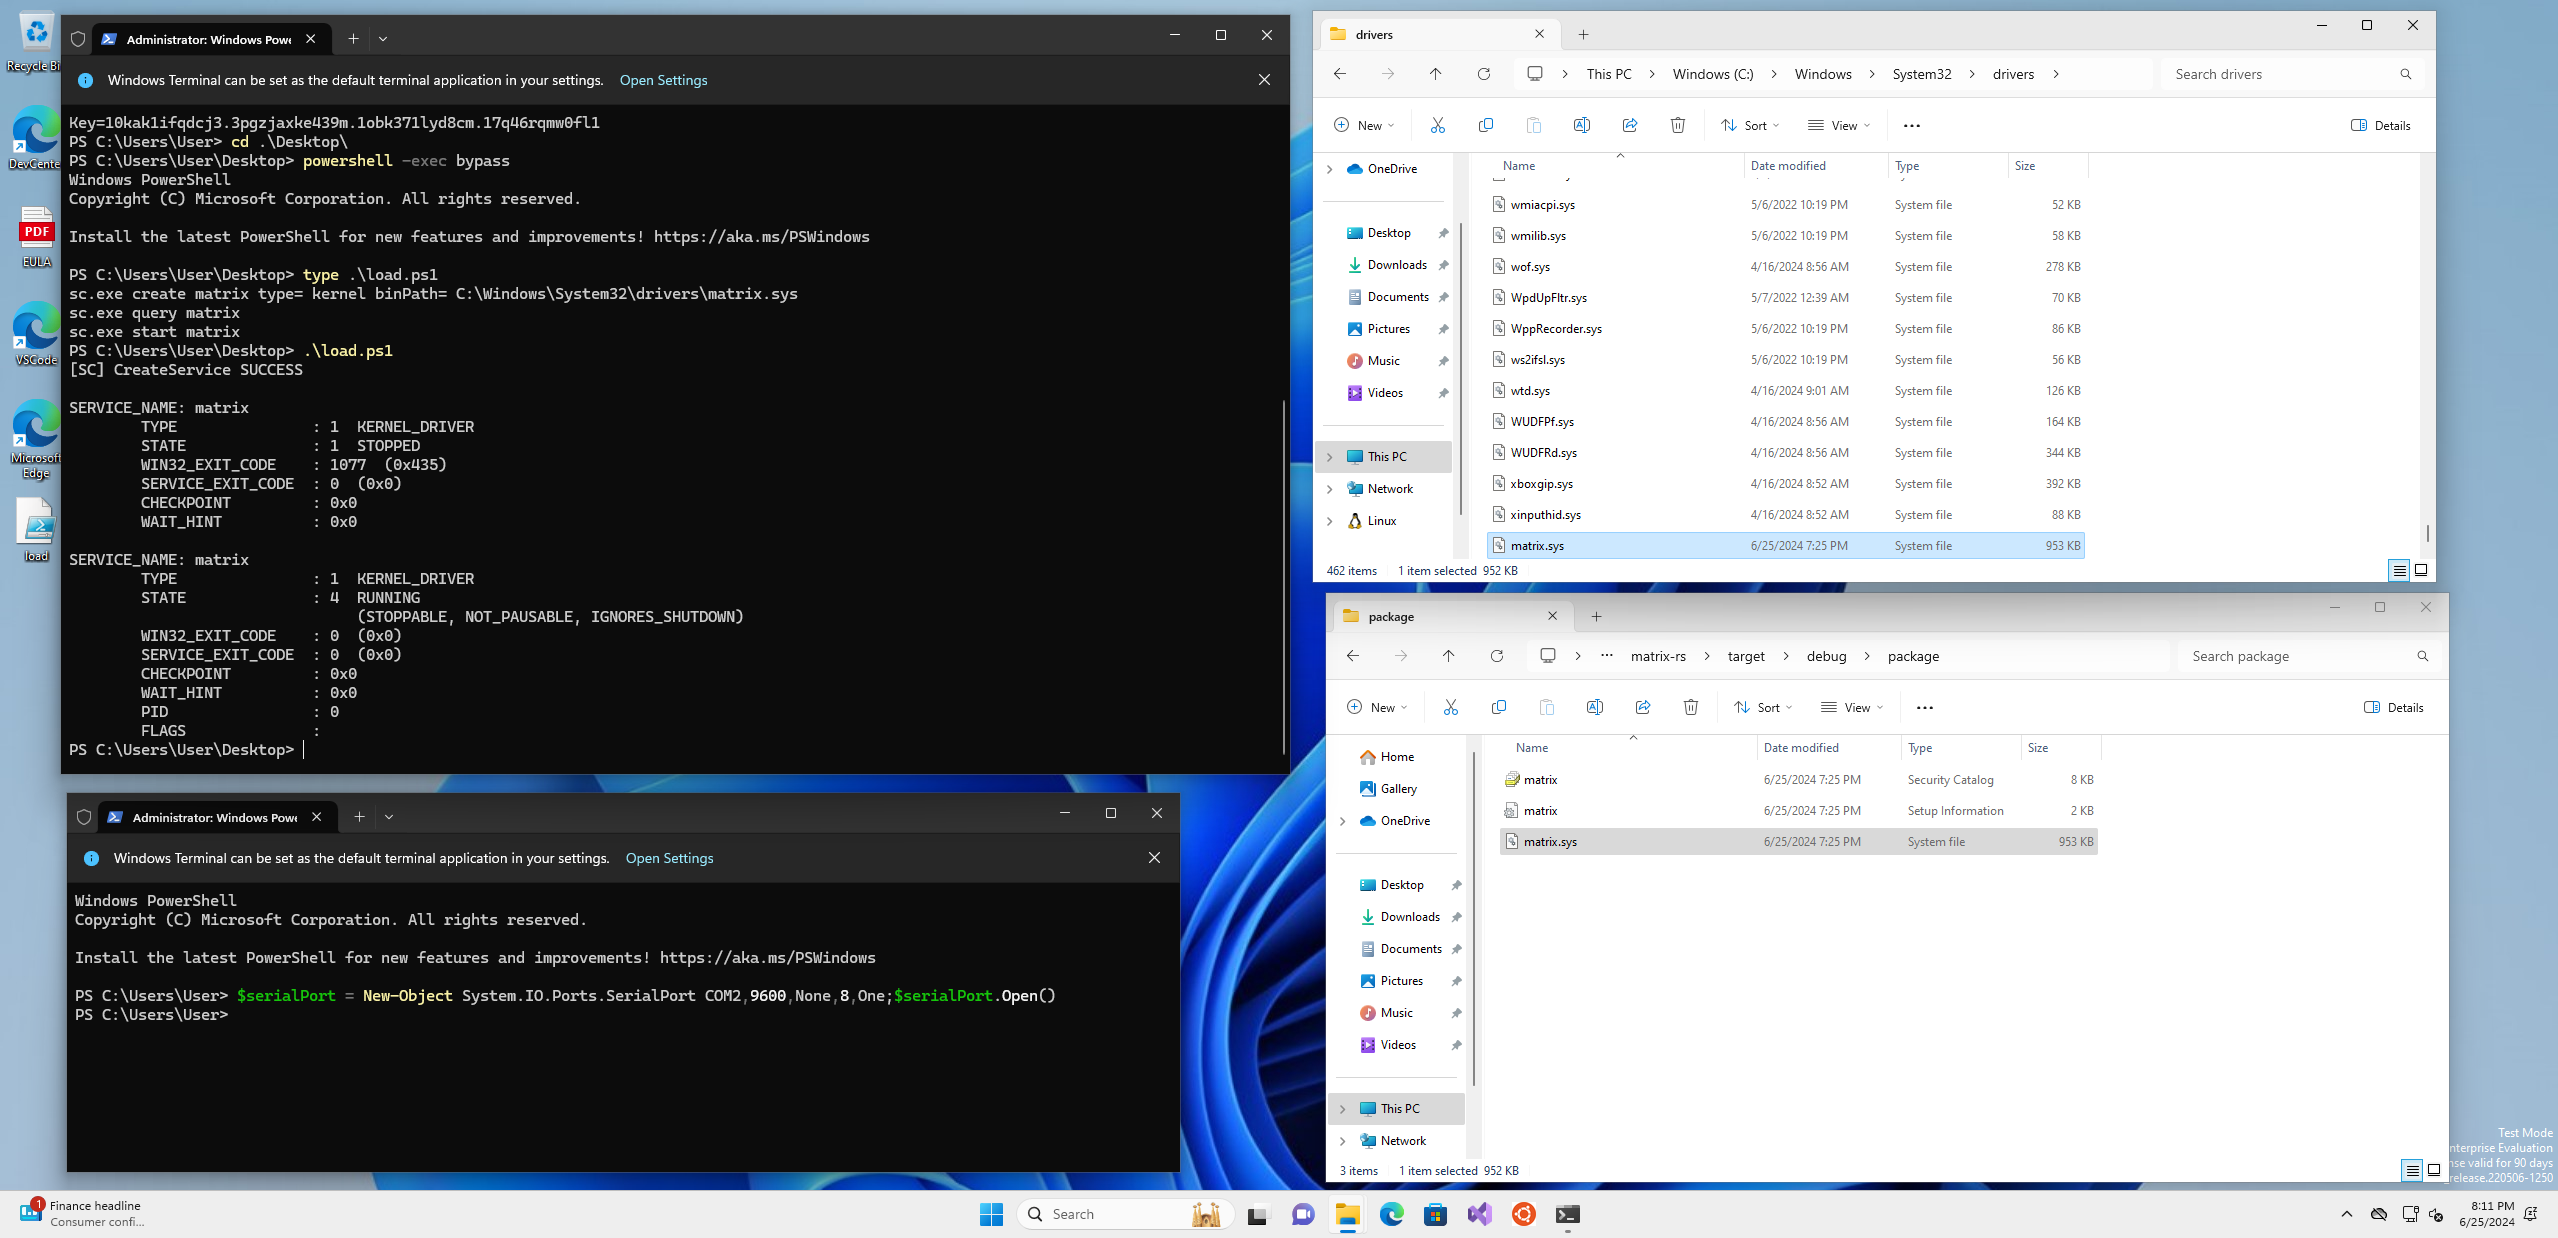 memn0ps/matrix-rs
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)
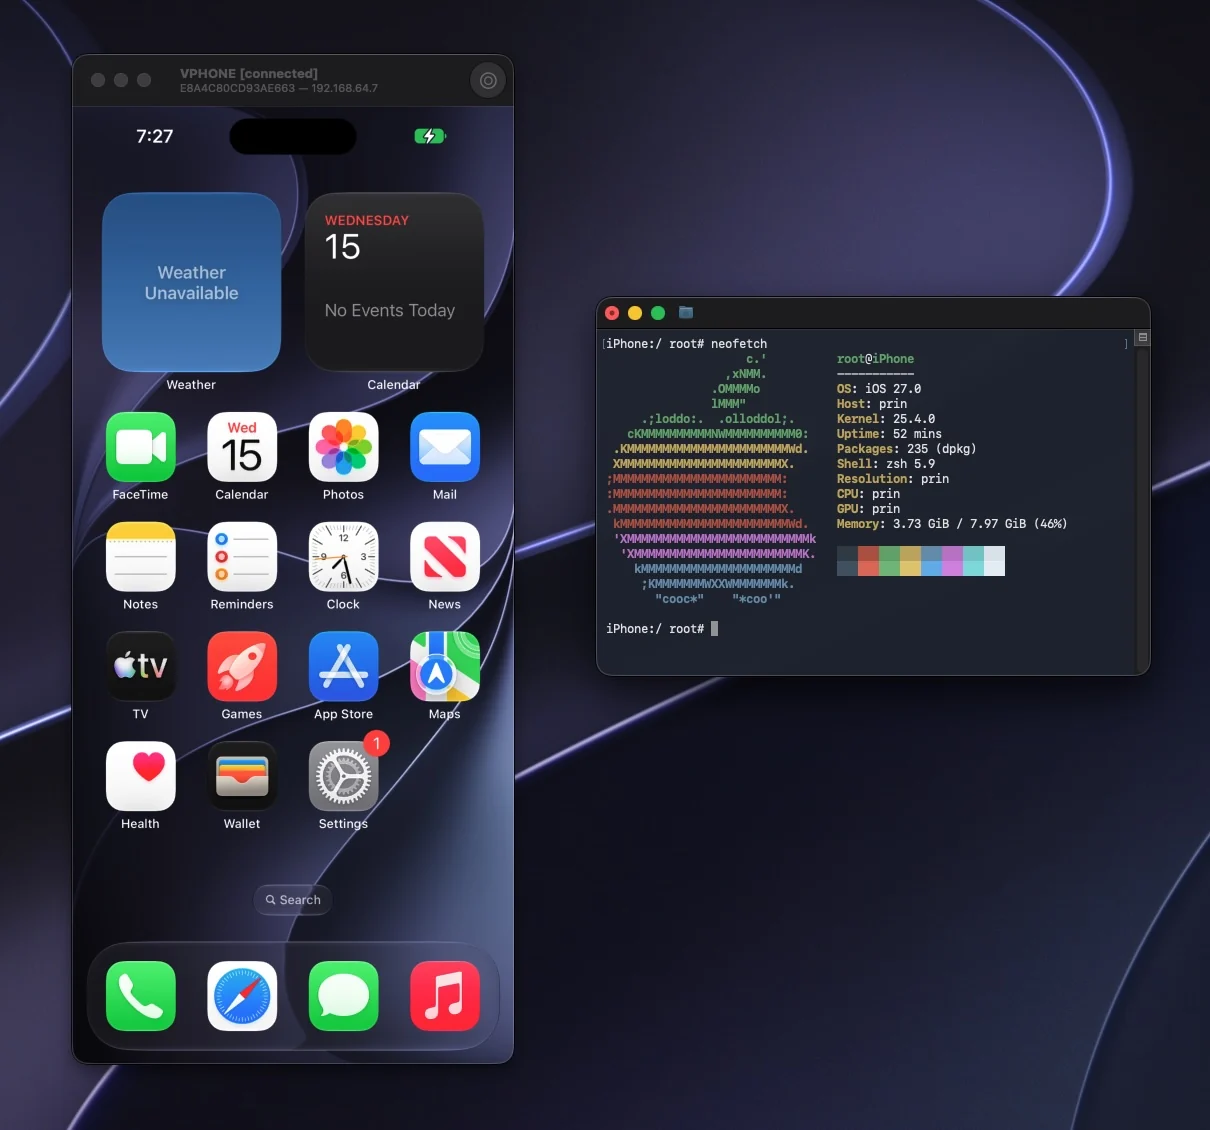 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 didierstevens/didierstevenssuite
Collection of Python scripts for malware analysis, file format parsing, hashing, and forensic triage, including PDF, OLE, and XOR analysis utilities.
 opengrep/opengrep
🔎 Static code analysis engine to find security issues in code.
 googleprojectzero/p0tools
Collection of Google Project Zero vulnerability research documents and small standalone security tools, including exploitation and…
 d4rksystem/vmwarecloak
A PowerShell script that attempts to help malware analysts hide their VMware Windows VM's from malware that may be trying to evade analysis.
 remnux/distro
Provides supplemental files and Debian package sources for a specialized Linux distro focused on malware analysis, reverse engineering, and digital…
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
 owasp/agentic-vulnerability-discovery-and-validation-harness
Agentic harness that automates vulnerability discovery and validation, orchestrating AI-driven analysis workflows to confirm exploitable findings.
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 0xblackash/cve-2026-64531
Reference analysis of a Linux kernel Open vSwitch memory-corruption vulnerability, covering root cause, impact, detection commands, and mitigation…