
blackarch
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
curated-resourceseducationexploit-frameworks+8
3.5k6 days ago
blackarch/blackarchAn ArchLinux based distribution for penetration testers and security researchers.
 kalilinux/build-scripts/kali-vm
Kali Linux VM images build script
 kalilinux/build-scripts/kali-docker
Kali Linux Docker
 phalanx-ccs/copy-fail
Passive diagnostic tool that checks if a Linux system is vulnerable to CVE-2026-31431 by testing AF_ALG socket reachability, providing mitigation…
 synacktiv/mofos
Virtual machines manipulation framework
 mandiant/commando-vm
Customizable Windows-based virtual machine distribution pre-packaged with offensive security tools for penetration testing and red teaming operations.
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
 pazhanivelmani/external_libcap-android10_r33_cve-2023-2603
POSIX.1e capability library for Android 10, addressing CVE-2023-2603 with tools for setting and getting process capabilities to manage privilege…
 atiilla/cve-2026-2441_poc
Proof-of-concept exploit for CVE-2026-2441, demonstrating the vulnerability and providing a working exploit for security testing and validation.
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 kalilinux/build-scripts/kali-packer
Create and configure lightweight, reproducible, and portable development environments Kali's HashiCorp Packer configurations to create Kali…
 gerhart01/hyperv_local_dos_poc
CVE-2020-0890 | Windows Hyper-V Denial of Service Vulnerability proof-of-concept code
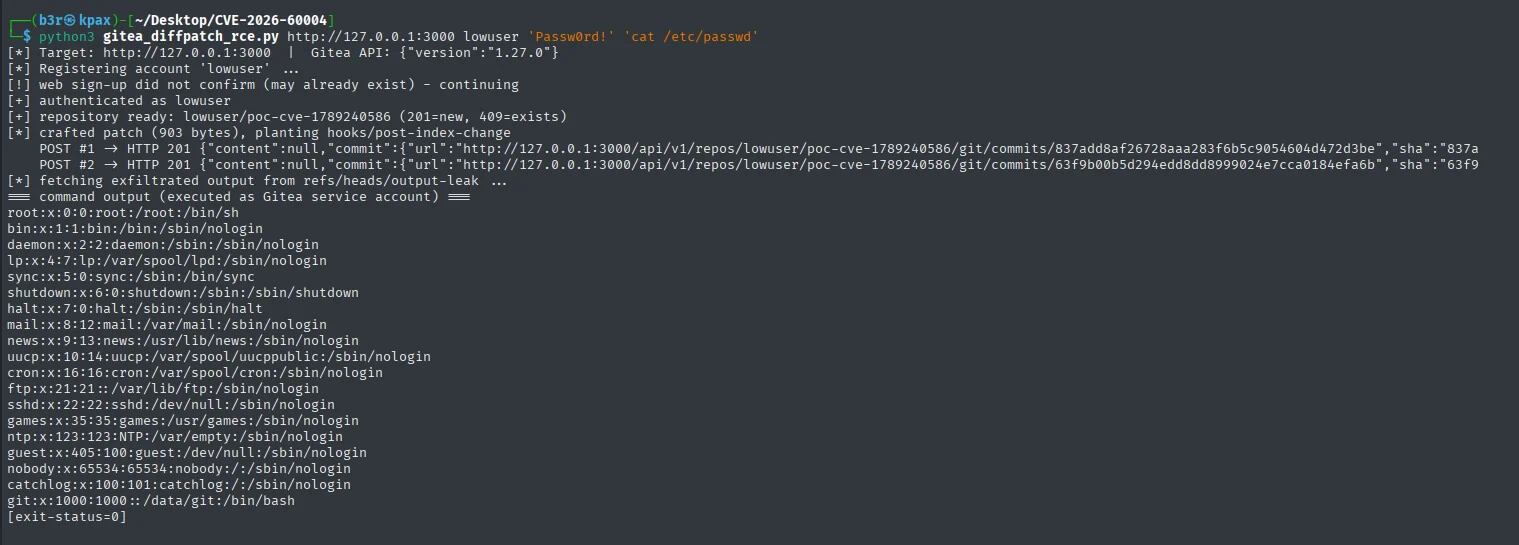 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 squeeze440/supernote-obsidian-plugin-poc
PoC — path traversal via malicious device sync in the Supernote Obsidian plugin (GHSA-3gx3-r874-5pp4, CVE-2026-86999, CVSS 5.6).
 ayub0x7/cve-2024-32019-poc
Checks Netdata ndsudo SUID PATH privilege escalation exposure for CVE-2024-32019 and validates patches without weaponized exploitation.