
tamago
 usbarmory/tamago
Framework for compiling and executing Go applications on bare metal processors, enabling secure firmware development with reduced attack surface…
embedded-systems-securityfirmware-analysishardware-security+1
2.1k
usbarmory/tamagoFramework for compiling and executing Go applications on bare metal processors, enabling secure firmware development with reduced attack surface…
 finbarr/yolobox
Let your AI go full send. Your home directory stays home.
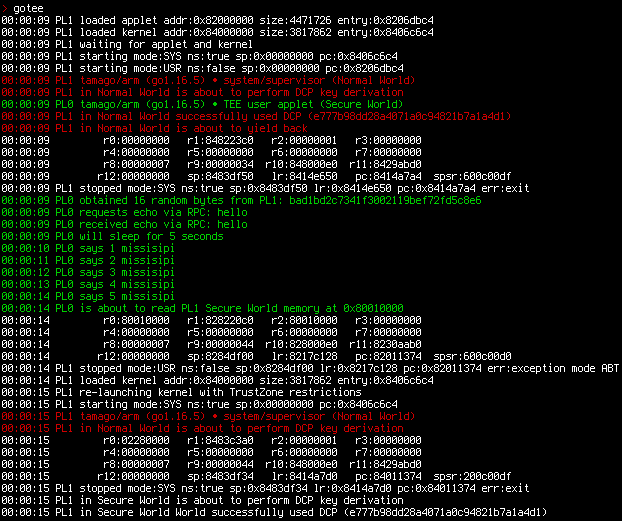 usbarmory/gotee
Go Trusted Execution Environment (TEE)
 nishitm/gobox
GO sandbox to run untrusted code
 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
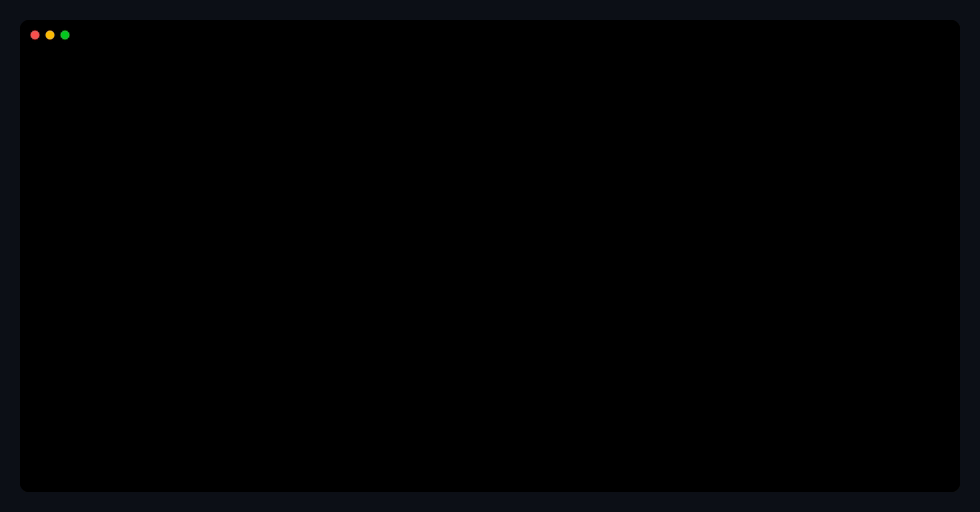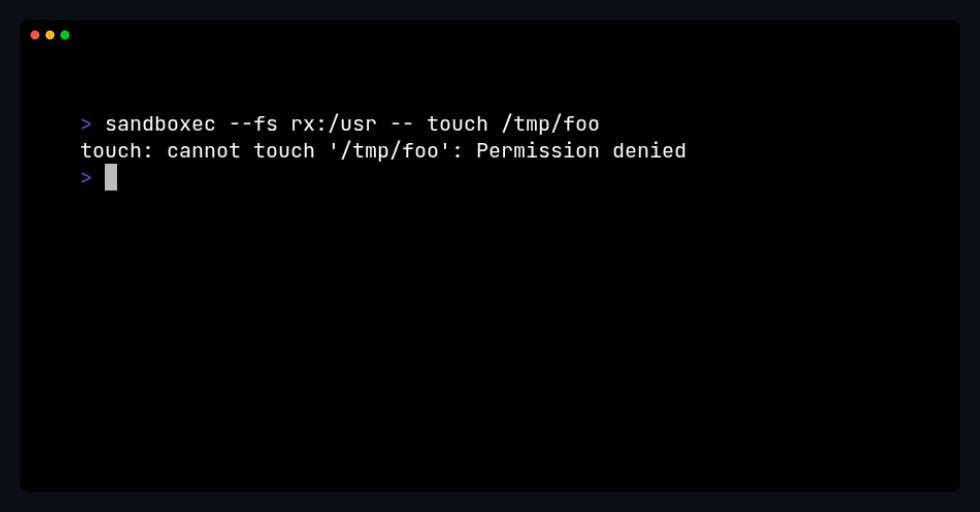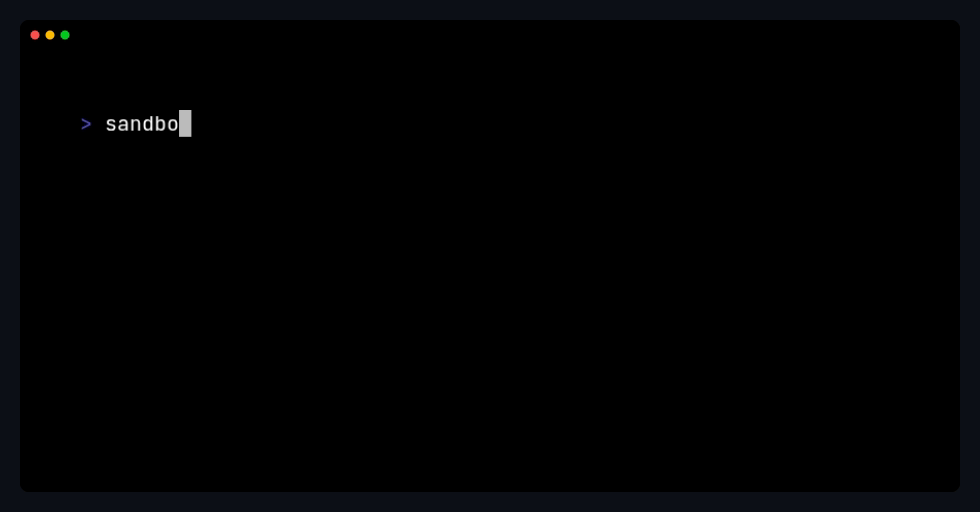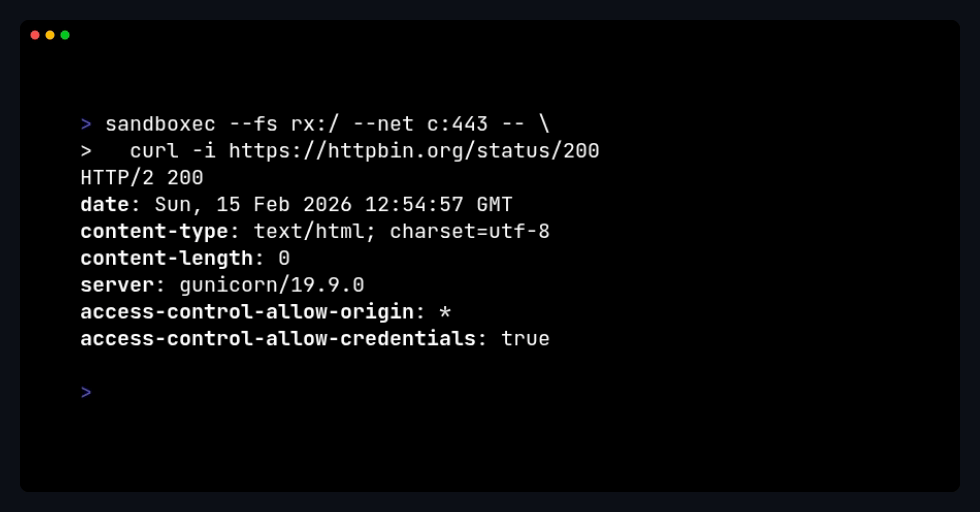 sandboxec/sandboxec
A lightweight command sandbox for Linux, secure-by-default, built on Landlock.
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
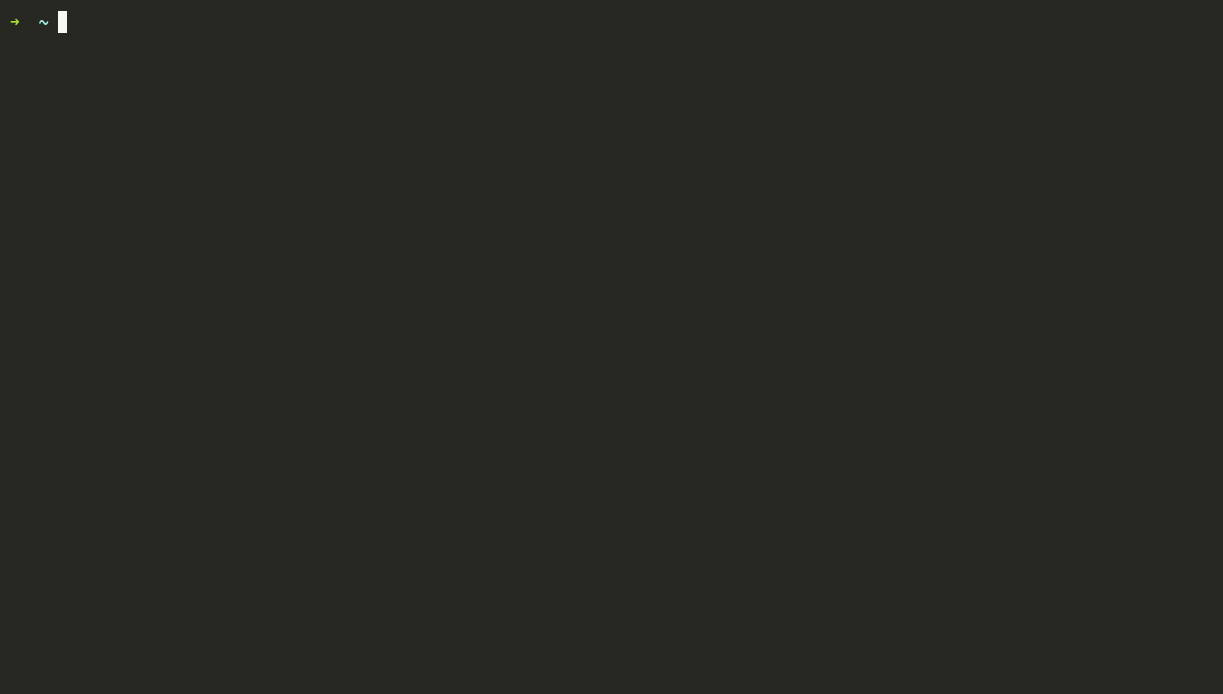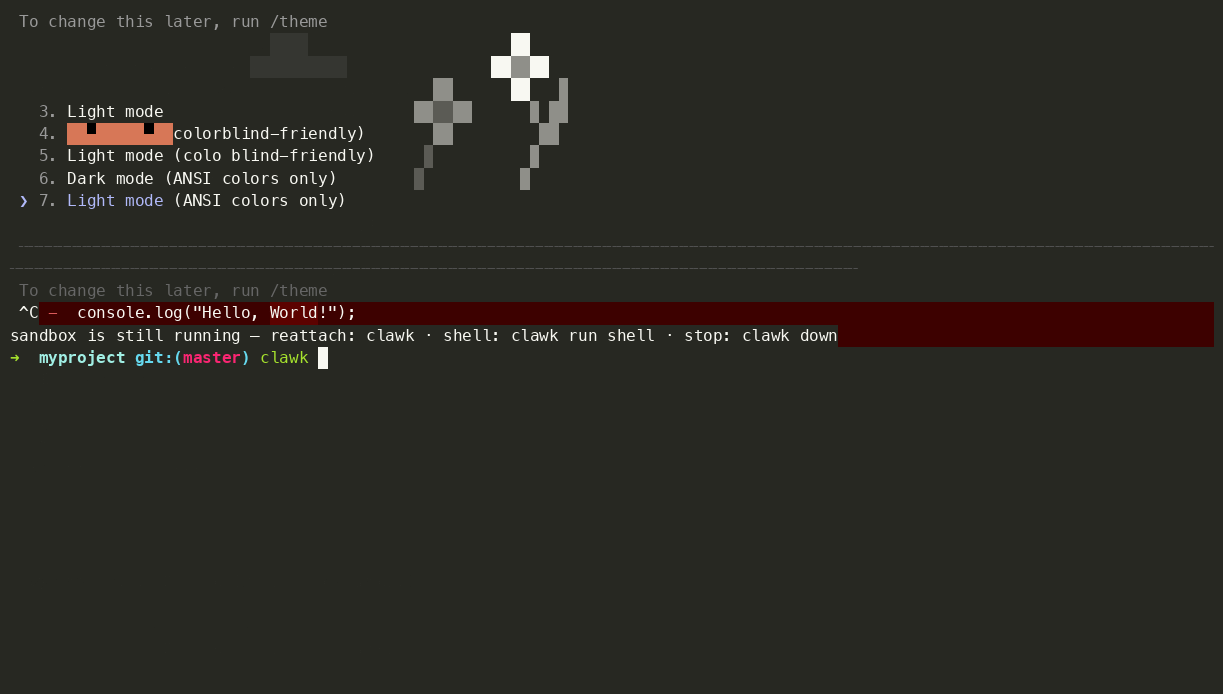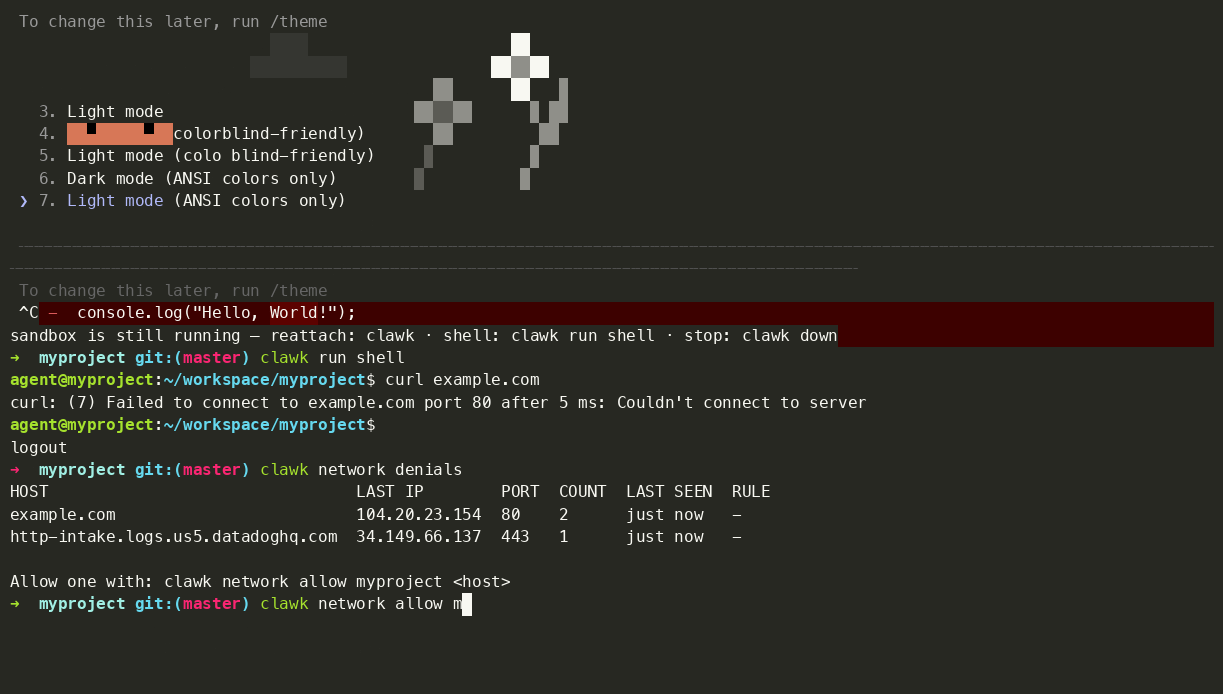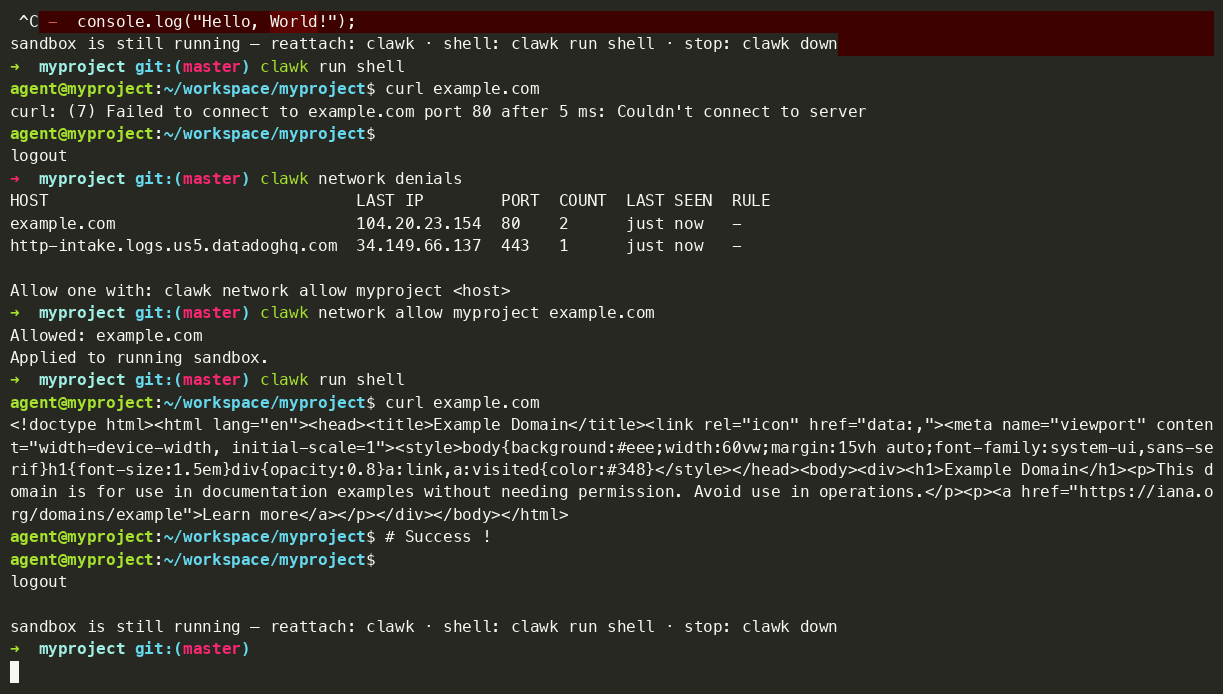 clawkwork/clawk
Give coding agents a disposable Linux VM, not your laptop
 jingkaihe/matchlock
Ephemeral microVM sandbox for AI agents with network allowlisting, secret injection via MITM proxy, and VM-level isolation. Boots in under a second,…
 rex-rs/rex
Rex is a safe and usable kernel extension framework that allows loading and executing Rust kernel extension programs in the place of eBPF.
 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
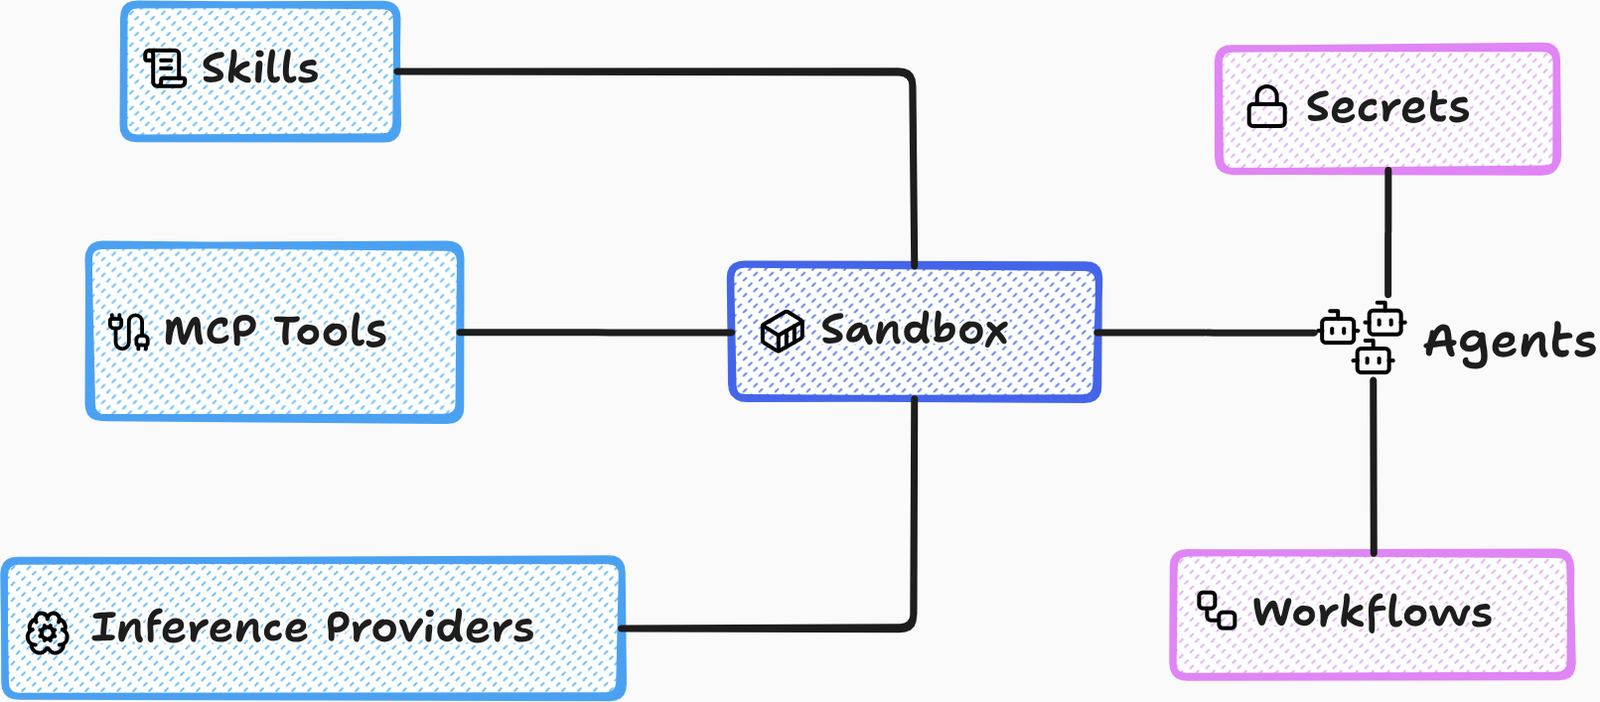 accuknox/agentz
Zero-trust agentic AI platform. Supports SaaS and OnPrem (airgapped) deployments.
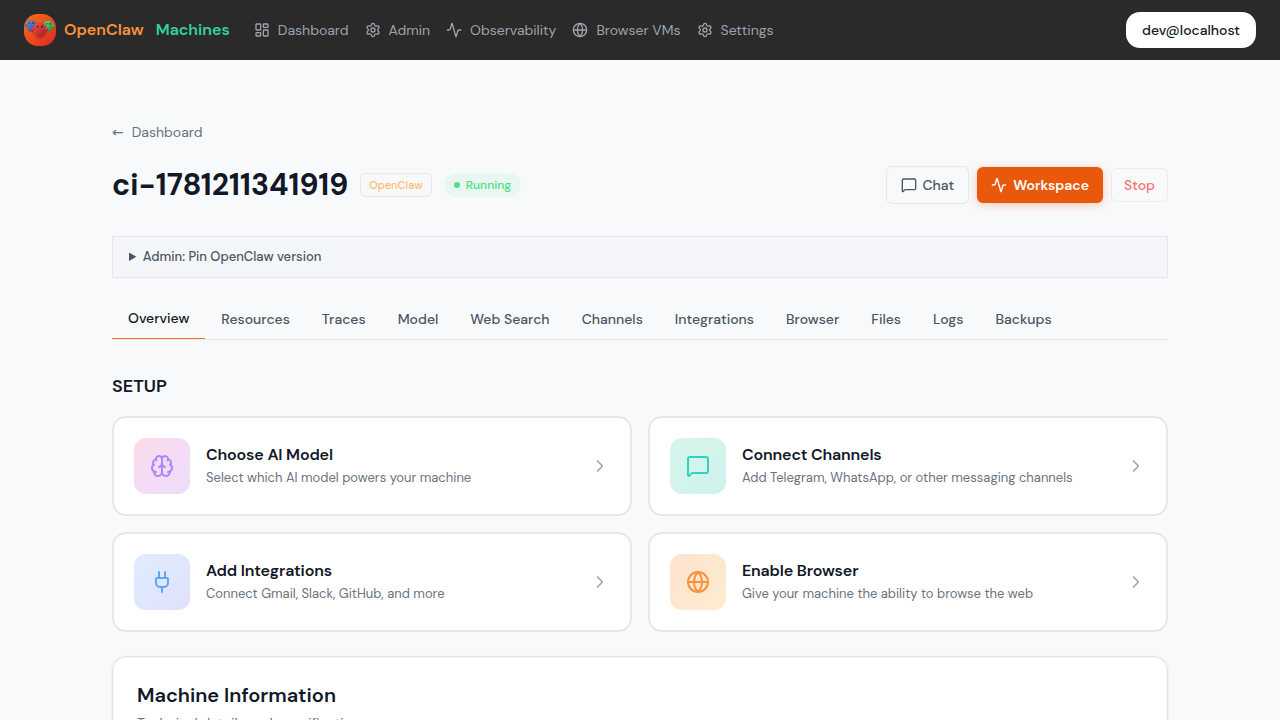 mathaix/openclawmachines
Manage OpenClaw in your team (Enterprise) by providing it compute infrastructure, tool integration, Authentication and security primitives
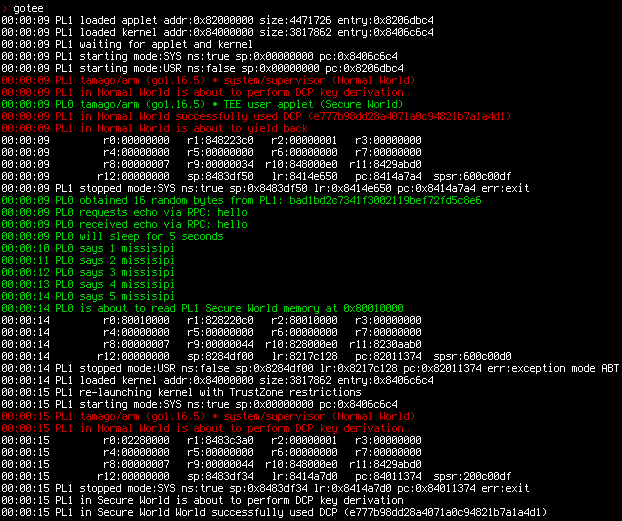 usbarmory/gotee-example
GoTEE - example application
 libriscv/libloong
The fastest LoongArch sandbox
 suominen/januscape
Tracking Januscape (CVE-2026-53359), the KVM/x86 guest-to-host escape
 suominen/itscape
Tracking ITScape (CVE-2026-46316), the KVM/arm64 guest-to-host escape
 siyad01/agentbox
Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.