CVE-2026-87902-PoC-pwnVader

Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.

Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.

Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…

Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…

WASM sandbox with capability enforcement for AI agent code. Agents can only call explicitly provided tools with defined constraints. Sandboxed…

Zero-trust sandbox for AI agents with kernel-level filesystem jail, transparent network proxy, and YAML-based policy engine to intercept and control…

Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…

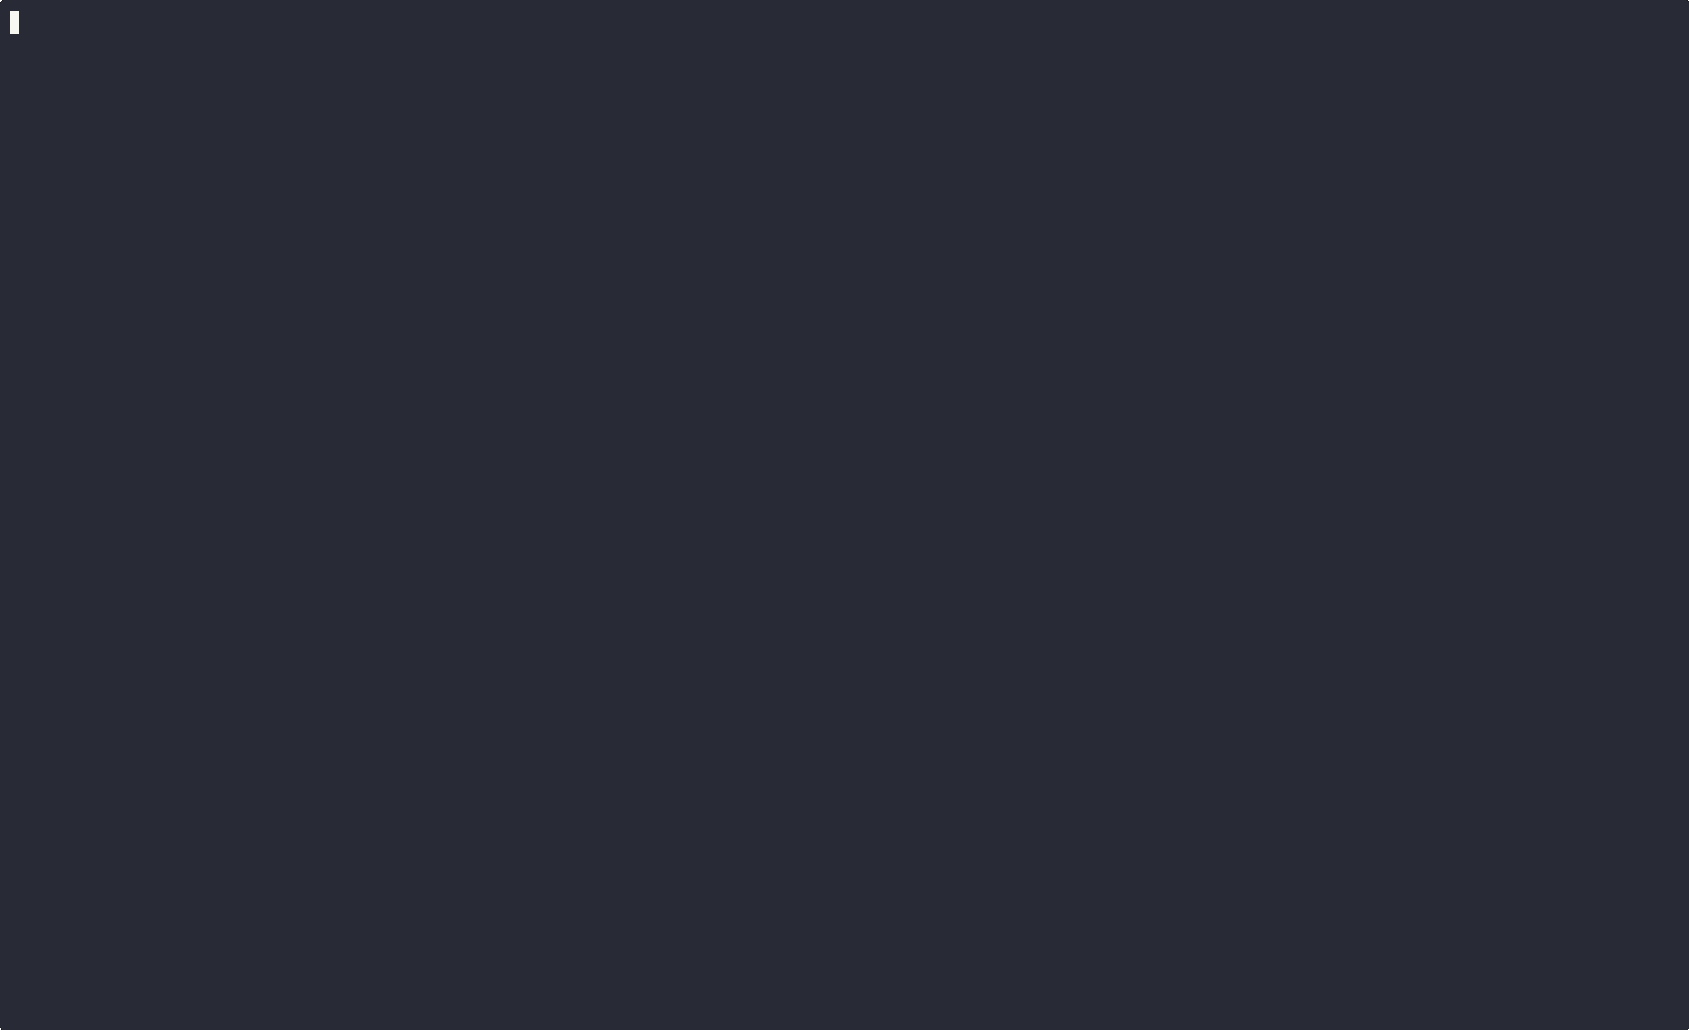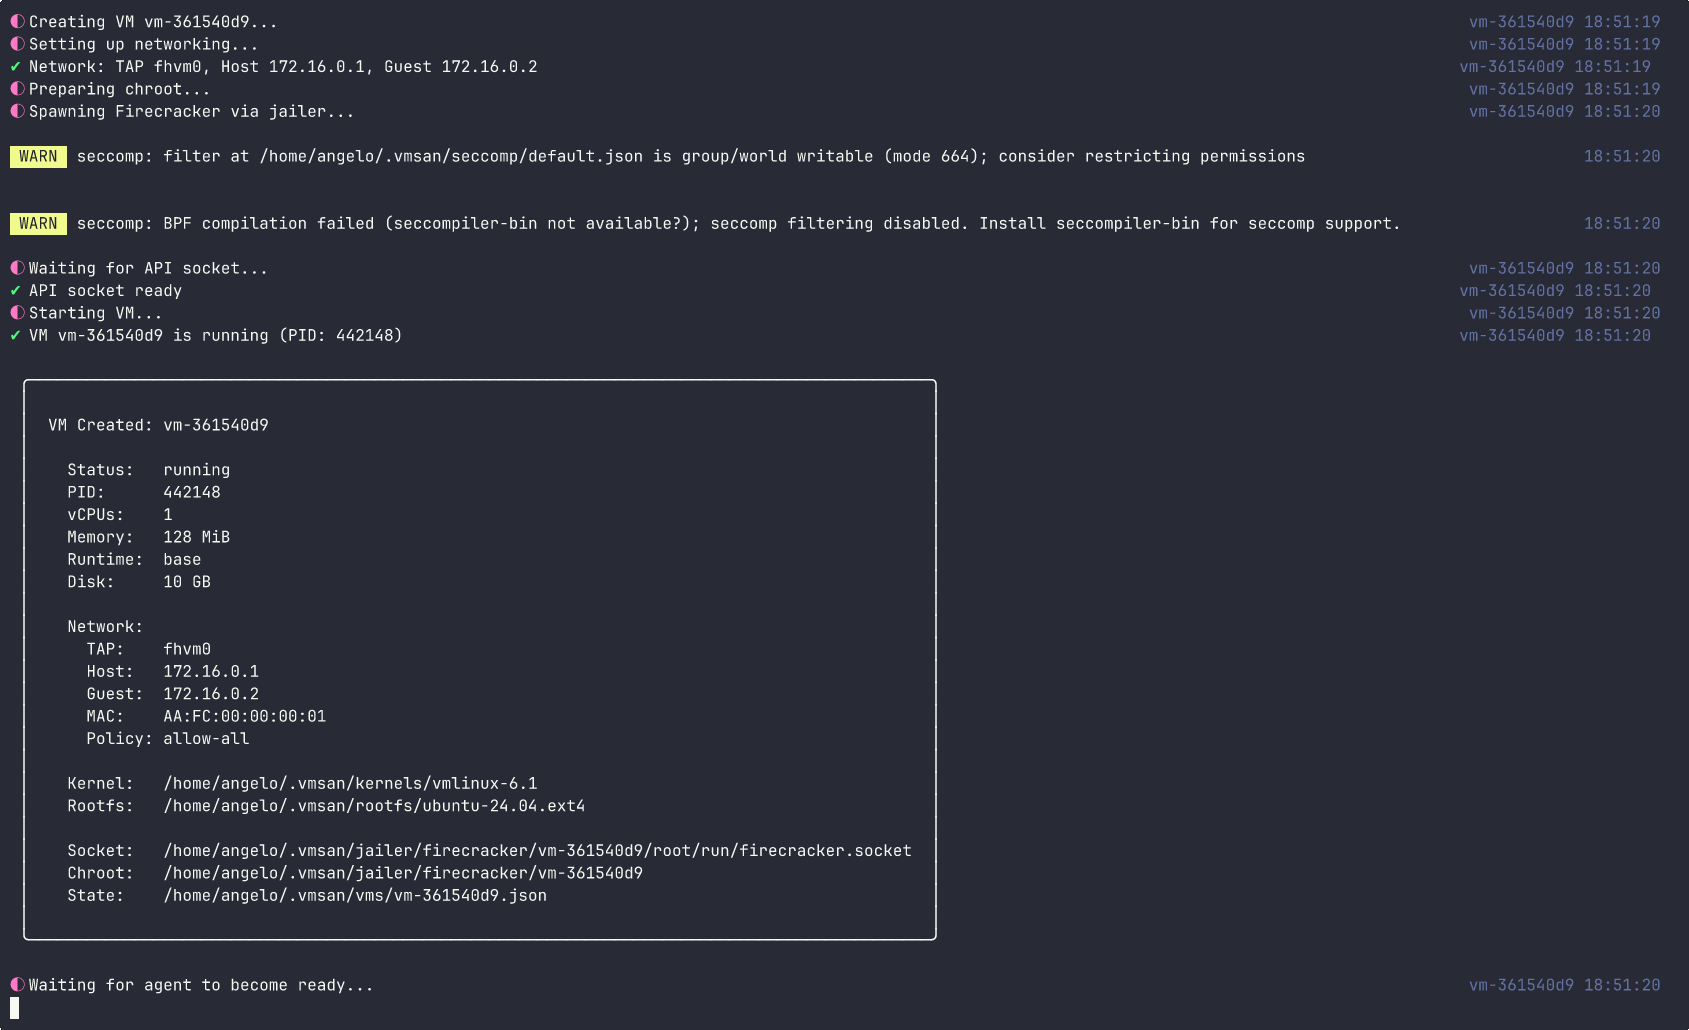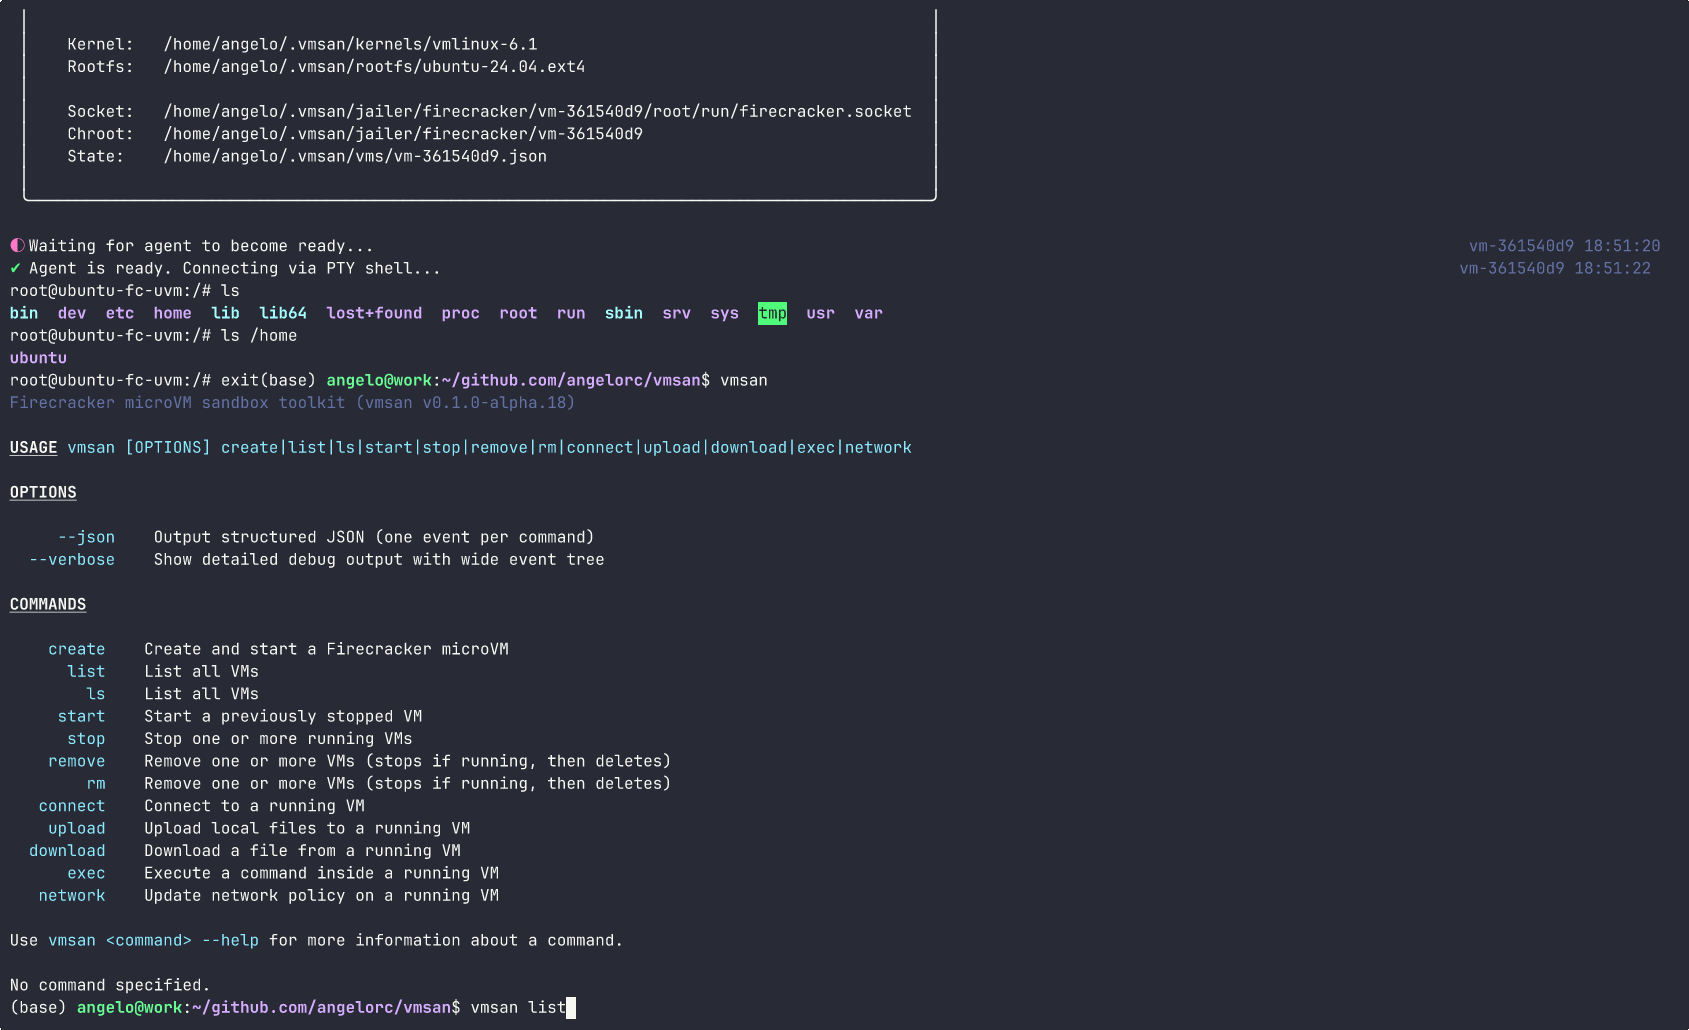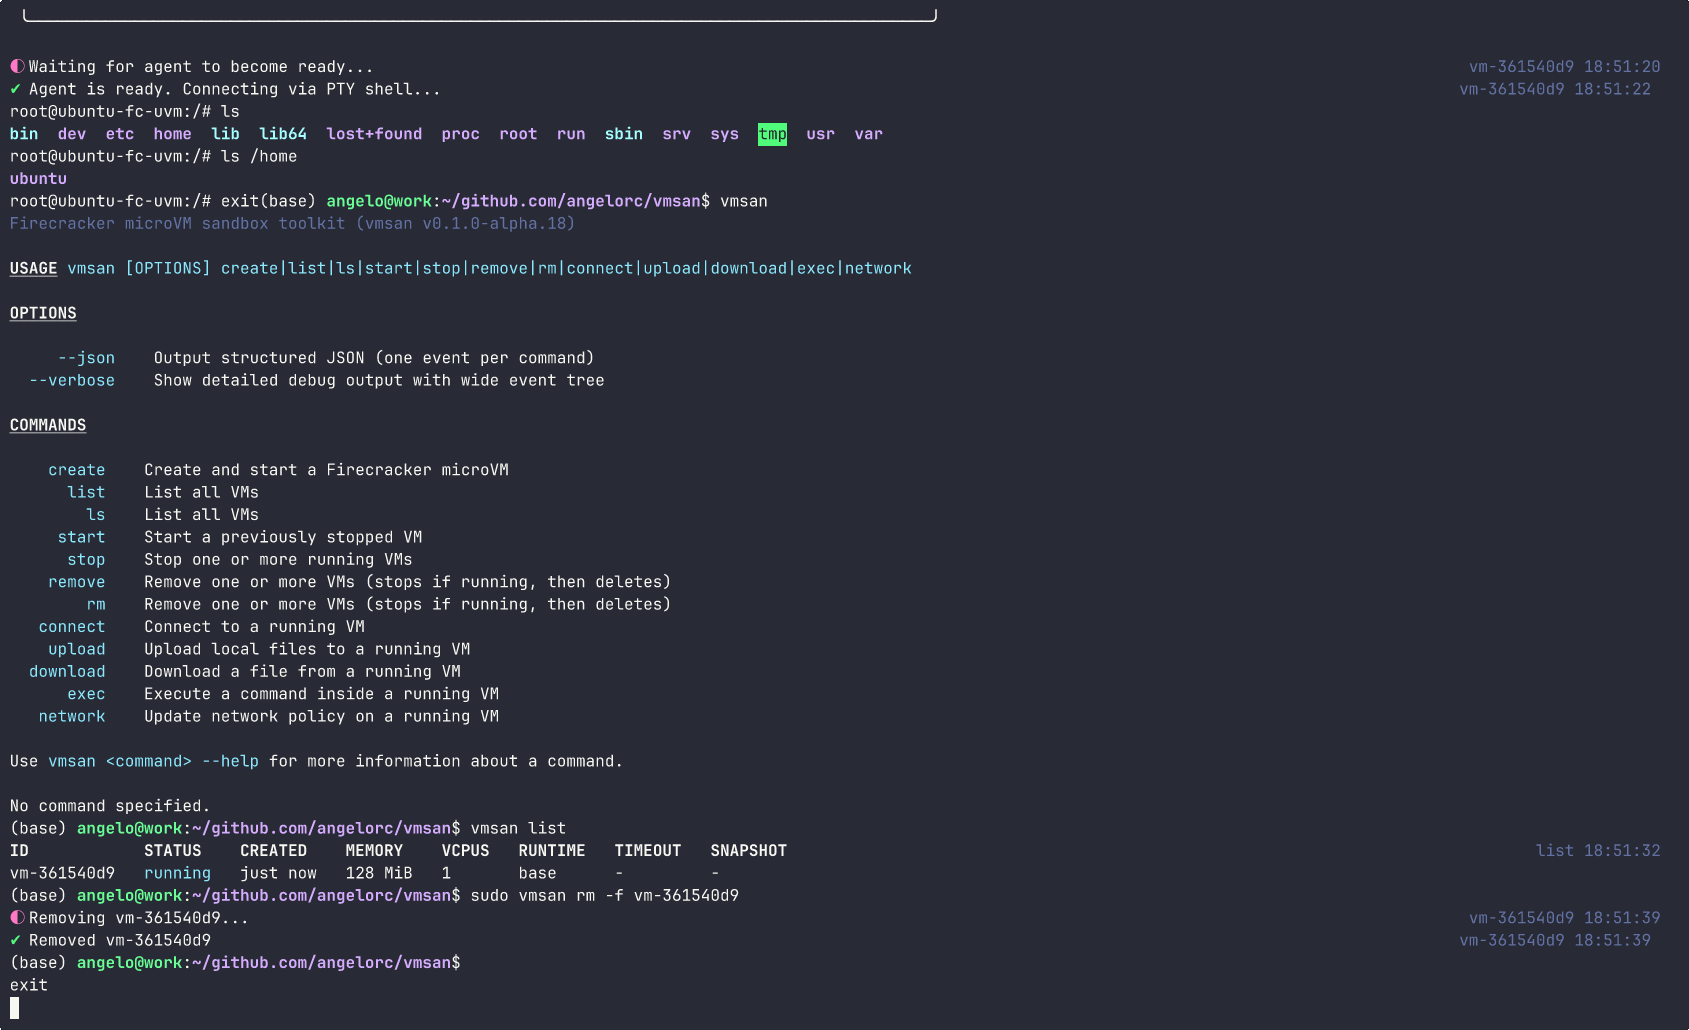
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.

wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.