
mxc
 microsoft/mxc
Policy-driven, layered isolation and containment
cloud-infrastructure-securityconfiguration-auditingcontainer-security+3
microsoft/mxcPolicy-driven, layered isolation and containment
 0xballpoint/load
Lord Of Active Directory - automatic vulnerable active directory on AWS
 vulhub/vulhub
Pre-Built Vulnerable Environments Based on Docker-Compose
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
 microsoft/pqcrypto-lweke
C library implementing FrodoKEM, a post-quantum key encapsulation mechanism based on the Learning with Errors problem, with variants for AES and…
 impalabs/hyperpom
AArch64 fuzzer based on the Apple Silicon hypervisor
 epsilon537/boxlambda
FPGA based microcomputer sandbox for software and RTL experimentation
 mandiant/commando-vm
Customizable Windows-based virtual machine distribution pre-packaged with offensive security tools for penetration testing and red teaming operations.
 schumilo/vusbf
A QEMU/KVM-based USB fuzzing framework that finds device-driver bugs via reproducible VM execution, multiprocessing, and XML testcase generation.
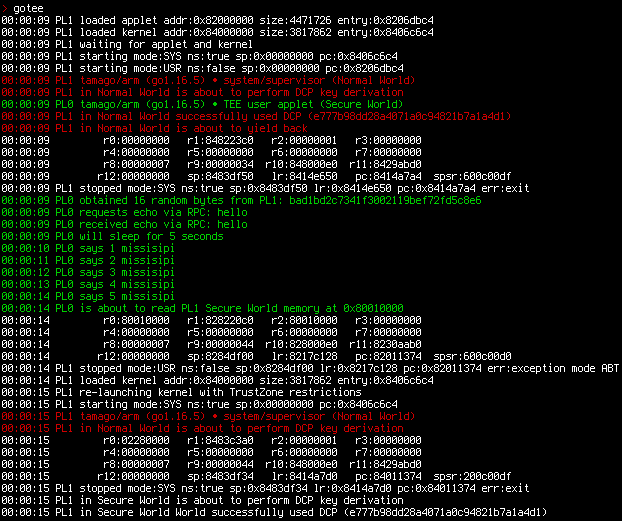 usbarmory/gotee
Go Trusted Execution Environment (TEE)
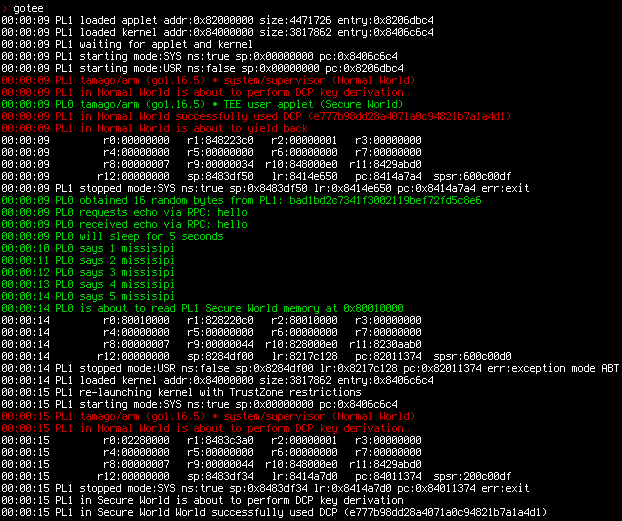 usbarmory/gotee-example
GoTEE - example application
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
