
Zapscape
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
binary-exploitationdefensive-toolsexploitation+2
1
aarif450/zapscapeGuest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
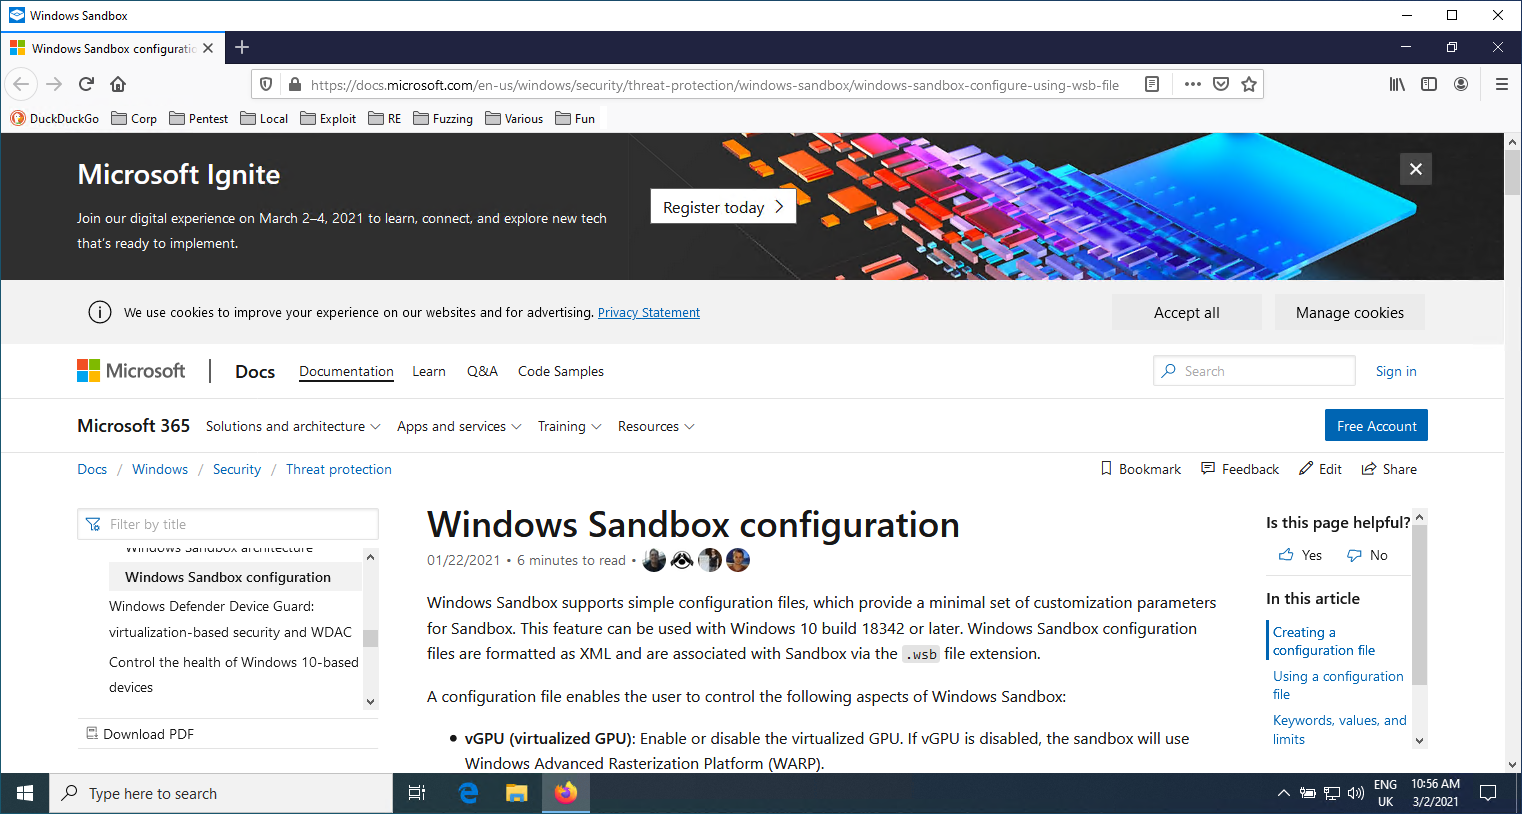 nccgroup/wubes
Qubes containerization on Windows
 zjuicsr/actbench
Code for paper "ActBench: Self-Evolving Benchmark of Behavioral Safety in Cowork Agents"
 suominen/januscape
Tracking Januscape (CVE-2026-53359), the KVM/x86 guest-to-host escape
 suominen/itscape
Tracking ITScape (CVE-2026-46316), the KVM/arm64 guest-to-host escape
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
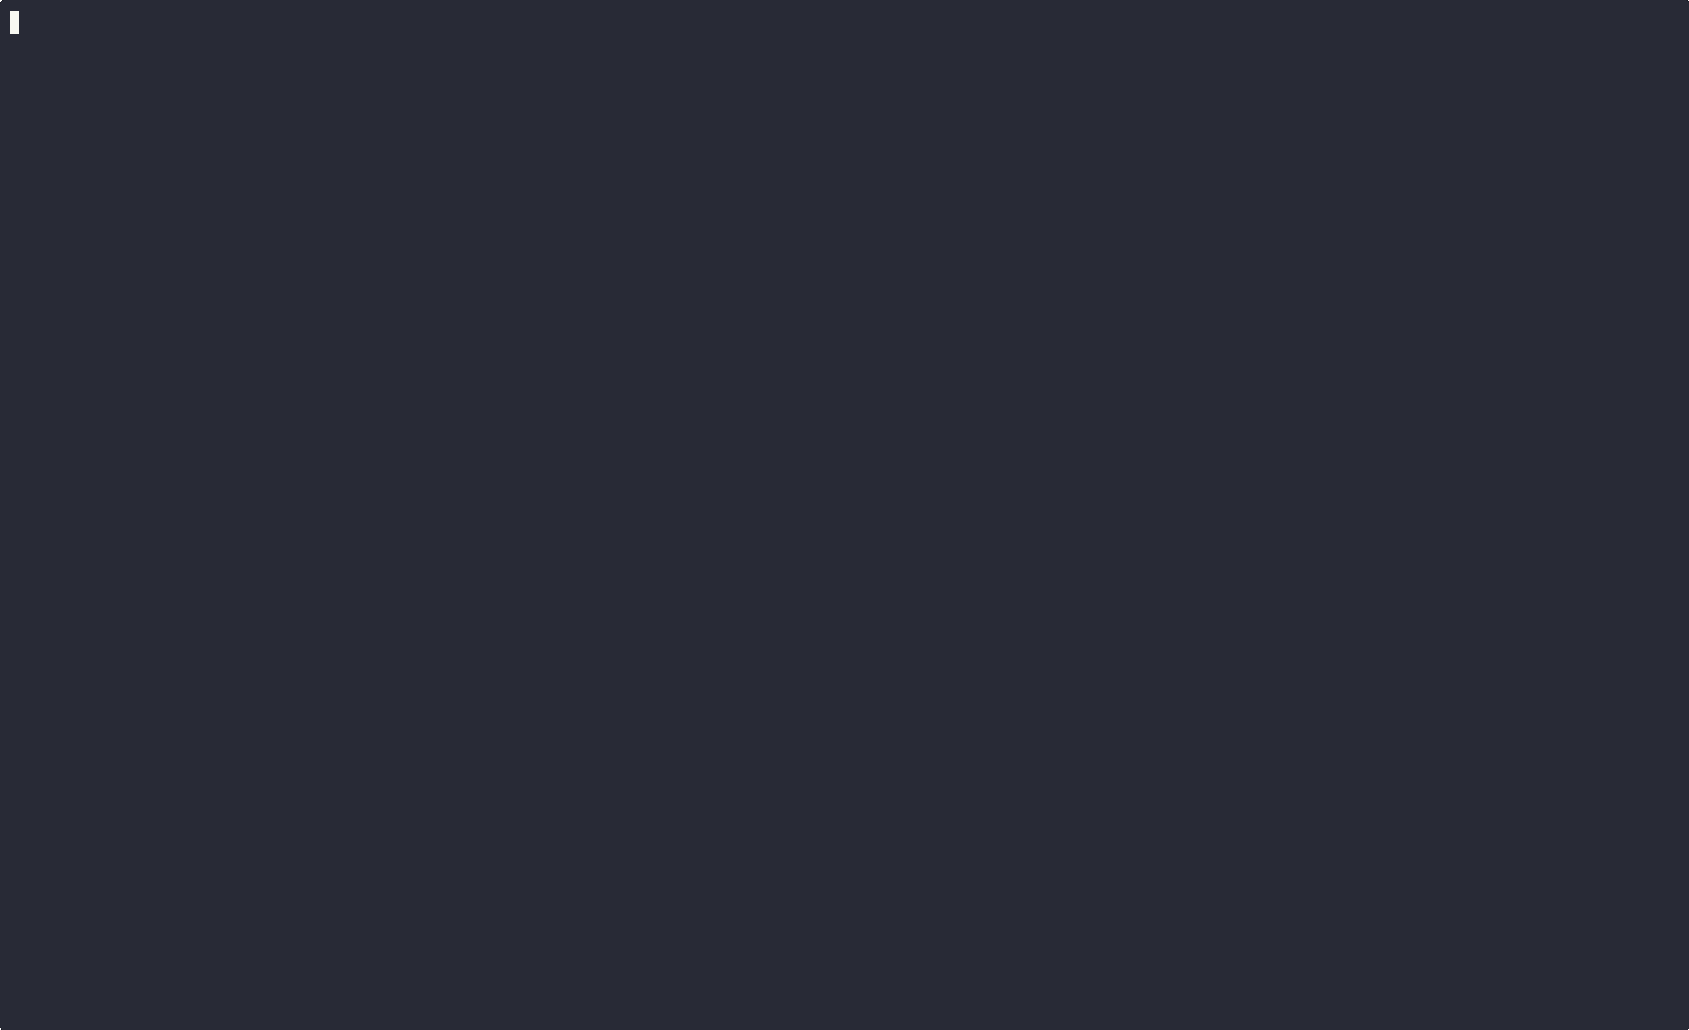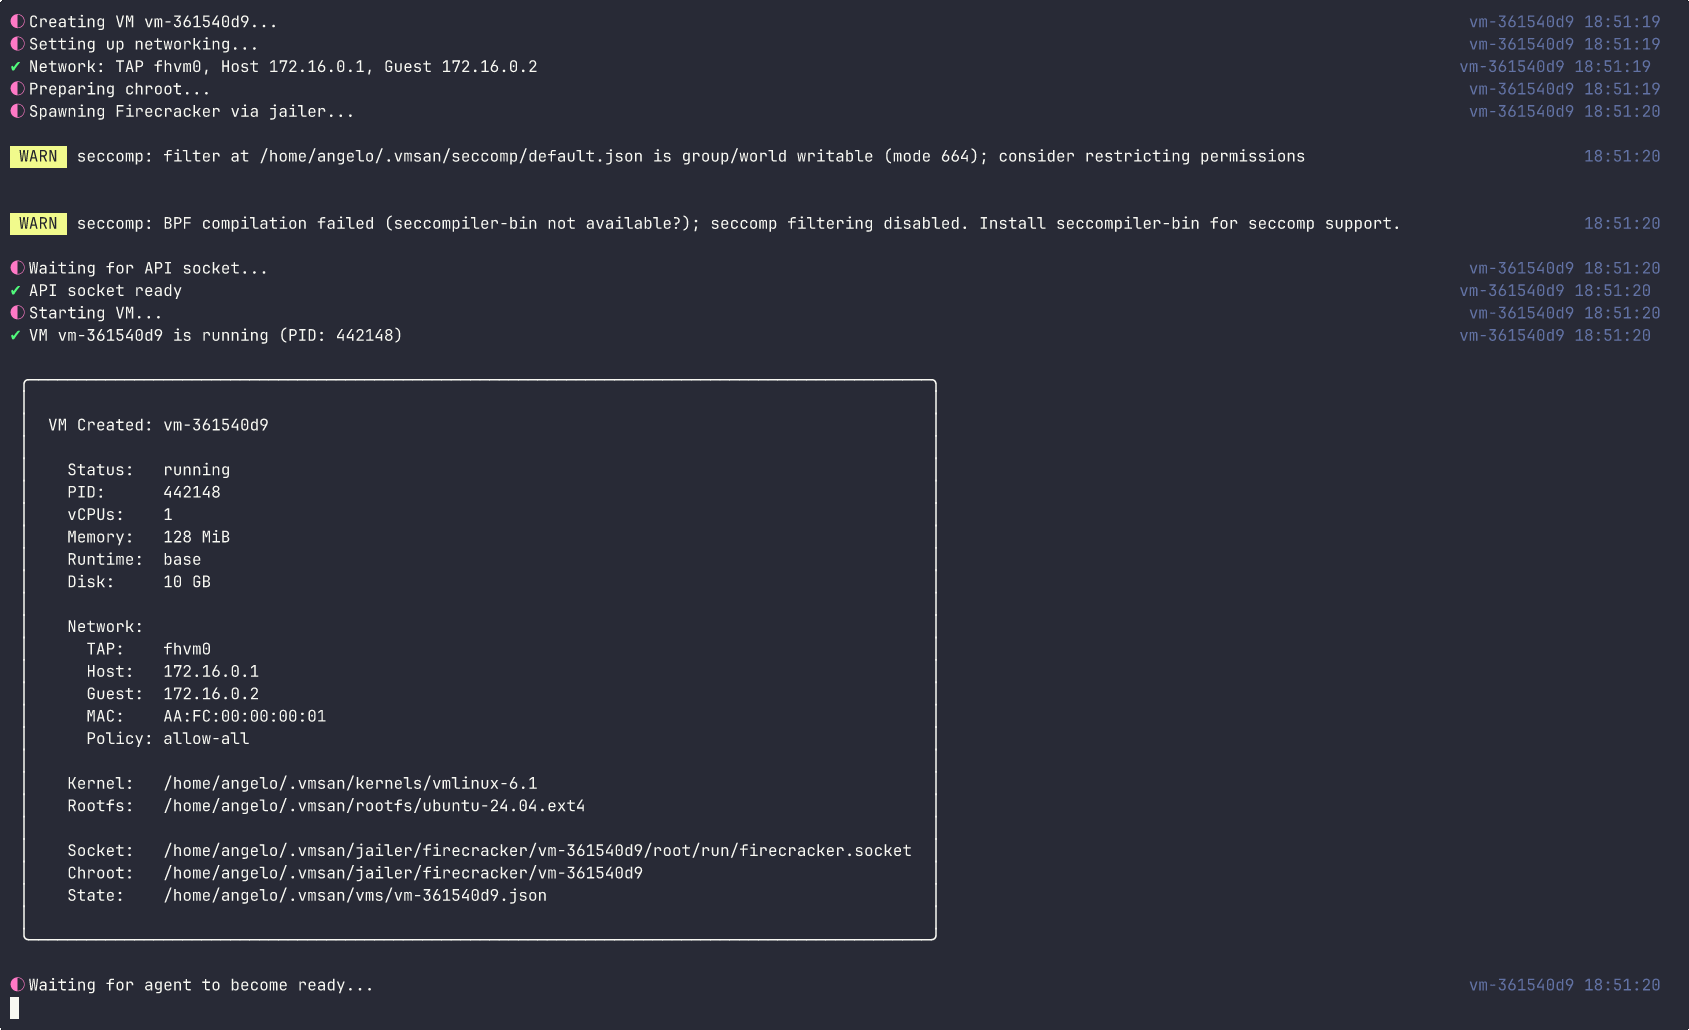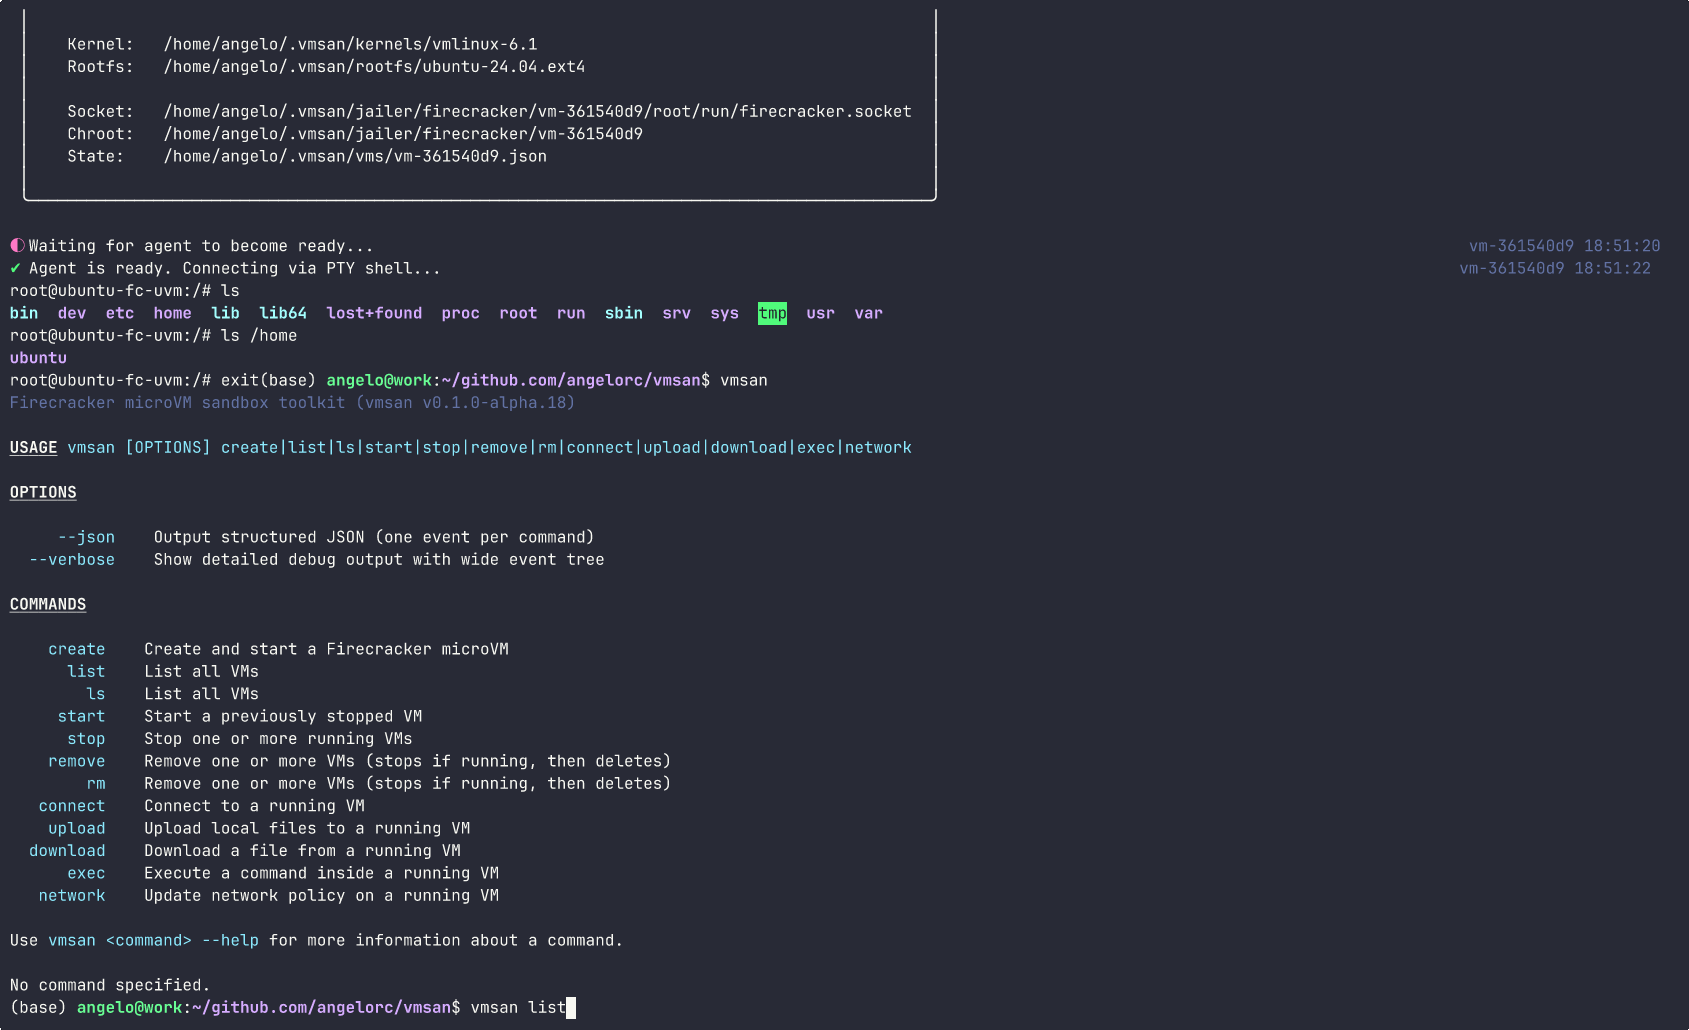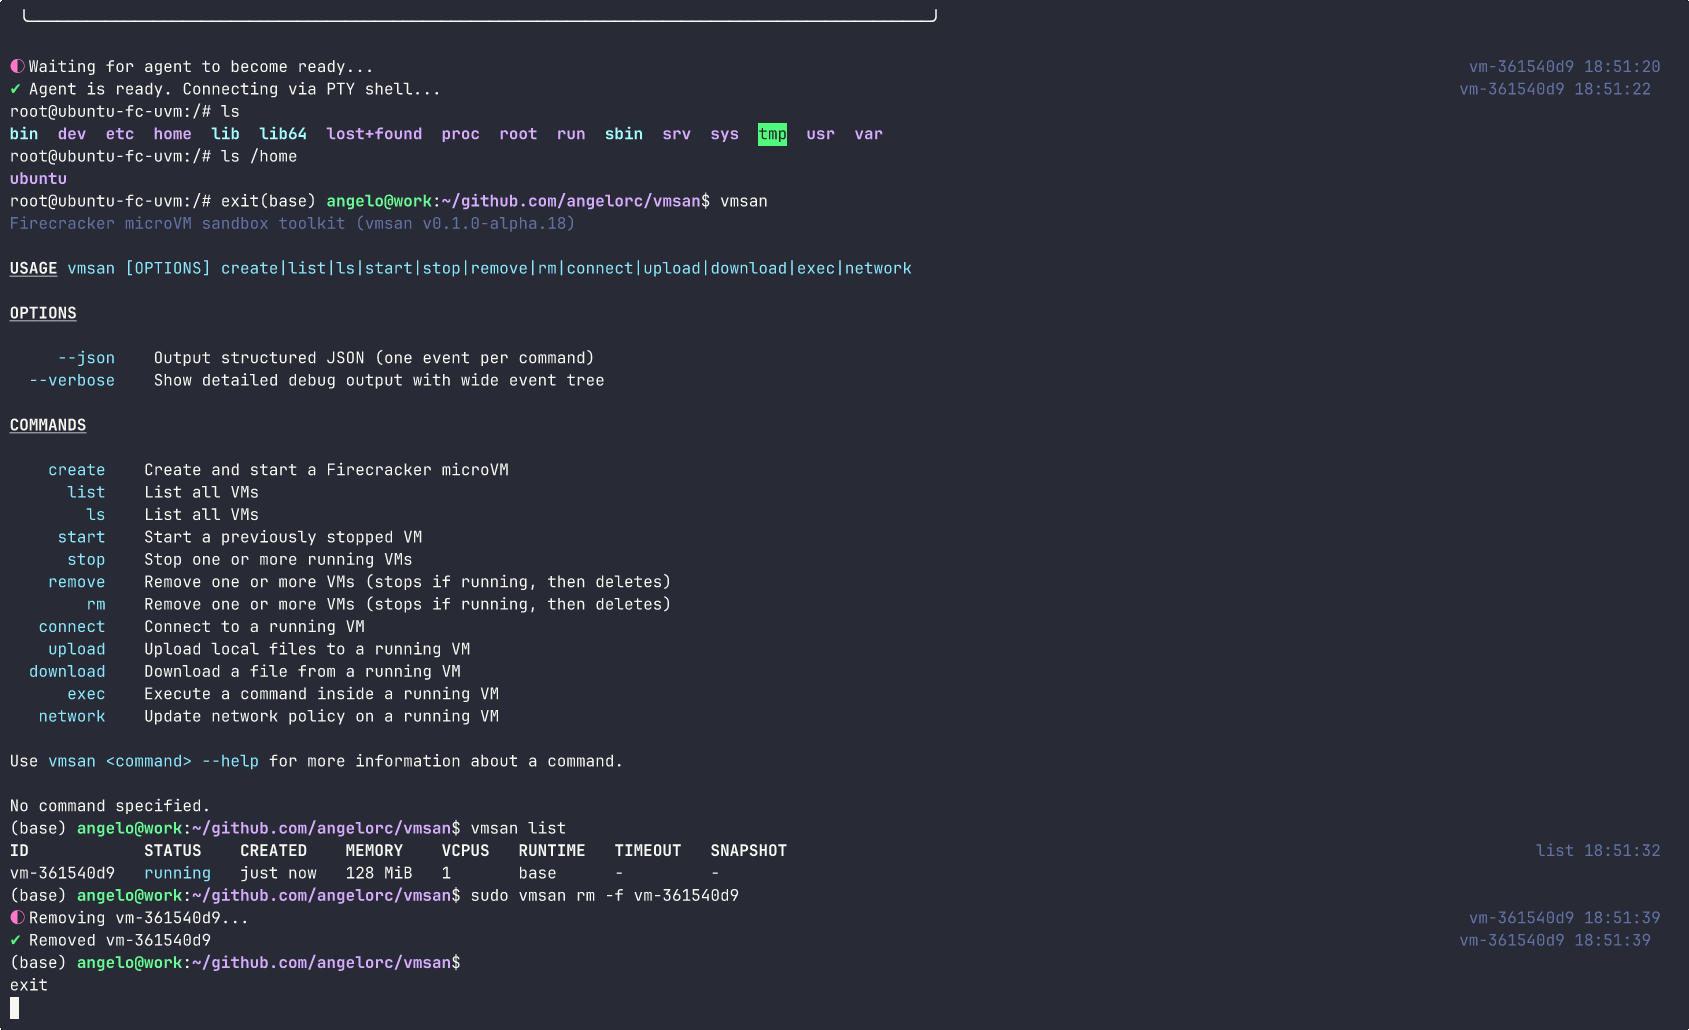 angelorc/vmsan
Firecracker made simple. Spin up secure microVMs in milliseconds, from install to interactive shell in one command.
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
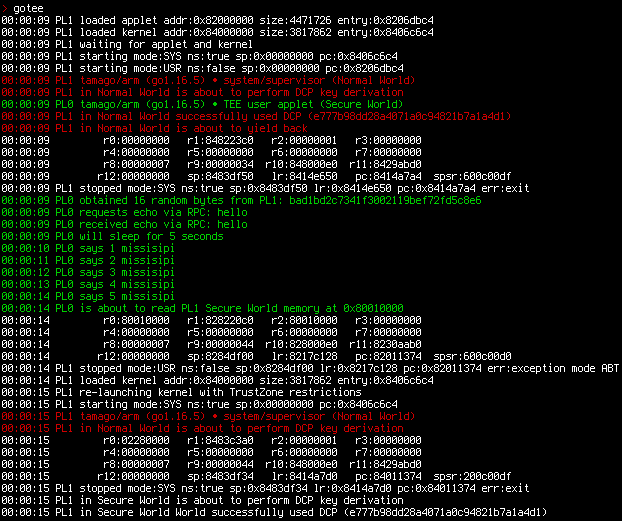 usbarmory/gotee
Go Trusted Execution Environment (TEE)
 usbarmory/gotee-example
GoTEE - example application
 intel/device-modeling-language
Domain-specific language for writing fast functional device models for virtual platforms. Compiles DML to C with API calls tailored for the Intel…
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 microsoft/secureboot_objects
Microsoft's curated repository of secure boot objects (KeK, Db, Dbx) for firmware and runtime, enabling transparent revocation updates and…
 0xballpoint/load
Lord Of Active Directory - automatic vulnerable active directory on AWS
 0xblackash/cve-2026-64531
Reference analysis of a Linux kernel Open vSwitch memory-corruption vulnerability, covering root cause, impact, detection commands, and mitigation…