

snapchange
 awslabs/snapchange
Lightweight fuzzing of a memory snapshot using KVM
debuggersdynamic-analysis-sandboxingdynamic-code-analysis+3
4722 years ago
awslabs/snapchangeLightweight fuzzing of a memory snapshot using KVM
 davidcarliez/trustmebro
Bypass llm guardrails by confusing it with fabricated tool output.
 getkern/kern
Rootless container runtime and sandbox that launches kernel-enforced OCI images in milliseconds with no daemon, featuring resource profiles, seccomp…
 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
 monad-developers/ultrafuzz
End-to-end agentic smart contract fuzzing and threat hunting
 ricccrd/dd
JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 amlalabs/amla-sandbox
WASM sandbox with capability enforcement for AI agent code. Agents can only call explicitly provided tools with defined constraints. Sandboxed…
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
 rcarmo/agentbox
Docker-based sandbox for coding agents with isolated environments, preinstalled agent tooling, service control, and workspace bootstrap for secure…
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 nccgroup/wubes
Qubes containerization on Windows
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 pwnfunction/sandbox
Run untrusted AI code safely, fast
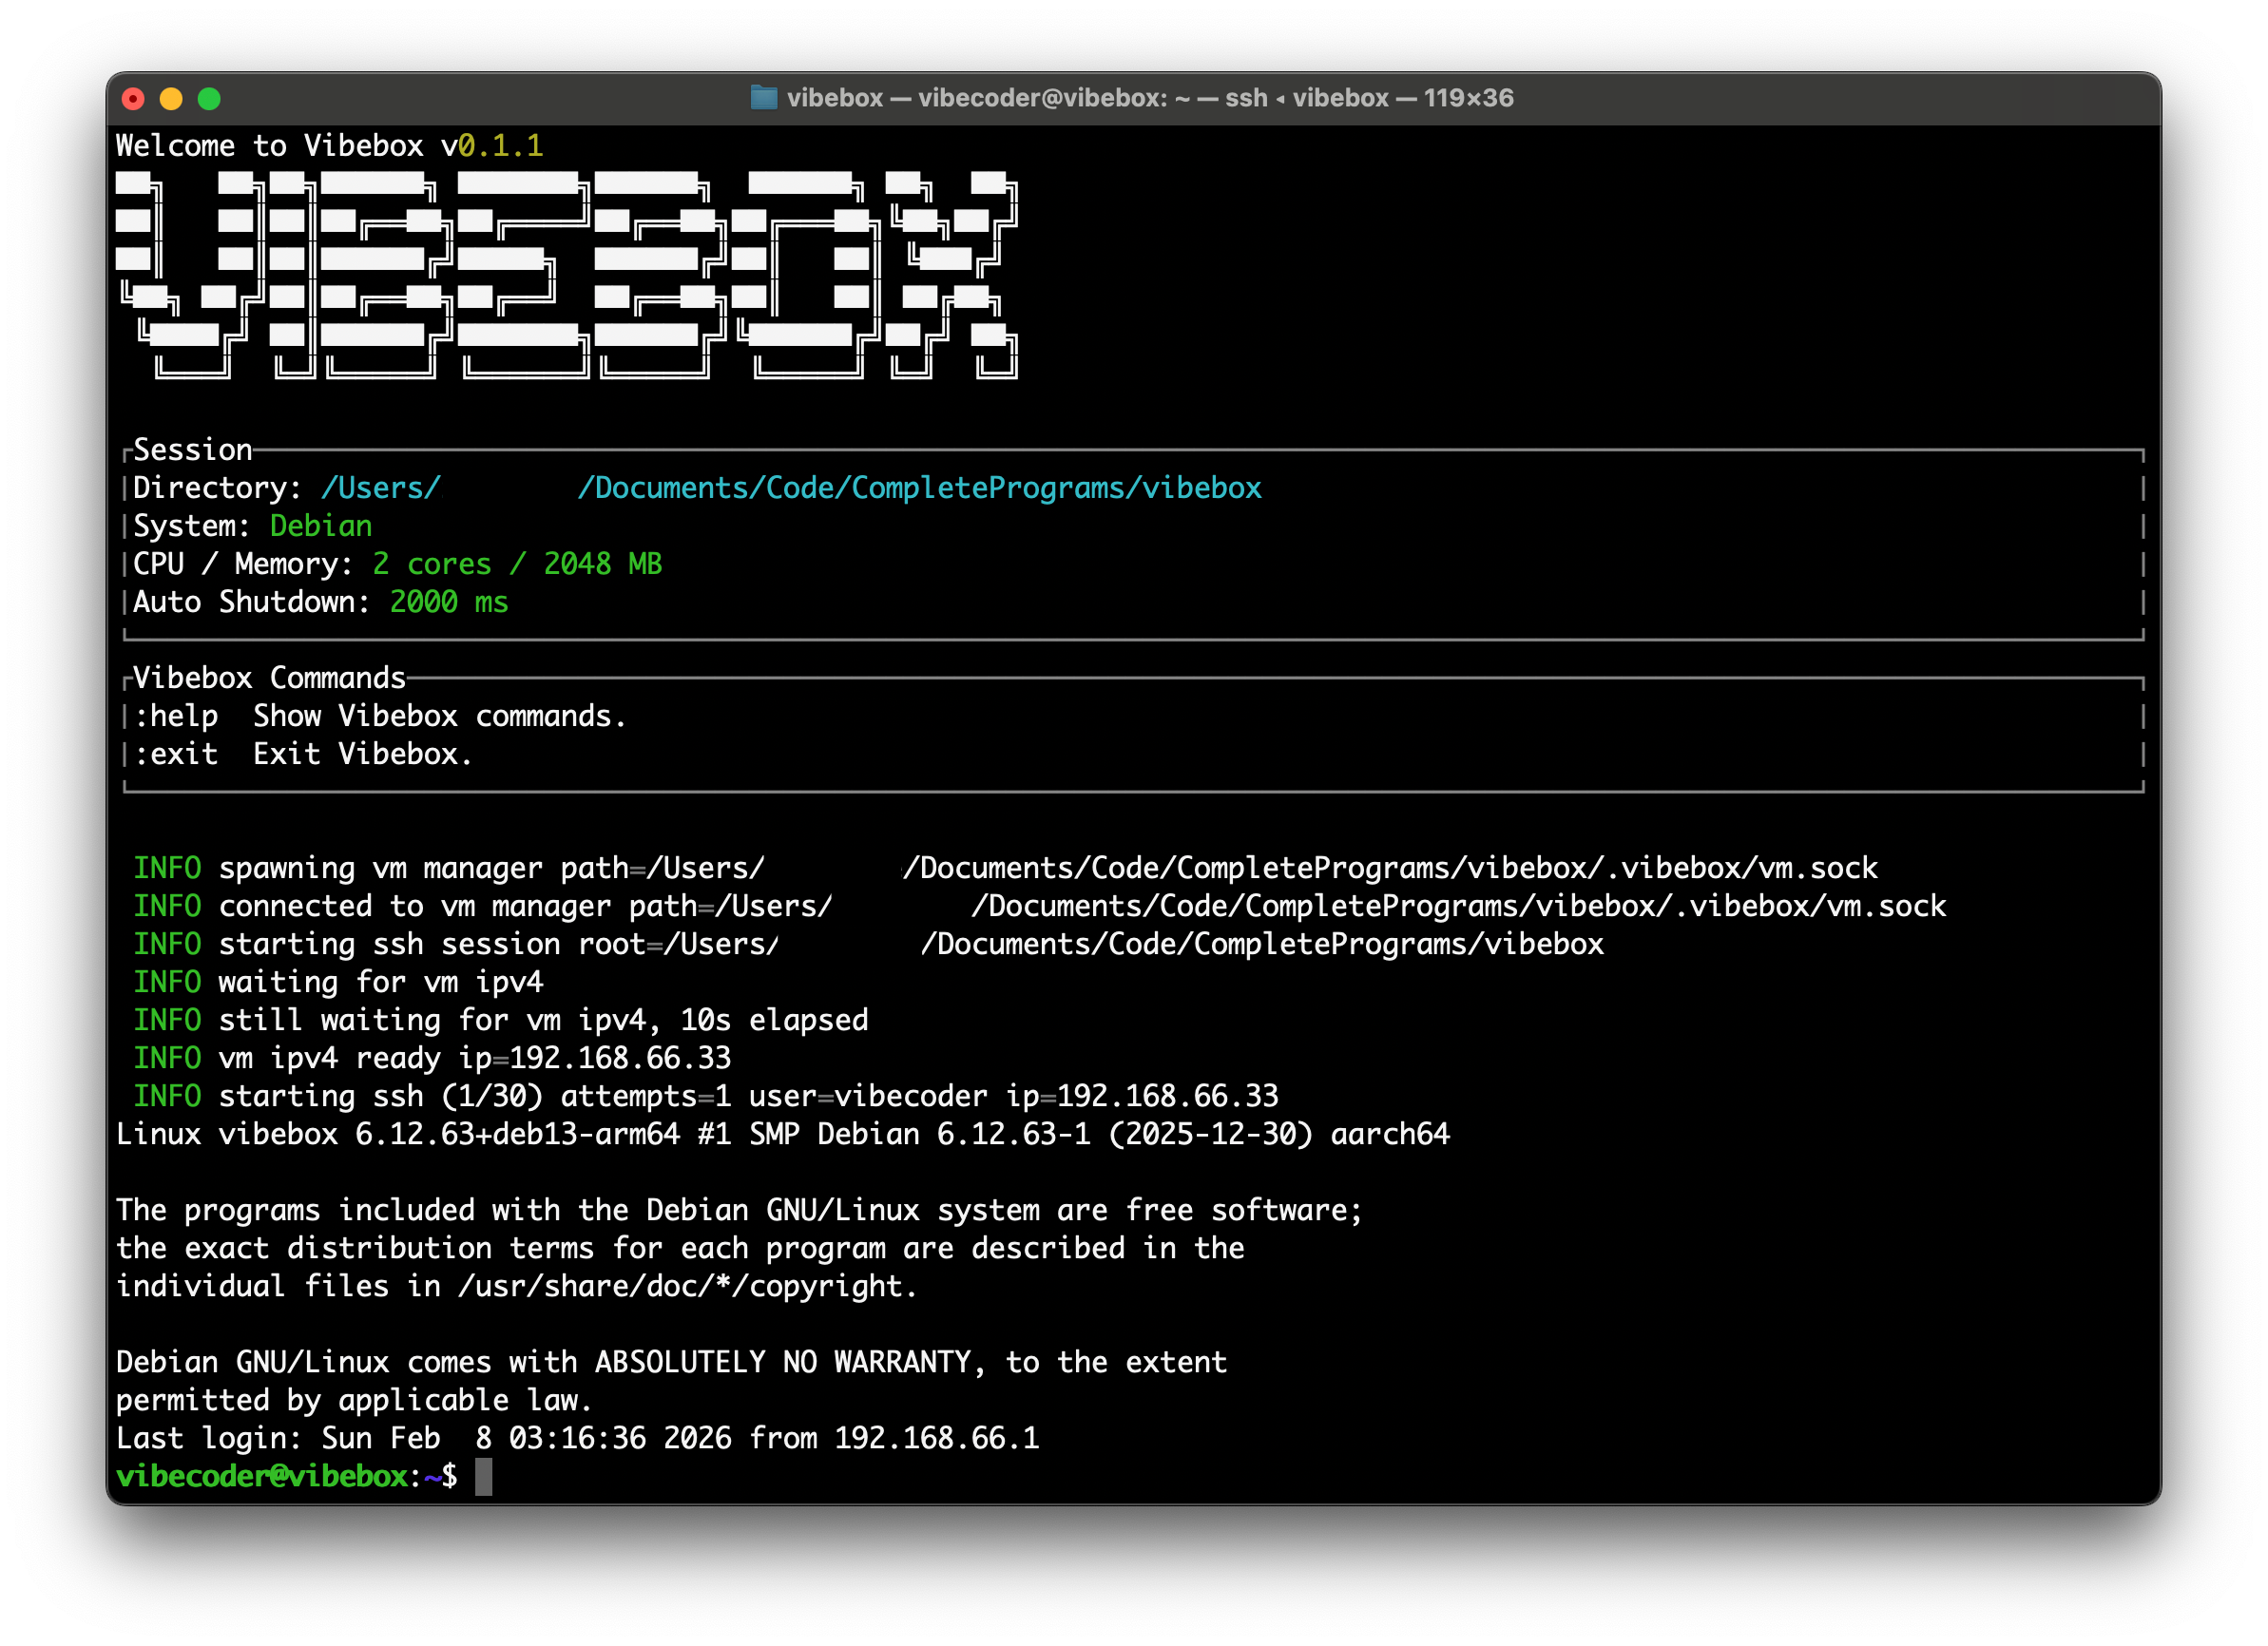 robcholz/vibebox
Ultrafast CLI on Apple Silicon macOS for fast, sandboxed development and LLM agents.
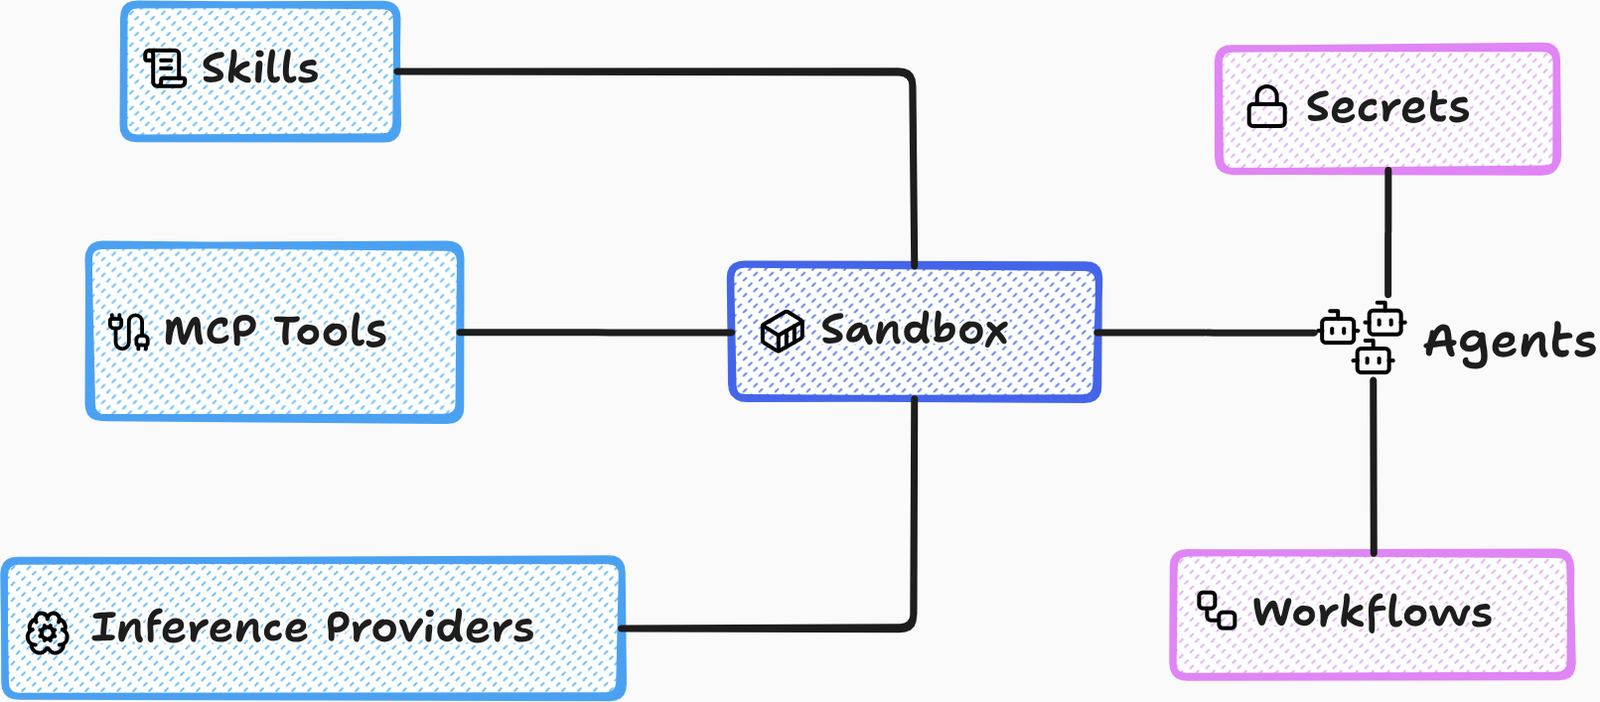 accuknox/agentz
Zero-trust agentic AI platform. Supports SaaS and OnPrem (airgapped) deployments.
 markakd/container_escape
Container escape proof-of-concept exploits for CVE-2026-80521 and CVE-2026-52910, with a disposable QEMU/Ubuntu VM harness for safe PoC execution.