
blackarch
 blackarch/blackarch
An ArchLinux based distribution for penetration testers and security researchers.
curated-resourceseducationexploit-frameworks+8
3.5k3 days ago
blackarch/blackarchAn ArchLinux based distribution for penetration testers and security researchers.
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 patriksimek/vm2
Isolated JavaScript sandbox for Node.js that runs untrusted code with restricted access to built-in modules and host resources via Proxy-based…
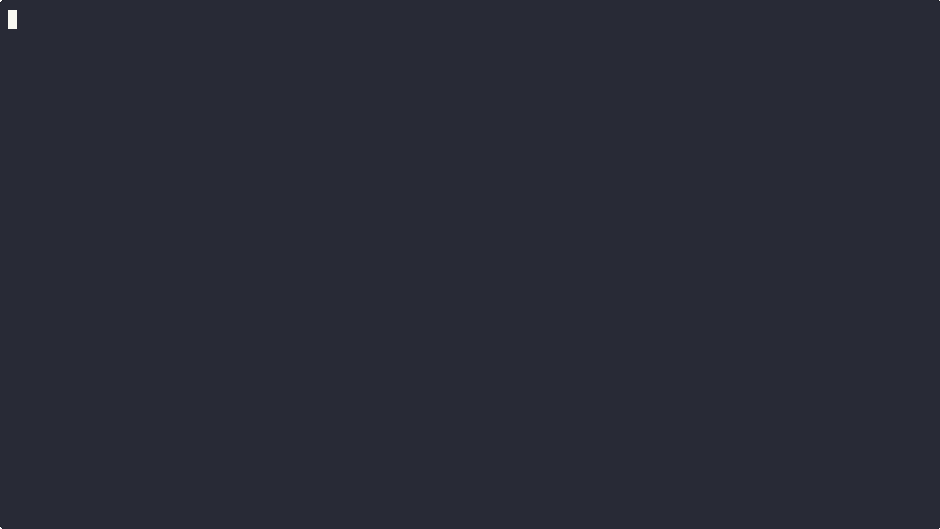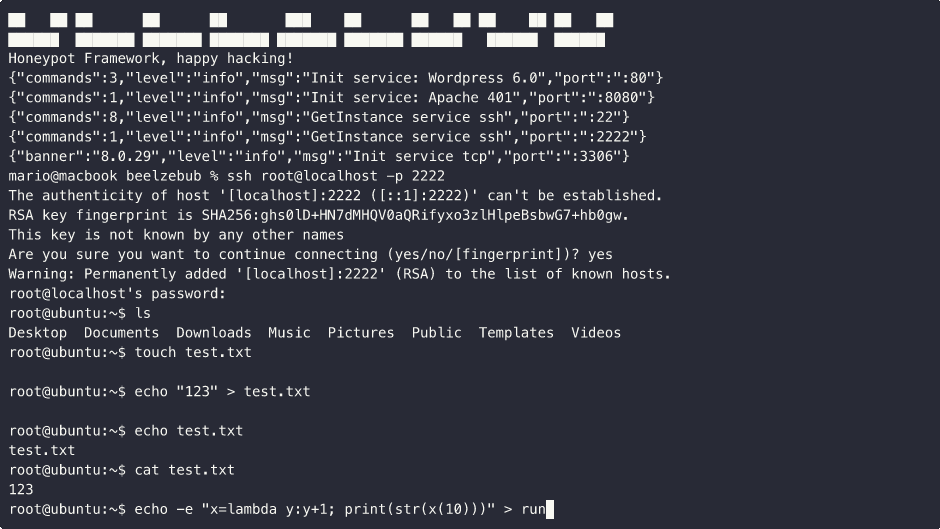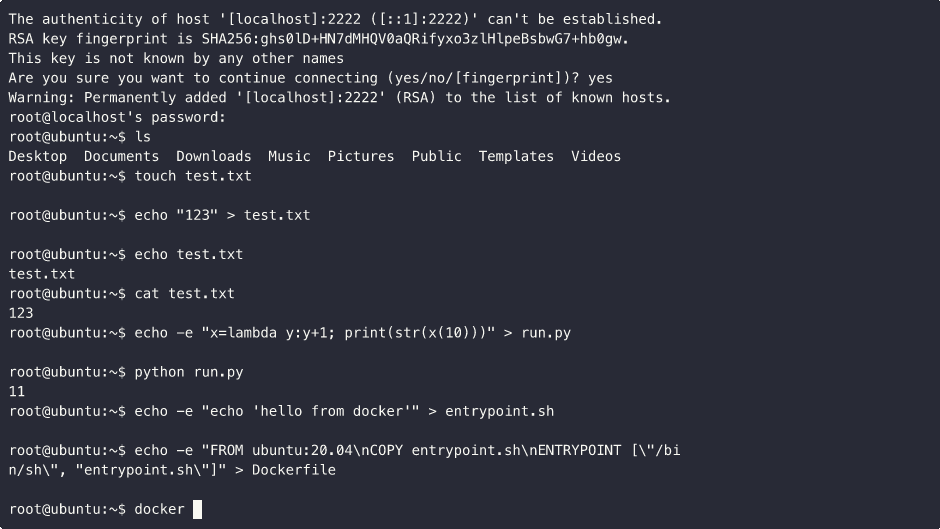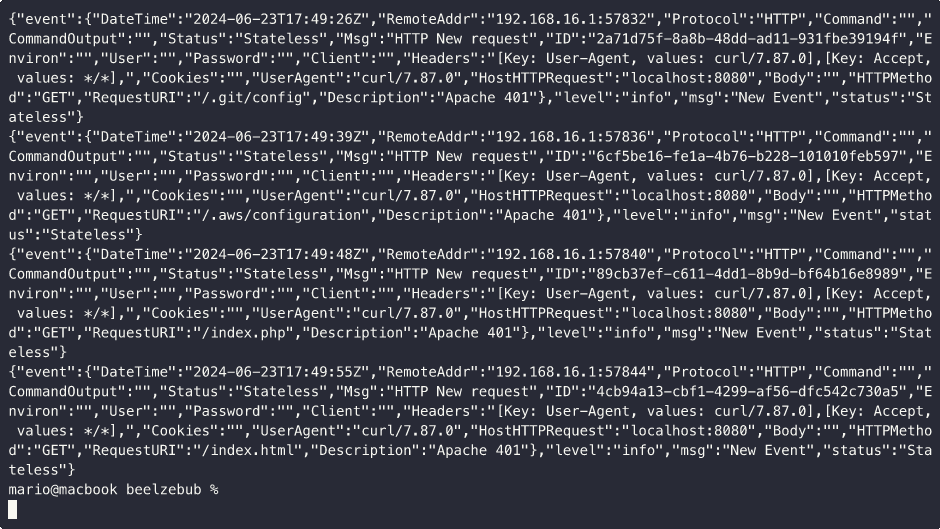 beelzebub-labs/beelzebub
A secure low code deception runtime framework, leveraging AI for System Virtualization.
 usbarmory/tamago
Framework for compiling and executing Go applications on bare metal processors, enabling secure firmware development with reduced attack surface…
 lxc/incus-os
Immutable Linux OS image optimized for running Incus containers and virtual machines, with UEFI Secure Boot, TPM 2.0 disk encryption, and automated…
 pentoo/pentoo-overlay
Gentoo overlay for security tools as well as the heart of the Pentoo Livecd
 s3n4t0r-0x0/bear-c2
The exploit server for out-of-band findings. Point a target at a domain you own. Every HTTP request and every email it sends back lands in a…
 tandasat/hypervisor-101-in-rust
The materials of "Hypervisor 101 in Rust", a one-day long course, to quickly learn hardware-assisted virtualization technology and its application…
 harbor-framework/terminal-bench-2
Benchmark for evaluating AI agents on real-world tasks including vulnerability resolution, code debugging, and protein assembly in containerized…
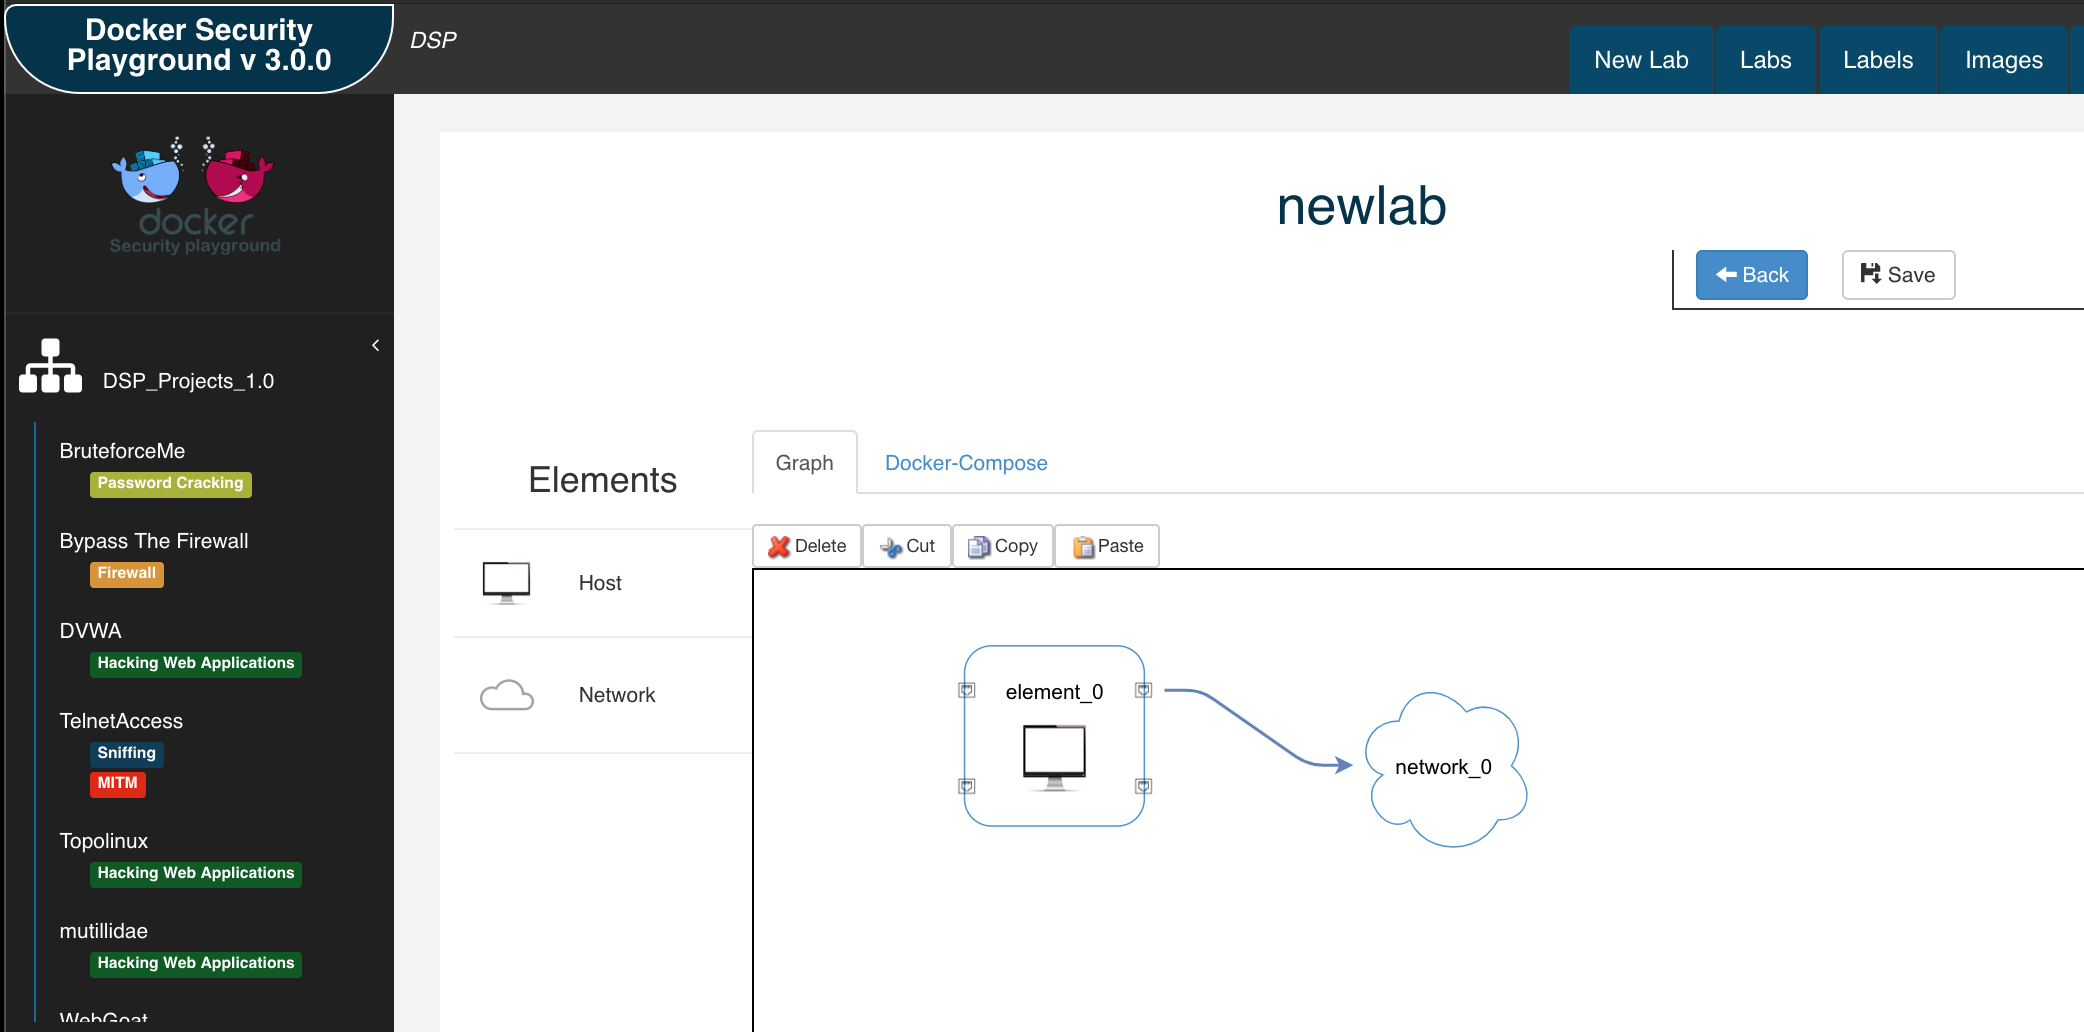 dockersecurityplayground/dsp
A Microservices-based framework for the study of Network Security and Penetration Test techniques
 qubesos/qubes-core-admin
Manages the core lifecycle of Qubes OS domains via a Python admin API, handling secure compartmentalization with Xen and exposing an event system for…
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
 devzero-security/redstackpro
A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud…
 ressl/cve-2026-87902-poc
PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…
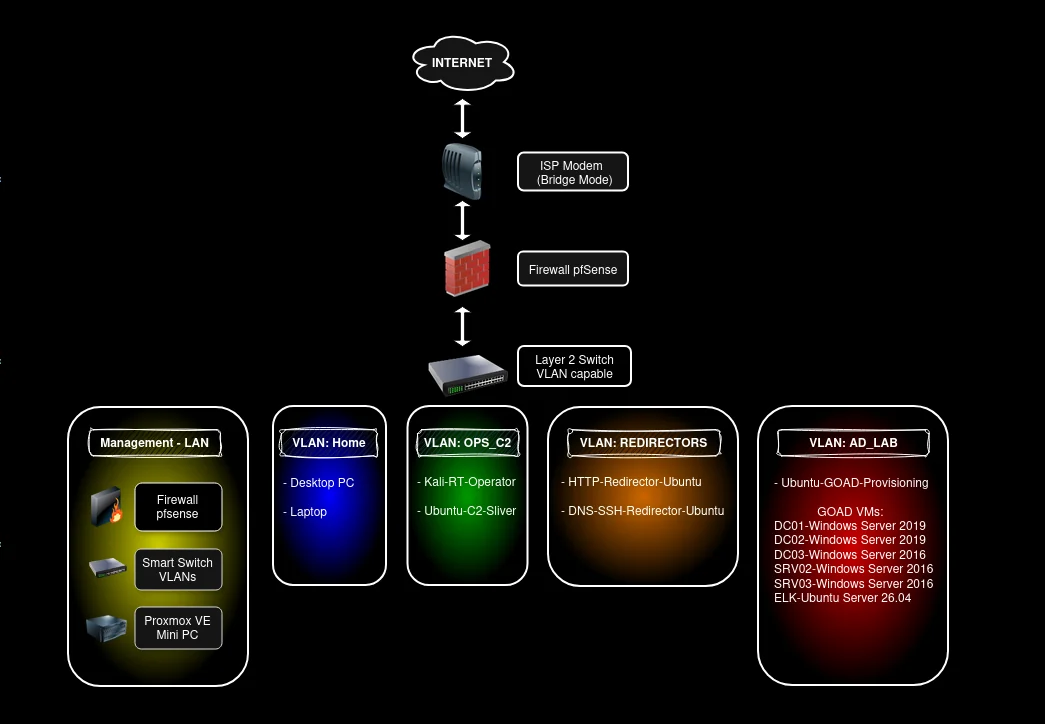 pho5nix/red-team-goad-lab-proxmox
Build guide for Red Teaming home lab. GOAD lab setup in Proxmox and pfSense, Operator/C2 and Redirectors.
 guneykabel/cve-2026-85706
Python PoC exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass, with writeup and…
 dmdhrumilmistry/security-harness
Multi-agent static application-security review harness for AI coding agents: maps codebases, hunts vulnerability classes, chains and verifies…