
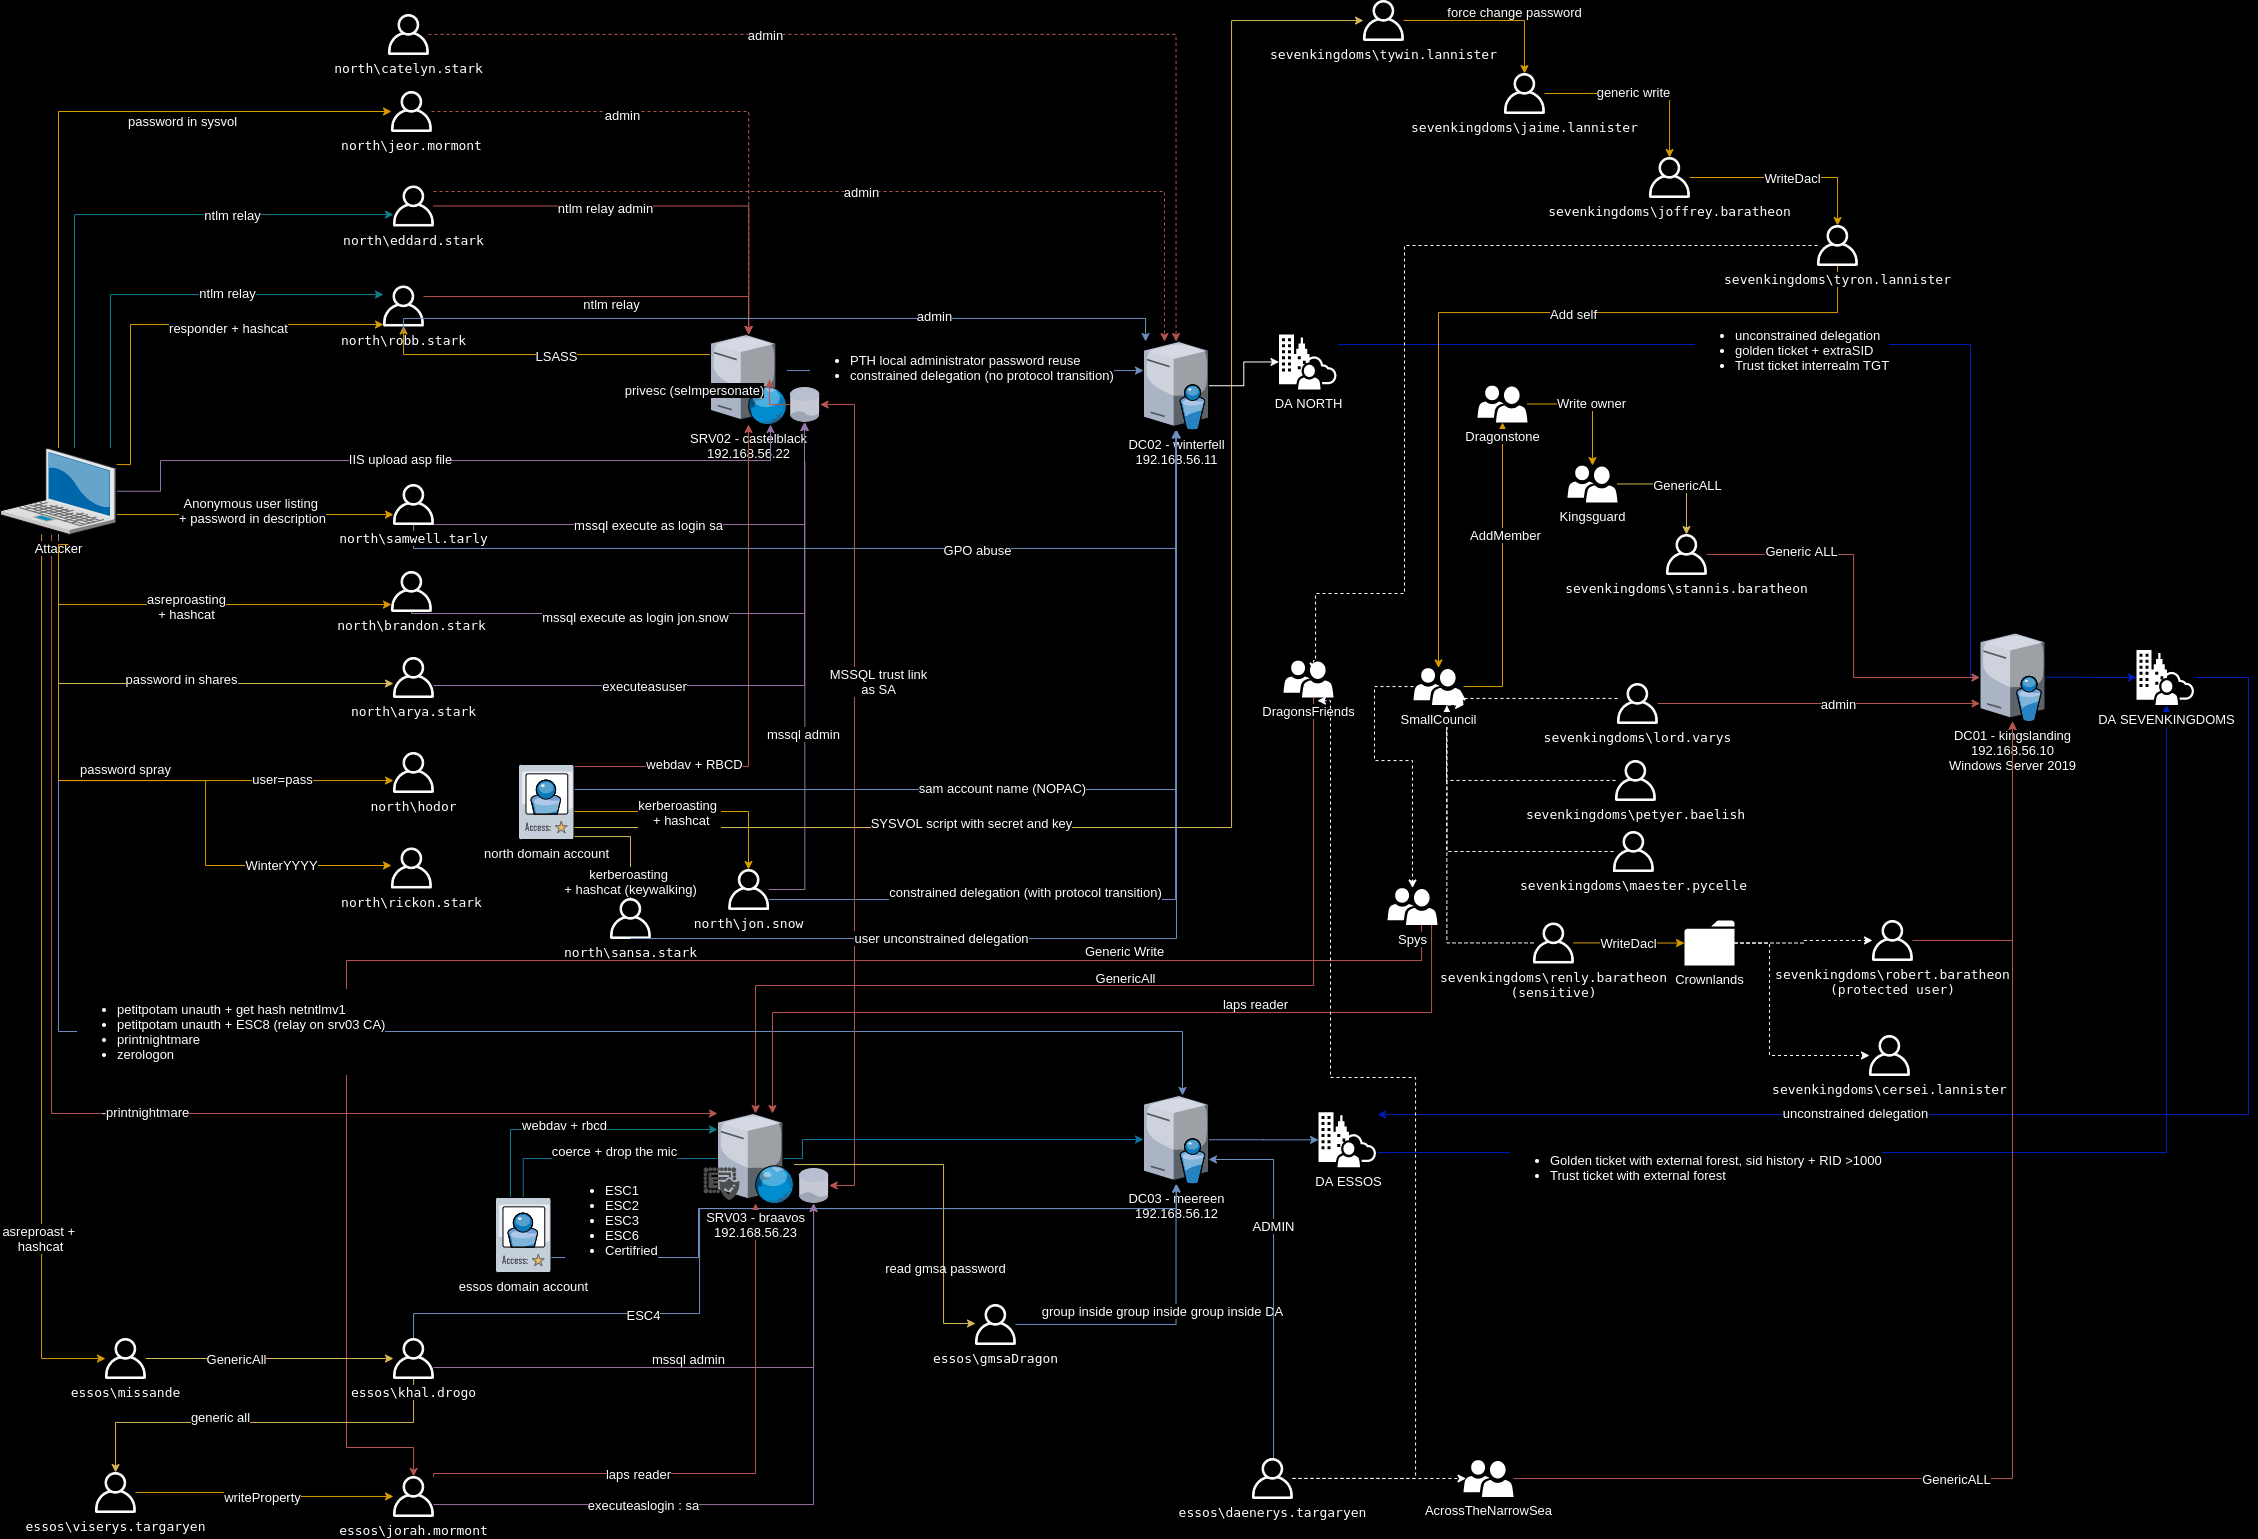
deploy-goad
 lkarlslund/deploy-goad
Script to install prerequisites for deploying GOAD on Ubuntu Linux 22.04
educationlabs-practicepenetration-testing+1
116
lkarlslund/deploy-goadScript to install prerequisites for deploying GOAD on Ubuntu Linux 22.04
 jinook-kim/cve-2025-64512_poc
Python PoC for CVE-2025-64512, a pdfminer.six pickle deserialization RCE. Generates gzipped pickle payloads and polyglot PDFs, then delivers them to…
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
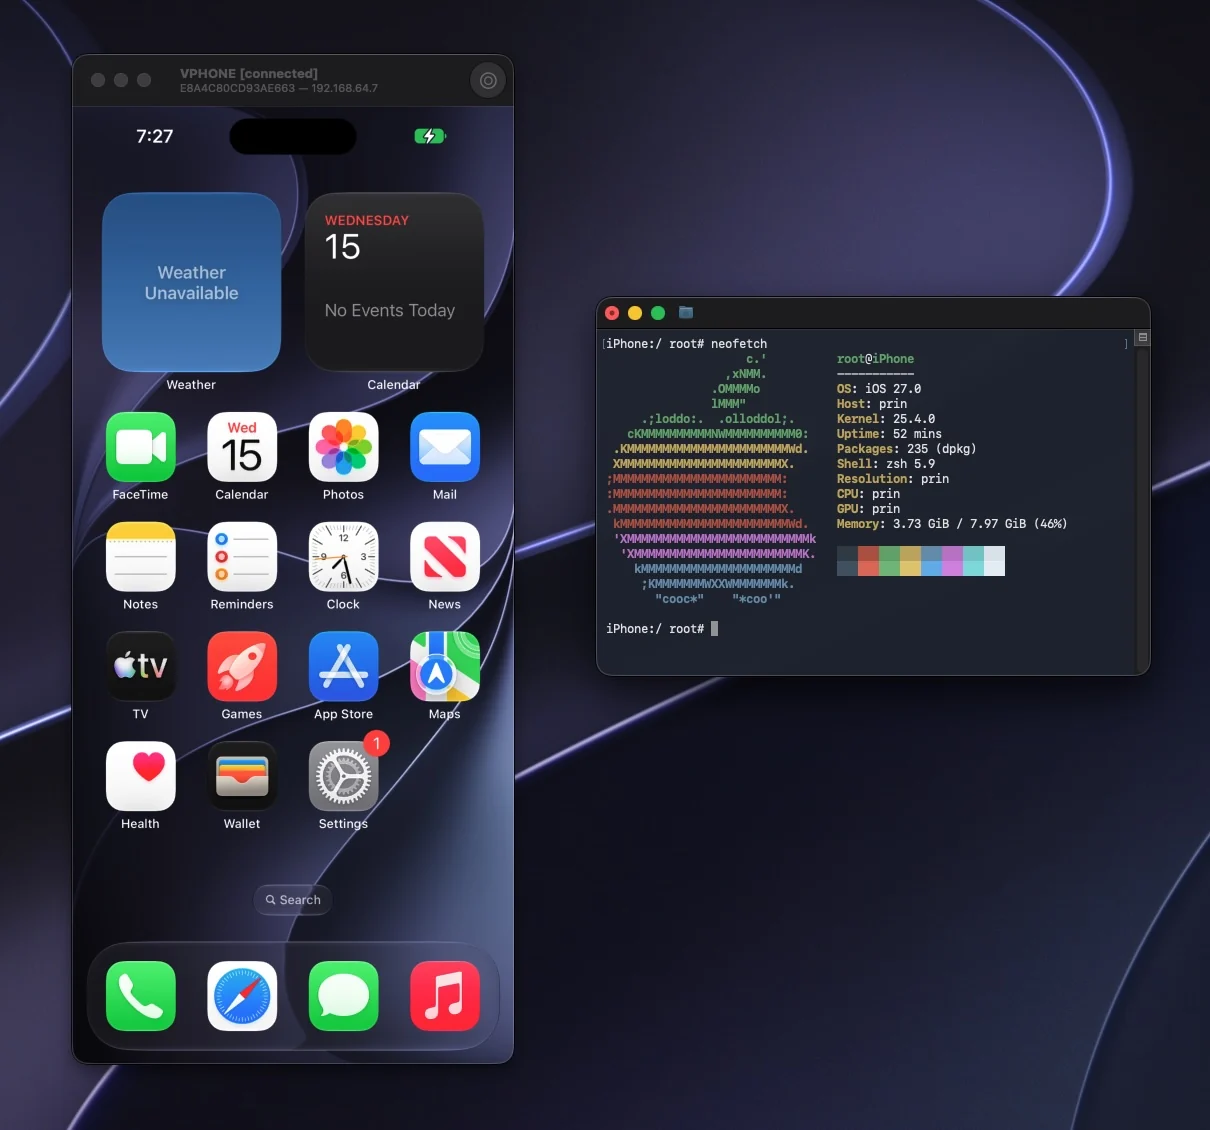 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 guneykabel/cve-2026-85706
Python PoC exploit for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab CE/EE via Workhorse path-encoding bypass, with writeup and…
 wgnet/wg.copyfail.patch
eBPF-based workaround for CVE-2026-31431 (Copy.Fail) that filters or kills AF_ALG socket creation to prevent local privilege escalation and container…
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
 hackspeak/cve-2026-64561
Zapscape (CVE-2026-64561) KVM/x86 shadow MMU UAF guest-to-host escape PoC mirror — V4bel/@v4bel, MIT; for authorized security testing
 spensercai/copy_fail
Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
 atiilla/cve-2026-2441_poc
Proof-of-concept exploit for CVE-2026-2441, demonstrating the vulnerability and providing a working exploit for security testing and validation.
 ayub0x7/cve-2024-32019-poc
Checks Netdata ndsudo SUID PATH privilege escalation exposure for CVE-2024-32019 and validates patches without weaponized exploitation.
 nikeee/cve-2026-27607
Proof-of-concept exploit for CVE-2026-27607, a missing post-policy validation in RustFS, demonstrating the vulnerability with a Node.js script and…
 0xcyberstan/cve-2026-59346-poc
PoC for CVE-2026-59346 - 32-bit integer overflow in VMware's VMXNET3 TSO segmentation path, guest-to-host crash.
 tc4dy/cve-2026-82329-poc-exploit
Exploit and detection toolkit for CVE-2026-82329, a JFrog Artifactory auth bypass. Forges join JWTs to mint admin tokens; includes a non-intrusive…
 gerhart01/hyperv_local_dos_poc
CVE-2020-0890 | Windows Hyper-V Denial of Service Vulnerability proof-of-concept code
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.
 squeeze440/zotlit-poc
PoC — attachment import copies files from unapproved local paths in ZotLit (GHSA-4qh7-66xv-h329, CVE-2026-87000, CVSS 5.5).