
litebox
 microsoft/litebox
A security-focused library OS supporting kernel- and user-mode execution
cloud-securitycontainer-securityembedded-systems-security+1
2.7k2h 7m ago
microsoft/liteboxA security-focused library OS supporting kernel- and user-mode execution
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 qemu/qemu
Official QEMU mirror. Please see https://www.qemu.org/contribute/ for how to submit changes to QEMU. Pull Requests are disabled. Please only use…
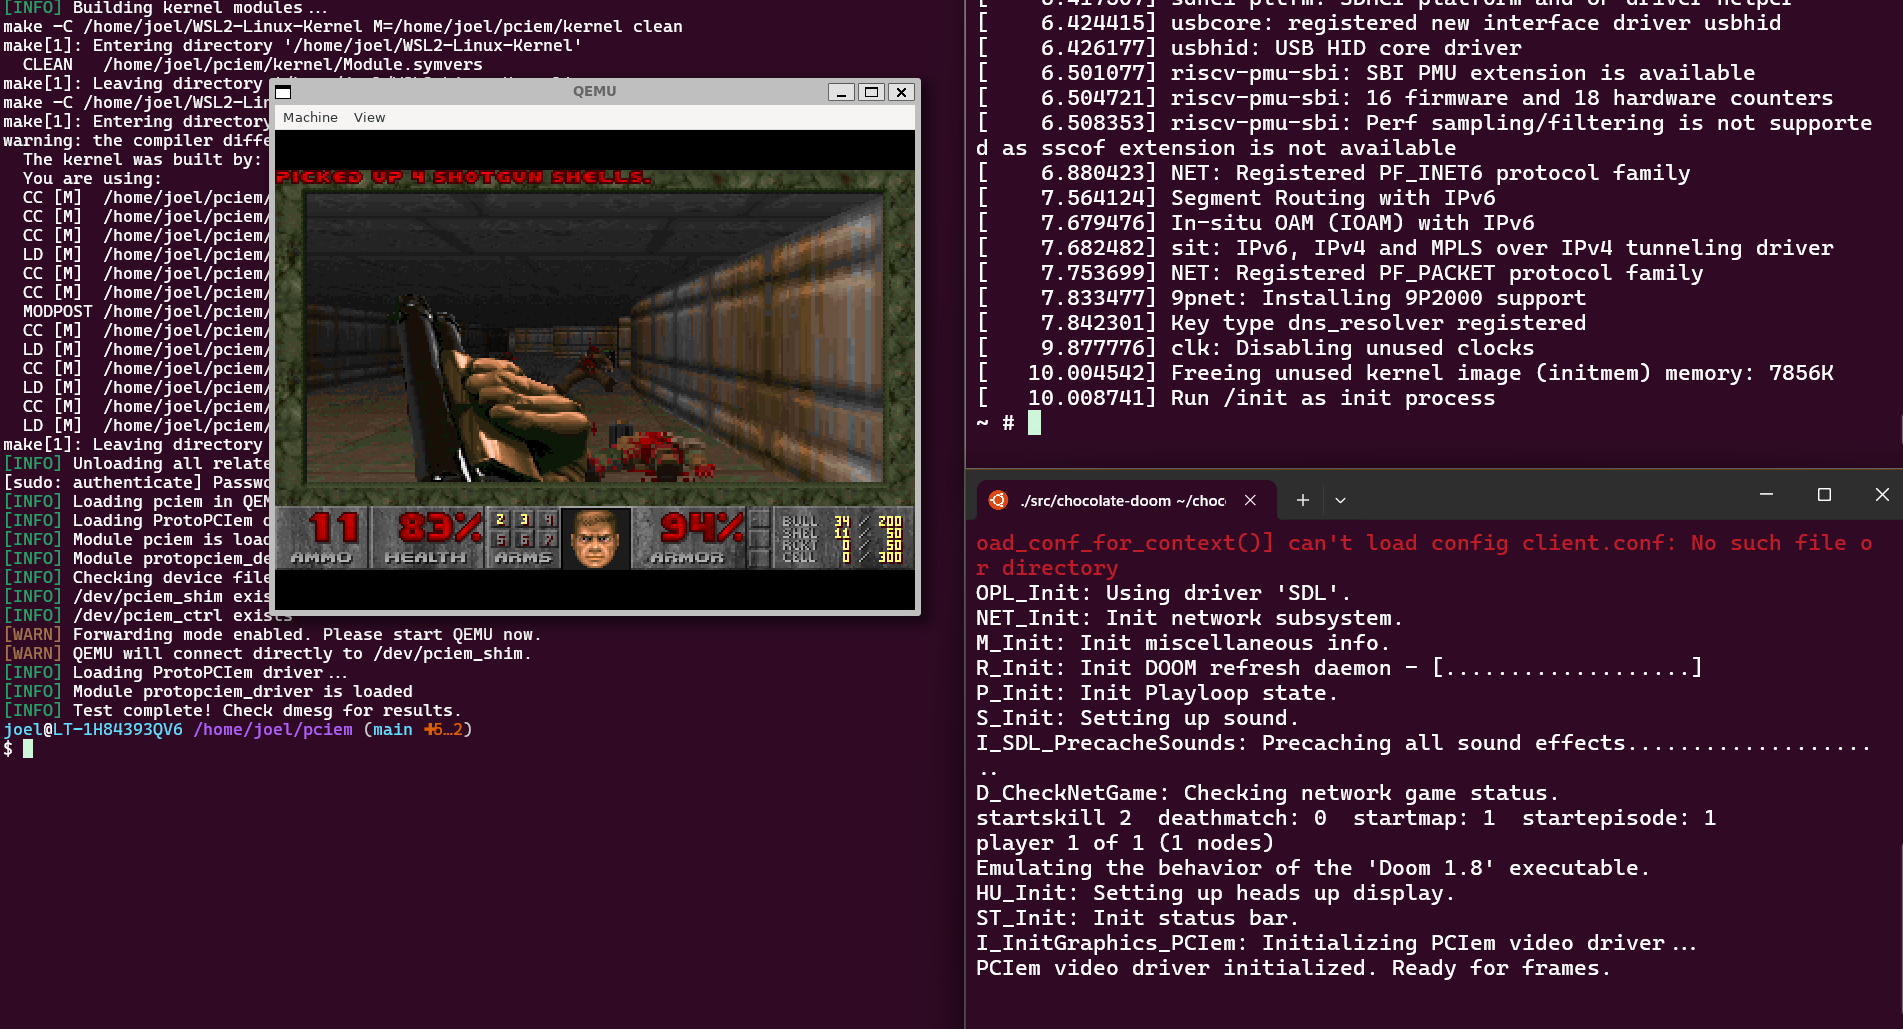 cakehonolulu/pciem
A Linux framework to enable userspace-defined "Virtual" PCIe card shims to enable in-host PCIe card driver development.
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 smol-machines/smolvm
An embeddable, portable, branchable virtual machine to safely run Agents locally.
 intel/device-modeling-language
Domain-specific language for writing fast functional device models for virtual platforms. Compiles DML to C with API calls tailored for the Intel…
 devzero-security/redstackpro
A canvas for red team infrastructure and cyber ranges. Compose a topology, export runnable Terraform and Ansible, and deploy it yourself. Your cloud…
 lxc/incus-os
Immutable Linux OS image optimized for running Incus containers and virtual machines, with UEFI Secure Boot, TPM 2.0 disk encryption, and automated…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 eqstlab/cve-2026-49869
PoC and Docker lab for CVE-2026-49869, an unauthenticated RCE in Kestra OSS via an AuthenticationFilter path bypass that allows flow creation and…
 firecracker-microvm/firecracker
Secure and fast microVMs for serverless computing.
 microsoft/mxc
Policy-driven, layered isolation and containment
 ungabunga-ctf/cve-2026-34990
Python proof-of-concept for CVE-2026-34990 in OpenPrinting CUPS, coercing cupsd to leak a Local auth token and overwrite root files via a file://…
 openedx/codejail
Secure code execution