
smolvm
 smol-machines/smolvm
Branchable computing by using a portable, lightweight, self-contained virtual machine
cloud-infrastructure-securitycontainer-securitydevsecops+2
6.1k
smol-machines/smolvmBranchable computing by using a portable, lightweight, self-contained virtual machine
 kata-containers/kata-containers
Kata Containers is an open source project and community working to build a standard implementation of lightweight Virtual Machines (VMs) that feel…
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
 microsoft/litebox
A security-focused library OS supporting kernel- and user-mode execution
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
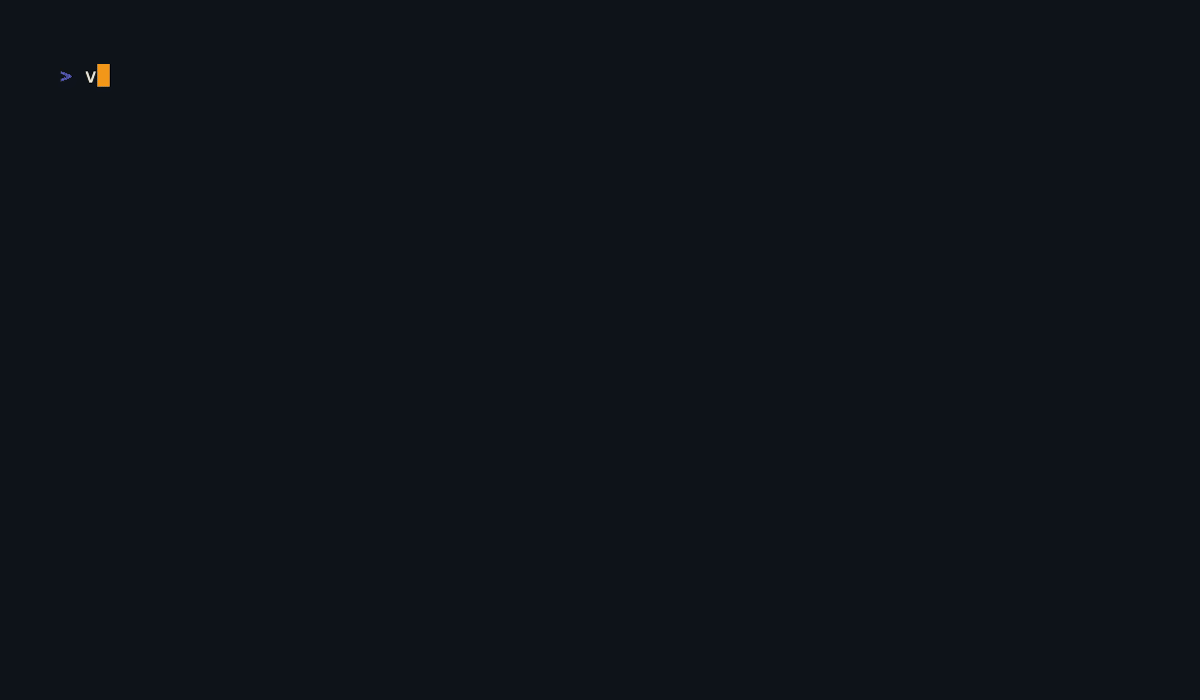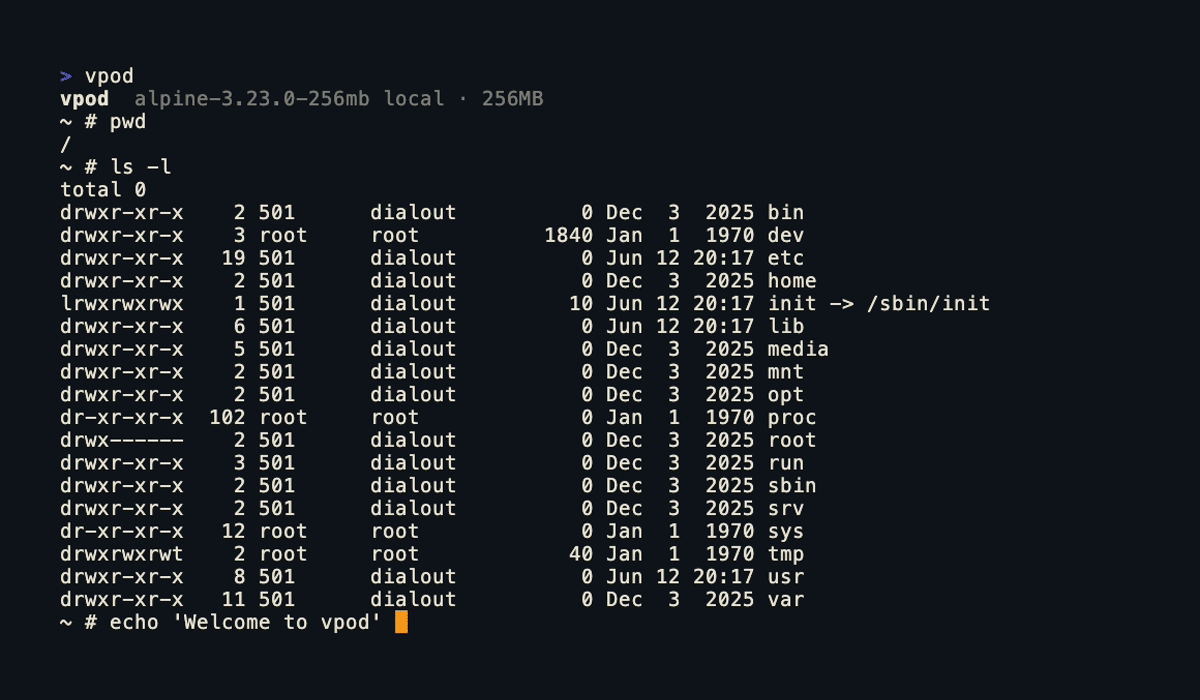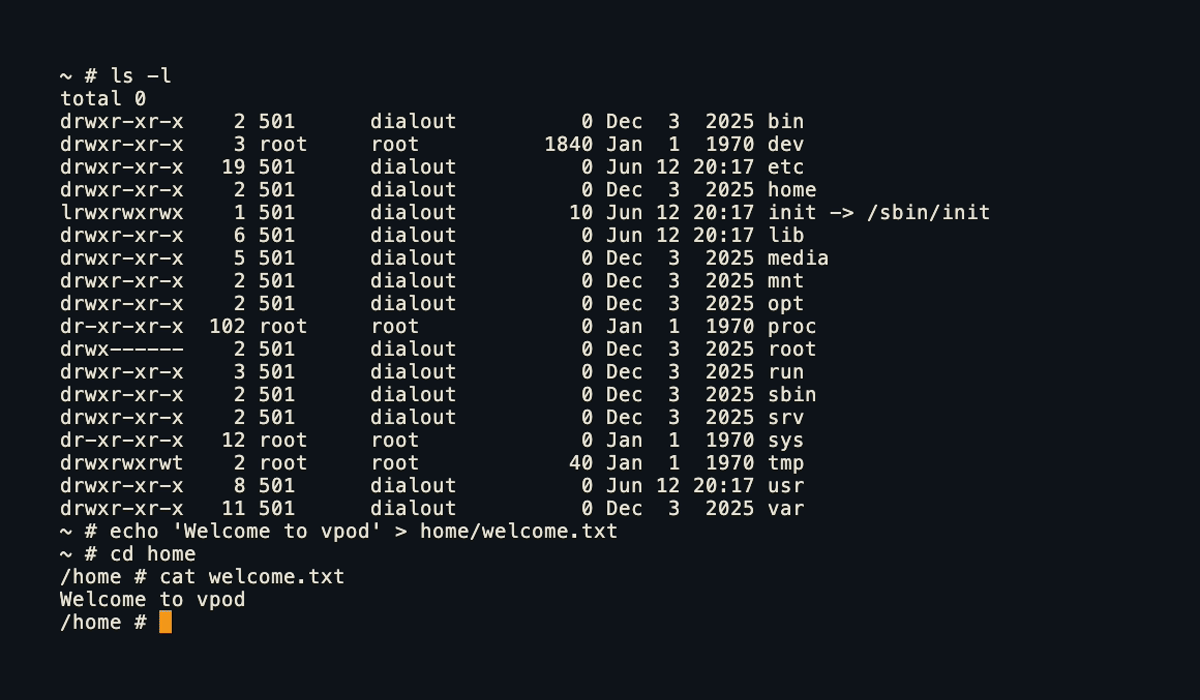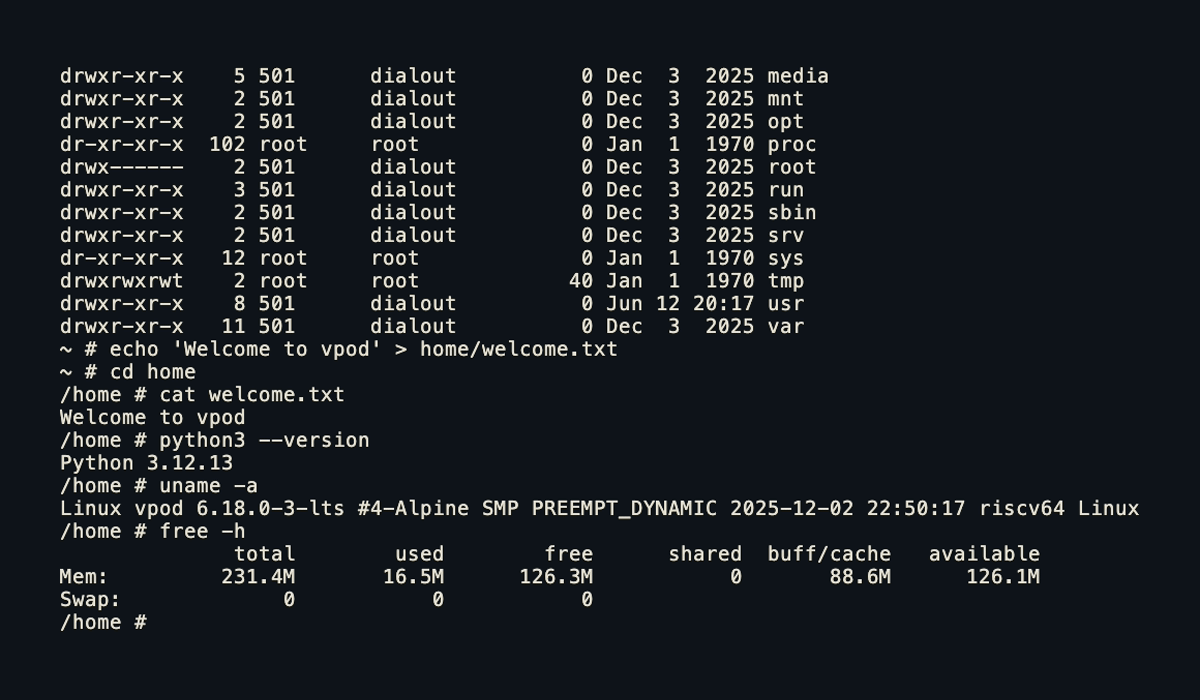 capsulerun/vpod
Lightweight, secure Linux sandboxes for untrusted processes. Runs in the browser and on the server.
 bmax121/apatch
The patching of Android kernel and Android system
 vulhub/vulhub
Pre-Built Vulnerable Environments Based on Docker-Compose
 flatpak/flatpak
Linux application sandboxing and distribution framework
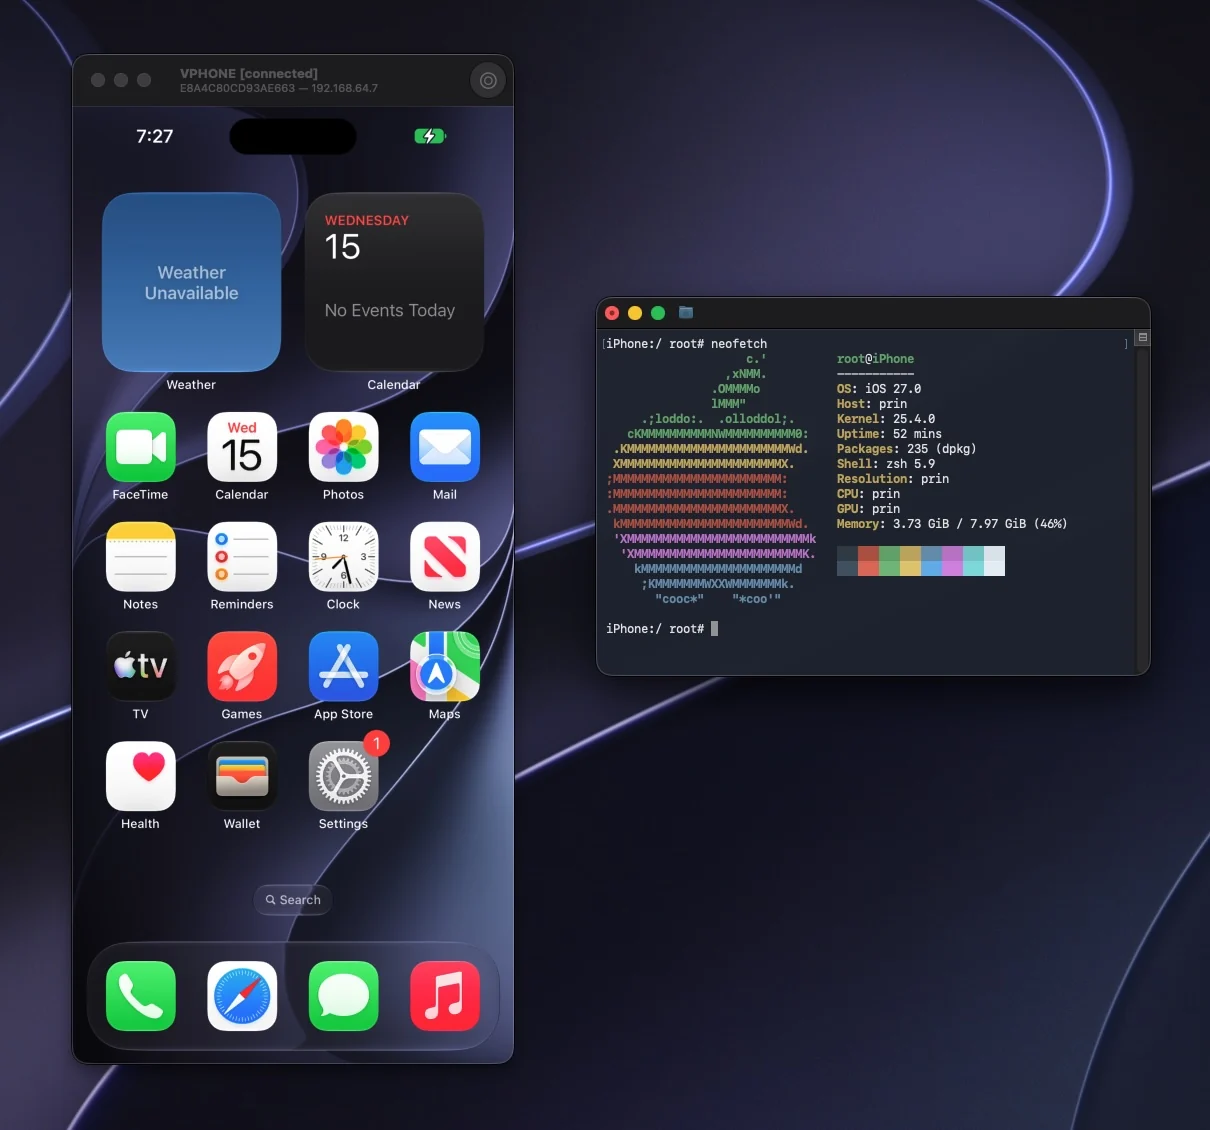 lakr233/vphone-cli
Boot and manage virtual iPhones on Apple Silicon with firmware patching, jailbreak variants, and security research features for iOS testing and…
 michaels1011/ephemora-cell
Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
 momo5502/sogen
🪅 Windows & Linux userspace emulator
 lxc/incus-os
Immutable Linux OS image optimized for running Incus containers and virtual machines, with UEFI Secure Boot, TPM 2.0 disk encryption, and automated…
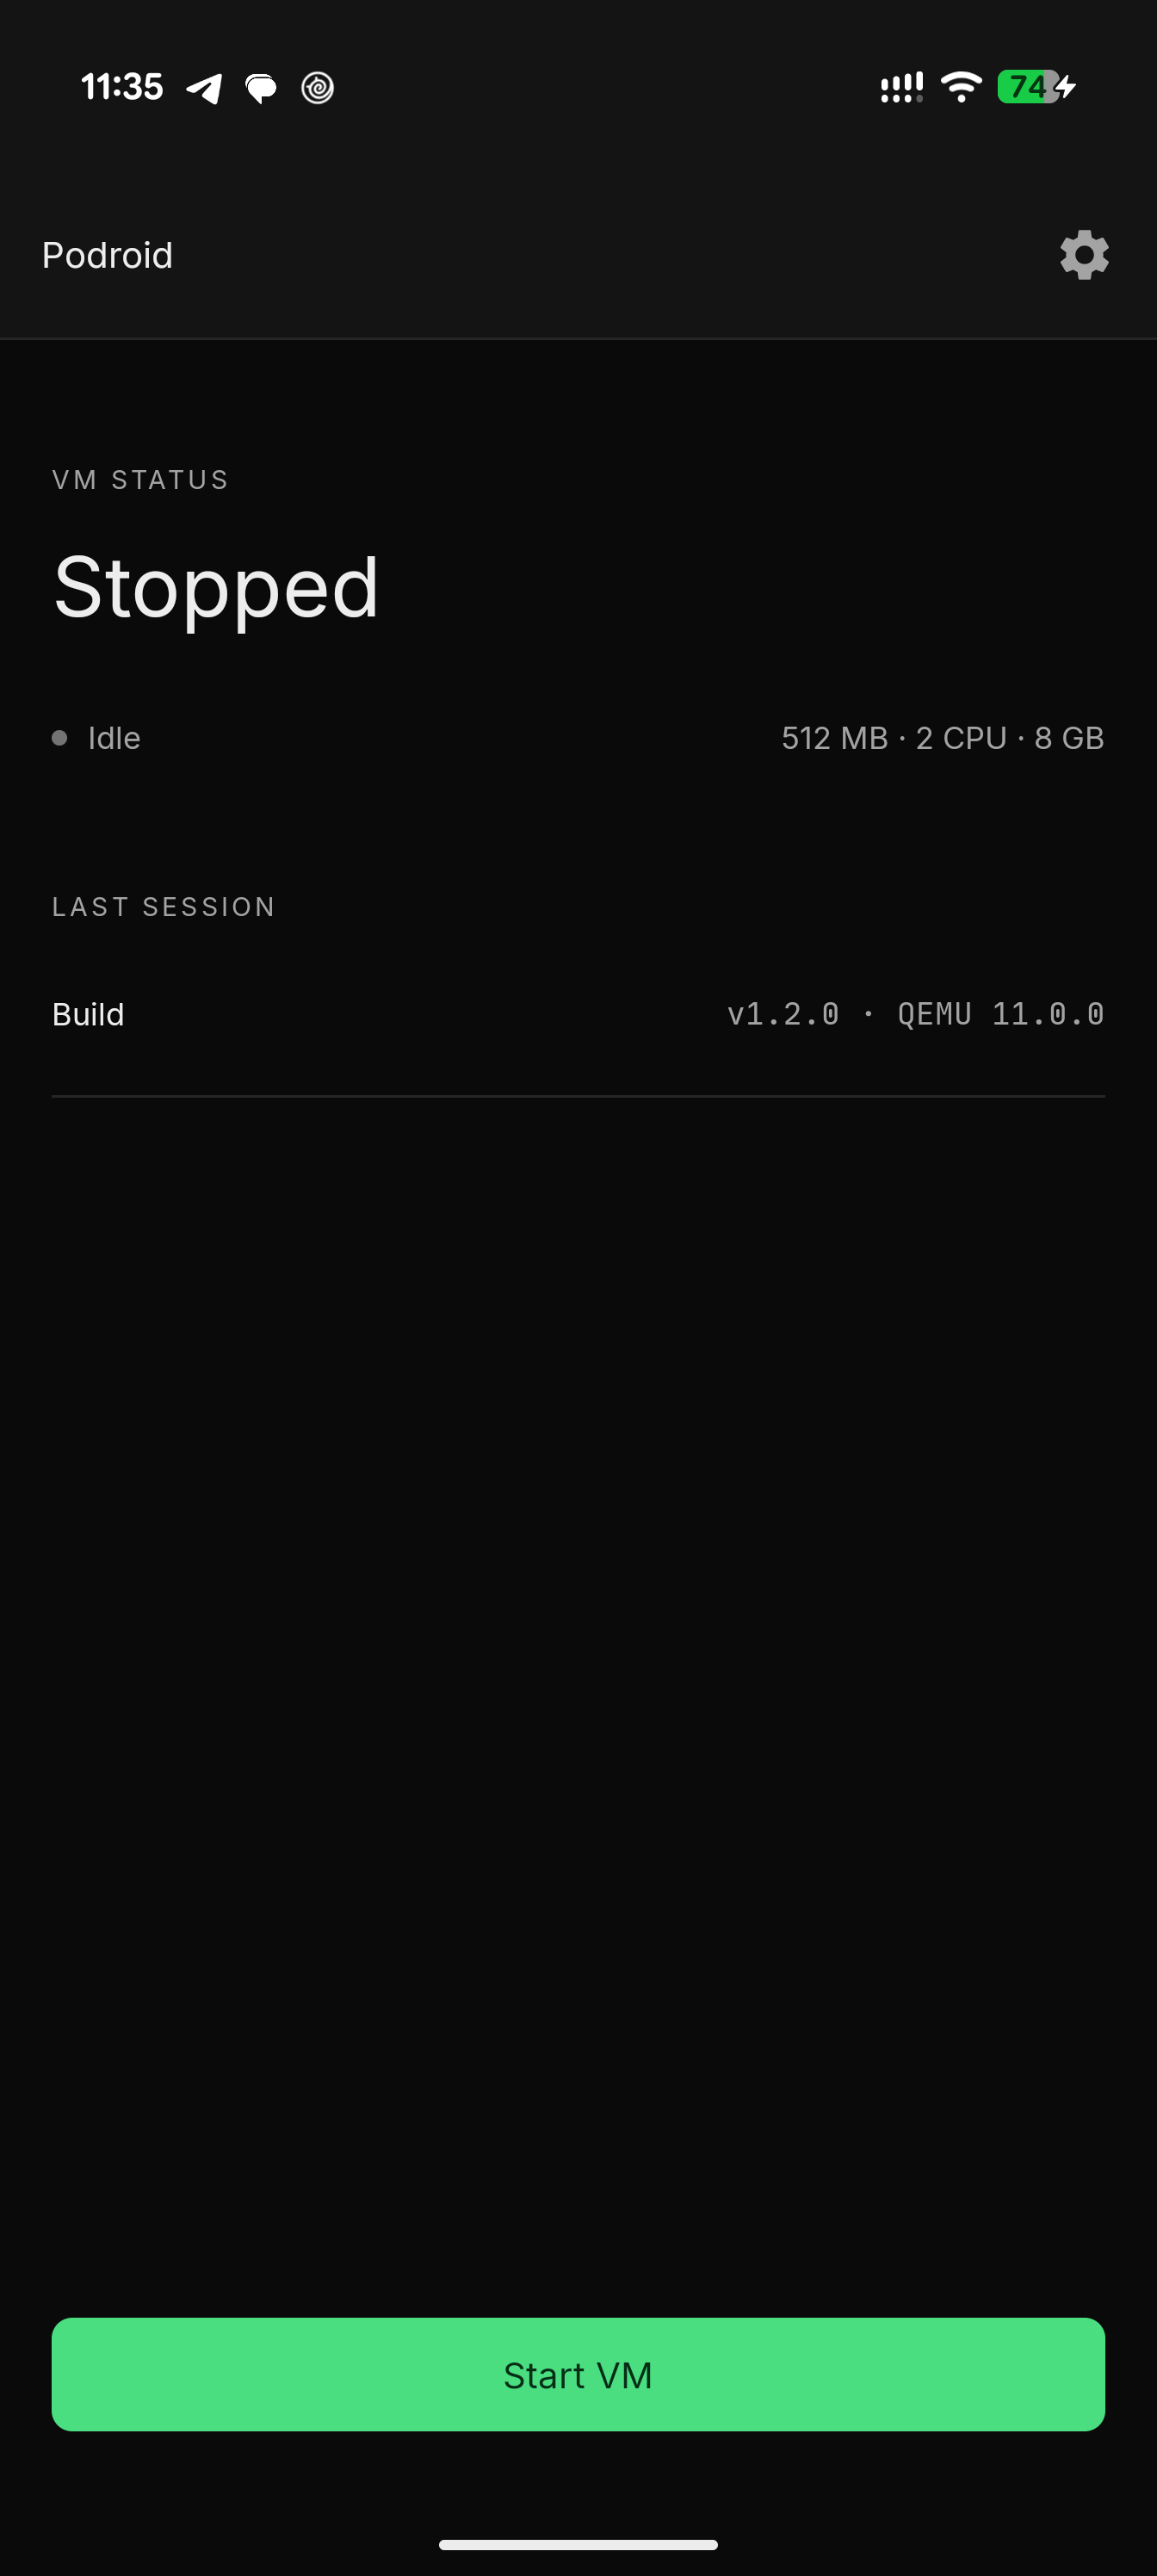 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
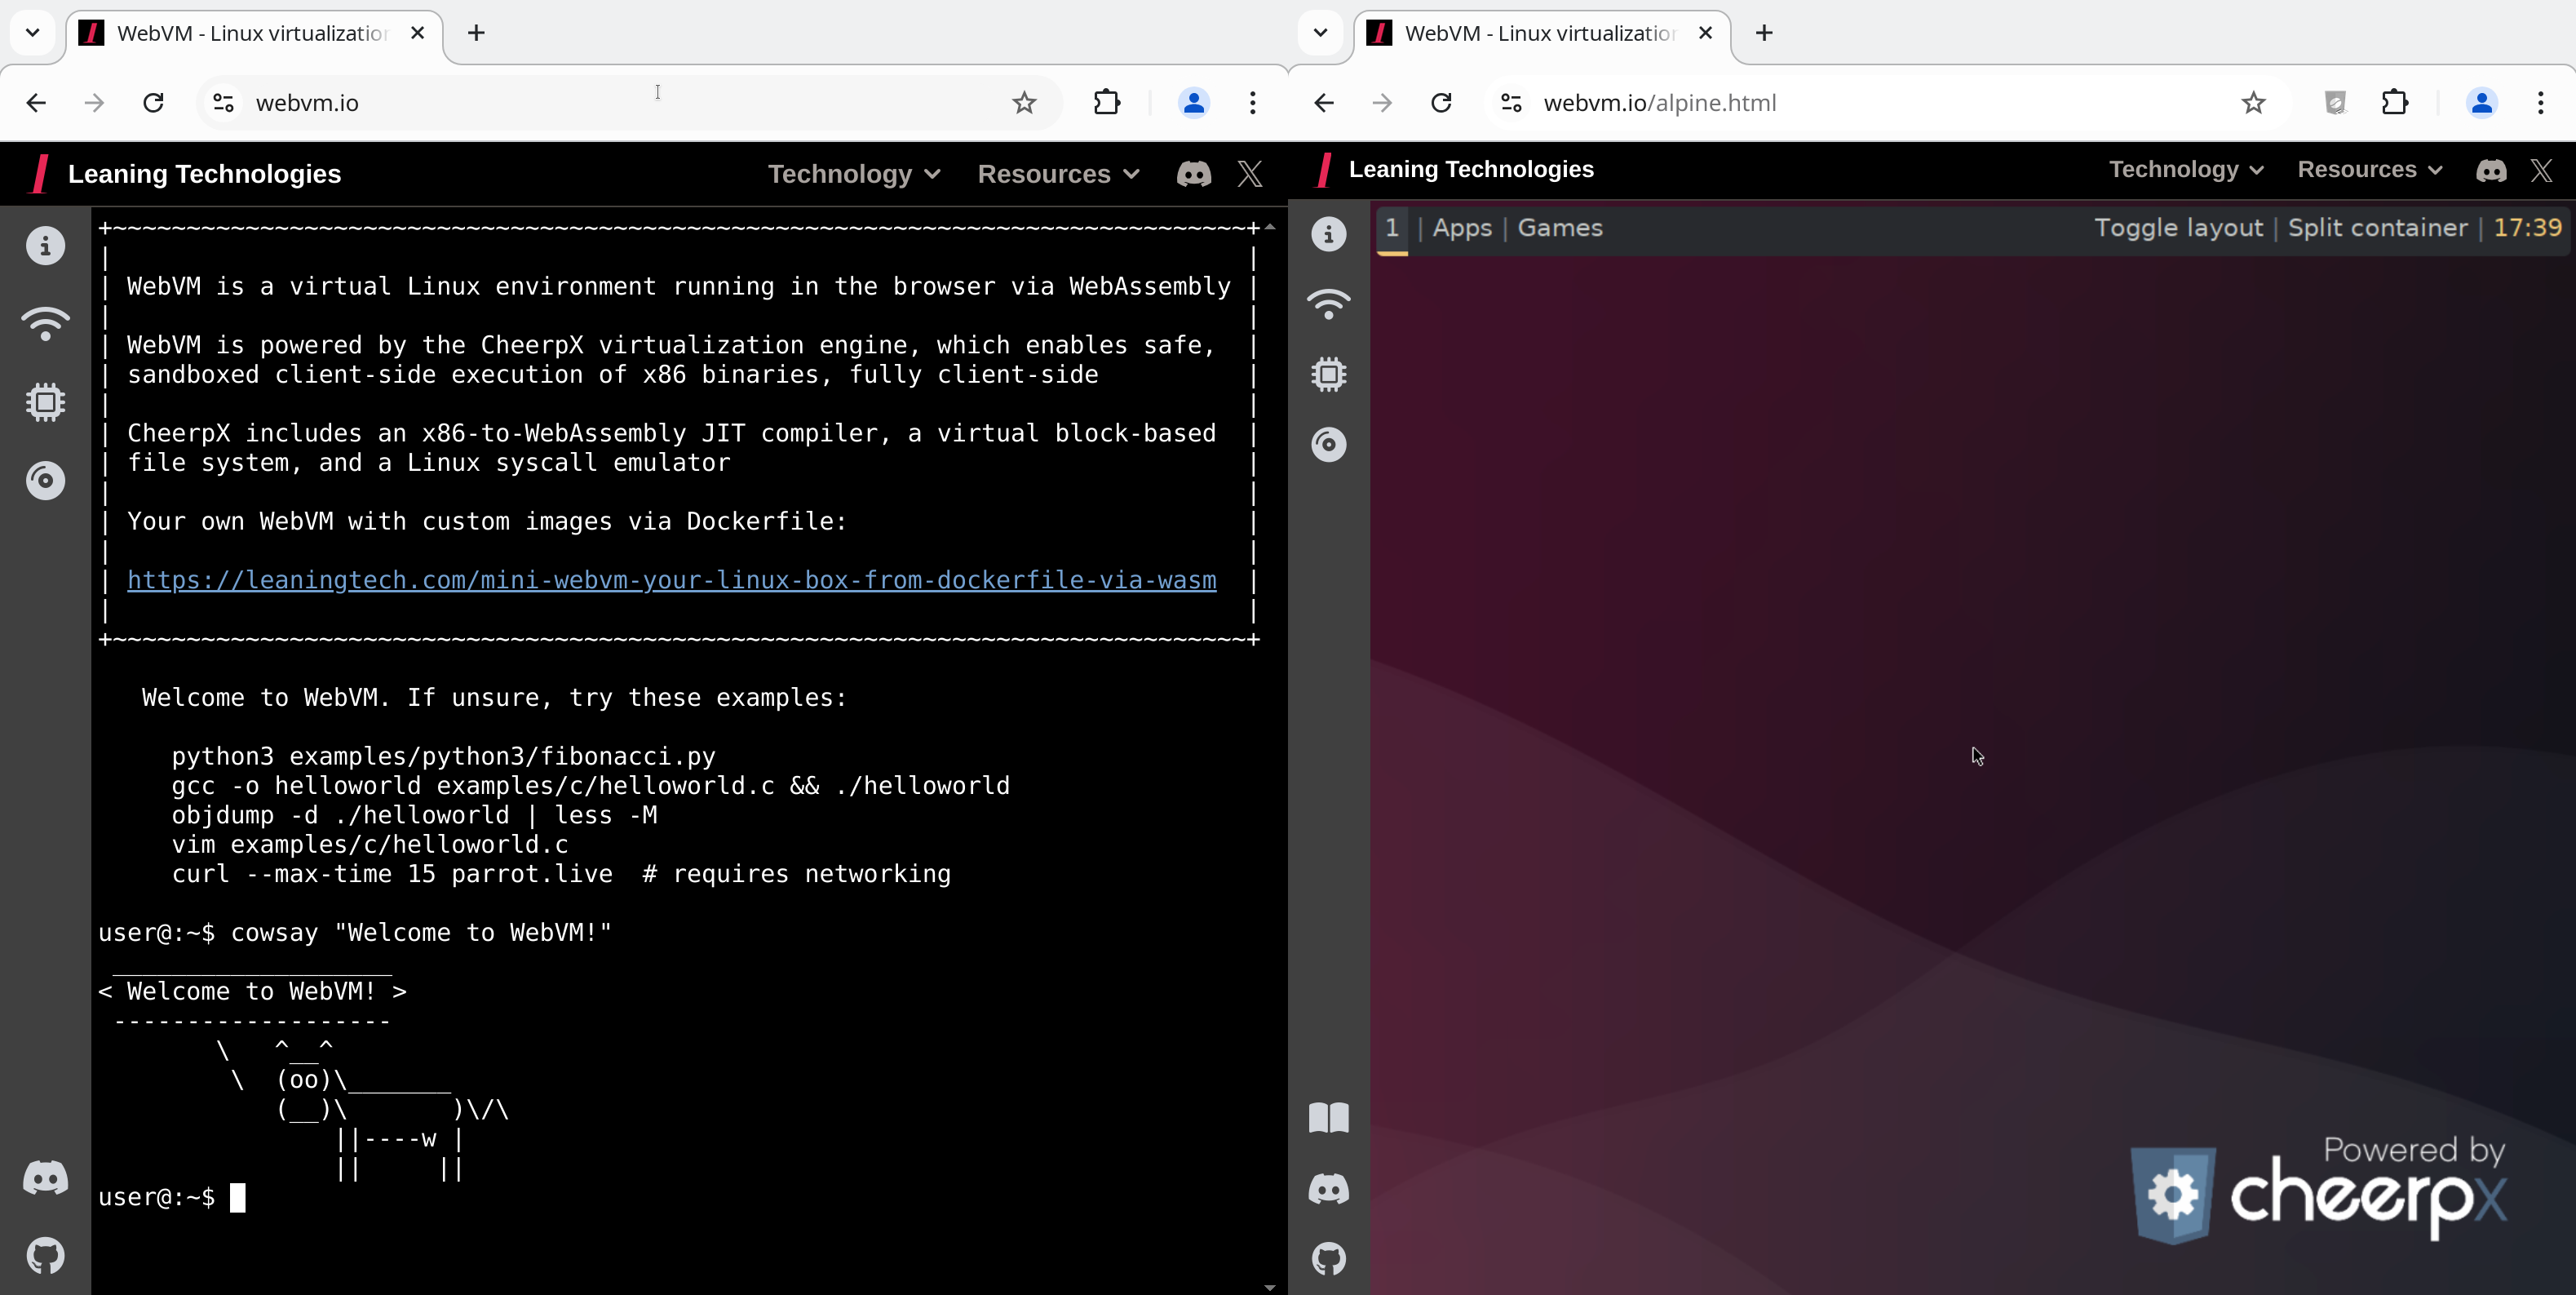 leaningtech/webvm
Client-side Linux virtual machine running in the browser via WebAssembly, with Tailscale networking, Dockerfile-based custom images, and CTF…
 s3v3n-jg/cve-2026-85706
Vagrant-based isolated GitLab lab for authorized defensive testing and validation of CVE-2026-85706, with vulnerable and patched profiles plus…
 shivammittal2403/cve-2026-59827-metabase-cyber-range
Educational cyber range for CVE-2026-59827 (Metabase H2 unsafe deserialization / CWE-502). Isolated Docker lab — training only, not for attacking…