
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
17 results
gmh5225 preview

gmh5225

GitHubgmh5225/gmh5225

LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
ai-assisted-reversingbinary-analysisbinary-exploitation+4
1 month ago
CVE-2026-59346-POC preview

CVE-2026-59346-POC

GitHub0xcyberstan/cve-2026-59346-poc

PoC for CVE-2026-59346 - 32-bit integer overflow in VMware's VMXNET3 TSO segmentation path, guest-to-host crash.
binary-exploitationexploitationhardware-iot-security+3
112 days ago
CVE-2013-2028-Exploit preview

CVE-2013-2028-Exploit

GitHubvanivamshi/cve-2013-2028-exploit

Docker-based lab and Python exploit for CVE-2013-2028, an Nginx 1.3.9 chunked-parser integer overflow, covering canary recovery, mprotect, and…

binary-exploitationeducationexploitation+6
14 days ago
ephemora-cell preview

ephemora-cell

GitHubmichaels1011/ephemora-cell

Capability-based WASM runtime for executing untrusted AI-generated code with enforced CPU, memory, time, I/O, and filesystem limits. Provides…
ai-securityapi-securitycloud-security+4
442 days ago
copy_fail preview

copy_fail

GitHubspensercai/copy_fail

Rust exploit PoC for Linux kernel LPE CVE-2026-31431 (AF_ALG page-cache write) plus eBPF runtime defense blocking AF_ALG socket creation via LSM or…
binary-exploitationdefensive-toolsexploitation+4
34 months ago
Sandb0x-Xtract0r preview

Sandb0x-Xtract0r

GitHubdarnellwashingtonjr94-art/sandb0x-xtract0r

Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…
dynamic-analysis-sandboxingmalware-analysismemory-forensics+3
37 days ago
wasm2c-tableflip preview

wasm2c-tableflip

GitHubtrustsig-eu/wasm2c-tableflip

wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.
binary-exploitationexploitationsecurity-virtualization+1
51 month ago
CVE-2026-53365 preview

CVE-2026-53365

GitHubhorkimhab/cve-2026-53365

CVE-2026-53365

binary-exploitationcontainer-escapeeducation+4
1 month ago
CVE-2026-64561 preview

CVE-2026-64561

GitHubhackspeak/cve-2026-64561

Zapscape (CVE-2026-64561) KVM/x86 shadow MMU UAF guest-to-host escape PoC mirror — V4bel/@v4bel, MIT; for authorized security testing

binary-exploitationexploitationred-teaming+2
21 month ago
snapchange preview

snapchange

GitHubawslabs/snapchange

Lightweight fuzzing of a memory snapshot using KVM
debuggersdynamic-analysis-sandboxingdynamic-code-analysis+3
4712 years ago
Zapscape preview

Zapscape

GitHubaarif450/zapscape

Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
binary-exploitationdefensive-toolsexploitation+2
18 days ago
aarif450.github.io preview

aarif450.github.io

GitHubaarif450/aarif450.github.io

Exploit KVM/x86 guest-to-host escape CVE-2026-64561 with Zapscape, a proof-of-concept demonstrating hypervisor vulnerability.

binary-exploitationcloud-infrastructure-securityexploitation+3
1 month ago
vmware-exploitation preview

vmware-exploitation

GitHubxairy/vmware-exploitation

A collection of links related to VMware escape exploits
binary-exploitationctfcurated-resources+5
1.5k2 years ago
Zapscape preview

Zapscape

GitHubv4bel/zapscape

PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
binary-exploitationcloud-securityexploitation+3
1611 month ago
Byepervisor preview

Byepervisor

GitHubps5dev/byepervisor

A PS5 hypervisor exploit for 1.xx-2xx firmwares.
binary-exploitationembedded-systems-securityexploitation+4
3571 year ago
emuko preview

emuko

GitHubwkoszek/emuko

RISC-V emulator in Rust that boots Linux with JIT on ARM64/x86_64 and Sv39 virtual memory
debuggerseducationembedded-systems-security+5
1035 months ago
matrix-rs preview
Archived

matrix-rs

GitHubmemn0ps/matrix-rs

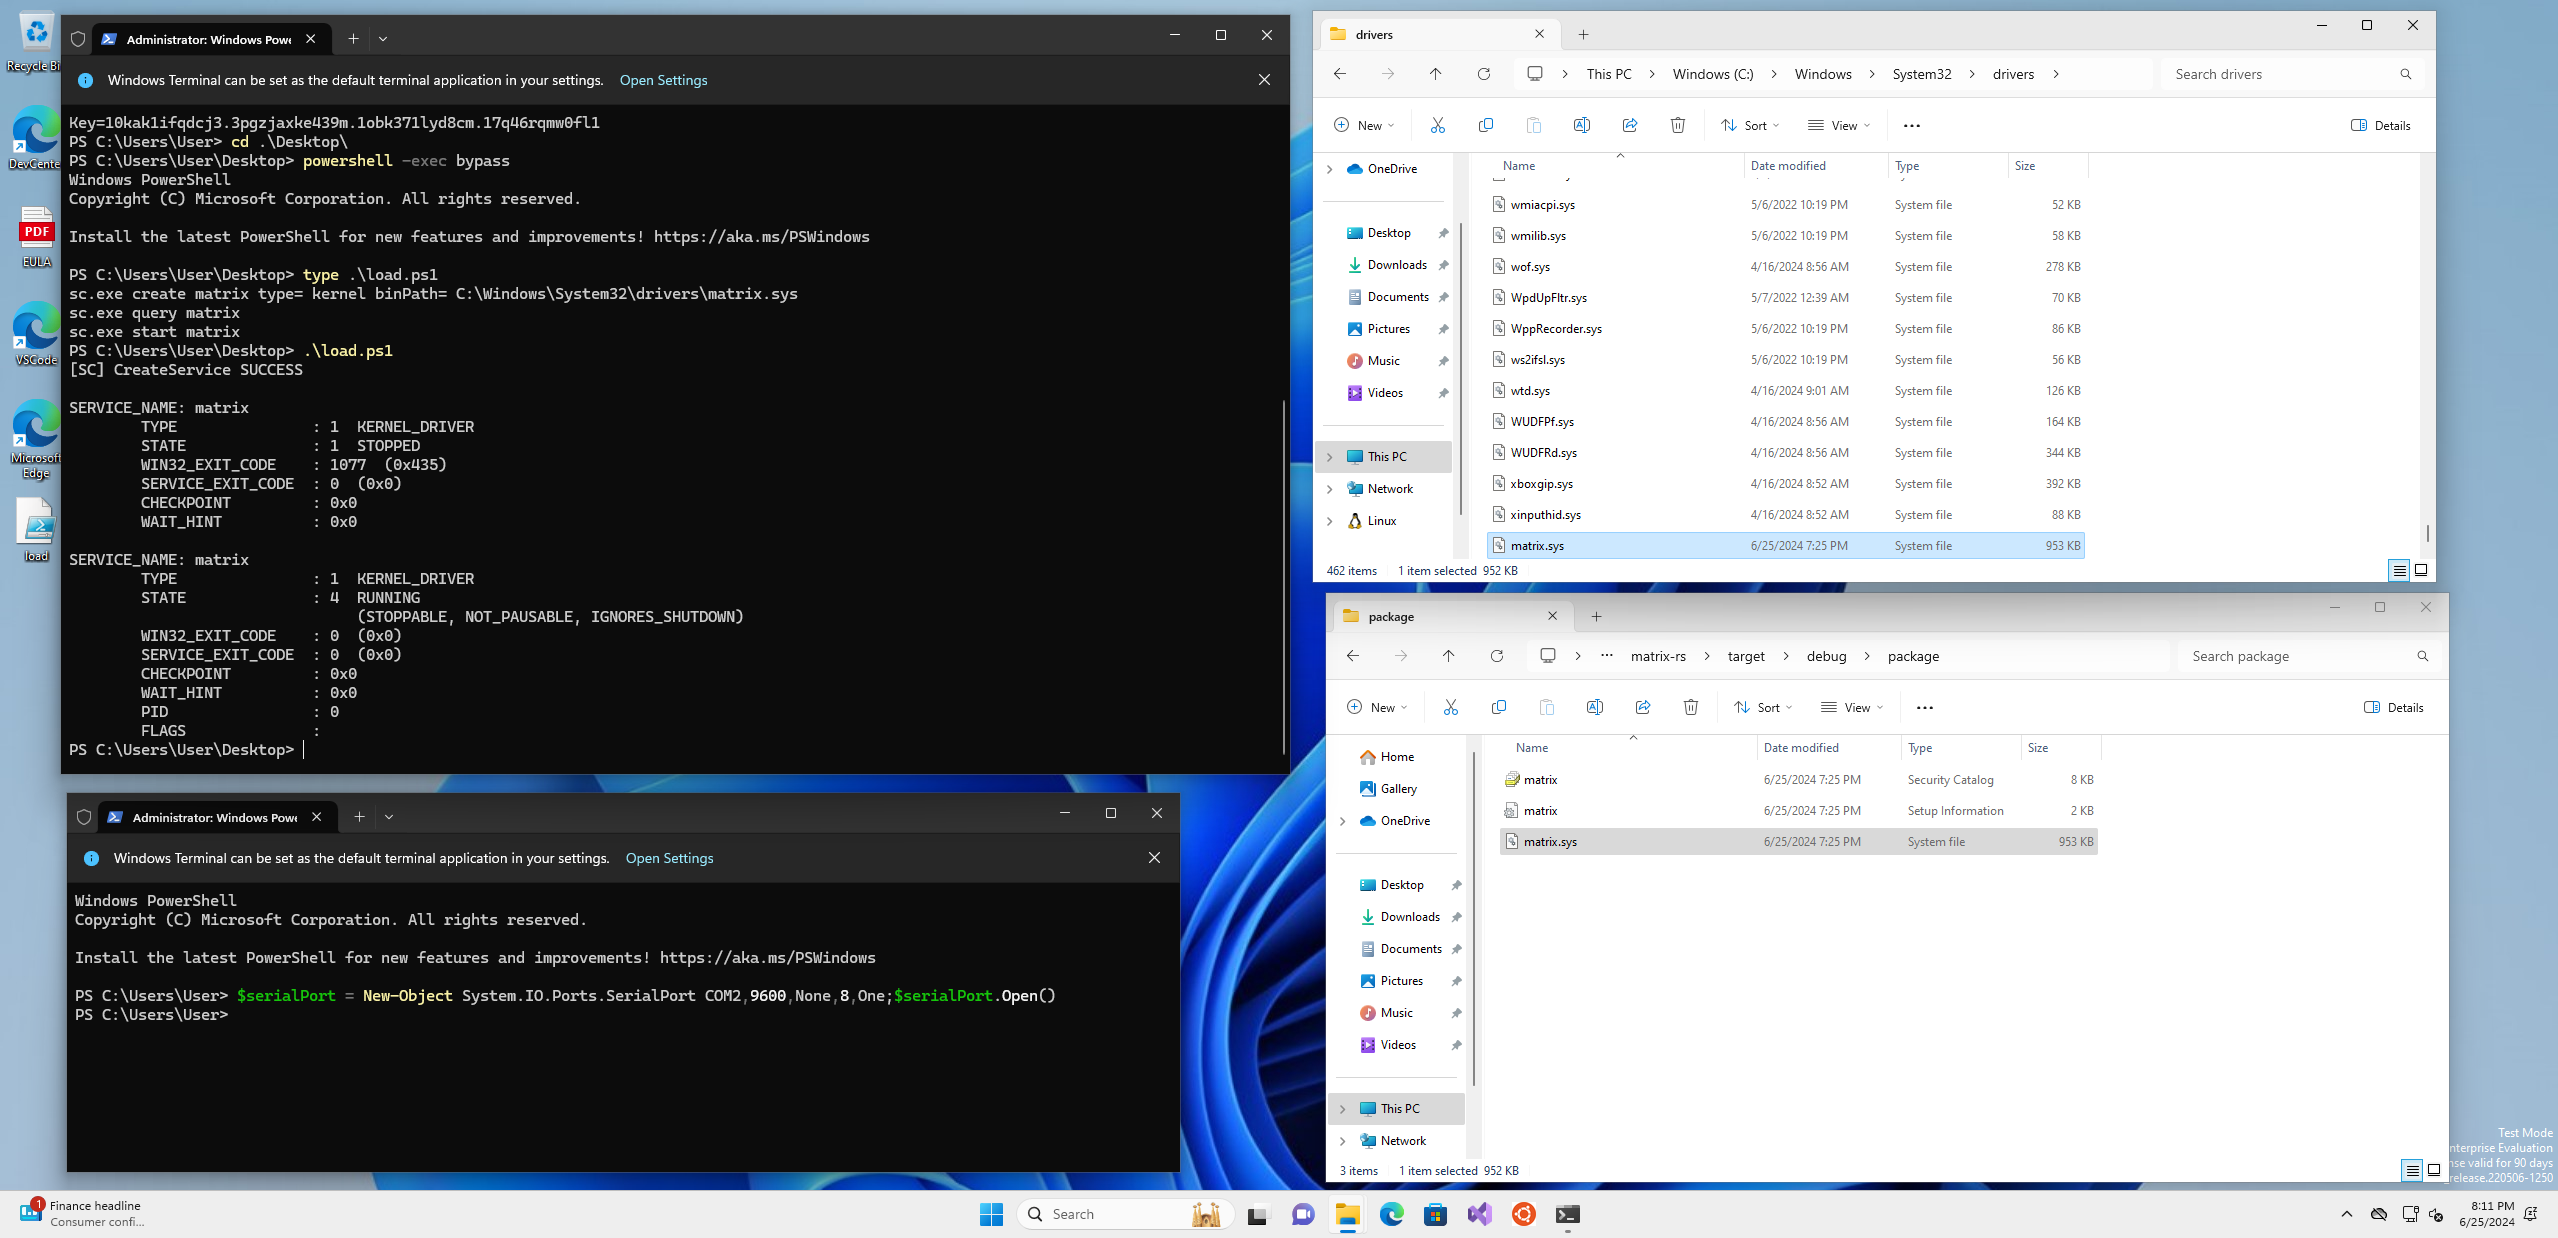
Rusty Hypervisor - Windows Kernel Blue Pill Type-2 Hypervisor in Rust (Codename: Matrix)

dynamic-code-analysiseducationids-ips-evasion+3
3594 months ago