
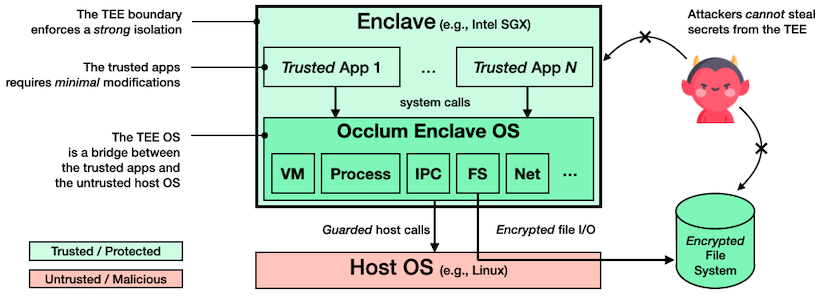
occlum
 occlum/occlum
Memory-safe, multi-process library OS for Intel SGX that runs legacy applications inside enclaves with encrypted filesystems and lightweight…
cloud-infrastructure-securitycloud-securitycryptography+5
1.5k
occlum/occlumMemory-safe, multi-process library OS for Intel SGX that runs legacy applications inside enclaves with encrypted filesystems and lightweight…
 githubsecuritylab/seclab-taskflows
Example AI-agent taskflows and MCP servers for auditing source code, triaging issues, and detecting vulnerabilities across web, Android, and iOS…
 opposum0112/cusimanse
Composable research-contract and YAML-recipe framework for agent-operated security experiments on disposable compute
 bmax121/apatch
The patching of Android kernel and Android system
 qubesos/qubes-core-admin
Manages the core lifecycle of Qubes OS domains via a Python admin API, handling secure compartmentalization with Xen and exposing an event system for…
 pazhanivelmani/external_libcap-android10_r33_cve-2023-2603
POSIX.1e capability library for Android 10, addressing CVE-2023-2603 with tools for setting and getting process capabilities to manage privilege…
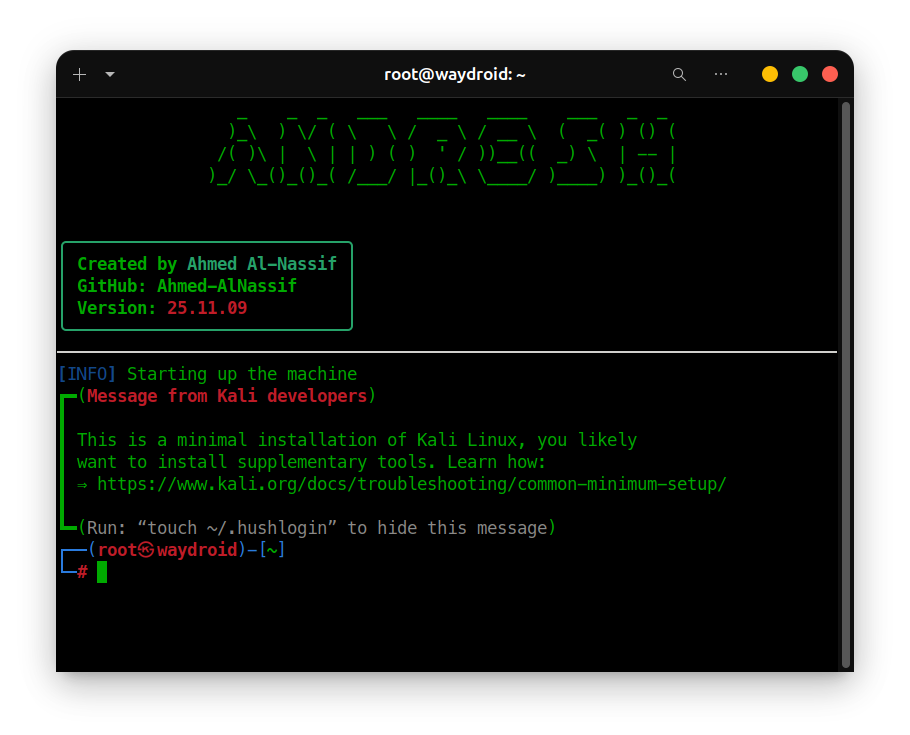 ahmed-alnassif/androsh
AndroSH No-Root Multi-Distro Linux on Android via Shizuku/ADB - Run Arch, Fedora, Alpine, Debian, Ubuntu, Kali, Void, Manjaro, OpenSUSE & Chimera…
 microsoft/litebox
A security-focused library OS supporting kernel- and user-mode execution
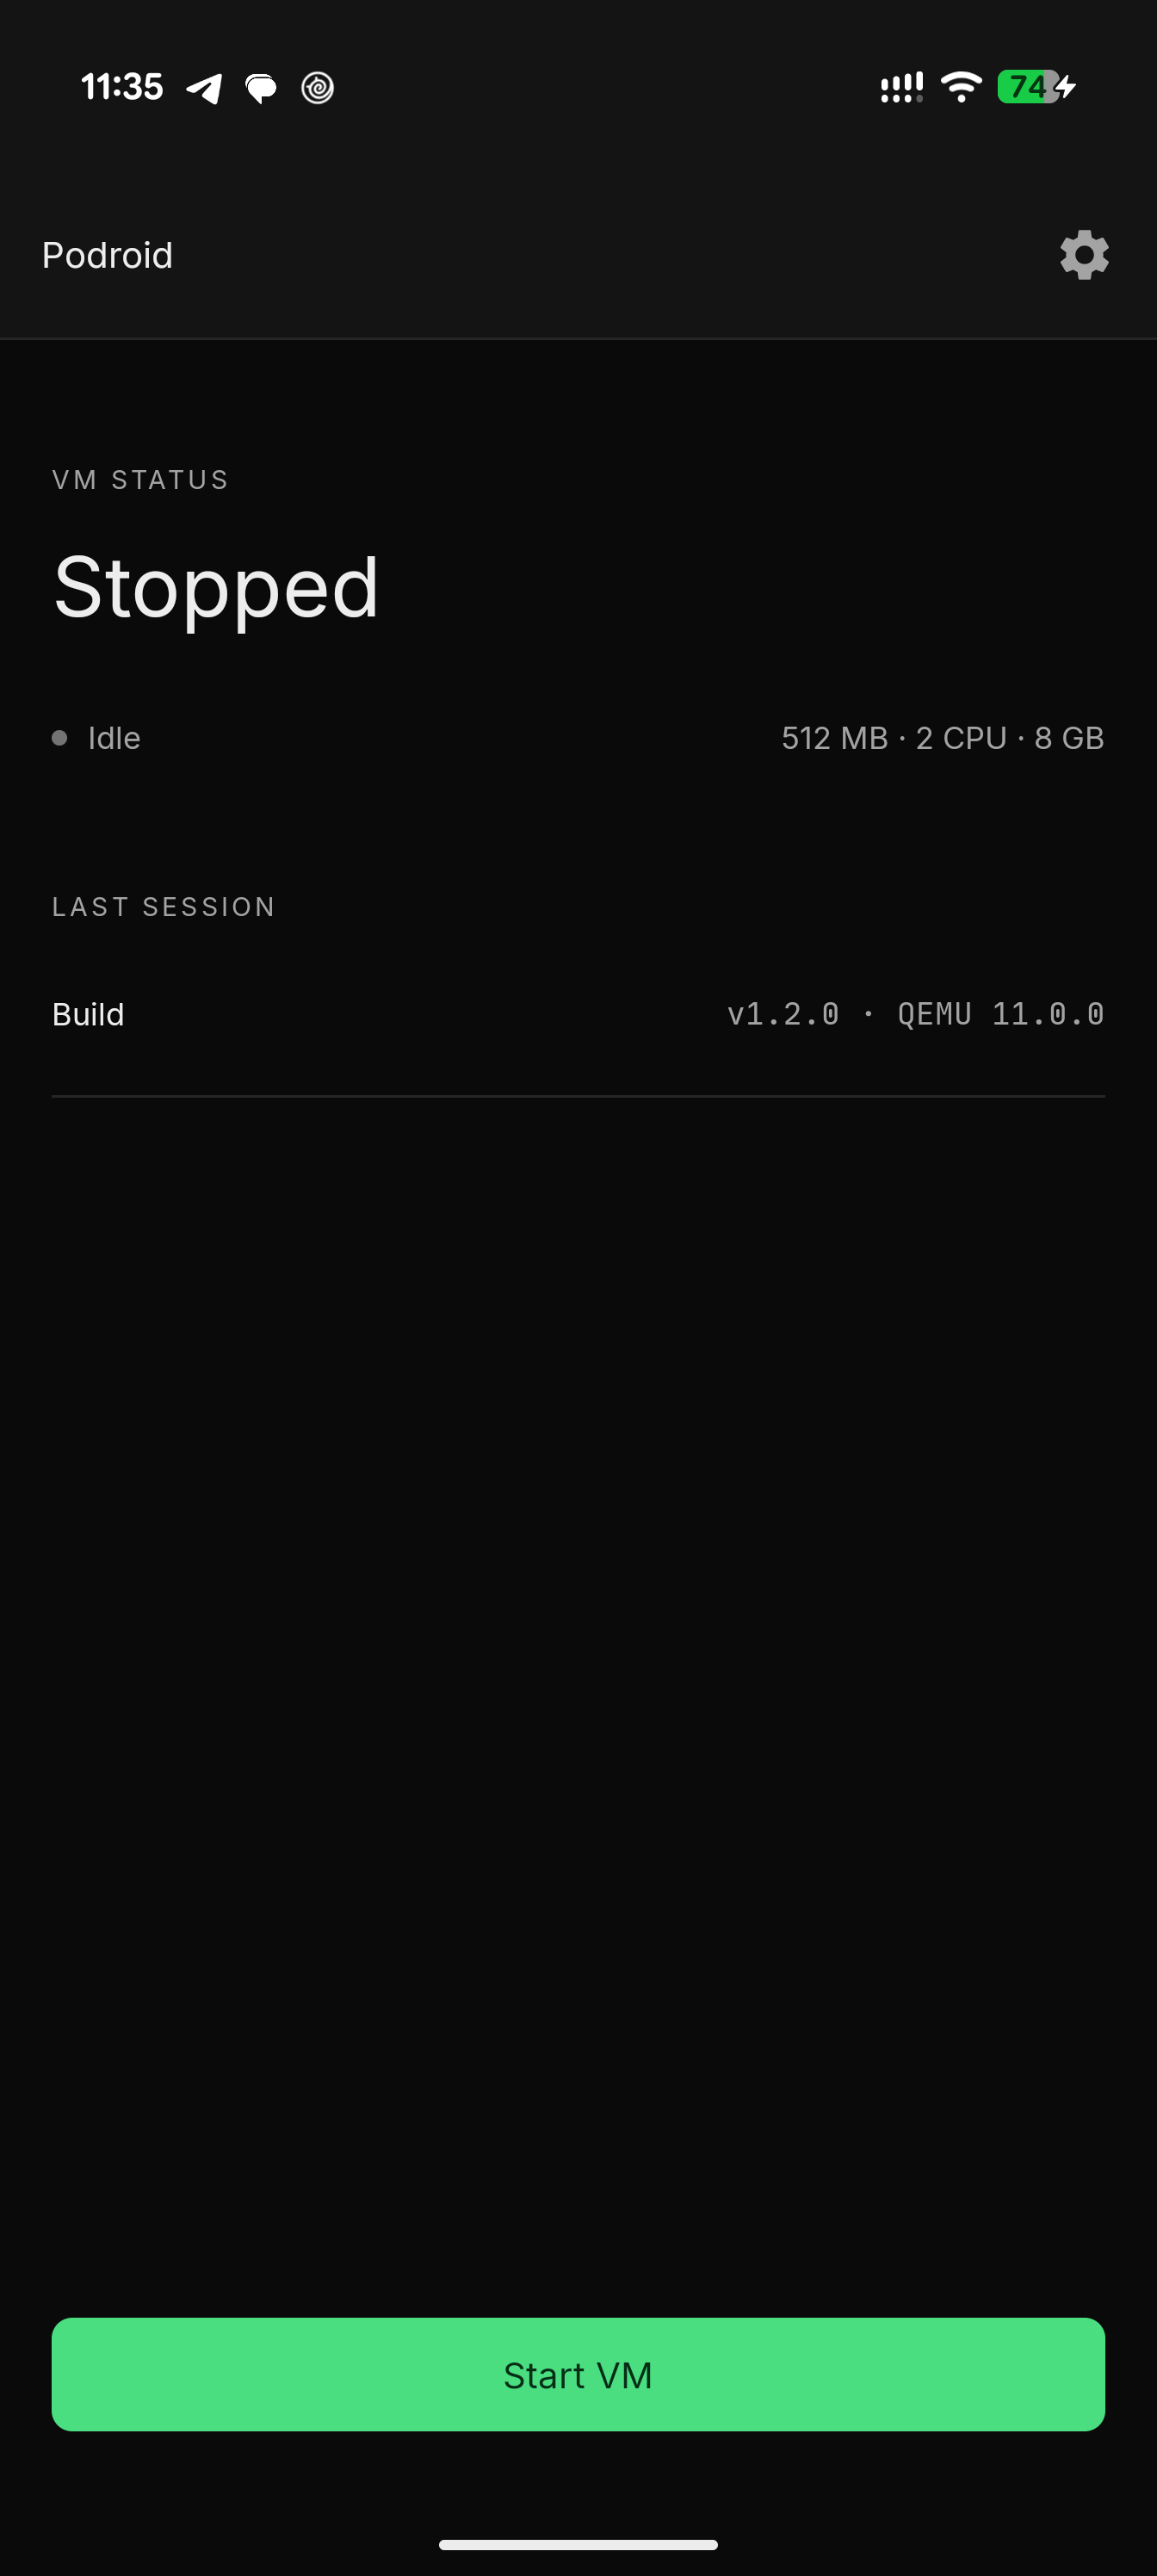 extv/podroid
A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.
 lxc/incus-os
Immutable Linux OS image optimized for running Incus containers and virtual machines, with UEFI Secure Boot, TPM 2.0 disk encryption, and automated…
 anthropic-experimental/sandbox-runtime
A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.
 qubesos/qvm-create-windows-qube
Spin up new Windows qubes quickly, effortlessly and securely on Qubes OS
 usbarmory/tamago
Framework for compiling and executing Go applications on bare metal processors, enabling secure firmware development with reduced attack surface…